SentinelOps
SentinelOps is an Australian investigator-built platform for managing investigation cases and operational intelligence.
What SentinelOps is
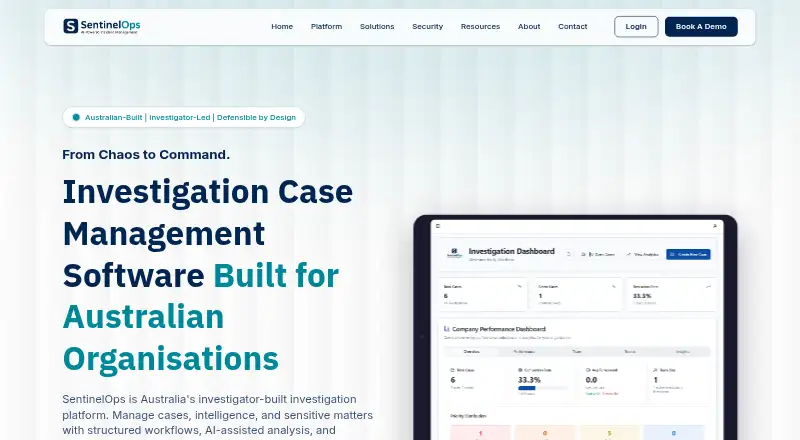
SentinelOps is an Australian investigator-built platform for managing investigation cases and operational intelligence. It supports structured intake, triage, assignment, configurable workflows, case linking, categorisation, and lifecycle tracking. Evidence tools provide secure storage, integrity verification, and chain-of-custody controls. AI assistance can help identify patterns and anomalies, search in natural language, analyze open-source information, and draft reports; investigators must review and approve the work. Its OSINT capabilities include public-source entity research, social media, corporate registries, media monitoring, and sanctions screening. Customer data is hosted exclusively in Australian data centres, without offshore replication or cross-border transfer. Records, evidence, attachments, and audit logs are encrypted at rest and in transit. Logs are append-only and cryptographically chained, including records of read access. The service runs as a managed Australian-hosted platform and is accessed through modern browsers on desktop, tablet, and mobile. It connects through a REST API, webhooks, identity standards, and documented integrations such as Azure AD, Okta, Splunk, Workday, SharePoint Online, and Google Drive. Pricing is on request.
Good
- Supports structured case intake and lifecycle tracking.
- Evidence controls include chain of custody and integrity checks.
- AI assistance requires investigator review and approval.
- Customer data stays in Australian data centres.
- Audit logs include read-access records.
Watch out
- Not currently ISO 27001 certified.
- No specific Essential Eight maturity assessment.
- Pricing is available on request.
Who it suits
It is intended for Australian enterprise, government, and regulated-industry organisations, including security, HR, financial crime, insurance, and investigative consultancy teams. It suits teams that need case workflows and evidence controls.
Verdict
SentinelOps combines investigation workflows, evidence handling, OSINT, and AI-assisted analysis with Australian data residency. Organisations needing a specific certification or Essential Eight assessment should note the stated limitations.
The facts
Each one read from SentinelOps's own pages, with the date it was checked.
What it does
- Access
- The platform is accessible through modern web browsers on desktop, tablet and mobile devices.checked 30 Sep 2026
- AI and OSINT
- SentinelOps provides AI-assisted analysis, OSINT integration, pattern detection and intelligent report drafting.checked 1 Oct 2026
- AI assistance
- AI features provide pattern and anomaly detection, natural-language search, OSINT analysis and report drafting while requiring investigator review and approval.checked 30 Sep 2026
- Audience
- The platform is intended for Australian enterprise, government and regulated-industry organisations, including security, HR, financial crime, insurance and investigative consultancy teams.checked 1 Oct 2026
- Audit trails
- Audit logs are tamper-evident, append-only and cryptographically chained, including records of read access.checked 1 Oct 2026
- Authentication
- Multi-factor authentication is enforced for every user, and enterprise customers can use standards-based single sign-on.checked 1 Oct 2026
- Case management
- The platform supports structured intake, triage, assignment, configurable workflows, case linking, categorisation and lifecycle management.checked 1 Oct 2026
- Certification limit
- SentinelOps states that it is not currently ISO 27001 certified and has not been assessed against a specific Essential Eight maturity level.checked 30 Sep 2026
- Compliance position
- SentinelOps says it is not currently ISO 27001 certified and has not been assessed against a specific Essential Eight maturity level.checked 1 Oct 2026
- Compliance posture
- SentinelOps is designed around Australian Government ISM expectations and supports frameworks including AUSTRAC, Positive Duty, SOCI Act, WHS and whistleblower obligations.checked 30 Sep 2026
- Connected systems
- Documented integrations include Azure AD, Okta, Splunk, Microsoft Sentinel, QRadar, Elastic, SAP SuccessFactors, Workday, Oracle HCM, SharePoint Online and Google Drive.checked 30 Sep 2026
- Data residency
- All customer data is hosted exclusively in Australian data centres with no offshore replication or cross-border transfer.checked 1 Oct 2026
- Deployment
- SentinelOps is delivered as a managed Australian-hosted service, while organisations with specific hosting mandates are asked to contact the team to discuss arrangements.checked 1 Oct 2026
- Encryption
- Case records, evidence, attachments and audit logs are encrypted at rest and in transit.checked 1 Oct 2026
- Evidence
- Evidence management includes secure storage, cryptographic fingerprinting and chain-of-custody controls.checked 1 Oct 2026
- Evidence handling
- Evidence management includes secure storage, chain-of-custody controls and integrity verification for files.checked 30 Sep 2026
- Integrations
- The RESTful API supports case, evidence, user, reporting and webhook integrations, with API keys, OAuth 2.0, rate limiting and IP allowlisting.checked 1 Oct 2026
- OSINT
- OSINT capabilities cover public-source entity research, social media, corporate registries, media monitoring and sanctions-list screening.checked 30 Sep 2026
- Purpose
- SentinelOps is an Australian investigation case management and operational intelligence platform.checked 1 Oct 2026
- Security
- Data is encrypted in transit and at rest, with cryptographically chained tamper-evident audit logs.checked 30 Sep 2026
- Support
- SentinelOps offers a 30-minute investigator-led walkthrough and discovery calls.checked 1 Oct 2026
- Supported systems
- Pre-built or supported integrations include Azure AD, Okta, Splunk, Microsoft Sentinel, QRadar, Elastic, SAP SuccessFactors, Workday, Oracle HCM, SharePoint Online and Google Drive.checked 1 Oct 2026
The company
- Headquarters
- Australiachecked 23 Sep 2026
The full review of SentinelOps
SentinelOps is an investigation case-management and operational-intelligence platform built for Australian organisations. It suits enterprise, government and regulated-industry teams that handle sensitive investigations. Its strongest case is the combination of evidence controls, OSINT and Australian-only hosting; organisations with specific certification requirements should consider another option.
Overview
Structured intake, triage, assignment, configurable workflows, case linking, categorisation and lifecycle tracking bring investigations into a single managed process. That breadth is useful for teams coordinating cases across security, HR, financial crime, insurance or investigative consulting, rather than organisations seeking a lightweight standalone reporting tool.
SentinelOps is delivered as a managed service hosted exclusively in Australian data centres, with no offshore replication or cross-border transfer. Organisations with a specific hosting mandate are invited to discuss arrangements with the team. The Australian residency commitment will matter to buyers with local data-handling obligations; it does not, by itself, establish a certification.
Key features
Evidence handling combines secure storage, cryptographic fingerprinting, integrity verification and chain-of-custody controls. Tamper-evident, append-only audit logs are cryptographically chained and record read access. Case records, evidence, attachments and logs are encrypted in transit and at rest. Together, these controls give investigation teams a clear accountability trail for sensitive material.
OSINT covers public-source entity research, social media, corporate registries, media monitoring and sanctions-list screening. AI assistance can detect patterns and anomalies, support natural-language search and OSINT analysis, and draft reports. Investigator review and approval remain required, so these features assist analysis rather than replace accountable judgment.
Integrations include a RESTful API, webhooks, SAML 2.0, OpenID Connect and SCIM provisioning, with supported connections to Azure AD, Okta, Splunk, Microsoft Sentinel, QRadar, Elastic, SAP SuccessFactors, Workday, Oracle HCM, SharePoint Online and Google Drive. That range can help organisations connect identity, investigative and HR systems. Multi-factor authentication is enforced for every user; enterprise customers can also use standards-based single sign-on.
The platform is designed around Australian Government ISM expectations and supports obligations and frameworks including AUSTRAC, Positive Duty, the SOCI Act, WHS and whistleblower requirements. But it is not currently ISO 27001 certified and has not been assessed against a specific Essential Eight maturity level. Buyers whose procurement depends on either should treat that as a substantive limitation, not assume the broader compliance posture is equivalent.
Pricing
SentinelOps is paid software with custom pricing. The company offers a 30-minute investigator-led demo and says it responds to enquiries within one business day. Without a published plan structure, buyers should request a quote for their intended team and deployment needs before comparing total cost.
Platforms
SentinelOps is available through its API and the web. Modern browsers support access on desktop, tablet and mobile devices, so teams can work across common device types without a separate native app being specified.
Who it's for
SentinelOps is aimed at Australian enterprise, government and regulated-industry organisations, particularly security, HR, financial-crime, insurance and investigative-consultancy teams. Its investigation workflows, evidence controls and local hosting make it a stronger fit for organisations managing sensitive cases than for buyers looking primarily for a low-cost, self-serve tool. Its certification limits make it a weaker fit for procurement processes that require ISO 27001 or a defined Essential Eight assessment.
Pros and cons
- Pros: Australian-only data hosting supports organisations with local residency needs.
- Pros: Cryptographic evidence controls and read-access audit trails strengthen accountability for sensitive investigations.
- Pros: OSINT, investigator-reviewed AI and a broad set of identity, security, HR and document integrations bring several investigation needs together.
- Cons: No ISO 27001 certification or specific Essential Eight maturity assessment may rule it out for some procurement requirements.
- Cons: Custom pricing means teams must request a quote rather than compare a published entry-level plan.
Alternatives
For a broader shortlist, see Workplace Investigation Software.
- Pulpstream Employee Relations is worth considering if Android or iOS access matters; its paid pricing is a custom quote billed as a flat fee per employee or per user.
- OnePointe may suit teams that want a stated setup and monthly cost: its Year 1 setup is $2,000 a month and Year 1 monthly is $250 a month.
- Ethicontrol is an option for buyers seeking a trial or a self-hosted platform; it offers a Starter plan at $99 a month and a free trial.
- Safecall Investigation Case Management is another paid, SaaS web-based investigation case-management option with pricing provided on request.
- Case360 is an alternative for teams looking for a web-based product with a free trial and a published Solo plan at A$33 a month.
- Sodales Employee Relations is another paid option, with annual subscription and setup fees based on employee count.
- InfraNet HR is a web-based option with custom pricing based on company size and invite-only access.
- HR Acuity is another paid, web-based alternative.
Verdict
Choose SentinelOps if your Australian organisation needs structured investigations, controlled evidence handling and OSINT in a locally hosted service, with AI kept under investigator review. Look elsewhere if ISO 27001 certification or an assessed Essential Eight maturity level is mandatory; those are clear gaps despite the platform's broad security controls and compliance focus.
Alternatives to SentinelOps
- 1
EQS Integrity Line
AndroidiOSWebAPI7.5From £85 a month - 2
FocusOSHR
Free planWeb7.4From $29 a month - 3
EQS Integrity Line
AndroidiOSWeb7.0From £85 a month - 4
Donesafe
AndroidiOSWebAPI6.5 - 5
Ethicontrol
WebAPISelf-hosted6.4From $99 a month - 6
OnePointe
WebAPImacOSWindows6.4