Sniffnet
Sniffnet is a free network monitoring app for Linux, macOS, and Windows.
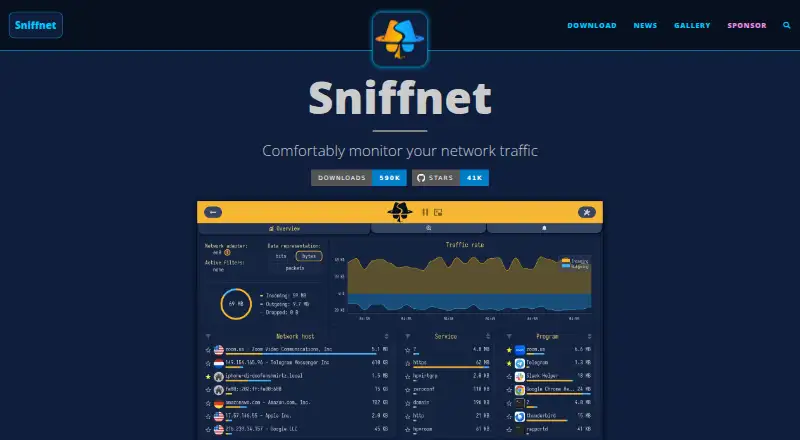
What Sniffnet is
Sniffnet is a free network monitoring app for Linux, macOS, and Windows. It tracks internet traffic, displays overall statistics and live traffic-intensity charts, and can show which programs are using bandwidth. Choose a network adapter, filter traffic, and import or export PCAP capture reports. Sniffnet can identify local connections, show remote hosts’ geographic locations, and find domain names and ASNs. It recognizes more than 6,000 upper-layer services, protocols, trojans, and worms. Users can set event notifications and import custom IP blacklists to flag potentially dangerous connections. The app also supports live capture, protocol dissectors, display filters, and offline trace analysis. It can read PCAPNG and CAP files as well as PCAP, and offers custom themes in 26 languages. Its listed plan is fully free and open-source under MIT or Apache-2.0. The 2025 security audit reported one low-severity finding, which was fixed. Sniffnet uses offline databases for most functions, but makes reverse DNS lookups to provide hostnames.
Good
- Free and open-source under MIT or Apache-2.0
- Shows live traffic charts and per-program bandwidth use
- Reads PCAP, PCAPNG, and CAP files
- Identifies more than 6,000 services and threats
- Available in 26 languages with custom themes
Watch out
- Does not support traffic decryption
- Reverse DNS lookups are used to provide hostnames
Who it suits
Sniffnet suits people who want to monitor network activity without relying on a complex analyzer. It also fits users who need capture filtering, host details, or alerts across Windows, macOS, or Linux.
Verdict
Sniffnet combines live monitoring, capture analysis, and host information in a free desktop app. Its lack of traffic decryption is worth noting if that capability is required.
Plans and prices
From Sniffnet's own pricing page, checked 15 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free | Free | Network monitoring · live charts · traffic statistics · PCAP import/export · Windows/macOS/Linux desktop builds |
| Sniffnet | Free | Fully free and open-source · MIT or Apache-2.0 |
The facts
Each one read from Sniffnet's own pages, with the date it was checked.
What it does
- Adapter selection
- Users can choose a network adapter to inspect.checked 15 Oct 2026
- Alerts and blacklists
- Users can configure notifications for network events and import custom IP blacklists to highlight potentially dangerous connections.checked 30 Sep 2026
- Capture and reports
- Users can choose a network adapter, filter observed traffic, and import or export capture reports as PCAP files.checked 30 Sep 2026
- Command-line interface
- Command-line options include selecting an adapter, printing the configuration path, viewing Windows logs, restoring defaults, and showing help or version information.checked 15 Oct 2026
- Documentation
- The project wiki contains installation, capture setup, monitoring, advanced-feature and FAQ sections.checked 15 Oct 2026
- Domain and ASN data
- The app displays domain names and autonomous-system information for hosts.checked 15 Oct 2026
- Favorites
- Hosts, services and programs can be saved as favorites.checked 15 Oct 2026
- Flow-level monitoring
- The project emphasizes flow details such as country, organization, domain and upper-layer service instead of presenting full packet payloads.checked 15 Oct 2026
- Funding
- NLnet records an NGI0 Commons Fund grant for Sniffnet covering June 2024 through July 2025.checked 15 Oct 2026
- Geolocation
- Remote hosts can be shown with geographical-location information.checked 15 Oct 2026
- Host details
- Sniffnet can identify local network connections, show remote hosts’ geographical locations, and find host domain names and ASNs.checked 30 Sep 2026
- Independent description
- Hysen Labs describes Sniffnet as a Rust and Iced cross-platform monitor aimed at visual live-traffic inspection rather than command-line packet analysis.checked 15 Oct 2026
- Independent licence listing
- SignPath Foundation lists Sniffnet as free, open-source, cross-platform software under the MIT License.checked 15 Oct 2026
- Integrations
- The webhook documentation gives SIGNL4, IFTTT, Svix and Webhook.site as compatible notification receivers.checked 15 Oct 2026
- Intended users
- The maker says Sniffnet is designed to be usable with ease by everyone, including people who find other network analyzers difficult to understand.checked 30 Sep 2026
- Licence
- Sniffnet is dual-licensed under MIT or Apache-2.0.checked 15 Oct 2026
- Limit: dependency setup
- An AlternativeTo reviewer reported that Windows 11 initially failed because wpcap.dll was missing until the installation instructions were followed.checked 15 Oct 2026
- Limit: no traffic control
- ITDeptTools says Sniffnet observes traffic but does not block applications or impose per-application speed limits.checked 15 Oct 2026
- Limit: PCAP exposure
- The published threat model warns that enabled PCAP export writes captured headers, hostnames, DNS queries and payloads to disk unencrypted.checked 15 Oct 2026
- Limit: shallow packet analysis
- Hysen Labs says Sniffnet is not a replacement for Wireshark or tcpdump when deep protocol dissection or headless automation is required.checked 15 Oct 2026
- Live charts
- Real-time charts show traffic intensity.checked 15 Oct 2026
- Local network view
- Sniffnet identifies connections in the local network.checked 15 Oct 2026
The company
- Company profile
- LinkedIn lists Sniffnet as a self-employed software-development organization with one employee, headquartered in Boissano, Italy, founded in 2022.checked 15 Oct 2026
Where it runs
- Linux requirements
- Linux builds may require libpcap, ALSA, Fontconfig and GTK development/runtime packages, and non-root users need network-capture capabilities.checked 15 Oct 2026
The full review of Sniffnet
Sniffnet is a free, open-source desktop network monitor for people who want a readable view of traffic, hosts, and the programs using bandwidth. Its combination of live monitoring and offline capture analysis is unusually broad for a no-cost tool, but it is not the right choice when traffic decryption is essential.
Overview
Sniffnet brings live traffic statistics, host information, alerts, and capture-file analysis into one application. You can select a network adapter, filter observed traffic, and follow traffic intensity in real time. That makes it useful for understanding activity on a connection without needing to start with a command-line workflow. It does not decrypt traffic, so users who need to inspect encrypted content should choose another tool.
Most functionality is provided through offline databases; the app also processes incoming traffic as needed and makes reverse DNS lookups to show hostnames for IP addresses. A 2025 security audit covered static and dynamic analysis, dependency checks, fuzzing, and interactive testing. Its only relevant finding was low severity and had been fixed.
Key features
- Traffic monitoring: Overall statistics and live intensity charts help reveal changes in bandwidth use. Application monitoring identifies programs using network bandwidth, and saved favorites make recurring attention easier.
- Capture and analysis: Sniffnet supports live capture and offline trace analysis, with display filters and protocol dissectors. It reads and writes PCAP files and reads PCAPNG and CAP files, so it can work with common capture material while limiting export to PCAP.
- Host and service details: The app can identify local connections, show remote hosts’ geographic locations, and find domain names and ASNs. Detection covers more than 6,000 upper-layer services, protocols, trojans, and worms, giving users useful context for observed connections.
- Alerts and customization: Configurable network-event notifications and imported custom IP blacklists help draw attention to connections of interest. Custom themes and 26 languages add flexibility without changing the core monitoring workflow.
- Command line: Sniffnet includes a command-line tool and command-line capture, alongside its desktop interface.
Pricing
Sniffnet is fully free and open source under MIT or Apache-2.0, at no cost. There is no paid tier or free-trial decision to navigate. Users get live capture, application monitoring, bandwidth alerts, and the same capture and analysis capabilities without a subscription; the principal functional limitation is the absence of traffic decryption.
Platforms
Sniffnet runs on Windows, macOS, and Linux. The download page directs people with persistent installation problems or questions to open an issue, a practical support route for a free open-source application.
Who it's for
Sniffnet suits home users, curious learners, and administrators who want to see bandwidth patterns, identify hosts and programs, or review capture files through a visual desktop app. Its maker aims to make network analysis approachable even for people who find other analyzers difficult. It is less suitable for investigations that depend on decrypting traffic or for anyone who needs a different platform than Windows, macOS, or Linux.
Pros and cons
- Pro: Live charts, program-level bandwidth monitoring, alerts, host context, and offline capture analysis put several useful network tasks in one free tool.
- Pro: PCAP read/write plus PCAPNG and CAP reading gives it flexibility for working with capture files.
- Pro: The 2025 audit found only a low-severity relevant issue, which had been fixed.
- Con: No traffic decryption means it cannot meet needs that require inspecting encrypted traffic.
- Con: Capture export is PCAP; PCAPNG and CAP are read-only formats in Sniffnet.
Alternatives
For a wider shortlist, browse Network Packet Capture Software, Network Packet Analyzer Software, and Bandwidth Monitoring Software.
- Termshark is another free option across Android, Linux, macOS, and Windows, but it requires tshark in PATH, a supported tshark version, and does not expose every tshark feature.
- Malcolm is a free, self-hosted, open-source alternative for readers who want that deployment model.
- NetworkMiner offers a free edition and GPLv2 open-source code for readers considering a freemium alternative.
- tcpdump is a free BSD-licensed alternative for readers who prefer a command-line capture tool; capture permission depends on the operating system and configuration.
- TShark is a free GPL v2 alternative from the Wireshark project for readers considering that project’s command-line tool.
- Wireshark is a free full-version alternative with no license fee.
- Arkime is a free, open-source option for readers seeking a self-hosted web-based tool with no paid-only features or license fees.
- PCAPdroid is an Android alternative with free core monitoring and capture; its paid features are a one-time purchase.
Verdict
Choose Sniffnet if you want a free desktop app that combines live bandwidth monitoring, host and service identification, alerts, and practical capture-file analysis. Its approachable visual focus and broad feature set make it a strong fit for routine network visibility across Windows, macOS, and Linux. Look elsewhere when traffic decryption is a requirement.
Alternatives to Sniffnet
- 1
ntopng
Free planOpen sourceWebAPILinuxmacOS8.3€299.95 one-time - 2
GlassWire
Free planAndroidWebWindows7.9From $2.99 a month - 3
NetBalancer
Free planWebAPIWindows7.5$34.95 one-time - 4

ManageEngine NetFlow Analyzer
Free planAndroidiOSWebLinux7.1From $172 a month - 5
sFlowTrend
Free planWebAPILinuxmacOS7.1Free plan - 6
SoftPerfect Bandwidth Manager
Free planLinuxmacOSWindows7.0$49 one-time