NetworkMiner
NetworkMiner analyzes captured network traffic and can sniff live traffic, extracting artifacts such as files, images, emails and passwords from PCAP files.
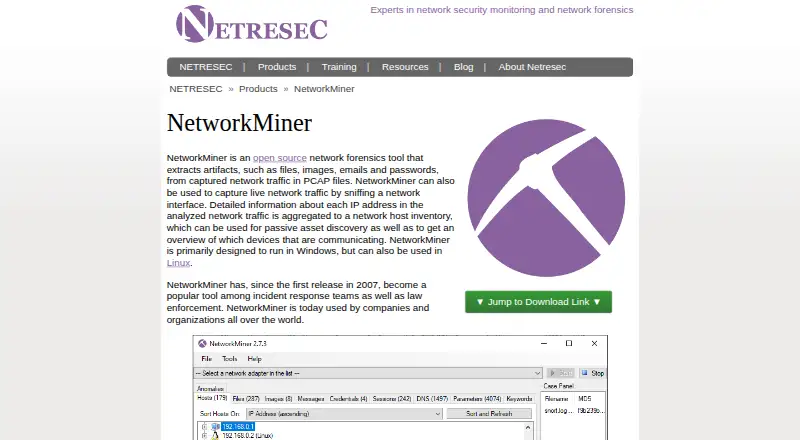
What NetworkMiner is
NetworkMiner analyzes captured network traffic and can sniff live traffic, extracting artifacts such as files, images, emails and passwords from PCAP files. It also builds a host inventory from IP address information to support passive asset discovery and communication overviews. The free edition parses PCAP and ETL files and supports live sniffing on Windows and Linux, but it does not parse PcapNG. NetworkMiner Professional accepts PcapNG, Pcap-over-IP and PacketCache data as well as PCAP and ETL, and exports results to CSV, JSON-LD or XML. Its protocol analysis and VoIP features include file and audio extraction, while OSINT lookups cover hashes, IP addresses, domains and URLs. NetworkMiner does not decrypt HTTPS or other TLS-encrypted sessions. Extracted data stays on the user's device, not in the cloud. The free and open-source code is released under GPLv2. The free plan is free; the Single User License is $1,300, paid once, valid for three years, and the Corporate License is $6,500, paid once.
Good
- Extracts files, images, emails and passwords from PCAP files
- Builds a host inventory for passive asset discovery
- Professional exports to CSV, JSON-LD and XML
- Supports live sniffing and multiple capture sources
Watch out
- Does not decrypt HTTPS or other TLS-encrypted sessions
- Free edition does not parse PcapNG
- PCAP files can automatically extract malware
- Professional is not FIPS 140-compliant
Who it suits
NetworkMiner suits incident response teams, law enforcement, companies and organizations that need to inspect captured or live network traffic. The free edition is for Windows and Linux users who do not need PcapNG parsing.
Verdict
NetworkMiner combines traffic artifact extraction with host inventory and live sniffing. Check its TLS and FIPS limitations, and use care with PCAP files because they may automatically extract malware.
Plans and prices
From NetworkMiner's own pricing page, checked 1 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free Edition | Free | live sniffing · PCAP/ETL parsing · Windows/Linux · no PcapNG parsing |
| Single User License | $1,300, paid once | one named employee · GUI application · free updates and support for three years · valid for three years from purchase |
| Corporate License | $6,500, paid once | unlimited employees in registered organization · GUI and command-line applications · free updates and support during first year · perpetual license |
The facts
Each one read from NetworkMiner's own pages, with the date it was checked.
What it does
- Command line
- NetworkMinerCLI provides command-line scripting support and is available only with a Corporate License.checked 1 Oct 2026
- Data location
- NetworkMiner stores extracted data locally on the end-user device rather than in the cloud.checked 1 Oct 2026
- FIPS compliance
- NetworkMiner Professional is not FIPS 140-compliant and requires FIPS enforcement to be disabled on the PC.checked 1 Oct 2026
- Host inventory
- The software aggregates detailed information about IP addresses into a network host inventory for passive asset discovery and communication overviews.checked 1 Oct 2026
- Open source
- The source code is written in 100% managed C# on the Microsoft .NET Framework and is released as GPLv2 free and open source software.checked 1 Oct 2026
- OSINT
- Professional provides OSINT lookups for file hashes, IP addresses, domain names and URLs, plus offline IP-to-country and IP ASN lookups.checked 1 Oct 2026
- Primary users
- Netresec says NetworkMiner has been used by incident response teams, law enforcement, companies and organizations worldwide since its first release in 2007.checked 1 Oct 2026
- Professional exports
- NetworkMiner Professional exports data in CSV for Excel, JSON-LD and XML formats.checked 1 Oct 2026
- Professional inputs
- NetworkMiner Professional accepts PCAP, PcapNG and ETL capture files, Pcap-over-IP, PacketCache data and live sniffing.checked 1 Oct 2026
- Protocol analysis
- Professional supports file extraction from FTP, TFTP, HTTP, HTTP/2, SMB, SMB2, SMTP, POP3, IMAP and LPR protocols.checked 1 Oct 2026
- Purpose
- NetworkMiner extracts artifacts such as files, images, emails and passwords from captured network traffic in PCAP files and can sniff live network traffic.checked 1 Oct 2026
- Safety guidance
- Netresec warns that opening PCAPs can automatically extract malware and recommends Linux or Windows Sandbox to reduce self-infection risk.checked 1 Oct 2026
- TLS handling
- NetworkMiner does not decrypt HTTPS or other TLS-encrypted sessions; it extracts X.509 certificates, and PolarProxy can decrypt traffic and forward it to NetworkMiner.checked 1 Oct 2026
- VoIP
- Professional supports SIP, RTP, G.711 and G.722, including audio extraction from unencrypted VoIP calls.checked 1 Oct 2026
The company
- Founded
- 2010checked 28 Sep 2026
- Headquarters
- Örsundsbro, Swedenchecked 28 Sep 2026
The full review of NetworkMiner
NetworkMiner is desktop software for extracting artifacts from network captures and building a passive inventory of hosts. It is best suited to incident responders and investigators who need to examine PCAPs or sniff live traffic. Its free edition covers basic parsing and sniffing, while Professional adds broader formats and analysis tools—but does not decrypt TLS traffic.
Overview
NetworkMiner pulls files, images, emails and passwords from captured network traffic, and can also sniff live traffic. It groups details about IP addresses into a host inventory, giving investigators a way to discover assets and review communications alongside extracted artifacts.
It runs on Linux, macOS and Windows, and keeps extracted data on the end-user device rather than in the cloud. The source code is GPLv2 open source, written in managed C# on the Microsoft .NET Framework. Its desktop focus suits workstation-based investigation, but it is not a cloud analysis service.
NetworkMiner does not decrypt HTTPS or other TLS-encrypted sessions. It can extract X.509 certificates, and PolarProxy can decrypt traffic and forward it to NetworkMiner; that adds a separate tool to the workflow rather than making decryption a native capability.
Opening PCAPs can automatically extract malware. Netresec recommends Linux or Windows Sandbox to reduce self-infection risk, so examining untrusted captures calls for an isolated environment.
Key features
Capture analysis and host inventory
The free edition parses PCAP and ETL files and supports live sniffing. Professional broadens inputs to PcapNG, Pcap-over-IP and PacketCache data, as well as PCAP, ETL and live traffic. That makes the paid version a better fit for teams receiving captures in varied formats or sources; the free edition is constrained by its lack of PcapNG parsing.
Professional investigation tools
Professional exports results to CSV, JSON-LD and XML. It extracts files from FTP, TFTP, HTTP, HTTP/2, SMB, SMB2, SMTP, POP3, IMAP and LPR, and can extract audio from unencrypted SIP/RTP VoIP calls using G.711 and G.722. OSINT lookups cover file hashes, IP addresses, domain names and URLs, with offline IP-to-country and IP ASN lookups as well.
NetworkMinerCLI adds command-line scripting, but it is limited to the Corporate License. That tier is the relevant choice for organizations that need scripted workflows; the Single User License is GUI-only.
Pricing
NetworkMiner uses a freemium model. The Free Edition costs nothing and includes live sniffing and PCAP/ETL parsing on Windows and Linux, but not PcapNG parsing.
The Single User License costs $1,300, paid once, valid for three years from purchase. It covers one named employee using the GUI application and includes free updates and support for three years. It suits an individual investigator who needs Professional features; the three-year term and single named seat are meaningful limits.
The Corporate License costs $6,500, paid once for a perpetual license covering unlimited employees in the registered organization. It includes GUI and command-line applications, with free updates and support during the first year. It is the tier for organizations needing CLI access or broader staff coverage, though ongoing updates and support are not included beyond that first year.
Professional is not FIPS 140-compliant and requires FIPS enforcement to be disabled on the PC, which rules it out for environments that must retain that enforcement.
Platforms
NetworkMiner is available for Linux, macOS and Windows. The Free Edition's stated platform support is Windows and Linux; the broader platform list applies to the product overall. It is desktop software, supports PCAP, and can work with both live and file-based capture sources.
Who it's for
Incident response teams, law enforcement, companies and organizations use NetworkMiner for network investigation. It is a strong fit when the task is extracting artifacts, assembling a host inventory or reviewing supported protocol traffic from captures. It is less suitable when investigators require TLS decryption, FIPS compliance, or PcapNG parsing without buying Professional.
Pros and cons
- Pros: Combines artifact extraction with passive host inventory, so investigators can connect files and other evidence with communicating IP addresses.
- Pros: Professional supports a broad set of capture inputs, protocol extraction, structured exports and OSINT lookups.
- Pros: Local data storage and GPLv2 open-source code may suit teams that prefer on-device analysis and inspectable software.
- Cons: It cannot decrypt TLS sessions; certificate extraction is not a substitute for access to encrypted content.
- Cons: PcapNG parsing and CLI scripting are gated to paid tiers, with CLI restricted to Corporate.
- Cons: Opening captures can automatically extract malware, so unsafe handling carries a self-infection risk.
- Cons: Professional's FIPS limitation requires disabling enforcement on the PC.
Alternatives
For a different forensic workflow, consider Paraben E3 Forensic Platform, a paid option with a free plan and trial across Android, iOS, Linux, macOS and Windows. Volatility 3 is a free, open-source option for readers seeking a framework available on Linux, macOS, Windows and self-hosted environments. CAINE is a free Linux and Windows option distributed as an approximately 4000 MB ISO, with third-party software under separate licenses.
Exterro FTK Imager offers a free Windows forensic imaging and preview tool, with a paid Pro tier. Arkime is a free, open-source option for Linux, self-hosted, web and API environments with no paid-only features or license fees. SUMURI PALADIN is a Linux freemium alternative whose free LTS edition accepts donations and whose Pro edition costs $99, paid once. Tsurugi Linux is a free 64-bit Linux distribution provided as-is without warranty. Cellebrite Inseyets is a paid web and Windows alternative with a free trial.
Browse more options in Digital Forensics Software, Network Packet Capture Software, Network Protocol Analyzers and Network Packet Analyzer Software.
Verdict
Choose NetworkMiner if your investigations center on extracting artifacts and mapping hosts from supported captures or live traffic, especially when local desktop analysis is preferred. The free edition is a practical entry point, while Professional's added formats and investigation tools justify consideration for fuller workflows. Look elsewhere if TLS decryption, FIPS compliance or uncomplicated handling of untrusted PCAPs is essential.
Getting started
- Visit the NetworkMiner website.
- Choose the free edition for live sniffing and PCAP or ETL parsing on Windows or Linux.
- For PcapNG parsing, Professional inputs, or Professional features, choose the Single User License or Corporate License.
- Open or capture network traffic using the selected edition's supported inputs.
- Use Linux or Windows Sandbox when opening PCAP files to reduce self-infection risk.
Limits worth knowing
The free edition supports live sniffing and PCAP and ETL parsing on Windows and Linux, but not PcapNG. The Single User License is $1,300, paid once and is valid for three years; the Corporate License is $6,500, paid once and is perpetual. NetworkMiner Professional is not FIPS 140-compliant and requires FIPS enforcement to be disabled on the PC.
Questions
What does NetworkMiner do?
It extracts artifacts from captured network traffic and can sniff live traffic. It also builds a host inventory from IP address details.
Is there a free edition?
Yes. The free edition supports live sniffing and PCAP and ETL parsing on Windows and Linux, but not PcapNG.
How much do the paid licenses cost?
The Single User License costs $1,300, paid once and is valid for three years from purchase. The Corporate License costs $6,500, paid once and is perpetual.
What platforms are supported by the free edition?
The free edition supports Windows and Linux.
Is NetworkMiner open source?
Yes. Its source code is released as GPLv2 free and open-source software.
Does NetworkMiner decrypt TLS traffic?
No. It does not decrypt HTTPS or other TLS-encrypted sessions, though it extracts X.509 certificates.
Alternatives to NetworkMiner
- 1

Arkime
Free planOpen sourceWebAPILinuxSelf-hosted7.3Free plan - 2
Plaso
Free planOpen sourceAPILinuxmacOSSelf-hosted7.3Free plan - 3
CAINE
Free planOpen sourceLinuxSelf-hostedWindows7.1Free plan - 4
Paraben E3 Forensic Platform
AndroidiOSLinuxmacOS7.1From $699 a year - 5
OSForensics
Free planAndroidSelf-hostedWindows7.0From $945 a year - 6
ADF Triage-G2
AndroidiOSLinuxmacOS6.8