OpenSCAP
OpenSCAP is a collection of open-source tools for security compliance and automated vulnerability assessment using the Security Content Automation Protocol (…
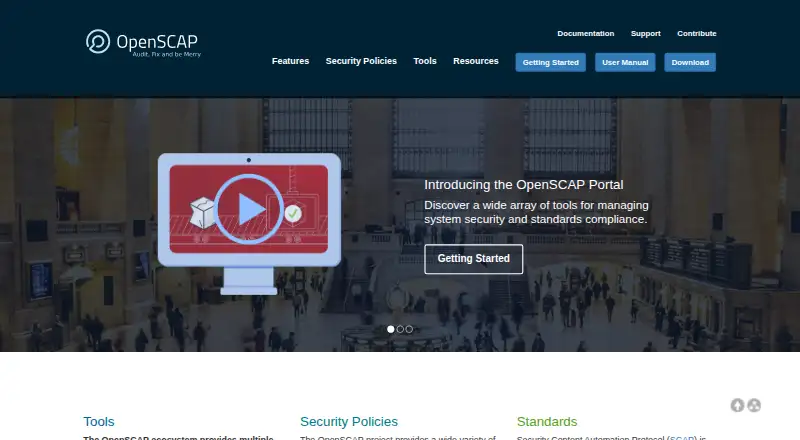
What OpenSCAP is
OpenSCAP is a collection of open-source tools for security compliance and automated vulnerability assessment using the Security Content Automation Protocol (SCAP). OpenSCAP Base includes a library and the oscap command-line tool for parsing and evaluating SCAP content, scanning systems, and producing documents. It supports XCCDF benchmarks and OVAL definitions, with SCAP 1.2 support and backward compatibility for SCAP 1.1 and 1.0. SCAP Workbench lets users customize SCAP content, run local or remote scans, and export results; OpenSCAP Daemon can schedule assessments of machines and containers. Users can adjust policy variables and rules, then save customized policies separately for reuse. Automated remediation may be available in policies, but some rules cannot be remediated automatically, and remediation can disrupt infrastructure functionality. OpenSCAP tools are free. OpenSCAP Base is available for Linux distributions including Red Hat Enterprise Linux, Fedora, and Ubuntu, and the project reports Windows support since version 1.3.0.
Good
- Free and open-source tools.
- Supports XCCDF benchmarks and OVAL definitions.
- Workbench can run local or remote scans.
- Policies can be customized and saved for reuse.
- Daemon schedules machine and container assessments.
Watch out
- Automated remediation may disrupt infrastructure.
- Not all rules can be remediated automatically.
- OpenSCAP Base's stated Windows support starts at version 1.3.0.
Who it suits
OpenSCAP suits government agencies and contractors, businesses, and open-source users seeking tools for compliance checks and vulnerability assessment. It also supports teams that need scheduled scans or customized policies.
Verdict
OpenSCAP combines SCAP content evaluation, system scanning, policy customization, and scheduled assessment in a free toolset. Consider the remediation warnings when deciding whether to apply automated fixes.
Plans and prices
From OpenSCAP's own pricing page, checked 30 Sep 2026.
| Plan | Price | What it gives you |
|---|---|---|
| OpenSCAP tools | Free | All projects under the OpenSCAP umbrella are open source and can be downloaded and used for free. |
The facts
Each one read from OpenSCAP's own pages, with the date it was checked.
What it does
- Automated remediation limit
- Security policies may include automated remediation, but the site warns that it can break infrastructure functionality and that not all rules can be remediated automatically.checked 30 Sep 2026
- Centralized management
- With Red Hat Satellite 6, the site describes centralized policy management, scheduled audits, and collection and search of audit results.checked 30 Sep 2026
- Certification
- The project says it was awarded SCAP 1.2 certification by NIST in 2014.checked 30 Sep 2026
- Compliance and vulnerability assessment
- The project provides tools and customizable policies for security compliance and automated vulnerability checking.checked 30 Sep 2026
- Container scanning
- Atomic Scan can scan containers for security vulnerabilities and compliance issues using the openscap Docker image in the official Red Hat registry.checked 30 Sep 2026
- Desktop scanning
- SCAP Workbench lets users tailor SCAP content, run local or remote scans, and export results.checked 30 Sep 2026
- Integrations
- The site lists integrations with Red Hat Satellite 6 (Foreman), Red Hat Satellite 5 (Spacewalk), RH Access Insights, Preupgrade Assistant, and orcharhino.checked 30 Sep 2026
- Intended users
- The site identifies government agencies and contractors, businesses, and the open source community as audiences for OpenSCAP.checked 30 Sep 2026
- OpenSCAP Base
- OpenSCAP Base provides a library and the oscap command-line tool to parse and evaluate SCAP content, scan systems, and format content into documents.checked 30 Sep 2026
- Policy customization
- Users can change policy variables, enable or disable rules, and save customized policies separately for reuse when the original content is updated.checked 30 Sep 2026
- Purpose
- OpenSCAP is a collection of open source tools for implementing and enforcing the Security Content Automation Protocol (SCAP) standard.checked 30 Sep 2026
- Scheduled assessment
- OpenSCAP Daemon evaluates machines and containers according to a schedule.checked 30 Sep 2026
- Supported content
- OpenSCAP Base supports XCCDF benchmarks and OVAL definitions and states support for SCAP 1.2 with backward compatibility for SCAP 1.1 and 1.0.checked 30 Sep 2026
- Supported operating systems
- OpenSCAP Base is available on Linux distributions including Red Hat Enterprise Linux, Fedora, and Ubuntu, and the site says it supports Microsoft Windows since version 1.3.0.checked 30 Sep 2026
The full review of OpenSCAP
OpenSCAP is a free, open-source toolset for applying the Security Content Automation Protocol (SCAP) to security checks. It is best suited to organizations and technical teams that need customizable compliance and vulnerability assessments across systems or containers. Its SCAP-focused toolkit is broad; automated remediation is the main reason to proceed carefully.
Overview
OpenSCAP brings together tools for evaluating security content, scanning systems, and managing policy. Its support for customizable rules and scheduled assessments can help teams make checks repeatable, while its command-line and policy-centered approach is less suited to readers looking for a single, browser-based security service.
The project identifies government agencies and contractors, businesses, and the open-source community as audiences. Its integration with Red Hat Satellite 6 adds centralized policy management, scheduled audits, and a way to collect and search audit results for teams using that platform.
Key features
OpenSCAP Base includes a library and the oscap command-line tool for parsing and evaluating SCAP content, scanning systems, and formatting content into documents. It supports XCCDF benchmarks and OVAL definitions, with SCAP 1.2 support and backward compatibility for SCAP 1.1 and 1.0. That makes it a natural fit for teams whose checks are built around those standards.
SCAP Workbench provides a desktop workflow to tailor content, run local or remote scans, and export results. Users can change policy variables, turn rules on or off, and save customized policies separately so they can reuse them when the original content is updated. OpenSCAP Daemon can assess machines and containers on a schedule, which suits teams that need recurring checks rather than one-off scans.
For container security, Atomic Scan can check containers for vulnerabilities and compliance issues using the OpenSCAP Docker image in the official Red Hat registry. The project also lists integrations with Red Hat Satellite 6, Red Hat Satellite 5, RH Access Insights, Preupgrade Assistant, and orcharhino. OpenSCAP Base is available for Linux distributions including Red Hat Enterprise Linux, Fedora, and Ubuntu, and supports Microsoft Windows since version 1.3.0. The project says it received SCAP 1.2 certification from NIST in 2014.
Automated remediation is possible when a security policy includes it, but it is not a safe universal shortcut: not every rule can be remediated automatically, and applying fixes may break infrastructure functionality. Teams should treat remediation as a change to assess, not a substitute for review.
Pricing
OpenSCAP tools cost free. The projects under the OpenSCAP umbrella are open source and can be downloaded and used for free. There is no paid OpenSCAP tier to add, so this is a strong fit for teams comfortable operating the tools themselves; organizations seeking a packaged commercial service should look elsewhere.
Platforms
The listed platforms are Linux, macOS, self-hosted, and Windows. OpenSCAP Base is specifically available on Linux distributions such as Red Hat Enterprise Linux, Fedora, and Ubuntu, and the project states Windows support from version 1.3.0. The self-hosted deployment model fits teams that want to run assessments within their own environment.
Who it's for
OpenSCAP suits government agencies, contractors, businesses, and open-source users who need SCAP-based compliance or vulnerability checks and want control over policy variables and rules. It is particularly relevant to teams already using Red Hat management tools or maintaining machines and containers that need recurring assessments. Readers who want a managed, browser-led workflow or turnkey remediation should consider another approach.
Pros and cons
- Pros: Free and open source, with tools for content evaluation, system scans, policy customization, scheduled checks, and container assessment.
- Pros: Support for XCCDF, OVAL, and SCAP 1.2 with backward compatibility can serve teams using those standards and content formats.
- Cons: The toolset centers on SCAP content and self-managed workflows, which may not suit teams seeking a hosted service.
- Cons: Automated remediation can disrupt infrastructure, and some rules cannot be fixed automatically.
Alternatives
For broader category comparisons, see Security Configuration Management Software and Infrastructure Testing Tools.
- Chef InSpec is worth considering if you want a freemium option with a free plan and trial, and support for Linux, macOS, Windows, API, and self-hosted platforms.
- Mondoo CSPM may fit better if you need scanning across cloud, Kubernetes, operating systems, SaaS, and APIs, with a free open-source tools plan.
- Qualys External Attack Surface Management is an alternative if a 30-day no-cost CSAM with EASM offer and a trial suit your evaluation.
- Kubescape is a free, self-hosted open-source option with a CLI and Kubernetes operator if your priority is Kubernetes-focused tooling.
- Lynis offers free, open-source software for Linux, macOS, and self-hosted environments, with a paid enterprise SaaS plan also available.
- Prowler Cloud has a 15-day trial with no cloud account limit and access to every check and compliance framework, alongside a free open-source plan.
- CloudSploit offers a self-hosted open-source version and a commercial hosted version.
- Tanium Deploy is a paid option for teams with the required Tanium license and Tanium Core Platform servers.
Verdict
Choose OpenSCAP if you need free, customizable SCAP-based compliance and vulnerability assessment across systems or containers, especially when scheduled checks or Red Hat integrations matter. Its open-source toolset gives technical teams room to shape policy and workflows. Look elsewhere if you need a managed service or expect automated remediation to be safe and complete without review.
Getting started
- Open the OpenSCAP website
- Choose a supported platform such as Linux, macOS, Windows, or self-hosted deployment
- Download the free OpenSCAP tools
- Select SCAP content and customize variables or rules
- Run scans with oscap or SCAP Workbench
- Schedule assessments with OpenSCAP Daemon when needed
Limits worth knowing
Automated remediation is not universal: some rules cannot be remediated automatically, and remediation actions may affect infrastructure functionality.
Questions
Is OpenSCAP free?
Yes. The OpenSCAP tools plan costs nothing, and projects under the OpenSCAP umbrella are open source and free to download and use.
Which platforms does OpenSCAP support?
The listed platforms are Linux, macOS, self-hosted, and Windows. OpenSCAP Base is available on Linux distributions including Red Hat Enterprise Linux, Fedora, and Ubuntu, with Windows support since version 1.3.0.
Can OpenSCAP scan containers?
Yes. OpenSCAP Daemon can assess containers on a schedule, and Atomic Scan uses the OpenSCAP Docker image to check containers for vulnerabilities and compliance issues.
Does OpenSCAP support policy customization?
Yes. Users can change policy variables, enable or disable rules, and save customized policies separately for reuse when original content is updated.
What integrations are available?
The project lists Red Hat Satellite 6, Red Hat Satellite 5, RH Access Insights, Preupgrade Assistant, and orcharhino integrations.
Alternatives to OpenSCAP
- 1
Chef InSpec
Free planOpen sourceAPILinuxmacOSSelf-hosted8.0From $59 a year - 2
AWS CloudFormation
Free planiOSWebAPILinux7.7Free plan - 3
CIS-CAT Pro Assessor
Free planAPILinuxmacOSSelf-hosted7.7From $2,400 a year - 4
Test Kitchen
Free planOpen sourceAPILinuxmacOSSelf-hosted7.2Free plan - 5
kube-score
Free planWebLinuxmacOSSelf-hosted7.0Free plan - 6
Conftest
Free planLinuxmacOSWindows6.8Free plan