MobSF
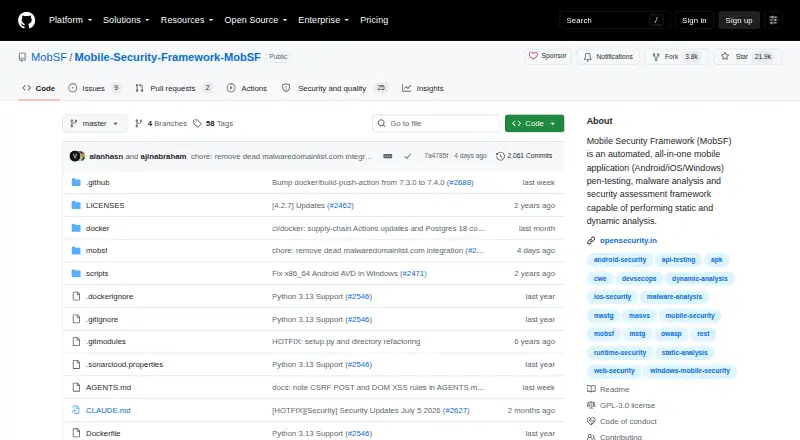
MobSF is a mobile application security research platform for penetration testing, malware analysis and privacy analysis.
What MobSF is
MobSF is a mobile application security research platform for penetration testing, malware analysis and privacy analysis. Its Static Analyzer accepts APK, IPA, APPX and source code. The Dynamic Analyzer supports Android and iOS applications, including interactive instrumented testing and analysis of runtime data and network traffic. The project also connects to DevSecOps and CI/CD pipelines through REST APIs and command-line tools, and pull request scans are supported.
MobSF can be run locally using the project’s Docker image and quick-start commands; the project also links to MobSF Static Analyzer Online at mobsf.live. The framework is open source under GPL-3.0, and its MobSF plan costs nothing. Free limited support for questions and discussions is offered through Slack, while GitHub issues are intended for bugs and feature requests. Paid support and training options are available: Professional is $2,999.99 a year, Enterprise is $6,999.99 a year, and Training is $10,999.99 a year. The listed services include priority support, troubleshooting, training, feature requests, bug fixes or consultation, depending on the plan. The project describes MobSF as made in India; OpenSecurity lists offices in Bangalore, India and Vancouver, Canada.
Good
- Static analysis supports APK, IPA, APPX and source code.
- Dynamic analysis supports Android and iOS applications.
- REST APIs and CLI tools enable DevSecOps and CI/CD integration.
- Pull request scans are supported.
- The framework is open source under GPL-3.0.
Watch out
- Paid Professional support costs $2,999.99 a year.
- Enterprise costs $6,999.99 a year.
- Training costs $10,999.99 a year.
- Free support is limited and directed to Slack.
Who it suits
MobSF suits security teams and developers assessing mobile apps through static or dynamic analysis, including teams that want CI/CD or pull request scanning. It also fits users who want a free, self-hosted GPL-3.0 framework, while organizations seeking paid support or training can consider its commercial plans.
Verdict
Pick MobSF if you need mobile app security analysis across source code or binaries, with Android and iOS dynamic analysis and pipeline integrations. Look elsewhere if you need paid support or training without the listed annual plan costs.
Plans and prices
From MobSF's own pricing page, checked 8 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| MobSF | Free | GPL-3.0 open-source framework |
| Professional | $2,999.99 a year | Live support and troubleshooting · priority email or Slack support · e-learning for 5 accounts · 1 minor feature request · priority bug fixes · $ 2999.99 / year |
| Enterprise | $6,999.99 a year | Live support and troubleshooting · priority email or Slack support · e-learning for 15 accounts · 2 major feature requests · priority bug fixes · $ 6999.99 / year |
| Training | $10,999.99 a year | Onsite or online live training · CTF challenges · $ 10999.99 / year |
The facts
Each one read from MobSF's own pages, with the date it was checked.
Where it runs
- Android analysis
- The repository describes Android as one of the supported application platforms.checked 21 Oct 2026
- iOS analysis
- The repository describes iOS as one of the supported application platforms.checked 21 Oct 2026
- Limit: app-store ratings
- The opened project repository describes a mobile app analysis framework and does not list a MobSF consumer app-store rating.checked 21 Oct 2026
- Limit: dynamic analysis device support
- The Docker guide says dynamic analysis supports rooted Android versions 4.1 through 11.0, up to API 30.checked 21 Oct 2026
What it does
- API authentication
- Configuration options include a custom API key and reading the key from a mounted file such as a Docker secret.checked 21 Oct 2026
- API-only mode
- Configuration documentation says MobSF can run in REST API-only mode with its web UI endpoints disabled.checked 21 Oct 2026
- Commercial support
- OpenSecurity lists paid MobSF support packages with priority support, live troubleshooting, feature requests, and bug fixes.checked 8 Oct 2026
- Deployment
- The project provides a Docker image and quick-start commands for running MobSF locally.checked 8 Oct 2026
- Documentation
- MobSF maintains a separate public documentation repository linked to its documentation site.checked 21 Oct 2026
- Dynamic analysis
- The project provides dynamic analysis for mobile applications.checked 21 Oct 2026
- Dynamic API
- The REST API includes endpoints for starting and stopping dynamic analysis and retrieving its report.checked 21 Oct 2026
- Independent limitation
- A Reddit commenter said MobSF's results cover only part of mobile penetration testing and that dynamic testing still requires interacting with the app.checked 21 Oct 2026
- Independent research
- A university research paper comparing mobile security tools discusses MobSF's detection results and notes that its severity classifications differed from another tool in some examples.checked 21 Oct 2026
- Independent research finding
- A research paper comparing MobSF with another analyzer reported that some findings were assigned different severity categories by the two tools.checked 21 Oct 2026
- Independent user discussion
- A Reddit commenter said MobSF and Burp were tools they would use for mobile security testing.checked 21 Oct 2026
- Integrations
- MobSF integrates with DevSecOps and CI/CD pipelines through REST APIs and CLI tools.checked 8 Oct 2026
- Licence
- The MobSF repository identifies its licence as GPL-3.0.checked 21 Oct 2026
- License
- The GitHub repository lists the project under the GPL-3.0 license.checked 8 Oct 2026
- Limit: review-site ratings
- The opened G2 and Capterra search results did not provide a MobSF rating or review count.checked 21 Oct 2026
- Online access
- The project links to MobSF Static Analyzer Online at mobsf.live.checked 8 Oct 2026
The company
- Company
- OpenSecurity describes itself as providing penetration testing, security engineering, training, and research, and lists MobSF among its tools.checked 21 Oct 2026
- Company location
- OpenSecurity's homepage names Bangalore and Vancouver in its page title and describes its security services.checked 21 Oct 2026
- Headquarters
- Bangalore, India; Vancouver, Canadachecked 28 Sep 2026
- Maker location
- The project describes MobSF as made in India, and OpenSecurity lists offices in Bangalore, India and Vancouver, Canada.checked 8 Oct 2026
The full review of MobSF
MobSF is a mobile application security research framework for penetration testing, malware analysis and privacy analysis. It suits teams assessing mobile apps across source code and binaries.
Overview
MobSF is a focused choice for Android and iOS security work, not a general-purpose code security platform. The free, GPL-3.0 framework can run locally, making it a practical fit for teams comfortable managing their own analysis environment.
Key features
The Static Analyzer covers APK, IPA and APPX files alongside source code, so teams can assess different mobile app inputs in one framework. The Dynamic Analyzer adds interactive instrumented testing for Android and iOS, including runtime data and network traffic analysis. That pairing makes MobSF more useful for mobile investigations where observed app behavior matters as well as code; its focus is mobile applications rather than security analysis across every software category.
REST APIs and CLI tools connect MobSF to DevSecOps and CI/CD pipelines, and the project supports pull request scans. A Docker image and quick-start commands offer a route to local deployment; the project also links to MobSF Static Analyzer Online at mobsf.live. The repository links to a security policy.
Slack is the channel for questions, help and discussion, while GitHub issues are for bugs and feature requests. Free Slack support is limited, so teams needing priority responses or live troubleshooting should weigh the paid packages.
Pricing
MobSF costs nothing and provides the GPL-3.0 open-source framework. It is the clear starting point for individuals and teams able to run the tool and rely on limited community help.
Professional costs $2,999.99 a year, billed $ 2999.99 / year. It adds live support and troubleshooting, priority support by email or Slack, an e-learning course for 5 accounts, 1 minor feature request and priority bug fixes. This fits a small team that wants responsive help without moving to the larger Enterprise training allowance.
Enterprise costs $6,999.99 a year, billed $ 6999.99 / year. It includes the same live and priority support, an e-learning course for 15 accounts, 2 major feature requests and priority bug fixes. The higher cost is aimed at organizations that need broader training access and more substantial feature requests.
Training costs $10,999.99 a year. It includes onsite or online live training, CTF challenges, CI/CD setup assistance, an e-learning course for 50 accounts and expert email consultation. Choose it for structured instruction and pipeline setup; it is difficult to justify if all that is needed is the analysis framework itself.
Platforms
MobSF supports API, Linux, macOS, self-hosted, web and Windows platforms. Its Docker image and local quick-start route make self-hosting a concrete option for teams that want to operate the framework themselves.
Who it's for
MobSF is best for mobile security researchers and development teams that need static and dynamic analysis across Android and iOS apps, plus pipeline integration.
Pros and cons
- Pros: Static analysis covers source code and APK, IPA and APPX binaries, while dynamic analysis covers Android and iOS behavior.
- Pros: REST APIs, CLI tools and pull request scans support CI/CD workflows.
- Pros: The GPL-3.0 framework is free, with Docker and quick-start commands for local use.
- Cons: Free support is limited to Slack; bug reports and feature requests use GitHub issues, not a priority support channel.
- Cons: Paid plans are annual commitments, starting at $2,999.99 a year for professional support and training.
Alternatives
For a broader shortlist, see SAST Tools. Snyk Open Source is worth considering if a freemium option and a free plan capped at 5 projects for Snyk Open Source (SCA) better match the need. Semgrep Code is another free-plan option, with its Free Edition capped at 10 repositories and 10 contributors. NaiveSystems Analyze offers a freemium alternative with some open-source components, including an on-premises analysis runner.
NodeJsScan, Flawfinder, Bandit, gosec and Security Code Scan are also alternatives to consider.
Verdict
Choose MobSF if you need mobile app security analysis spanning source code, binaries and runtime behavior, with CI/CD integration and a free open-source framework. Look elsewhere if your work is not centered on mobile apps, or if you need live support and training without committing to an annual paid plan.
Getting started
- Visit the MobSF GitHub project.
- Run MobSF locally using the provided Docker image or quick-start commands.
- Use MobSF Static Analyzer Online at mobsf.live for online access.
- Connect REST APIs or CLI tools to a DevSecOps or CI/CD pipeline if needed.
- Use Slack for support questions and discussions; report bugs and feature requests through GitHub issues.
Questions
Is MobSF free?
The MobSF plan costs nothing and is an open-source framework under GPL-3.0.
Which file types can its Static Analyzer handle?
It supports APK, IPA, APPX and source code.
Which mobile platforms does Dynamic Analyzer support?
It supports Android and iOS applications, including interactive instrumented testing and runtime data and network traffic analysis.
Can MobSF be used in CI/CD pipelines?
Yes. It integrates with DevSecOps and CI/CD pipelines through REST APIs and CLI tools, and supports pull request scans.
What paid options are available?
Professional costs $2,999.99 a year, Enterprise costs $6,999.99 a year, and Training costs $10,999.99 a year.
Where can users get help?
Free limited help for questions and discussions is offered through Slack. GitHub issues are for bugs and feature requests.
Alternatives to MobSF
- 1
Semgrep Code
Free planOpen sourceWebAPIExtensionLinux8.3From $15 a month - 2

GitHub CodeQL
Free planWebExtensionLinuxmacOS7.5From $30 a month - 3
Bandit
Free planOpen sourceExtensionLinuxmacOSSelf-hosted7.2Free plan - 4
gosec
Free planOpen sourceAPILinuxmacOSSelf-hosted7.2Free plan - 5
NaiveSystems Analyze
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.2Free plan - 6
Kiuwan Code Security
WebAPILinuxmacOS6.8From $49 a month