gosec
gosec is a free security checker that scans Go source code for potential problems.
What gosec is
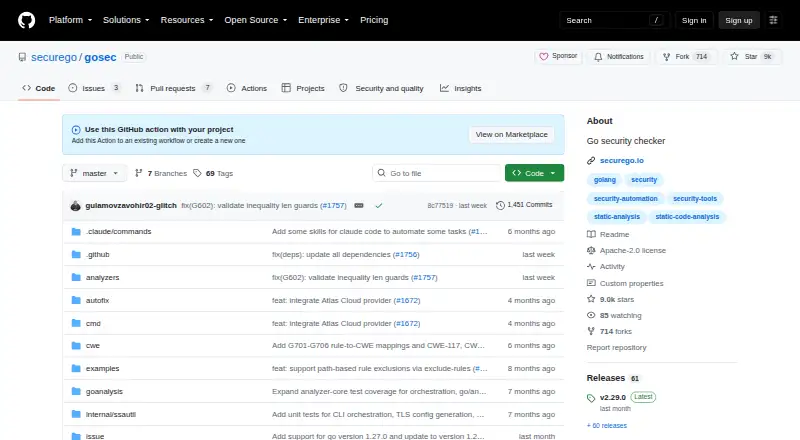
gosec is a free security checker that scans Go source code for potential problems. It analyzes the abstract syntax tree and static single assignment representation, applying pattern-based rules, SSA analyzers, and taint analysis. Checks cover risks such as injection, path traversal, SSRF, and unsafe deserialization, alongside secure coding, file handling, crypto and TLS, blocklisted imports, and Go-specific rules. Each detected issue maps to a Common Weakness Enumeration entry. Users can select or exclude rules, set path-based exclusions, and adjust global settings such as audit mode. Reports can be produced as text, JSON, YAML, CSV, JUnit XML, HTML, SonarQube, golint, and SARIF. The project documents GitHub Actions use and SARIF uploads to GitHub code scanning; its goanalysis package supports compatible tools such as Bazel nogo. Local installation requires Go 1.25 or newer. An optional AI feature can suggest vulnerability fixes through listed providers or custom OpenAI-compatible APIs. Automated detection can produce false positives, which annotations can suppress when findings are verified safe.
Good
- Checks include taint analysis and SSA analyzers.
- Supports rule selection and path-based exclusions.
- Offers reports in formats including SARIF and JUnit XML.
- Documents GitHub Actions and GitHub code scanning integration.
- Maps detected issues to CWE entries.
Watch out
- Local installation requires Go 1.25 or newer.
- Automated detection can produce false positives.
- Free trial is not offered.
Who it suits
gosec is for Go developers and teams who want source-code security checks in local workflows or CI. It also suits teams that need configurable rules and machine-readable reports.
Verdict
gosec provides configurable security analysis for Go code, with multiple report formats and CI integration options. Users should verify findings because automated checks can produce false positives, and local installation requires Go 1.25 or newer.
Plans and prices
From gosec's own pricing page, checked 7 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| gosec | Free | Open source Go security checker · Apache License 2.0 |
The facts
Each one read from gosec's own pages, with the date it was checked.
What it does
- AI providers
- Documented providers include Atlas Cloud, Gemini, Claude, OpenAI and arbitrary OpenAI-compatible endpoints such as Azure OpenAI, LocalAI and Ollama.checked 21 Oct 2026
- AI remediation
- An optional autofix mode calls an AI API to suggest fixes for findings.checked 21 Oct 2026
- AI suggestions
- An optional feature can suggest vulnerability fixes by calling an AI API, with providers including Atlas Cloud, Gemini, Claude, OpenAI, and custom OpenAI-compatible APIs.checked 7 Oct 2026
- Bazel integration
- The goanalysis package exposes a golang.org/x/tools/go/analysis Analyzer usable by Bazel nogo.checked 21 Oct 2026
- CI integration
- The project supplies an official GitHub Action for scanning repositories in workflows.checked 21 Oct 2026
- Community
- The Secure Go site links to project guidelines, tools, a community Slack, Stack Overflow, and a blog.checked 7 Oct 2026
- Configuration
- A JSON configuration file supports global settings such as audit mode and suppression behavior.checked 21 Oct 2026
- Dependencies
- gosec loads packages using Go modules and says dependencies are resolved automatically in most projects.checked 7 Oct 2026
- Detection
- It includes pattern-based rules, SSA analyzers, and taint analysis for risks such as injection, path traversal, SSRF, and unsafe deserialization.checked 7 Oct 2026
- Documentation depth
- Secure Go publishes per-rule guidance pages and links to API reference, Stack Overflow and Slack support channels.checked 21 Oct 2026
- Exit behavior
- Exit code 0 means no unsuppressed findings or processing errors; code 1 indicates at least one finding or processing error, while -no-fail forces 0.checked 21 Oct 2026
- False positives
- The documentation says automated detection can produce false positives and supports code annotations to suppress verified safe findings.checked 7 Oct 2026
- GitHub code scanning
- SARIF results can be uploaded through GitHub's upload-sarif action for code-scanning findings.checked 21 Oct 2026
- Independent description
- DEV.co describes gosec as a Go static analyzer using pattern matching, control-flow analysis and taint tracking with SARIF support.checked 21 Oct 2026
- Independent feature summary
- AppSec Santa reports more than 50 CWE-mapped rules covering credentials, injection, cryptography, filesystem, network and memory issues.checked 21 Oct 2026
- Independent installation example
- Google's Secure Source Code codelab installs gosec 2.15.0 with the project's install script and runs it with a policy file.checked 21 Oct 2026
- Independent praise: deployment
- AppSec Santa praises that the core scanner runs locally through Go modules without a hosted control plane or build server.checked 21 Oct 2026
- License
- The repository states that gosec is licensed under Apache License 2.0.checked 7 Oct 2026
- Limit: coverage scope
- AppSec Santa says gosec does not exercise a running application, validate exploitability, model authorization logic or replace dependency scanning and secret rotation.checked 21 Oct 2026
- Limit: false positives
- A 2026 NDSS study found gosec had the broadest coverage among evaluated tools but also the highest noise, with 68 findings comprising 31 true positives and 37 false positives (45.59% precision).checked 21 Oct 2026
- Limit: language scope
- AppSec Santa says gosec analyzes Go only, so mixed-language repositories need other scanners for languages, infrastructure and containers.checked 21 Oct 2026
- Limit: recurring false positives
- The NDSS study reports that many integer-conversion and weak-cryptography findings were false positives after contextual review.checked 21 Oct 2026
- Local installation
- The documented installation command is go install github.com/securego/gosec/v2/cmd/gosec@latest.checked 21 Oct 2026
Where it runs
- CWE mapping
- Each detected issue is mapped to a Common Weakness Enumeration identifier.checked 21 Oct 2026
Alternatives to gosec
- 1
DeepSource
Free planWebAPILinuxmacOS8.0From $30 a month - 2
Qodana
Free planWebAPIExtensionLinux7.9From $5 a month - 3

GitHub CodeQL
Free planWebExtensionLinuxmacOS7.5From $30 a month - 4
Cppcheck
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.4Free plan - 5

Gitar
Free planWebAPISelf-hosted7.2From $20 a month - 6
Understand
APIExtensionLinuxmacOS7.2From $100 a month