Security Code Scan
Security Code Scan is a free, open-source static analyzer for .NET code written in C# and VB.NET.
What Security Code Scan is
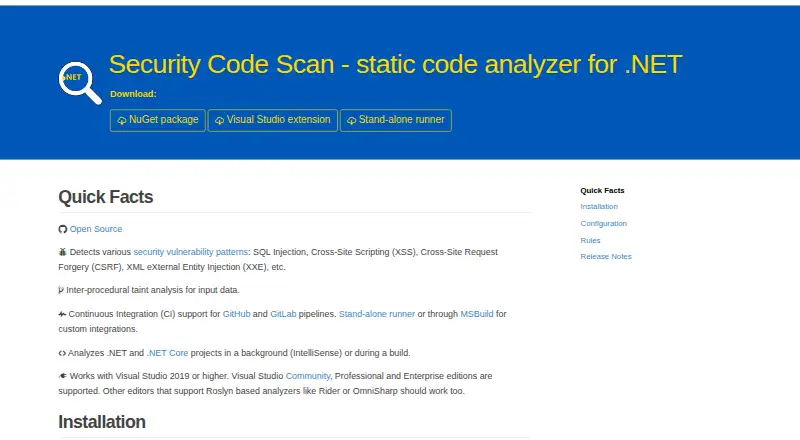
Security Code Scan is a free, open-source static analyzer for .NET code written in C# and VB.NET. It detects vulnerability patterns such as SQL injection, cross-site scripting, CSRF, and XML external entity injection, using inter-procedural taint analysis to follow input data. It can analyze projects in the background as IntelliSense or during a build. For automated workflows, it supports GitHub and GitLab pipelines, MSBuild, and a stand-alone runner for custom integrations. Custom integrations can produce SARIF results and display warnings alongside other build messages. Users can configure taint sources, sinks, sanitizers, validators, and project-specific settings. The analyzer supports Visual Studio 2019 or later; the project says other Roslyn analyzer editors, including Rider and OmniSharp, should work. It is available as a NuGet package, a Visual Studio extension, and a stand-alone runner, and supports Windows and Linux. The maker recommends CI/CD integrations as the more common use case and warns that the Visual Studio extension or NuGet package can slow the IDE because of extensive analysis. The repository identifies the license as LGPL-3.0.
Good
- Analyzes C# and VB.NET vulnerability patterns.
- Supports GitHub and GitLab pipelines, MSBuild, and custom runners.
- Allows configuration of taint sources, sinks, and sanitizers.
- Can return SARIF results for custom integrations.
Watch out
- The Visual Studio extension or NuGet package can slow the IDE.
- Audit mode can add warnings when enabled.
- Automated fixes are not provided.
Who it suits
Security Code Scan suits .NET developers who want vulnerability-pattern analysis during coding or in CI/CD pipelines. Teams can also tailor taint analysis settings to project needs.
Verdict
Security Code Scan offers configurable static analysis for .NET projects and multiple ways to include it in development workflows. Its maker’s CI/CD recommendation is worth considering if IDE performance is a concern.
Plans and prices
From Security Code Scan's own pricing page, checked 9 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Security Code Scan | Free | Open source static analyzer for .NET |
The facts
Each one read from Security Code Scan's own pages, with the date it was checked.
What it does
- CI recommendation
- The maker says CI/CD is the more common use case and recommends pipeline integrations for that use.checked 9 Oct 2026
- Customization
- Users can configure custom taint sources, sinks, sanitizers, validators, and project-specific settings.checked 9 Oct 2026
- Detection
- It detects patterns including SQL injection, cross-site scripting, CSRF, and XML external entity injection.checked 9 Oct 2026
- Downloads
- Official releases are offered as a NuGet package, a Visual Studio extension, and a stand-alone runner.checked 9 Oct 2026
- Editors
- It supports Visual Studio 2019 or higher and says other Roslyn analyzer editors such as Rider or OmniSharp should work.checked 9 Oct 2026
- Integrations
- The site lists GitHub and GitLab pipeline support, plus MSBuild and a stand-alone runner for custom integrations.checked 9 Oct 2026
- License
- The project repository identifies its license as LGPL-3.0.checked 9 Oct 2026
- Limitations
- Audit mode is off by default and can produce more warnings about data with unknown taint state when enabled.checked 9 Oct 2026
- Performance
- The maker warns that installing it as a Visual Studio extension or NuGet package can slow the IDE because it performs extensive static analysis.checked 9 Oct 2026
- Purpose
- Security Code Scan is a static code analyzer for .NET that detects vulnerability patterns in C# and VB.NET.checked 9 Oct 2026
- Results
- For custom integrations, it can produce SARIF results and show warnings alongside other build messages.checked 9 Oct 2026
- Support
- The maker provides a troubleshooting guide and directs users to project issues and contributions on GitHub.checked 9 Oct 2026
- Taint analysis
- The analyzer performs inter-procedural taint analysis for input data.checked 9 Oct 2026
- Usage
- It analyzes projects in the background as IntelliSense or during a build.checked 9 Oct 2026
Alternatives to Security Code Scan
- 1
Semgrep Code
Free planOpen sourceWebAPIExtensionLinux8.3From $15 a month - 2
MobSF
Free planOpen sourceWebAPILinuxmacOS8.2From $2,999.99 a year - 3

GitHub CodeQL
Free planWebExtensionLinuxmacOS7.5From $30 a month - 4
Bandit
Free planOpen sourceExtensionLinuxmacOSSelf-hosted7.2Free plan - 5
gosec
Free planOpen sourceAPILinuxmacOSSelf-hosted7.2Free plan - 6
NaiveSystems Analyze
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.2Free plan