Coverity Scan
Coverity Scan is a free cloud static-analysis service for registered open source projects.
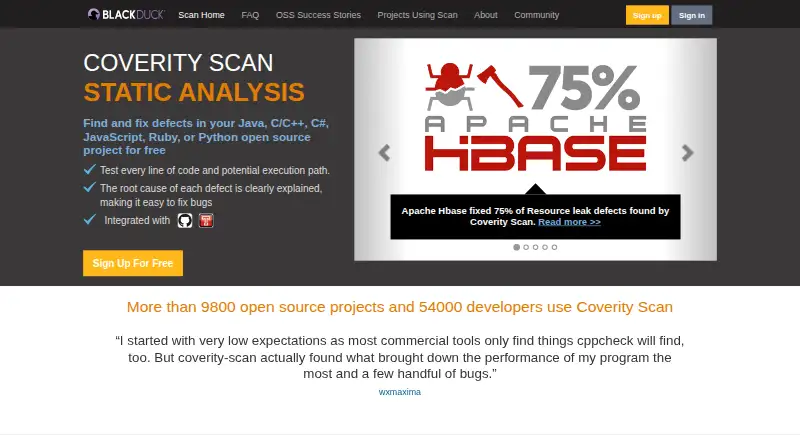
What Coverity Scan is
Coverity Scan is a free cloud static-analysis service for registered open source projects. It examines source code without running it and follows possible execution paths to identify defects such as resource leaks, null pointer dereferences, memory corruption, buffer overruns, concurrency problems, and insecure data handling. Each reported defect includes an explanation of its root cause to guide fixes. Listed languages are Java, C, C++, C#, JavaScript, Ruby, and Python. Users can sign in with GitHub and import projects, while the sign-in page describes Travis CI build automation. Registered Eclipse Foundation projects can use a plugin on a Hudson server to send build and source-control information for cloud analysis. Eligibility is restricted to registered open source projects, with possible approval for projects maintained by for-profit corporations at Black Duck’s discretion. Detailed results are generally limited to approved project members. Build allowances vary by project size, and only the latest two tool releases are supported.
Good
- Free plan for registered open source projects
- Static analysis follows possible execution paths
- Explains each defect’s root cause
- Supports seven listed programming languages
- GitHub and Travis CI workflows
Watch out
- Eligibility limited to registered open source projects
- Build limits vary by project size
- Only latest two tool releases supported
- Detailed results restricted to approved members
Who it suits
Coverity Scan suits maintainers of registered open source projects who need cloud static analysis across its listed languages. Eclipse Foundation projects and GitHub-based teams may benefit from the documented integrations.
Verdict
Coverity Scan provides source-code defect analysis and integrations for qualifying open source projects. Confirm eligibility and build allowances before planning frequent scans or private project use.
Plans and prices
From Coverity Scan's own pricing page, checked 7 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Coverity Scan | Free | Registered open source projects only · Build frequency varies by project size |
The facts
Each one read from Coverity Scan's own pages, with the date it was checked.
What it does
- Analysis
- Its static analysis examines source code without executing it and can follow possible execution paths through the code.checked 7 Oct 2026
- Build limits
- Weekly build limits range from 7 to 28 per project depending on lines of code, with daily limits from 1 to 4; excess weekly requests are rejected.checked 7 Oct 2026
- Defects
- Examples of issues it finds include resource leaks, null pointer dereferences, memory corruption, buffer overruns, concurrency issues, and insecure data handling.checked 7 Oct 2026
- Eclipse integration
- Registered Eclipse Foundation projects can use a Coverity Scan plugin on a Hudson server to send build and source control information for cloud analysis.checked 7 Oct 2026
- Eligibility
- Use is limited to registered open source projects, though projects initiated and maintained by for-profit corporations may be approved at Black Duck's discretion.checked 7 Oct 2026
- GitHub
- Users can sign in with GitHub and import GitHub projects for analysis.checked 7 Oct 2026
- Languages
- The site lists Java, C/C++, C#, JavaScript, Ruby, and Python as supported languages.checked 7 Oct 2026
- Project access
- Access to detailed results is generally limited to project members approved by the project administrator, and the service follows responsible disclosure.checked 7 Oct 2026
- Purpose
- Coverity Scan provides static analysis results for registered open source projects.checked 7 Oct 2026
- Results
- The site says the root cause of each defect is explained to help developers fix bugs.checked 7 Oct 2026
- Support policy
- The site says only the latest two tool releases are supported and projects should expect to update approximately once a year or more often.checked 7 Oct 2026
- Travis CI
- The sign-in page says users can automate Coverity Scan builds with Travis CI.checked 7 Oct 2026
- Upload API
- The site announced a new API endpoint for uploading builds larger than the previous 500 MB request limit.checked 7 Oct 2026
The company
- Founded
- 2006checked 28 Sep 2026
Alternatives to Coverity Scan
- 1
DeepSource
Free planWebAPILinuxmacOS8.0From $30 a month - 2
Qodana
Free planWebAPIExtensionLinux7.9From $5 a month - 3

GitHub CodeQL
Free planWebExtensionLinuxmacOS7.5From $30 a month - 4
Cppcheck
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.4Free plan - 5

Gitar
Free planWebAPISelf-hosted7.2From $20 a month - 6
gosec
Free planOpen sourceAPILinuxmacOSSelf-hosted7.2Free plan