42Crunch API Security Platform
42Crunch provides API security testing and runtime protection, and applies contract-driven governance to MCP servers used by AI agents.
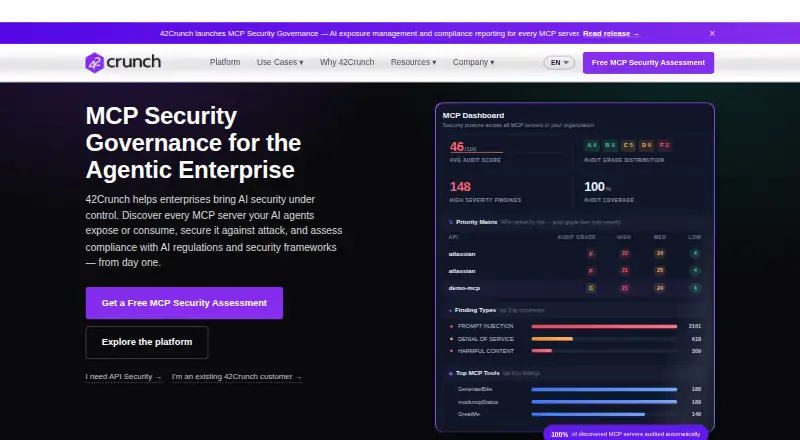
What 42Crunch API Security Platform is
42Crunch provides API security testing and runtime protection, and applies contract-driven governance to MCP servers used by AI agents. Its API tests are generated from OpenAPI definitions and map findings to the OWASP API Security Top 10. A runtime micro-firewall builds an allowlist from an API contract and blocks traffic not declared there, with stated sub-millisecond overhead. For MCP, the platform finds servers across registries, gateways, and repositories, then generates contracts for their advertised tools, resources, and prompts. It maps MCP security findings to NIST AI RMF, OWASP MCP Top 10, EU AI Act, ISO/IEC 42001, and CSA AICM controls. Integrations and CI/CD support span development environments, build services, and tools such as Kubernetes, Docker, Postman, and MuleSoft. Enterprise deployment options are cloud, on-premises, and hybrid. A free plan is listed; Individual costs $9 per month and Individual Pro costs $20 per month. A 14-day trial requires a corporate email and no credit card. The CI/CD documentation says GraphQL federation is unsupported in that integration, and Jenkins instructions say GraphQL scanning requires a separate subscription.
Good
- Generates API tests from OpenAPI definitions.
- Maps API findings to the OWASP API Security Top 10.
- Finds MCP servers and generates contracts for advertised capabilities.
- Offers cloud, on-premises, and hybrid deployment.
- Free plan and 14-day trial are listed.
Watch out
- GraphQL federation is unsupported in CI/CD integration.
- Jenkins GraphQL scanning requires a separate subscription.
- Trial signup requires a corporate email.
Who it suits
It suits teams securing APIs through OpenAPI-based testing and runtime traffic controls, as well as organizations governing MCP servers used by AI agents. Enterprise teams can choose cloud, on-premises, or hybrid deployment.
Verdict
42Crunch combines contract-based API testing with runtime protection and MCP governance. Teams using GraphQL should note the stated CI/CD limitation and separate Jenkins scanning subscription requirement.
Plans and prices
From 42Crunch API Security Platform's own pricing page, checked 14 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Starter | Free | Single user · API SAST & DAST · vulnerability and identity scans · default quality gate · IDE integration · community support · 14 days |
| Free | Free | AI coding plugin · OpenAPI audit · vulnerability scans · automatic fixes · enough tokens to try the product |
| Individual | $9 a month | 1,000 security tokens/month · 1 user · API SAST & DAST · vulnerability and identity scans · IDE integration · email support · monthly or annually |
| Individual Pro | $20 a month | 3,000 security tokens/month · 1 user · API SAST & DAST · vulnerability and identity scans · IDE integration · email support · monthly or annually |
| Team 10 | $349 a month | Up to 10 users · up to 250 endpoints · unlimited tokens · shared API workspace · drift scans · customizable dictionaries and quality gates · $3,560 annually |
| Team 25 | $599 a month | 11–25 users · up to 1,000 endpoints · unlimited tokens · shared API workspace · drift scans · customizable dictionaries and quality gates · $6,000 annually |
| Enterprise API Security Platform | Priced on request | Unlimited tokens · runtime threat protection · Secure MCP Server · CI/CD, gateway and SIEM/SOC integrations · SSO and audit logs · dedicated encrypted tenant · dedicated support manager |
| Enterprise | Priced on request | Scoped to APIs, MCP servers, and users · dedicated encrypted tenant · SSO · unlimited context · dedicated support manager · cloud, on-prem, or hybrid |
The facts
Each one read from 42Crunch API Security Platform's own pages, with the date it was checked.
What it does
- API formats
- The platform supports OpenAPI 2, 3.0 and 3.1 definitions in JSON or YAML.checked 14 Oct 2026
- API testing
- Its API security testing uses static and dynamic tests generated from OpenAPI definitions and maps findings to the OWASP API Security Top 10.checked 30 Sep 2026
- Audit coverage
- The audit checks more than 200 contract structure, semantics, security and data-definition conditions.checked 14 Oct 2026
- CI/CD quality gates
- Audit and Scan can run as Security Quality Gates that fail a pipeline when an API is non-conforming.checked 14 Oct 2026
- CI/CD support
- The platform's CI/CD documentation lists Azure Pipelines, Bamboo, Bitbucket Pipelines, GitHub Actions, GitLab Pipelines, Jenkins, Tekton, and a generic Docker image for REST API static security testing.checked 30 Sep 2026
- Compliance
- The platform maps MCP security findings to NIST AI RMF, OWASP MCP Top 10, EU AI Act, ISO/IEC 42001, and CSA AICM controls.checked 30 Sep 2026
- Component licences
- GitHub lists the vscode-openapi and scan-manager repositories under AGPL-3.0 and the API security audit action under Apache-2.0.checked 14 Oct 2026
- Deployment
- Enterprise deployment options listed by the maker are cloud, on-premises, and hybrid.checked 30 Sep 2026
- Documentation
- The documentation site covers audit, scan, protection, integrations, tasks, concepts, support material and release notes.checked 14 Oct 2026
- Dynamic scan
- API Scan generates traffic against a live endpoint to test implementation conformance and security.checked 14 Oct 2026
- Editor capabilities
- The editor provides IntelliSense, linting, navigation, schema enforcement, SwaggerUI or ReDoc preview, snippets and Try-it execution.checked 14 Oct 2026
- GraphQL support
- GraphQL schema files are supported, but introspection files are not and GraphQL requires a separate subscription.checked 14 Oct 2026
- IDE support
- The free OpenAPI editor supports VS Code, IntelliJ-based IDEs and Eclipse, with Visual Studio Enterprise support added in 2026.checked 14 Oct 2026
- Independent pricing criticism
- FAUN.dev scored pricing transparency low and said team or enterprise use requires a sales-sized subscription.checked 14 Oct 2026
- Integrations
- Documented integrations include CI/CD plugins, IDE extensions, SonarQube and a Postman collection.checked 14 Oct 2026
- Latest release
- The September 30, 2026 release added MCP security governance in platform version 1.60.x.checked 14 Oct 2026
- Limit: setup complexity
- Reviewers report setup and pipeline troubleshooting friction, a learning curve for advanced features and limited report or policy customization.checked 14 Oct 2026
- Limit: specification dependence
- Reviewers say incomplete or outdated OpenAPI contracts reduce the effectiveness of audits, scans and runtime protection.checked 14 Oct 2026
- Local scanning
- The free API Scan mode runs locally and does not upload the API file to 42Crunch.checked 14 Oct 2026
The company
- Company
- The current website identifies the company as 42Crunch Ltd. and its leadership page names Jacques Declas and Philippe Leothaud as co-founders.checked 30 Sep 2026
- Company founding and headquarters
- LinkedIn lists the company as founded in 2016 and headquartered in Dublin.checked 14 Oct 2026
- Company size
- LinkedIn lists 42Crunch as a privately held company with 51–200 employees.checked 14 Oct 2026
- Funding and ownership
- Crunchbase describes 42Crunch as private, Series A, headquartered in London, with Adara Ventures and Energy Impact Partners among its investors.checked 14 Oct 2026
- Headquarters
- London, United Kingdomchecked 28 Sep 2026
The full review of 42Crunch API Security Platform
Overview
42Crunch API Security Platform combines API security testing with runtime protection. Its approach centers on API contracts: OpenAPI definitions drive security checks, while the contract also informs runtime traffic controls. The platform extends this contract-based governance to MCP servers used by AI agents.
Its listed capabilities include API discovery, API posture management, sensitive data detection, and specification governance. For APIs, it generates static and dynamic tests from OpenAPI definitions and maps findings to the OWASP API Security Top 10. At runtime, a micro-firewall builds an allowlist from the API contract and blocks traffic that is not declared there; 42Crunch states that this operates with sub-millisecond overhead.
For MCP, the platform discovers servers across registries, gateways, and repositories, then generates contracts for their advertised tools, resources, and prompts. Security findings can be mapped to NIST AI RMF, OWASP MCP Top 10, the EU AI Act, ISO/IEC 42001, and CSA AICM controls.
Key features
- OpenAPI-based security testing: Static and dynamic tests use API definitions as their basis, with findings organized against the OWASP API Security Top 10.
- Runtime micro-firewall: Contract-derived allowlisting is used to block undeclared traffic. The stated overhead is sub-millisecond.
- MCP server discovery: The platform searches registries, gateways, and repositories for MCP servers and creates contracts covering their advertised tools, resources, and prompts.
- MCP compliance mapping: Findings can be related to a range of AI, security, and governance frameworks, including NIST AI RMF, the EU AI Act, and ISO/IEC 42001.
- Development workflow integrations: Named technology partners include Visual Studio Code, IntelliJ, Eclipse, Bitbucket, Bamboo, GitHub, GitLab, Jenkins, Microsoft Azure, Azure Sentinel, SonarQube, Kubernetes, Docker, Postman, and MuleSoft.
- Security and privacy commitments: 42Crunch says it is ISO/IEC 27001 certified, with controls covering areas such as risk assessment, access, encryption, monitoring, and business continuity. It also says it commits to applicable privacy laws including GDPR, CCPA, UK GDPR, and Australia's APPs.
Pricing
42Crunch offers a free plan, paid individual plans, and enterprise pricing on request. The free trial lasts 14 days, requires a corporate email address, and does not require a credit card.
| Plan | Price | Included |
|---|---|---|
| Free | free | AI coding plugin, OpenAPI audit, vulnerability scans, automatic fixes, and enough tokens to try the product. |
| Individual | $9 a month (billed $9 / month) | 1,000 security tokens/month, 1 user, coding agents, API scans, IDE integration, email support, and extra tokens at +$0.03 per token. |
| Individual Pro | $20 a month (billed $20 / month) | 3,000 security tokens/month, 1 user, coding agents, API scans, IDE integration, community support, and extra tokens at +$0.025 per token. |
| Enterprise | Price not listed | Scoped to APIs, MCP servers, and users; dedicated encrypted tenant, SSO, unlimited context, dedicated support manager, and cloud, on-premises, or hybrid deployment. |
Platforms
Listed platforms are API, extension, Linux, macOS, self-hosted, web, and Windows. Enterprise deployment options include cloud, on-premises, and hybrid.
CI/CD documentation names Azure Pipelines, Bamboo, Bitbucket Pipelines, GitHub Actions, GitLab Pipelines, Jenkins, and Tekton, as well as a generic Docker image for REST API static security testing. IDE integration documentation names Visual Studio Code, JetBrains IDEs, Eclipse, and Microsoft Visual Studio.
There are specific GraphQL constraints to note: GraphQL federation is not supported in CI/CD integration, and Jenkins instructions say GraphQL scanning requires a separate subscription.
Who it's for
42Crunch is aimed at teams that define APIs with OpenAPI and want security checks tied to those definitions, along with runtime controls based on the same contracts. Its MCP discovery and governance features may also suit organizations overseeing MCP servers used by AI agents. The plan structure ranges from a free option and single-user subscriptions to enterprise deployments scoped to APIs, MCP servers, and users.
Pros and cons
Pros
- OpenAPI definitions inform both generated security tests and runtime allowlisting.
- Findings map to named API and AI governance frameworks.
- CI/CD and IDE integrations cover several commonly used development tools.
- Enterprise deployment choices include cloud, on-premises, and hybrid.
- The trial is 14 days and does not require a credit card.
Cons
- Enterprise pricing is not listed.
- GraphQL federation is not supported in CI/CD integration.
- GraphQL scanning in Jenkins requires a separate subscription.
- Support varies by plan: email for Individual, community support for Individual Pro, and a dedicated support manager for enterprise pricing.
Alternatives
Other products to consider include Akto API Security Platform, Wallarm API Security, APISec Platform, F5 BIG-IP APM, Palo Alto Networks Cortex Cloud API Security, Cisco Panoptica, APIPosture, and Onam Security API Security.
Verdict
42Crunch stands out for linking OpenAPI-based testing and runtime traffic controls, while extending contract governance to MCP server discovery. The listed free and individual plans provide clear entry points, although enterprise pricing is undisclosed. Teams with GraphQL workflows should account for the stated CI/CD and Jenkins limitations.
Explore the API Security Software and API Security Testing Software categories for more options.
Getting started
- Visit https://42crunch.com/.
- Use the free plan or choose Individual at $9.00 per month or Individual Pro at $20.00 per month.
- For the 14-day trial, sign up with a corporate email; no credit card is required.
- Use a supported IDE, such as Visual Studio Code, JetBrains IDEs, Eclipse, or Microsoft Visual Studio.
- Connect through a listed CI/CD option such as GitHub Actions, GitLab Pipelines, Jenkins, or Azure Pipelines.
Limits worth knowing
The free plan provides enough tokens to try the product. Individual includes 1,000 security tokens per month for one user, with extra tokens at $0.03 each. Individual Pro includes 3,000 per month for one user, with extra tokens at $0.025 each.
Questions
Is there a free plan?
Yes. The Free plan includes an AI coding plugin, OpenAPI audit, vulnerability scans, automatic fixes, and enough tokens to try the product.
How much do the individual plans cost?
Individual costs $9.00 per month. Individual Pro costs $20.00 per month.
How long is the free trial?
The trial lasts 14 days, requires a corporate email, and does not require a credit card.
Which platforms are supported?
The listed platforms are API, extension, Linux, macOS, self-hosted, web, and Windows.
Can it be deployed on-premises?
Enterprise deployment options include cloud, on-premises, and hybrid.
Which tools does it integrate with?
Listed technology partners include Visual Studio Code, IntelliJ, Eclipse, GitHub, GitLab, Jenkins, Kubernetes, Docker, Postman, and MuleSoft. CI/CD documentation also names Azure Pipelines, GitHub Actions, GitLab Pipelines, Jenkins, and other options.
Alternatives to 42Crunch API Security Platform
- 1
APIPosture
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.8From $9 a month - 2
Onam Security API Security
Free planWebAPILinuxmacOS7.8From $22 a month - 3
APISec Platform
Free planWebAPIExtensionLinux7.5From $690 a month - 4

DataDome API Protection
AndroidiOSWebAPI6.8From $3,830 a month - 5
Haltdos
Free planWebAPILinuxSelf-hosted6.8From $30 a month - 6
apPosture API Security
WebAPILinuxSelf-hosted6.7From $35 a month