Onam Security API Security
Onam Security API Security discovers API endpoints across cloud environments and checks their configurations against 241 application and API security rules.
What Onam Security API Security is
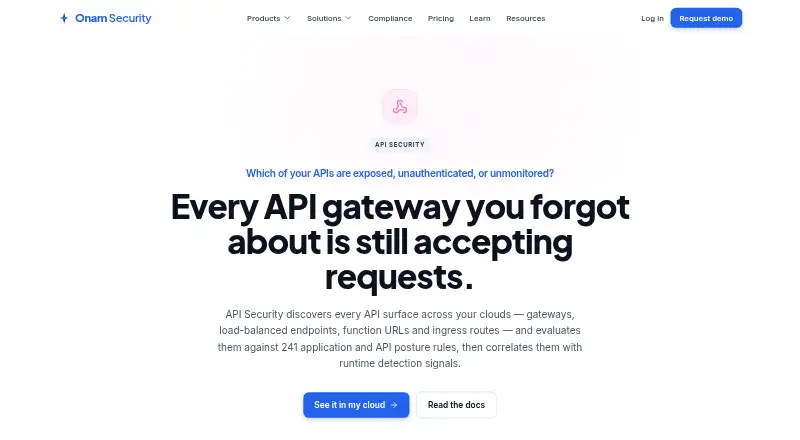
Onam Security API Security discovers API endpoints across cloud environments and checks their configurations against 241 application and API security rules. It finds surfaces including gateways, load-balanced endpoints, function URLs, and ingress routes across AWS, Azure, GCP, OCI, Alibaba, and Kubernetes. The product compares endpoints with a network graph to identify APIs reachable through open paths and flag shadow or orphaned APIs. Scanning reads configuration through read-only cloud APIs and does not send traffic to APIs for active testing. Rules cover authentication, authorisation, throttling, WAF association, TLS policy, and logging. The Free plan costs nothing and covers one cloud account, up to 500 resources, 30-day finding history, and community support. Pro costs $22 a month, billed per resource each month, and includes unlimited cloud accounts and one-year finding history. A 14-day trial is listed. Integrations include Jira, ServiceNow, Slack, Microsoft Teams, PagerDuty, Splunk, Azure Sentinel, AWS Security Hub, GitHub Actions, and GitLab CI.
Good
- Discovers API surfaces across six named cloud environments and Kubernetes.
- Checks endpoints against 241 security rules.
- Read-only configuration scans send no API traffic.
- Integrates with security and collaboration tools.
Watch out
- Free plan is limited to one cloud account.
- Free plan caps coverage at 500 resources.
- Free finding history lasts 30 days.
Who it suits
It suits teams seeking visibility into exposed, unauthenticated, or unmonitored APIs across cloud environments. The free tier is limited to one cloud account and 500 resources.
Verdict
Onam Security API Security focuses on cloud API discovery, configuration checks, and exposure visibility without active API testing. Consider the Free plan’s account and resource caps when assessing fit.
Plans and prices
From Onam Security API Security's own pricing page, checked 14 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free | Free | 1 cloud account · up to 500 resources · core CSPM rules · CIS benchmarks · 30-day finding history · community support · forever |
| Pro | $22 a month | Unlimited cloud accounts · all 29 engines · 78 compliance frameworks · agentless workload scanning · SaaS security · threat detection · REST API · 1-year finding history · email support under 24h · per resource/month, billed monthly; platform fee applies |
| Enterprise | — | Everything in Pro · multi-tenant support · custom frameworks · SAML 2.0 · custom RBAC · dedicated security engineer · on-premises option · custom retention · contractual 99.9% uptime SLA · priority support under 4h · custom annual contract |
The facts
Each one read from Onam Security API Security's own pages, with the date it was checked.
What it does
- Active testing limit
- API posture scans read cloud configuration and do not send traffic; active endpoint testing is handled separately by the DAST scanner.checked 14 Oct 2026
- API authentication
- API calls use signed login tokens delivered as an access-token cookie; long-lived API keys are listed as coming soon.checked 14 Oct 2026
- API discovery
- API Security discovers API surfaces across clouds, including gateways, load-balanced endpoints, function URLs, and ingress routes.checked 5 Oct 2026
- API inventory
- API Security inventories gateway-managed APIs across AWS, Azure, Google Cloud, OCI, Alibaba Cloud and Kubernetes.checked 14 Oct 2026
- Authentication checks
- The API Security capability detects unauthenticated or openly reachable endpoints.checked 14 Oct 2026
- Certifications
- The Trust Center lists SOC 2 Type II, ISO 27001:2022, ISO 27017, and PCI DSS v4.0 as achieved.checked 5 Oct 2026
- Cloud connection model
- Cloud onboarding uses read-only IAM roles, service principals or service accounts, with no agents or write access required.checked 14 Oct 2026
- Cloud coverage
- Discovery spans AWS, Azure, GCP, OCI, Alibaba, and Kubernetes.checked 5 Oct 2026
- Compliance coverage
- The compliance engine maps findings to 78 frameworks and exports PDF, Excel, CSV and JSON reports.checked 14 Oct 2026
- Data retention
- Full-detail security findings are retained for 12 months, aggregated scores for 36 months, raw scan configurations for 90 days and audit logs for seven years.checked 14 Oct 2026
- Deployment
- The service is SaaS by default; Enterprise offers an on-premises deployment option.checked 14 Oct 2026
- Documentation depth
- Documentation includes getting-started guides, seven cloud onboarding guides, feature deep dives, architecture, compliance, trust, API reference, integrations, RBAC and release notes.checked 14 Oct 2026
- Exposure detection
- The product cross-references endpoints with the network graph to identify APIs reachable through open paths and flags shadow or orphaned APIs.checked 5 Oct 2026
- Independent feature limit
- Capterra's product summary says the listing includes cloud application security and vulnerability scanning but not monitoring or security auditing.checked 14 Oct 2026
- Independent pricing note
- Capterra lists the Pro plan as $22 per active resource monthly plus a platform fee, with free and trial options.checked 14 Oct 2026
- Independent support note
- Capterra describes documentation, webinars, videos, email/help-desk support, a knowledge base and chat as available support channels.checked 14 Oct 2026
- Integrations
- Documented integrations include Jira, ServiceNow, Azure DevOps, Linear, GitHub Issues, Slack, Microsoft Teams, PagerDuty, OpsGenie, Splunk, Azure Sentinel, AWS Security Hub and generic webhooks.checked 14 Oct 2026
- Intended users
- The API Security page describes the product for teams seeking visibility into exposed, unauthenticated, or unmonitored APIs across their cloud environments.checked 5 Oct 2026
- Legal name
- Crunchbase identifies the legal name as “candc.”checked 14 Oct 2026
- Limit: API keys
- Programmatic long-lived API keys are not yet available and are listed on the roadmap.checked 14 Oct 2026
The company
- Company headquarters
- LinkedIn lists Delhi, India as the headquarters, while Crunchbase specifies New Delhi, Delhi, India.checked 14 Oct 2026
- Company size
- LinkedIn lists onamsecurity as a privately held computer and network security company with 2–10 employees.checked 14 Oct 2026
- Founded
- LinkedIn lists the company as founded in 2018.checked 14 Oct 2026
Money
- Free plan limits
- The Free plan includes one cloud account and up to 500 resources, with 30-day finding history.checked 5 Oct 2026
The full review of Onam Security API Security
Onam Security API Security is a cloud API posture product for security teams that need to inventory endpoints and spot configuration or exposure risks across cloud environments. It is best suited to organizations managing APIs across multiple providers; its read-only approach provides broad visibility without sending test traffic, but does not assess API behavior through active requests.
Overview
The product discovers API surfaces across gateways, load-balanced endpoints, function URLs, and ingress routes, then evaluates them against 241 application and API security rules. By comparing endpoints with a network graph, it can identify APIs reachable through open paths and flag shadow or orphaned APIs. That combination makes it useful for finding overlooked exposure as well as checking configuration.
Scanning reads configuration through read-only cloud APIs rather than sending traffic to the endpoints. This is a good fit for posture reviews that should avoid active testing, but teams still need other methods to assess how APIs behave under real requests.
Key features
- Multi-environment discovery: Coverage spans AWS, Azure, GCP, OCI, Alibaba, and Kubernetes. That breadth benefits teams with distributed cloud estates; a team focused on a narrow environment may not need as much coverage.
- Focused configuration checks: The 241 rules address authentication, authorisation, throttling, WAF association, TLS policy, and logging. This gives security teams a substantial set of posture controls to review without implying active validation of those controls.
- Exposure context: Cross-referencing APIs with network paths helps distinguish endpoints that are reachable through open routes and brings shadow or orphaned APIs into view. That is valuable for prioritizing visibility gaps, though it is not a substitute for request-based testing.
- Operational connections: The integration catalog includes Jira, ServiceNow, Slack, Microsoft Teams, PagerDuty, Splunk, Azure Sentinel, AWS Security Hub, GitHub Actions, and GitLab CI. Teams using these systems can connect API posture work to ticketing, notifications, security operations, or CI workflows.
- Platform assurances: Onam documents a unified REST API under /api/v1. Its Trust Center lists SOC 2 Type II, ISO 27001:2022, ISO 27017, and PCI DSS v4.0 as achieved, and states that data is encrypted at rest with AES-256 and traffic uses TLS 1.3. These may help organizations evaluating governance and platform security requirements.
Pricing
The Free plan costs nothing and is billed forever. It allows one cloud account and up to 500 resources, keeps findings for 30 days, and includes community support. That is a practical starting point for a limited deployment, but the account and resource caps constrain use across larger or multi-cloud environments.
Pro costs $22 a month, billed per resource / month and billed monthly. It removes the cloud-account limit, includes all 29 engines, extends finding history to one year, and provides email support with a stated response time under 24 hours. The per-resource billing means the monthly price grows with the footprint, so the entry price alone does not establish the cost of a large environment.
Enterprise uses an annual contract with custom pricing. It adds custom data retention, a contractual 99.9% uptime SLA, priority support under four hours, and a choice of SaaS or on-premises deployment. This tier is better suited to organizations that need contractual service commitments or deployment flexibility; the Free plan and Pro do not include those stated terms. A 14-day trial is available for evaluating the product before choosing a plan.
Platforms
Onam lists API, self-hosted, and web platforms, with a hybrid deployment model. Enterprise explicitly offers SaaS or on-premises deployment, making it the clearest fit for organizations that require that choice. The Free and Pro plan details do not state the same deployment options.
Who it's for
Onam is aimed at teams seeking visibility into exposed, unauthenticated, or unmonitored APIs across cloud environments. It is particularly relevant when security staff need to inventory endpoints, check configuration, and understand network exposure across several providers. Teams that need active API behavior testing should pair it with a testing approach that sends requests, rather than treating posture scanning as a complete assessment.
Pros and cons
- Pro: Discovery covers six cloud environments and Kubernetes, giving multi-cloud teams a broad view of API surfaces.
- Pro: Network-path analysis can surface reachable, shadow, and orphaned APIs alongside configuration findings.
- Pro: Read-only scanning avoids sending traffic to APIs, which suits configuration-focused reviews.
- Con: No active API traffic testing means the product does not show how endpoints respond to real requests.
- Con: Free is limited to one cloud account, 500 resources, and 30-day finding history, which can be restrictive beyond a small evaluation.
- Con: Pro is billed per resource per month, so costs scale with the monitored footprint.
Alternatives
For a comparison across API-focused products, see the API Security Software directory. Onam's emphasis is cloud discovery and configuration posture rather than active traffic testing.
- Zscaler Private Access is a paid private-access option with a Standard plan described as limited private access for 5% of users.
- Skyhigh Private Access is another paid private-access option.
- Bedrock Data Security Platform has a free Snowflake-only plan with weekly scans; choose it when that narrower data-security scope is the priority.
- Cyberhaven Data Security Platform is a paid alternative with pricing provided by request and a product demo offered by the company.
- Forcepoint Data Security Cloud is a paid option with pricing by request.
- Netwrix Password Secure is a paid alternative whose self-service plan starts at $60 a year, with a minimum one-year purchase commitment.
- Proofpoint Email DLP and Encryption is a paid alternative.
- Siberson Data Security Posture Management is a paid option licensed per terabyte of data.
Readers comparing adjacent categories can also browse Data Security Posture Management Software, Cloud Security Platforms, SaaS Security Posture Management Software, and Cloud Vulnerability Scanners.
Verdict
Choose Onam Security API Security when your team needs a cross-cloud inventory of API endpoints, configuration checks, and visibility into network exposure without active testing traffic. Its breadth of discovery and read-only posture scanning are the core reasons to consider it. Look elsewhere or add a separate testing tool if you need to evaluate API behavior through requests, and weigh Pro's per-resource billing against the size of your environment.
Alternatives to Onam Security API Security
- 1
Kubescape
Free planOpen sourceAPILinuxmacOSSelf-hosted8.2From $30 a month - 2
Armor
Free planWebAPILinuxmacOS7.7From $99 a month - 3
C3M Cloud Control
Free planAndroidiOSWebAPI7.4Free plan - 4
Microsoft Defender for Individuals
AndroidiOSWebmacOS7.3From $99.99 a year - 5
Sysdig Secure
WebAPILinuxmacOS7.2From $20 a month - 6
Prowler Cloud
Free planWebAPILinuxSelf-hosted7.0From $99 a month