TinyLoad
TinyLoad v7.4 is an open-source packer and crypter for Windows x64 PE executables.
What TinyLoad is
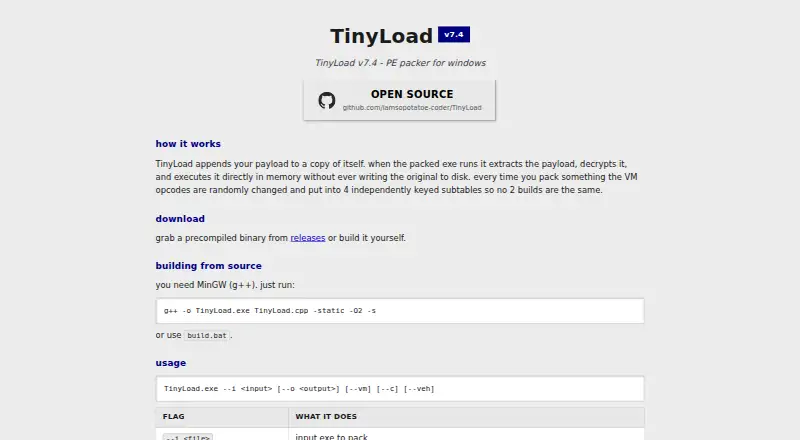
TinyLoad v7.4 is an open-source packer and crypter for Windows x64 PE executables. It adds protection layers intended to make packed programs harder to reverse engineer. The packed file appends a payload to a copy of itself, then extracts, decrypts, and runs it in memory without writing the original payload to disk. Optional LZ77 compression uses hash-chain matching with a 64 KB sliding window. Its custom virtual machine has 28 opcodes in four subtables, and the payload uses XXTEA encryption. With VEH enabled, pages decrypt when accessed and a watchdog re-encrypts pages untouched for 200 ms. TinyLoad also redirects four APIs through wrappers and clears the payload’s import directory after loading. It accepts x64 PE files and requires at least one of VM encryption, compression, or VEH. The MIT-licensed project can be built with MinGW g++ or build.bat, and precompiled binaries are linked from GitHub Releases. The maker reports nine VirusTotal detections for TinyLoad and files packed with it.
Good
- Open-source project licensed under MIT.
- Offers optional LZ77 compression and VEH features.
- Packed payload executes in memory without writing the original to disk.
- Precompiled binaries and source code are available.
Watch out
- Supports 64-bit PE files only.
- Requires VM encryption, compression, or VEH.
- The maker reports nine VirusTotal detections.
- The maker says packers are expected to be flagged.
Who it suits
TinyLoad is for users packing 64-bit PE executables on Windows who need the listed protection options. The maker describes it as intended for legitimate purposes and asks users not to pack malware with it.
Verdict
TinyLoad offers several packing and protection options for Windows x64 PE files. Its architecture limit and reported antivirus detections are important considerations.
The facts
Each one read from TinyLoad's own pages, with the date it was checked.
What it does
- Anti-dump
- The site says TinyLoad redirects four APIs through wrapper functions and zeroes the payload’s import directory after loading.checked 3 Oct 2026
- Antivirus detections
- The maker says packers are expected to be flagged and reports nine VirusTotal detections for TinyLoad and files packed with it.checked 3 Oct 2026
- Build
- The maker says to build from source with MinGW (g++) or use build.bat.checked 3 Oct 2026
- Build requirements
- The maker says to build from source with MinGW g++ or the included build.bat file, and describes the project as a single C++ source file with no external dependencies.checked 3 Oct 2026
- Compatibility limit
- The maker says TinyLoad works on most files they have tested, and release notes state it supports only 64-bit PE files.checked 3 Oct 2026
- Compression
- Its optional LZ77 compression uses hash-chain matching and a 64 KB sliding window.checked 3 Oct 2026
- Downloads
- The maker links to GitHub Releases for precompiled binaries and also offers source code in the repository.checked 3 Oct 2026
- Encryption
- Its 28 opcode virtual machine uses randomly placed opcodes in four independently keyed subtables, and the payload is encrypted using XXTEA.checked 3 Oct 2026
- How it works
- It appends a payload to a copy of itself, then extracts, decrypts, and executes the payload in memory without writing the original to disk.checked 3 Oct 2026
- In-memory execution
- The packed executable extracts and decrypts its payload, then executes it in memory without writing the original payload to disk.checked 3 Oct 2026
- Input requirements
- The packer accepts x64 PE executables and requires at least one of the VM encryption, compression, or VEH options.checked 3 Oct 2026
- Intended use
- The maker says TinyLoad is intended for legitimate purposes and asks users not to pack malware with it.checked 3 Oct 2026
- License
- TinyLoad is licensed under MIT.checked 3 Oct 2026
- Memory handling
- With VEH enabled, a vectored exception handler decrypts PE section pages on access and a watchdog re-encrypts pages untouched for 200ms.checked 3 Oct 2026
- Page decryption
- With the optional VEH feature, pages are decrypted on access and a watchdog re-encrypts pages that have not been touched in 200 ms.checked 3 Oct 2026
- Product
- TinyLoad v7.4 is an open-source PE packer and crypter for Windows x64 executables.checked 3 Oct 2026
- Purpose
- It packs executables with protection layers intended to make them harder to reverse engineer.checked 3 Oct 2026
- Support
- The maker invites users to open an issue if TinyLoad breaks on their file and to submit suggestions or feature ideas through issues.checked 3 Oct 2026
- Usage requirements
- At least one of --vm, --c, or --veh is required when packing an executable.checked 3 Oct 2026
- VM encryption
- Its custom virtual machine uses 28 opcodes arranged in four subtables, and the payload is encrypted using XXTEA.checked 3 Oct 2026
Alternatives to TinyLoad
- 1
Obsidian
Free planOpen sourceAndroidiOSExtensionLinux8.4From $48 a year - 2
Enigma Protector
WebAPILinuxSelf-hosted7.4 - 3
Virbox Protector
AndroidiOSLinuxmacOS7.1CN¥2,499 one-time - 4
VMProtect
LinuxmacOSWindows6.6 - 5
Crinkler
Free planWindows6.3Free plan - 6
Themida
Windows6.3From €79 a year