ThreatForge
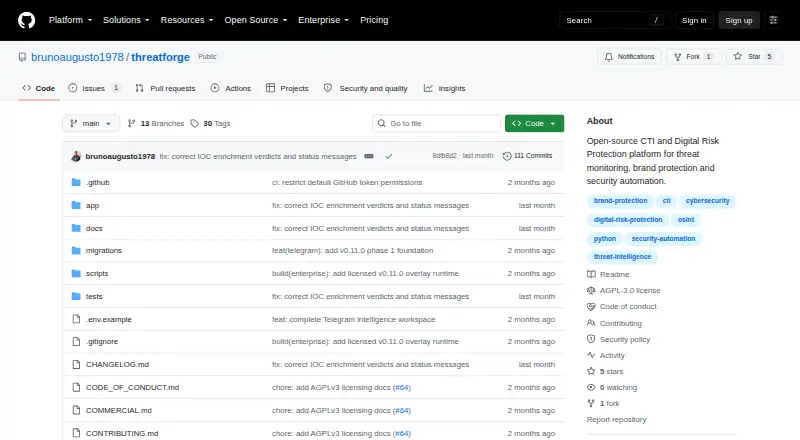
ThreatForge is an open-source CTI and Digital Risk Protection platform for threat monitoring, brand protection, and digital risk investigation.
What ThreatForge is
ThreatForge is an open-source CTI and Digital Risk Protection platform for threat monitoring, brand protection, and digital risk investigation. It is intended for security analysts, SOC teams, fraud teams, and researchers. Users can submit IPs, domains, URLs, hashes, email addresses, and CVEs for enrichment from public sources; the platform produces explainable risk scores from 0 to 100 and Markdown reports. Community connectors include CISA KEV, URLhaus/abuse.ch, MITRE ATT&CK, and EPSS/FIRST. Brand monitoring can generate typosquatting variants and add Certificate Transparency, DNS, MX, RDAP, and certificate-age details. Outbound alerts can use Telegram, webhooks, or SMTP, with each channel operating independently on a best-effort basis. The project documents Docker Compose deployment, a web UI served by the API, and interactive API documentation. Community is free under AGPL-3.0-or-later and is identified as a preview release, so its schema, API, and UI may change before stable 1.0. Community email observables are intake-only in the MVP, and the platform does not perform automatic takedowns.
Good
- Enriches six types of indicators from public sources.
- Produces explainable risk scores from 0 to 100.
- Includes several community threat-data connectors.
- Supports brand monitoring and outbound alerts.
- Free Community edition is open source.
Watch out
- Community email observables are intake-only in the MVP.
- It does not perform automatic takedowns.
- Community is a preview release and may change.
- Several integrations are stubs in Community.
Who it suits
ThreatForge is intended for security analysts, SOC and fraud teams, and researchers who need to organize indicators, enrich observables, monitor brand abuse, or prioritize risk.
Verdict
ThreatForge combines indicator enrichment, brand monitoring, scoring, and reporting in a free Community edition. Its preview status, best-effort alert channels, and Community limits matter for teams assessing it for operational use.
Plans and prices
From ThreatForge's own pricing page, checked 2 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Community Edition | Free | Open source · AGPL-3.0-or-later |
| Enterprise Edition | Priced on request | Commercial license · 90-day trial · commercial support and SLAs per agreement |
The facts
Each one read from ThreatForge's own pages, with the date it was checked.
What it does
- Access controls
- The platform supports multi-tenant isolation, tenant and platform roles, tenant-scoped API keys and audit logs for sensitive actions.checked 2 Oct 2026
- Alerts
- Outbound alerts can use Telegram, webhooks or SMTP, and each channel operates independently on a best-effort basis.checked 2 Oct 2026
- Brand protection
- Brand monitoring includes typosquatting variation generation, Certificate Transparency discovery, DNS/MX/RDAP and certificate-age enrichment, and abuse scoring.checked 2 Oct 2026
- Deployment
- The README documents Docker Compose deployment, a web UI served by the API and interactive API documentation.checked 2 Oct 2026
- Enterprise limits
- Community locks PDF export, premium enrichment and inbound Telegram Intelligence behind an active Enterprise license; locked requests return HTTP 402.checked 2 Oct 2026
- Integrations
- MISP, OpenCTI and generic integrations are listed as catalog entries and stubs in Community, while the Enterprise edition enables them.checked 2 Oct 2026
- Intended users
- It is described as helping security analysts, SOC teams, fraud teams and researchers organize indicators, enrich observables, monitor brand abuse and prioritize risk.checked 2 Oct 2026
- IOC features
- It accepts IPs, domains, URLs, hashes, e-mails and CVEs, enriches observables from public sources, calculates explainable risk scores from 0 to 100 and generates Markdown reports.checked 2 Oct 2026
- Notable limits
- Community email observables are intake-only in the MVP, and ThreatForge does not perform automatic takedowns.checked 2 Oct 2026
- Public connectors
- Community connectors include CISA KEV, URLhaus/abuse.ch, MITRE ATT&CK and EPSS/FIRST.checked 2 Oct 2026
- Purpose
- ThreatForge is an open-source CTI and Digital Risk Protection platform for threat monitoring, brand protection and digital risk investigation.checked 2 Oct 2026
- Release status
- The repository identifies Community v0.11.1 as a preview release and says its schema, API and UI may evolve before a stable 1.0.checked 2 Oct 2026
- Security
- The web UI uses JWT sessions in httpOnly and SameSite=Strict cookies, Argon2id password handling when available, and web security headers and login rate limiting.checked 2 Oct 2026
- Support
- The commercial license typically includes commercial support, SLAs and indemnification per agreement; the comparison describes Community support as community support.checked 2 Oct 2026
The full review of ThreatForge
Overview
ThreatForge is an open-source threat intelligence and digital risk platform for investigating indicators and monitoring brand abuse. It suits security analysts, SOC and fraud teams, and researchers who want a self-hosted way to enrich observables and prioritize risk. Its Community edition is a broad free starting point, but the preview release and Enterprise-only capabilities make it a cautious choice for operational dependence.
Key features
Analysts can submit IPs, domains, URLs, hashes, emails, and CVEs for enrichment from public sources. Explainable scores from 0 to 100 help prioritize investigation, while Markdown reports give findings a shareable format. Community connectors include CISA KEV, URLhaus/abuse.ch, MITRE ATT&CK, and EPSS/FIRST. Email observables are intake-only in the Community MVP, so teams needing fuller email analysis should not assume the same enrichment coverage as for other indicators.
Brand monitoring generates typosquatting variations and combines Certificate Transparency discovery with DNS, MX, RDAP, and certificate-age enrichment to score abuse. This makes ThreatForge relevant to teams watching for domain impersonation, though it does not perform automatic takedowns. Telegram, webhook, and SMTP alerts can connect findings to existing channels, but each works best-effort and independently; they are not a guaranteed notification path.
Multi-tenant isolation, tenant and platform roles, tenant-scoped API keys, and audit logs for sensitive actions provide useful separation for teams. The web UI uses JWT sessions in httpOnly and SameSite=Strict cookies, Argon2id password handling when available, security headers, and login rate limiting. Docker Compose deployment, an API-served web UI, and interactive API documentation support self-hosted and API-oriented use.
Community includes indicator enrichment, report management, workflow automation, and case management. MISP, OpenCTI, and generic integrations appear as catalog entries and stubs rather than enabled integrations in that edition, limiting its fit for teams that require those connections without an Enterprise license.
Pricing
| Plan | Price and terms | Best fit |
|---|---|---|
| Community Edition | free; open source under AGPL-3.0-or-later | Teams and researchers exploring core enrichment, monitoring, and workflows. |
| Enterprise Edition | Custom pricing; commercial license; 90-day trial; commercial support and SLAs per agreement | Organizations needing enabled integrations, premium features, or commercial terms. |
Community locks PDF export, premium enrichment, and inbound Telegram Intelligence; requests for those features return HTTP 402. Its free price is attractive for evaluation and self-hosting, but the preview release and these gates make it less suitable when those capabilities are essential. Enterprise also includes commercial support, SLAs, and indemnification per agreement; Community receives community support.
Platforms
ThreatForge supports API, self-hosted, and web use. Docker Compose deployment and a web UI served by the API make it a practical option for teams comfortable operating their own service.
Who it's for
Choose ThreatForge if your security, SOC, fraud, or research team wants one self-hosted platform for public-source indicator enrichment, explainable scoring, brand-abuse monitoring, and reporting. Look elsewhere if you need automatic takedowns, dependable alert delivery, full Community email-observable analysis, or integrations and premium capabilities without an Enterprise license. Community v0.11.1 is identified as a preview, and its schema, API, and UI may change before a stable 1.0.
Pros and cons
- Pro: Community covers enrichment, scoring, brand monitoring, reports, workflows, and case management at no cost.
- Pro: Tenant isolation, scoped API keys, role controls, and audit logs support separated team use.
- Con: The preview status means the schema, API, and UI may evolve before stable 1.0.
- Con: Best-effort alerts and the lack of automatic takedowns limit its role in time-critical response.
- Con: Enterprise gates PDF export, premium enrichment, inbound Telegram Intelligence, and enabled MISP/OpenCTI integrations.
Alternatives
For a broader directory of options, see Threat Intelligence Platforms.
- OpenAEV is a free Community Edition option for on-premise attack simulation and tabletop exercises, making it a better fit when those activities are the priority.
- IBM X-Force Exchange offers a free portal tier, but without X-Force API access; choose it when limited portal access is enough.
- Security Vision TIP uses sales-based individual pricing, a fit for buyers evaluating a paid TIP by modules, connectors, event volume, nodes, and support needs.
- SOCRadar Extended Threat Intelligence Platform has paid monitoring plans including $600 a month for 1 domain and 1 seat, or $1,145 a month for its Business tier; consider it when a priced dark-web monitoring plan better matches your requirements.
- Flashpoint Ignite uses pricing by request.
- ThreatQ requires licensed, non-perpetual platform access, with additional modules requiring license updates.
- Anomali Platform directs buyers to contact sales for pricing.
- Intel 471 Verity471 directs buyers to contact sales for a demo and product information.
Verdict
ThreatForge is a strong candidate for analysts and smaller security teams that want free, self-hosted indicator enrichment and brand-risk investigation with explainable scoring. Its broad Community toolkit is the main reason to choose it; look elsewhere if your operation depends on guaranteed alerts, automated takedowns, stable-release assurances, or Enterprise-gated integrations and enrichment.
Alternatives to ThreatForge
- 1
MISP
Free planOpen sourceWebAPILinuxSelf-hosted7.9From €7.31 a year - 2
Pulse Intelligence
Free planWebAPILinuxmacOS6.8Free plan - 3
Google Cloud Secret Manager
Free planWeb6.5From $0.02 a month - 4
Kaspersky Threat Intelligence Portal
Free planWebAPI6.5Free plan - 56.5From $4,550 a year
- 6
IBM X-Force Exchange
Free planWebAPI6.3Free plan