Security Vision TIP
Security Vision TIP collects, analyzes and enriches cybersecurity threat data to support detection, investigation and response across an organization's infra…
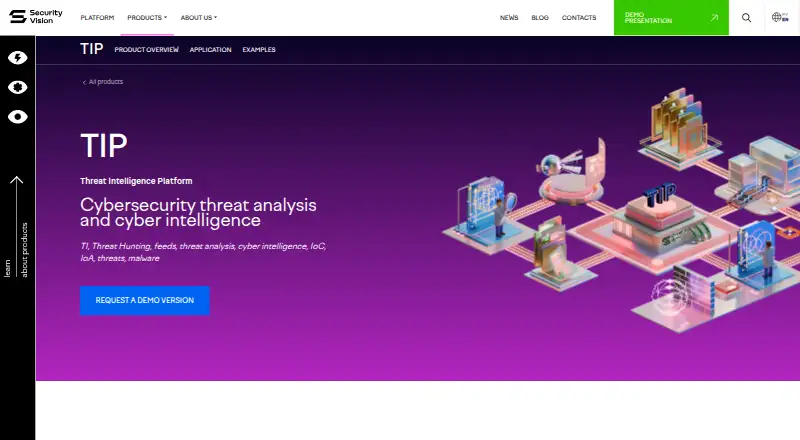
What Security Vision TIP is
Security Vision TIP collects, analyzes and enriches cybersecurity threat data to support detection, investigation and response across an organization's infrastructure. It handles indicators at technical, tactical, operational and strategic levels, including hashes, IP addresses, URLs, processes, vulnerabilities and attacker attribution. The platform has more than 50 connectors for event sources such as SIEM, NGFW, proxy and email solutions, and can support development of additional connectors. Listed formats include Syslog, CEF, LEEF, EMBLEM and Event log. TIP applies machine learning to DGA detection and supports both match searches and retrospective searches across collected data. Analysts can enrich indicators using MITRE ATT&CK and services such as VirusTotal, Shodan, KasperskyOpenTIP, IPInfo.io and MaxMind Geo-IP. Graph and table views can launch response actions, including blocking an IP, adding a URL to a web-control policy, stopping host processes or terminating a user session. The browser-accessed, self-hosted platform supports Linux distributions and Windows Server 2016 and higher, and includes an API. Pricing is individually calculated through sales; the product page offers a demo but states no price or trial duration.
Good
- More than 50 connectors cover key event-source classes.
- Supports match and retrospective indicator searches.
- Enrichment includes MITRE ATT&CK and listed services.
- Analysts can launch response actions from graph and table views.
- Custom cards and tables have no licensing restrictions, per product page.
Watch out
- Pricing is individually calculated through sales.
- At least one trained technician is required.
- No trial duration is stated.
Who it suits
Security Vision TIP suits security teams that need to collect and investigate threat indicators from multiple sources and coordinate response actions. The listed staffing requirements call for at least one trained technician covering administration, development and management responsibilities.
Verdict
Security Vision TIP combines threat-data intake, indicator analysis, enrichment and response actions in a self-hosted platform. Its deployment and staffing requirements, along with individually calculated pricing, are important considerations.
Plans and prices
From Security Vision TIP's own pricing page, checked 1 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Security Vision TIP | Priced on request | Modules and products · connectors or processed events per second · additional nodes · support level · permanent or temporary license · multi-tenancy · Individual calculation via sales |
The facts
Each one read from Security Vision TIP's own pages, with the date it was checked.
What it does
- Access model
- Security Vision is a client-server platform implemented as web applications and accessed through a web browser without a thick client.checked 1 Oct 2026
- API
- The platform has an API for interaction with technology partners and their APIs.checked 1 Oct 2026
- Commercial feeds
- Supported commercial subscriptions include Kaspersky, Group IB, BI.Zone and RST Cloud.checked 1 Oct 2026
- Connectors
- TIP provides 50+ connectors for SIEM, NGFW, proxy and email-server classes, with the ability to develop new connectors.checked 1 Oct 2026
- Customization
- Cards and table views can add properties, columns and buttons without licensing restrictions.checked 1 Oct 2026
- Data formats
- Listed supported formats include Syslog, CEF, LEEF, EMBLEM, and Event log.checked 30 Sep 2026
- Data sources
- TIP uses internal SIEM, NGFW, proxy and email-server sources, commercial and open-source feeds, analytical-center data and Syslog, CEF, LEEF, EMBLEM and Event Log formats.checked 1 Oct 2026
- Demo and contact
- The product page offers a demo and lists [email protected] as a contact; it does not state a trial duration or product price.checked 30 Sep 2026
- Detection
- DGA mechanisms using machine learning, match and retro search detect matches in object parameters.checked 1 Oct 2026
- Enrichment
- Automatic indicator enrichment uses MITRE ATT&CK, VirusTotal, Shodan, KasperskyOpenTIP, IPgeolocation.io, IPInfo.io, MaxMind Geo-IP, HaveIBeenPwned and LOLBAS.checked 1 Oct 2026
- Event collection
- The product page states that TIP has 50+ connectors for receiving events from SIEM, NGFW, proxy, and email solutions, and can support development of new connectors.checked 30 Sep 2026
- Indicator coverage
- The analytical base covers technical, tactical, operational and strategic threat-analysis levels.checked 1 Oct 2026
- Open-source feeds
- Supported open-source indicator sources include Alien Vault, Feodo Tracker and DigitalSide.checked 1 Oct 2026
- Operating systems
- The platform supports multiple Linux distributions and Microsoft Windows Server 2016 and higher.checked 1 Oct 2026
- Operational staffing
- At least one trained technician is required, covering 0.5 FTE administration and at least 0.5 FTE development and management.checked 1 Oct 2026
- Purpose
- Security Vision TIP collects, analyzes and enriches cybersecurity threat data and supports infrastructure detection, investigation and response.checked 1 Oct 2026
- Response actions
- Analysts can launch actions such as blocking IP traffic, adding URLs to Web-control policy, stopping host processes and services, and terminating sessions or changing passwords.checked 1 Oct 2026
- Security and compliance
- The company page states that Security Vision is FSTEC-certified at trust level 4 and meets GOST R ISO 9001-2015 and GOST R ISO/IEC 27001 management-system requirements.checked 30 Sep 2026
- Security certifications
- Security Vision is FSTEC-certified at the fourth trust level, included in the Unified Register of Russian Computer Programs and Databases, and meets GOST R ISO 9001-2015, GOST R ISO/IEC 27001 and PCI DSS requirements.checked 1 Oct 2026
- Support pricing
- Technical-support percentages listed are 25% standard and 33% extended in license format, 30% and 40% by certificate, and 35% and 45% when services are provided.checked 1 Oct 2026
- Threat data
- It processes indicators across technical, tactical, operational, and strategic levels, including hashes, IP addresses, URLs, processes, vulnerabilities, and attacker attribution.checked 30 Sep 2026
- Threat feeds
- The product page lists commercial feed subscriptions from Kaspersky, Group IB, BI.Zone, and RST Cloud, plus open sources including Alien Vault, Feodo Tracker, and DigitalSide.checked 30 Sep 2026
Money
- Free feeds
- A company news page says a Security Vision feed package provides about 50,000 IoCs daily without a subscription and without a request limit via API or web interface.checked 30 Sep 2026
The company
- Headquarters
- Moscow, Russiachecked 28 Sep 2026
The full review of Security Vision TIP
Overview
Security Vision TIP is a self-hosted threat intelligence platform for security teams that need to combine organizational telemetry with external threat data. It is best suited to organizations with existing security infrastructure and staff for administration and development. Its collection, analysis and response capabilities are broad, but the operating commitment and custom pricing make it a poor fit for teams seeking a lightweight service.
Key features
TIP draws from SIEM, firewall, proxy and email systems through more than 50 connectors, with the option to develop new ones. It accepts Syslog, CEF, LEEF, EMBLEM and Event Log formats, giving teams several ways to bring existing telemetry into a shared analysis workflow. The flexibility is useful in mixed environments, but developing connectors adds work for an organization’s technical staff.
Its analytical coverage spans technical, tactical, operational and strategic threat levels, including hashes, IP addresses, URLs, processes, vulnerabilities and attacker attribution. Analysts can search for indicator matches and retrospectively query collected data; machine learning is used for domain-generation algorithm detection. These capabilities help teams investigate indicators against both current and historical data.
Feed options include commercial subscriptions from Kaspersky, Group IB, BI.Zone and RST Cloud, as well as open sources such as Alien Vault, Feodo Tracker and DigitalSide. A separate Security Vision feed package provides about 50,000 IoCs daily without a subscription or request limit through the API or web interface. That feed can provide a substantial stream of indicators, while paid subscriptions remain an additional option.
Automatic enrichment uses MITRE ATT&CK and services including VirusTotal, Shodan, KasperskyOpenTIP, IPInfo.io and MaxMind Geo-IP. Analysts can launch response actions from graph and table views, including blocking an IP, adding a URL to a web-control policy, stopping host processes or terminating a user session. This joins enrichment and response in the analysis workflow, though those actions sit within a platform that requires self-hosted operation.
Cards and tables can be adapted with properties, columns and buttons without licensing restrictions. TIP also supports indicator enrichment, STIX/TAXII, report management, workflow automation and case management. Its hybrid anomaly methods cover users, accounts, devices, hosts and processes, with automated response.
Pricing
Security Vision TIP is paid, with custom pricing calculated individually through sales. Cost depends on modules, connectors or processed events per second, additional nodes, support level, permanent or temporary licensing, and multi-tenancy. This model allows the deployment and support arrangement to be tailored, but teams cannot compare a fixed tier against a published price before contacting sales.
Technical support percentages vary by format and level: standard and extended support are 25% and 33% in license format, 30% and 40% by certificate, and 35% and 45% when services are provided. The product page offers a demo, but no trial duration is stated.
Platforms
TIP is a client-server platform accessed through a web browser without a thick client. It is self-hosted, supports multiple Linux distributions and Microsoft Windows Server 2016 and later, and provides an API for technology partners and their APIs. That deployment model suits organizations that need to operate the platform within their own environment, rather than buyers looking for a hosted service.
Who it's for
At least one trained technician is required, with 0.5 FTE for administration and at least 0.5 FTE for development and management. That staffing commitment makes TIP most appropriate for organizations able to assign both operational and development capacity, not small teams looking for a low-overhead feed reader.
Security Vision holds FSTEC certification at trust level 4, is included in the Unified Register of Russian Computer Programs and Databases, and meets GOST R ISO 9001-2015, GOST R ISO/IEC 27001 and PCI DSS requirements. Those credentials may matter to organizations evaluating security and management-system requirements.
Pros and cons
- Pro: More than 50 connectors, multiple event formats and support for new connector development give teams several ways to integrate existing security sources.
- Pro: Indicator enrichment, retrospective search and response actions connect investigation to operational follow-up.
- Pro: The separate feed package supplies about 50,000 IoCs daily without a subscription or request limit via API or web interface.
- Con: Individual custom pricing depends on deployment and support choices, so buyers need a sales discussion to establish cost.
- Con: The required trained technician allocation of at least 1 FTE across administration, development and management is a substantial operating commitment.
- Con: Self-hosted deployment and connector development are less suitable for teams seeking a hosted, low-maintenance option.
Alternatives
For behavioral analytics rather than a threat-intelligence platform, compare User and Entity Behavior Analytics Software; for a category-level comparison focused on threat intelligence platforms, see Threat Intelligence Platforms.
Netskope One Behavior Analytics is a paid alternative with Android, iOS, Linux, macOS, web and Windows support, and a Standard UEBA plan covering sequential anomaly rules for cloud-app activity and data movement.
Proofpoint Email DLP and Encryption is a paid option for readers considering an email DLP and encryption product, with Android, iOS, web and Windows support.
DTEX Insider Risk Management is another paid insider-risk option, available for Linux, macOS, web and Windows.
Teramind Insider Risk Management is worth comparing for teams seeking a paid option with a free trial and self-hosted, web and desktop platform support; its Enterprise plan includes tailored deployment assistance, custom reporting and behavior-rule configuration, and premium support and SLA.
Security Vision UEBA shares TIP’s paid, self-hosted platform and individual pricing model, with cost based on modules, connectors or event volume, additional nodes, support level, license type and multi-tenancy.
Securonix UEBA is a web-based paid alternative with plans that differ in storage duration and search capacity.
VbtEngine UEBA is a paid option for teams considering self-hosted or web deployment.
CYBERQUEST UEBA is a paid alternative available as a self-hosted or web product.
Verdict
Choose Security Vision TIP if your organization needs to bring internal security events and threat feeds together for enrichment, investigation and response, and can dedicate staff to a self-hosted deployment. Its breadth of connectors and integrated response actions are the strongest reasons to choose it. Look elsewhere if custom pricing, development work or the minimum staffing commitment outweigh that operational breadth.
Getting started
- Open the Security Vision TIP product page
- Request a demo or contact [email protected]
- Deploy the client-server platform on a supported Linux distribution or Windows Server 2016 or later
- Connect SIEM, NGFW, proxy, or email sources through the available connectors
- Add commercial or open-source threat feeds and configure indicator enrichment
Limits worth knowing
TIP is self-hosted and requires at least one trained technician, covering 0.5 FTE administration and at least 0.5 FTE development and management. Licensing and support costs are calculated individually, with support percentages depending on the license or service format.
Questions
How is TIP priced?
Pricing is determined individually through sales. The listed plan is billed by individual calculation based on modules, connectors or processed events, nodes, support level, licensing term, and multi-tenancy.
What deployment options are available?
TIP is a self-hosted, client-server platform delivered as web applications accessed through a browser.
Which operating systems are supported?
The platform supports multiple Linux distributions and Microsoft Windows Server 2016 and higher.
What event connectors and formats does it support?
It lists more than 50 connectors for SIEM, NGFW, proxy, and email-server classes. Supported formats include Syslog, CEF, LEEF, EMBLEM, and Event log.
Which threat feeds can be used?
Commercial subscriptions include Kaspersky, Group IB, BI.Zone, and RST Cloud. Open sources include Alien Vault, Feodo Tracker, and DigitalSide.
Is a trial available?
The product page offers a demo. No trial duration is stated in the listed details.
Alternatives to Security Vision TIP
- 1
MISP
Free planOpen sourceWebAPILinuxSelf-hosted7.9From €7.31 a year - 2
Pulse Intelligence
Free planWebAPILinuxmacOS6.8Free plan - 3
Google Cloud Secret Manager
Free planWeb6.5From $0.02 a month - 4
Kaspersky Threat Intelligence Portal
Free planWebAPI6.5Free plan - 56.5From $4,550 a year
- 6
IBM X-Force Exchange
Free planWebAPI6.3Free plan