SecurStack
SecurStack is an application security platform for finding, prioritizing and addressing software risk before production.
What SecurStack is
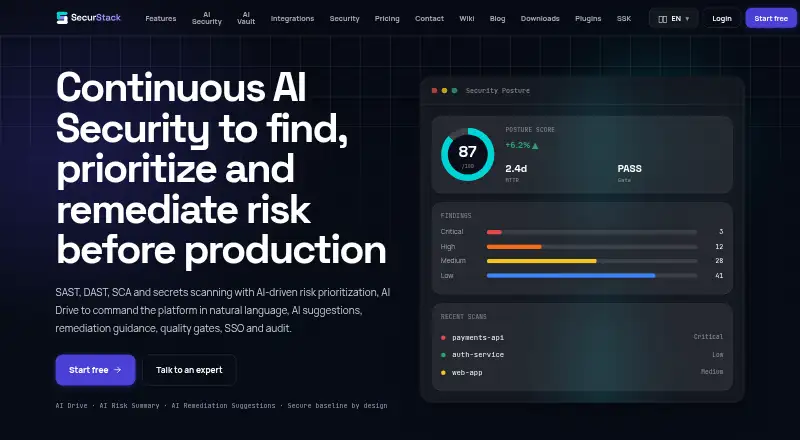
SecurStack is an application security platform for finding, prioritizing and addressing software risk before production. Its scans combine static and dynamic application security testing, software composition analysis with SBOM, and secrets scanning. Risk scores draw on severity, exposure, service criticality, exploitability and repository history. Teams can set policies to block builds that do not meet their security baseline. AI Drive accepts natural-language requests about risks, releases, repositories, owners and SLAs; AI suggestions include remediation paths, code snippets, validations and policies. The platform lists integrations for GitHub Actions, GitLab CI, Bitbucket Pipelines, Azure DevOps, Jenkins and CircleCI, plus plugins for JetBrains IDEs and VS Code. Its MCP server is compatible with Codex, Claude Code and other agents. AI Vault stores credentials by collection and provides scoped access through MCP, while auditing reveals without showing secret values in listings, logs or reports. The Free plan includes 500 scan credits per month, 3 users and 10 projects.
Good
- Combines SAST, DAST, SCA and secrets scanning
- Risk scoring incorporates repository history
- Quality gates can block builds
- Free plan includes 500 monthly scan credits
- AI Vault audits reveals without displaying secret values
Watch out
- Free plan limited to 3 users
- Free plan limited to 10 projects
- Enterprise price not listed
Who it suits
SecurStack is aimed at engineering, security and compliance teams, including engineering leaders and CISOs, who need to manage application risk before production.
Verdict
SecurStack combines several types of scanning with risk prioritization, remediation guidance and build policies. The Free plan has defined user, project and scan-credit limits; paid plans start at $5 a month.
Plans and prices
From SecurStack's own pricing page, checked 30 Sep 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free | Free | 500 scan credits/month · 3 users · 10 projects · SAST + SCA + Secrets |
| Basic | $5 a month | 2,500 scan credits/month · 10 users · 25 projects · 10 API keys |
| Pro | $15 a month | 10,000 scan credits/month · 25 users · Unlimited projects · SSO and quality gates |
| Enterprise | Priced on request | 50,000+ credits/month · 100+ users · 100+ API keys · Private runners and SLA |
The facts
Each one read from SecurStack's own pages, with the date it was checked.
What it does
- AI features
- AI Drive accepts natural-language commands about risks, releases, repositories, owners and SLAs.checked 30 Sep 2026
- AI Vault
- AI Vault stores credentials by collection, grants scoped access through MCP and audits reveals without showing secret values in listings, logs or reports.checked 30 Sep 2026
- CI/CD integrations
- The site lists GitHub Actions, GitLab CI, Bitbucket Pipelines, Azure DevOps, Jenkins and CircleCI.checked 30 Sep 2026
- Developer tools
- The site lists plugins for JetBrains IDEs and VS Code, plus an MCP server compatible with Codex, Claude Code and other agents.checked 30 Sep 2026
- Intended users
- The platform describes its use cases for engineering, security and compliance teams, including engineering leadership and CISOs.checked 30 Sep 2026
- Purpose
- SecurStack provides continuous application security to find, prioritize and remediate risk before production.checked 30 Sep 2026
- Quality gates
- Teams can define policies that block builds that fall below their security baseline.checked 30 Sep 2026
- Remediation
- AI suggestions provide remediation paths, code snippets, validations and policies to help prevent recurrence.checked 30 Sep 2026
- Risk prioritization
- AI-driven risk scoring combines severity, exposure, service criticality, exploitability and repository history.checked 30 Sep 2026
- Scanning
- The platform combines SAST, DAST, software composition analysis with SBOM, and secrets scanning.checked 30 Sep 2026
- Security controls
- The site describes multi-tenant isolation, granular RBAC, immutable audit logs, secrets redaction, TLS in transit and at rest, and workers without public ingress.checked 30 Sep 2026
- Support
- The contact page offers a personalized demo and says the team responds within one business day.checked 30 Sep 2026
Money
- Free plan limit
- The Free plan includes 500 scan credits per month, 3 users, 10 projects, and SAST, SCA and Secrets scanning.checked 30 Sep 2026
The full review of SecurStack
SecurStack is a cloud application-security platform for engineering, security and compliance teams that want vulnerability work connected to development. It suits organizations managing multiple repositories and releases, especially those that need prioritization and build controls rather than a scan report alone. Its broad coverage and low-cost entry are compelling, but lower-tier quotas can become a practical constraint.
Overview
SecurStack combines application scanning, risk management and remediation in one cloud service, accessible through a web interface and extension. SAST, DAST, software composition analysis with SBOM, and secrets scanning cover code, running applications, dependencies and exposed credentials. Finding correlation and ownership mapping help turn separate results into accountable work, while remediation workflows and SBOM management support follow-through after detection.
The service is designed for engineering, security and compliance operations, including engineering leadership and CISOs. Its controls include multi-tenant isolation, granular role-based access, immutable audit logs, secrets redaction, TLS in transit and at rest, and workers without public ingress. AI Vault adds collection-based credential storage, scoped MCP access and audited reveals without exposing secret values in listings, logs or reports.
Key features
AI-driven risk scoring weighs severity with exposure, service criticality, exploitability and repository history. That context is more useful for triage than severity alone when teams have many findings competing for attention. AI Drive accepts natural-language commands concerning risks, releases, repositories, owners and SLAs, giving teams another way to navigate operational security data.
For remediation, AI suggestions provide proposed paths, code snippets, validations and policies. These outputs are aimed at fixing issues and reducing recurrence, rather than merely explaining a finding. Teams can define quality gates that block builds below their security baseline, which makes SecurStack a better fit for organizations willing to enforce security in delivery pipelines.
Integrations cover GitHub Actions, GitLab CI, Bitbucket Pipelines, Azure DevOps, Jenkins and CircleCI. JetBrains and VS Code plugins bring developer tooling into the IDE, while an MCP server works with Codex, Claude Code and other agents. The combination is broad, though teams should match scan-credit consumption to repository and pipeline volume.
Pricing
The Free plan costs nothing and includes 500 scan credits per month, 3 users, 10 projects, SAST, SCA and Secrets scanning. It is a credible starting point for a small team, but it excludes DAST and leaves little room for many projects or frequent pipeline scans.
Basic costs $5 a month and raises capacity to 2,500 scan credits, 10 users, 25 projects and 10 API keys. It fits a growing team that needs more seats and automation at a modest monthly price, while still imposing finite project and credit limits.
Pro costs $15 a month and includes 10,000 scan credits, 25 users, unlimited projects, SSO and quality gates. This is the practical choice for teams that need policy enforcement and no project ceiling. Enterprise has custom pricing and provides 50,000+ credits per month, 100+ users, 100+ API keys, private runners and an SLA; it is aimed at larger or governance-heavy deployments.
The site offers a personalized demo and says responses arrive within one business day. Cloud deployment is the stated option.
Platforms
SecurStack runs on the web and as an extension. Its CI/CD integrations, IDE plugins and MCP server extend coverage into pipelines, editors and agent workflows, while Enterprise adds private runners.
Who it's for
Choose SecurStack when engineering and security teams need one workflow spanning code, dependencies, applications and secrets, with ownership, prioritization and remediation tied to releases. Pro is particularly suitable for teams ready to block noncompliant builds. Small teams can start free or on Basic, provided the scan, user and project caps match their activity.
Look elsewhere if you require a self-hosted deployment, or if a small workload makes a multi-scan platform unnecessary. The lower plans also demand attention to credit consumption as usage grows.
Pros and cons
Pros
- Wide scan coverage: SAST, DAST, SCA with SBOM and secrets scanning address several risk sources in one service.
- Action-oriented prioritization: scoring combines severity, exposure, criticality, exploitability and repository history.
- Delivery controls: quality gates can block builds that miss the security baseline.
- Accessible entry pricing: Free and 5.00 USD-per-month tiers let small teams begin without an enterprise contract.
- Developer and agent reach: CI integrations, JetBrains and VS Code plugins, and MCP support connect security to existing workflows.
Cons
- Free-plan constraints: 500 monthly credits, 3 users and 10 projects limit sustained or multi-team use, and the included scans omit DAST.
- Quota-based scaling: Basic and Pro still cap monthly credits, so high-frequency pipelines need capacity planning.
- Cloud-only deployment: organizations requiring self-hosting do not get that option in the stated plans.
- Enterprise-only extras: private runners and an SLA require custom-priced Enterprise.
Alternatives
Conviso Platform is worth choosing for API and web access with a free tier supporting up to 5 contributing developers, 5 assets, 10 users and 2 integrations, or a Developers plan from $19 a month.
Ivanti Neurons for Zero Trust Access is the alternative for teams seeking a paid, named-user SaaS product across a broad desktop and mobile platform range.
OWASP DefectDojo suits organizations wanting a free-forever open-source community edition with self-hosting and OWASP Slack and GitHub support.
Phoenix Security is an option for asset-focused teams whose free tier covers up to 1,000 assets and two premium users plus guests.
Strobes ASPM fits teams seeking a free tier with up to 100 assets, 500 tasks per month, ASM, RBVM, ASPM and one connector.
Arnica Secrets Security is the more focused choice when secrets and identity-oriented scanning are the priority.
OX Security is a paid alternative offering code, dependency, secrets/PII, SBOM, IaC, CI/CD, container, IDE and CLI coverage.
Foxnode ASPM is another free ASPM option with API, Linux, self-hosted and web platforms.
Verdict
SecurStack is a strong choice for engineering and security teams that want broad scanning, contextual prioritization and enforceable pipeline policies in one cloud platform. Its main reason to look elsewhere is the combination of credit, seat and project ceilings on lower plans, plus the absence of self-hosting; larger or highly specialized deployments may need Enterprise or a different operating model.
Alternatives to SecurStack
- 1
OWASP DefectDojo
Free planOpen sourceWebAPILinuxSelf-hosted8.0$100 usage-based - 2
Strobes ASPM
Free planWebAPILinuxmacOS7.8From $29,000 a year - 3
OX Security
Free planWebAPIExtensionLinux7.4Free plan - 4
Conviso Platform
Free planWebAPI7.3From $19 a month - 5
Phoenix Security
Free planWebAPI7.2From £1,495 a month - 6
Arnica Secrets Security
Free planWebAPISelf-hosted6.6From $300 a year