RedForge
C
C tier on AI Security Testing ToolsScore 6.1 · #26 of 29
- Android app
- Not listed
- Free plan
- Yes
- Runs on
- api, Linux, self-hosted
Summary
RedForge is ranked #26 of 29 in AI security testing tools on Everything Xiaomi. It runs on API, Linux, Self-hosted. There is a free plan.
RedForge plans and pricing
All plansCompared on AI security testing tools
- Prompt injection tests
- Yesgithub.com
- Jailbreak tests
- Yesgithub.com
- Data leakage tests
- Yesgithub.com
- Unsafe output tests
- Yesgithub.com
- Custom test cases
- Yesgithub.com
- Deployment mode
- self_hostedgithub.com
Facts
- Purpose
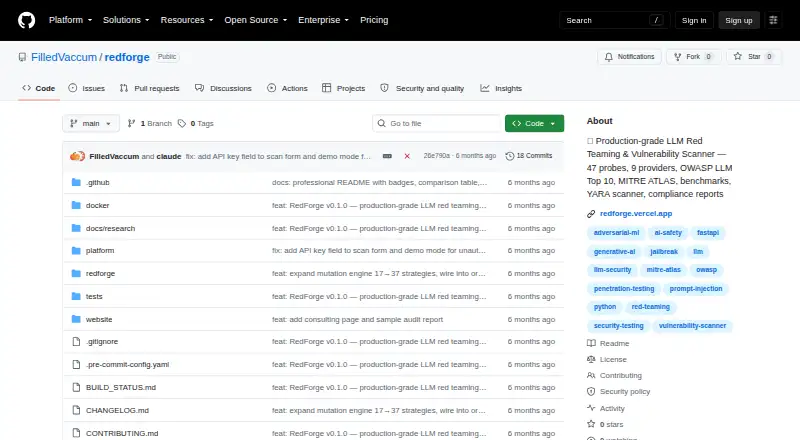
- RedForge is an LLM security testing platform for red teaming and vulnerability scanning.github.com · 9 Oct 2026
- Probe coverage
- It lists 49+ probes and full OWASP LLM Top 10 coverage, with YAML probes that can be added without Python.github.com · 9 Oct 2026
- Attack modules
- Its attack modules include PAIR, Crescendo multi-turn escalation, Skeleton Key, many-shot jailbreaking, and GCG adversarial suffixes.github.com · 9 Oct 2026
- Mutation engine
- The mutation engine expands two payloads to 37 variants across encoding, Unicode, cognitive reframing, and structural injection strategies.github.com · 9 Oct 2026
- Model providers
- It lists adapters for OpenAI, Anthropic, Google Gemini, AWS Bedrock, Azure OpenAI, Mistral, Ollama, HuggingFace, and generic REST endpoints.github.com · 9 Oct 2026
- Local use
- The Ollama adapter runs locally without an API key, and the README describes it as zero cost.github.com · 9 Oct 2026
- Reports
- Scans automatically produce JSON, JSONL audit, and failures reports, with additional HTML, Markdown, SARIF, JSON, audit, and failures formats.github.com · 9 Oct 2026
- Compliance
- Compliance reporting covers NIST AI RMF, EU AI Act, ISO/IEC 42001, GDPR, and OWASP LLM Top 10, and users can add custom YAML frameworks.github.com · 9 Oct 2026
- Detectors
- The README lists seven detector types, including YARA-style, similarity, refusal, regex, keyword, code, and unsafe-content detectors.github.com · 9 Oct 2026
- Security controls
- Documented controls include masking API keys in logs, setting result files to mode 0600, bearer-token REST API authentication, disabled-by-default CORS, and a rate limit of 10 scan requests per minute per client.github.com · 9 Oct 2026
- Deployment
- The Docker instructions say the container runs as non-root user redforge (UID 1001) with a read-only filesystem.github.com · 9 Oct 2026
- CI integration
- RedForge can emit SARIF for GitHub Code Scanning and exits with status 1 on critical or high findings for use as a CI gate.github.com · 9 Oct 2026
- License and use
- The repository identifies the license as Apache 2.0 and says the tool is for authorized use only.github.com · 9 Oct 2026
- Attack methods
- Attack modules include PAIR, Crescendo multi-turn escalation, Skeleton Key, many-shot jailbreaking, and GCG adversarial suffixes.github.com · 9 Oct 2026
- Guardrails
- A bidirectional guardrail pipeline scans inputs and outputs for prompt injection, PII, toxicity, and secrets.github.com · 9 Oct 2026
- Providers
- The README lists provider adapters for OpenAI, Anthropic, Google Gemini, AWS Bedrock, Azure OpenAI, Mistral, Ollama, HuggingFace, and generic REST endpoints.github.com · 9 Oct 2026
- Integrations
- It can export SARIF for GitHub Code Scanning and documents a GitHub Actions workflow that uploads the SARIF file.github.com · 9 Oct 2026
- Usage requirement
- The CLI requires an authorization value indicating owned, authorized, or research use.github.com · 9 Oct 2026
- License
- The project is released under the Apache 2.0 license, and the README says probe payloads are released under CC0.github.com · 9 Oct 2026
Best RedForge alternatives
See all 20
Where it ranks on Everything Xiaomi
Is RedForge yours?
Claim it for free: prove the domain, then correct facts, plans and screenshots. An editor reviews every change.
Sources
- github.com/FilledVaccum/redforge· checked 9 Oct 2026