AIRTA Red Team
AIRTA Red Team is a self-hosted tool for authorized adversarial assessments of LLMs and LLM-driven applications.
What AIRTA Red Team is
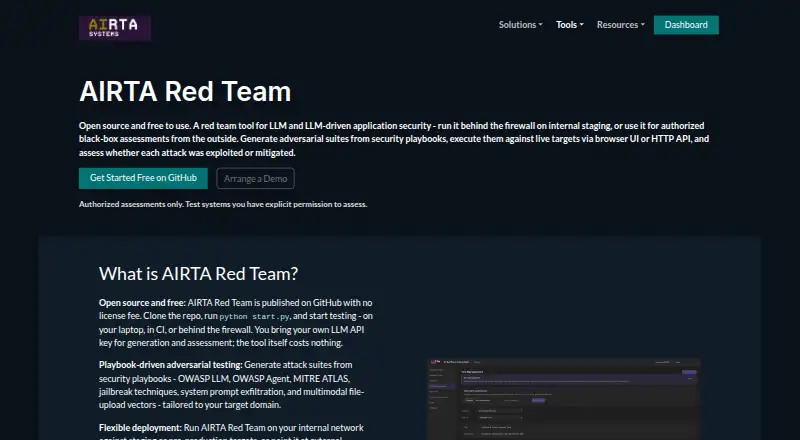
AIRTA Red Team is a self-hosted tool for authorized adversarial assessments of LLMs and LLM-driven applications. It builds test suites from security playbooks, discovers target components and authentication, runs attacks, assesses outcomes, and exports reports. Listed playbooks cover OWASP LLM, OWASP Agent, MITRE ATLAS, jailbreaks, system prompt exfiltration, and custom scenarios. Strategies include zero-shot, multi-shot, few-shot, iterative, multimodal, jailbreak, and chain-of-thought testing. Targets can be reached using a Playwright browser runner or direct HTTP API transports, including file uploads and tool calls. The tool can run locally in Docker, behind a firewall, in CI, or against external endpoints for authorized black-box assessments. Runs record prompts, uploads, responses, and tool calls in attack_log.json; pipeline_report.json summarizes categories and severity. Results can be sent to AIRTA Systems through its bulk import API for review and regression tracking. The free plan has no license fee or subscription, but users supply their own LLM API key. Assessments focus on observable runtime behavior, not source-code static analysis. The repository says the tool is deprecated and no longer maintained.
Good
- Includes OWASP LLM, OWASP Agent, and MITRE ATLAS playbooks.
- Supports browser and direct HTTP API testing.
- Captures prompts, uploads, responses, and tool calls.
- Can run locally in Docker, behind a firewall, or in CI.
- No license fee or subscription.
Watch out
- Users must provide their own LLM API key.
- It does not perform source-code static analysis.
- The repository says it is deprecated and no longer maintained.
Who it suits
It is intended for red teams, whitehat testers and pentesters, and AppSec and MLsec teams assessing LLM behavior. Use is limited to systems for which the user has explicit permission.
Verdict
AIRTA Red Team offers a broad runtime assessment workflow and detailed run artifacts at no subscription cost. Its deprecated, unmaintained status is an important consideration before adopting it.
Plans and prices
From AIRTA Red Team's own pricing page, checked 4 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| AIRTA Red Team | Free | Open source; no license fee or subscription · Bring your own LLM API key |
| Free | Free | Full pipeline, web UI, playbooks and CLI · self-hosted use · No license fee; bring your own LLM API key |
The facts
Each one read from AIRTA Red Team's own pages, with the date it was checked.
What it does
- Assessment models
- Playbook-specific expert models and a judge model classify attacks as exploited or mitigated and assign severity by category.checked 15 Oct 2026
- Assessment scope
- The product page says assessments focus on observable runtime behavior rather than source-code static analysis.checked 4 Oct 2026
- Attack coverage
- Listed playbooks include OWASP LLM, OWASP Agent, MITRE ATLAS, jailbreak, system prompt exfiltration, and custom playbooks.checked 4 Oct 2026
- Attack strategies
- The documented strategies include zero-shot, few-shot, multi-shot, jailbreak, multimodal, iterative and chain-of-thought testing.checked 15 Oct 2026
- Authorization
- The product page says to test only systems for which the user has explicit permission.checked 4 Oct 2026
- Authorized use
- The maker restricts use to systems for which the tester has explicit permission.checked 15 Oct 2026
- Capterra pricing listing
- Capterra lists AIRTA Systems pricing as contact-vendor, with no free trial and no free version included in that listing.checked 15 Oct 2026
- Deployment
- The maker documents local Docker deployment with python start.py, CLI operation with main.py, CI use, behind-firewall staging and authorized external black-box testing.checked 15 Oct 2026
- Documentation
- The maker provides a support documentation page with article search and category filters, but the page currently shows a loading posts area rather than a visible Red Team manual.checked 15 Oct 2026
- Editable suites
- Attack suites are JSON files containing playbooks, categories, prompts and optional multimodal payloads that can be edited in the web interface.checked 15 Oct 2026
- Evidence
- Runs capture prompts, uploads, responses, and tool calls in attack_log.json and produce pipeline_report.json with category rollups and severity.checked 4 Oct 2026
- Evidence files
- Runs capture prompts, uploads, responses and tool calls in attack_log.json and summarize results in pipeline_report.json.checked 15 Oct 2026
- Execution
- Targets can be tested through a Playwright browser runner or direct HTTP API transports, including file uploads and tool calls.checked 4 Oct 2026
- Execution transports
- Targets can be exercised through a Playwright browser runner or direct HTTP transports named api_document and api_multipart.checked 15 Oct 2026
- Independent-review availability
- G2, Capterra, GetApp and Software Advice pages opened for AIRTA Systems each show zero or no user reviews, so there is no repeated reviewer praise or complaint pattern to report.checked 15 Oct 2026
- Integration
- The documented integration sends pipeline_report.json to AIRTA Systems through a bulk import API for review, regression tracking and compliance workflows.checked 15 Oct 2026
- Integrations
- The tool can export assessment results to AIRTA Systems through its bulk import API for review and regression tracking.checked 4 Oct 2026
- Intended users
- The product page identifies red teams, whitehat testers and pentesters, and AppSec and MLsec teams as intended users.checked 4 Oct 2026
The company
- Company founders
- The about page says AIRTA Systems was founded in London by Cindy Ogidi and Bob Morel.checked 15 Oct 2026
- Company founding year
- LinkedIn lists the company as founded in 2026.checked 15 Oct 2026
- Company legal name
- The product site footer identifies the maker as AIRTA Systems Ltd.checked 15 Oct 2026
- Company size
- LinkedIn lists AIRTA Systems as having 11–50 employees.checked 15 Oct 2026
- Company type
- LinkedIn classifies AIRTA Systems as a public company in the technology, information and internet industry.checked 15 Oct 2026
Where it runs
- GetApp listing
- GetApp shows no user reviews and places AIRTA Systems in the Other Artificial Intelligence software category.checked 15 Oct 2026
The full review of AIRTA Red Team
AIRTA Red Team is a self-hosted tool for authorized runtime security assessments of LLMs and LLM-driven applications. It is best suited to red teams, pentesters, and AppSec or MLsec teams seeking structured attack runs and evidence. Its broad assessment workflow costs nothing, but its deprecated, unmaintained status is a serious drawback for ongoing use.
Overview
The workflow builds suites from security playbooks, discovers target components and authentication, runs attacks, assesses outcomes, and exports reports. Because it evaluates observable runtime behavior, it can help teams identify issues exposed through application interactions; it does not perform source-code static analysis. Use it only on systems for which you have explicit permission.
Deployment can be local in Docker, behind a firewall, in CI, or against external endpoints for authorized black-box assessments. Targets can be reached with a Playwright browser runner or direct HTTP API transports, including file uploads and tool calls. This gives teams options for browser-based and API targets, while requiring them to supply their own LLM API key for test generation and assessment.
Key features
Playbooks and attack strategies
Playbooks cover OWASP LLM, OWASP Agent, MITRE ATLAS, jailbreak, system prompt exfiltration, and custom scenarios. Strategies include zero-shot, few-shot, multi-shot, iterative, multimodal, jailbreak, and chain-of-thought testing. This range supports varied runtime probes without limiting teams to a single attack style.
Execution evidence and reporting
Run artifacts capture prompts, uploads, responses, and tool calls in attack_log.json. The generated pipeline_report.json provides category rollups and severity, giving reviewers material to examine after a run. Results can also be exported through AIRTA Systems’ bulk import API for review and regression tracking.
Pricing
AIRTA Red Team: free. The open-source plan has no license fee or subscription, making it suitable for teams that can operate a self-hosted assessment tool. The main cost consideration is that you must bring your own LLM API key; no trial or paid tier is needed to access the free plan.
Platforms
AIRTA Red Team supports API, Linux, macOS, web, and Windows. Its self-hosted deployment options make it a fit for teams that want to run assessments in their own environments rather than rely on a hosted testing workflow.
Who it's for
Red teams, whitehat testers, pentesters, and AppSec or MLsec teams can use it to probe authorized LLM applications and preserve run evidence. It is less suitable for teams that need static code analysis, or for organizations that depend on active maintenance and support.
Pros and cons
- Pros: Playbooks and strategies span multiple attack styles, with custom playbooks and test cases for tailored assessments.
- Pros: Browser and direct HTTP execution support a range of target interfaces, while captured run artifacts and severity rollups aid review.
- Pros: The open-source plan has no license fee or subscription.
- Cons: Users must supply an LLM API key for test generation and assessment.
- Cons: Runtime assessment does not replace source-code static analysis.
- Cons: The repository marks the project deprecated and no longer maintained, a significant concern for continued security work.
Alternatives
For a broader comparison, see AI Security Testing Tools.
- Project Moonshot is another free option with API, Linux, macOS, self-hosted, web, and Windows support; consider it if those platform options better suit your deployment.
- OpenSecureAI Scanner has a free plan and a Pro plan at $49 a month, billed $49/month, with 50,000 API requests/month and 120 requests/minute per key; choose it if those stated Pro request limits and hosted AI remediation or LLM Gateway completions match your needs.
- PromptGuard offers a free plan with 20,000 scans a month, one API key, one project, and 24-hour log retention, plus a Team plan at $19 a month; it may suit readers whose needs fit those free-plan caps.
- Promptfoo’s free Community plan includes 10k red-team probes/month, LLM evaluation features, model providers and integrations, and local or self-hosted operation; choose it if that stated probe allowance and evaluation scope fit your workflow.
- PyRIT is a free open-source framework that requires a Python environment and configured AI endpoints; consider it if that framework setup suits your team.
- Augustus is free, open-source software for Linux, macOS, self-hosted environments, and Windows; API usage may require provider credentials.
- Basilisk is free AGPL-3.0 software distributed as a CLI, desktop app, Docker image, or source, for authorized use only.
- F5 BIG-IP APM is a paid alternative with a free trial and perpetual-license availability across virtual editions, hardware, or hybrid environments.
Verdict
AIRTA Red Team is a sensible no-license-fee option for security teams that want a self-hosted runtime workflow with diverse attack strategies and inspectable run artifacts. Its key drawback is decisive for long-term adoption: the project is deprecated and no longer maintained. Choose it for authorized assessments only if your team can accept that maintenance risk and supply its own LLM API key; otherwise, consider an alternative better aligned with your support and workflow needs.
Getting started
- Open the AIRTA Red Team website or repository
- Run the tool locally in Docker, behind a firewall, or in CI
- Provide your own LLM API key for generation and assessment
- Connect a target through the Playwright runner or direct HTTP API
- Select an available or custom security playbook
- Run the authorized assessment and review the exported reports
Limits worth knowing
The free plan has no license fee or subscription, but each user supplies an LLM API key. Assessments cover observable runtime behavior and do not provide source-code static analysis.
Questions
Is AIRTA Red Team free?
Yes. The AIRTA Red Team plan costs nothing and is open source with no license fee or subscription.
Do I need my own model access?
Yes. Users provide their own LLM API key for test generation and assessment.
Where can it run?
It can run locally in Docker, behind a firewall, in CI, or against external endpoints for authorized black-box assessments.
What attacks can it test?
Listed coverage includes OWASP LLM, OWASP Agent, MITRE ATLAS, jailbreak, system-prompt exfiltration, and custom playbooks, with strategies such as zero-shot, multimodal, iterative, and chain-of-thought testing.
Is the project maintained?
The GitHub repository says AIRTA Red Team is deprecated and no longer maintained, directing users to Genbounty LLM Hunter.
Alternatives to AIRTA Red Team
- 1
OpenSecureAI Scanner
Free planOpen sourceWebAPILinuxmacOS8.1From $49 a month - 2

PromptGuard
Free planWebAPIExtensionLinux7.9From $19 a month - 3
Promptfoo
Free planOpen sourceWebAPILinuxmacOS7.8Free plan - 4
Giskard
Free planOpen sourceWebAPILinuxSelf-hosted7.6Free plan - 5
CyberSecEval
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 6
Project Moonshot
Free planWebAPILinuxmacOS6.9Free plan