OpenSecureAI Scanner
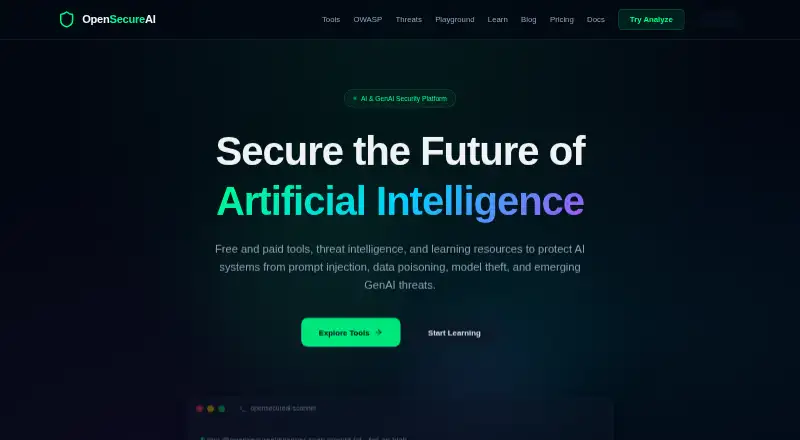
OpenSecureAI Scanner checks untrusted text for patterns linked to prompt injection, jailbreaks, system-prompt leaks, and data exfiltration.
What OpenSecureAI Scanner is
OpenSecureAI Scanner checks untrusted text for patterns linked to prompt injection, jailbreaks, system-prompt leaks, and data exfiltration. Its scanPrompt library API returns a score from 0 to 100, a risk level, and findings for individual rules. Developers can use the scanner through an npm package, CLI, GitHub Action, or REST API; the package targets Node 18+ and has no runtime dependencies. Authenticated hosted scans add checks for obfuscation, indirect injection, tool abuse, multilingual overrides, and de-obfuscation. The LLM Gateway can forward prompts to a selected OpenAI, Anthropic, xAI, or Groq provider and scan the response. Documentation says authenticated scans save a summary to the dashboard without storing raw prompt text, and gateway provider keys are not stored or logged. Free access includes 2,000 API requests per month; Pro is $49 a month. Paid checkout is not self-serve, so customers must contact sales for setup.
Good
- Detects injection, jailbreak, prompt-leak, and exfiltration patterns
- Returns a score, risk level, and per-rule findings
- Available as an npm package, CLI, GitHub Action, and REST API
- Raw prompt text is not stored for authenticated scans
Watch out
- Free API access is limited to 2,000 requests monthly
- Paid checkout requires contacting sales
- Pro costs $49 a month
Who it suits
It suits AI application teams, agent and MCP developers, security and compliance reviewers, learners, and red-teamers. Developers seeking text-scanning tools with API and command-line options may find it relevant.
Verdict
OpenSecureAI Scanner combines text-risk checks with developer-facing interfaces and an optional hosted engine. Review its free request limit and sales-led paid setup before choosing it.
Plans and prices
From OpenSecureAI Scanner's own pricing page, checked 15 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free | Free | 2,000 API requests/month · 30 requests/minute per key · browser tools and npm packages · hosted advanced engine · scan history · LLM Gateway BYOK · BYOK AI remediation · $0/month |
| Pro | $49 a month | 50,000 API requests/month · 120 requests/minute per key · hosted AI remediation · hosted LLM Gateway completions · priority email support · $49/month |
| Team | Priced on request | 250,000 API requests/month · 300 requests/minute per key · team seats and SSO planned · custom rules and SLA planned · Custom |
The facts
Each one read from OpenSecureAI Scanner's own pages, with the date it was checked.
What it does
- Agent Guard
- Agent Guard audits OpenAI, Anthropic and MCP tool definitions for excessive agency, code-execution and SSRF sinks, secret access and cross-tool exfiltration.checked 15 Oct 2026
- API
- The public REST API exposes scan, unified analysis, agent-guard, gateway, events and threat-feed endpoints.checked 15 Oct 2026
- CLI and CI
- The scanner and firewall packages include command-line interfaces, and the scanner provides a GitHub Action for pull-request gating.checked 15 Oct 2026
- Developer use
- The scanner is available as an npm package, CLI, GitHub Action, and REST API, and its package targets Node 18+ with zero runtime dependencies.checked 2 Oct 2026
- Documentation depth
- Documentation includes installation, library API, CLI flags and exit codes, GitHub Action configuration, REST examples, observability fields, system-prompt auditing and threat-feed queries.checked 15 Oct 2026
- Gateway integrations
- The gateway names OpenAI, Anthropic, xAI and Groq as supported providers and accepts customer-supplied keys.checked 15 Oct 2026
- Hosted engine
- Authenticated hosted API calls add private detections for obfuscation and encoding evasions, indirect injection, tool abuse, multilingual overrides, and de-obfuscation.checked 2 Oct 2026
- Independent domain assessment
- ScamAdviser describes opensecureai.com as very likely safe, citing valid SSL and DNSFilter safety signals.checked 15 Oct 2026
- Independent package publisher
- The npm profile aistar lists three OpenSecureAI packages: scanner 0.2.0, firewall 0.2.0 and agent-guard 0.1.0.checked 15 Oct 2026
- Independent reputation score
- Gridinsoft reports a 72/100 trust score for opensecureai.com and says no major malware or phishing detections were found.checked 15 Oct 2026
- Integrations
- The LLM Gateway can forward prompts to a selected OpenAI, Anthropic, xAI, or Groq provider/model and scan the response.checked 2 Oct 2026
- Intended users
- The maker identifies AI application teams, agent and MCP developers, security and compliance reviewers, learners, and red-teamers as audiences for its platform.checked 2 Oct 2026
- Key handling
- The docs state that LLM Gateway provider keys are never stored or logged.checked 2 Oct 2026
- License status
- OpenSecureAI says its core engine and npm packages are open source, while the hosted advanced engine contains private detections; the pages do not name a specific open-source license.checked 15 Oct 2026
- Limit: account and enterprise controls
- Team seats, SSO, custom rules and SLA support are marked planned, and paid checkout currently requires contacting sales.checked 15 Oct 2026
- Limit: domain transparency
- ScamAdviser flags free registration email addresses and low Tranco traffic rank as negative signals.checked 15 Oct 2026
- Limit: independent verification
- Gridinsoft characterizes the domain as reliable but still requiring verification rather than fully validated.checked 15 Oct 2026
- LLM Gateway
- The gateway scans an input, forwards it to a selected model provider, scans the response and can mask leaked secrets or PII or block risky traffic.checked 15 Oct 2026
- Observability
- LLM Observability aggregates injection attempts, blocks and anomalies from API events while instructing users to send labels and metadata instead of raw prompts or responses.checked 15 Oct 2026
The company
- Company founding
- OpenSecureAI states that it was founded in 2026 and launched its prompt-injection scanner and platform during 2026.checked 15 Oct 2026
- Company history
- The About page says OpenSecureAI was founded in 2026 and is global and remote-first.checked 2 Oct 2026
- Founded
- 2026checked 28 Sep 2026
- Headquarters
- The company describes itself as global and remote-first rather than listing a physical headquarters.checked 15 Oct 2026
Money
- Free access
- The maker says its in-browser tools and npm packages are free and open, and the anonymous API uses the basic engine with IP rate limiting.checked 2 Oct 2026
The full review of OpenSecureAI Scanner
Overview
OpenSecureAI Scanner screens untrusted text for prompt injection and related risks, with options for browser-based checks, developer integrations and a hosted API. It suits AI application developers and security reviewers who need a focused screening layer; its key trade-off is a small free API allowance and sales-led setup for paid plans.
The scanPrompt library returns a score from 0 to 100, a risk level and findings for individual rules. Its scope includes jailbreaks, system-prompt leaks and data-exfiltration patterns alongside prompt injection. That focus makes it useful for checking text in an AI workflow, but it should not be mistaken for comprehensive protection against every threat to an AI system.
Key features
Developers can integrate the scanner through an npm package, CLI, GitHub Action or REST API. The package targets Node 18 and later and has no runtime dependencies, making it a practical option for Node applications and build workflows. In-browser tools and npm packages are free and open. Anonymous API access uses the basic engine and is rate-limited by IP, so it is best for trying the service or modest use rather than relying on higher-volume or advanced checks.
Authenticated hosted API calls add detections for obfuscation and encoding evasions, indirect injection, tool abuse, multilingual overrides and de-obfuscation. These checks broaden coverage beyond direct, plainly worded attacks, but require an API key. The LLM Gateway can forward prompts to a selected OpenAI, Anthropic, xAI or Groq provider and scan the response, a useful fit for teams already using one of those providers.
Authenticated scans save a summary to the dashboard without storing raw prompt text. Gateway provider keys are not stored or logged. The company says it responds to vulnerability reports within 48 hours, a concrete disclosure commitment for security-conscious adopters.
Pricing
The Free plan is billed $0/month and includes 2,000 API requests/month, 30 requests/minute per key, in-browser tools and npm packages, plus the hosted advanced engine with an API key. It is a sensible starting point for learning, prototypes and low-volume evaluation, but the request cap and rate limit can constrain production use.
Pro costs $49 a month (billed $49/month). It raises the allowance to 50,000 API requests/month and 120 requests/minute per key, and includes hosted AI remediation, LLM Gateway completions and priority email support. It is the clearest fit for an individual developer or smaller team that needs more capacity and hosted features, though paid checkout is not self-serve: customers must contact sales to be set up.
Team has custom pricing and includes 250,000 API requests/month and 300 requests/minute per key. Team seats and SSO, as well as custom rules and an SLA, are planned rather than current inclusions, so the stated capacity may suit larger workloads but should not be read as a present promise of those team controls.
Platforms
OpenSecureAI Scanner is available through API, Linux, macOS, web and Windows. Its npm package and command-line options suit developer workflows, while browser tools provide a lower-friction way to try checks.
Who it's for
AI application teams, agent and MCP developers, security and compliance reviewers, learners and red-teamers are the intended audiences. Developers integrating text checks into Node projects will value the dependency-free package and multiple interfaces. Teams seeking broad security coverage beyond text scanning, or a paid plan they can activate without sales contact, should look elsewhere.
Pros and cons
Pros
- Several integration paths: npm, CLI, GitHub Action and REST API let developers place checks in applications or build workflows.
- Advanced hosted detections: Authenticated calls cover indirect injection, tool abuse and obfuscation-related evasions beyond the basic engine.
- Privacy-conscious handling: Authenticated scans retain a summary rather than raw prompt text, and Gateway provider keys are not stored or logged.
- Free ways to start: Browser tools and npm packages are free and open, with a $0/month API plan for limited hosted use.
Cons
- Free API capacity is modest: 2,000 requests/month and 30 requests/minute per key may be insufficient for sustained application traffic.
- Paid setup requires sales: Pro is not self-serve, adding friction for buyers who want to upgrade immediately.
- Team controls are planned: Seats, SSO, custom rules and SLA are not current Team inclusions.
- Focused scope: The scanner checks untrusted text patterns, not every security risk affecting AI systems.
Alternatives
PromptGuard is worth considering when a higher free scan allowance matters: its Free plan includes 20,000 scans a month, one API key, one project and 24-hour log retention. Promptfoo is a stronger fit for broader LLM evaluation and red-team probing, with a Community plan that includes 10k red-team probes/month and local or self-hosted use. Project Moonshot is a free alternative for readers who want its available API, desktop and self-hosted platform options.
AIRTA Red Team is a free, open-source option for users prepared to bring their own LLM API key. PyRIT is a free open-source framework for readers comfortable with a Python environment and configured AI endpoints. Augustus is a free Apache 2.0 option available for desktop operating systems and self-hosted use. Basilisk is another free open-source choice, with CLI, desktop, Docker or source distribution and authorized use only. F5 BIG-IP APM is a paid alternative with a free trial for readers evaluating an access-management product rather than a focused text scanner.
Browse more AI Security Testing Tools or AI Red Teaming Tools.
Verdict
OpenSecureAI Scanner is a good choice for developers and AI security teams that want to add prompt-risk checks through a lightweight package or API, especially when authenticated hosted detections and the Gateway fit their workflow. Its free tools make evaluation accessible, but the capped API plan and sales-led paid setup are real constraints; choose another option if you need broad security coverage, higher free volume or self-serve paid onboarding.
Getting started
- Open the OpenSecureAI website.
- Use the free in-browser tools or npm packages, or choose an API integration route.
- For anonymous API use, work with the basic engine and its IP rate limiting.
- For hosted advanced-engine access, use an API key.
- Contact sales to be set up on a paid plan.
Limits worth knowing
The Free plan allows 2,000 API requests per month and 30 requests per minute per key. Pro costs $49 a month and allows 50,000 API requests monthly at 120 requests per minute per key; paid checkout requires contacting sales.
Questions
Is OpenSecureAI Scanner free?
Yes. The Free plan is $0/month and includes 2,000 API requests per month, 30 requests per minute per key, in-browser tools and npm packages. The maker says the in-browser tools and npm packages are free and open.
How much does Pro cost?
Pro is $49 a month, billed at $49/month. It includes 50,000 API requests per month and 120 requests per minute per key.
What platforms and integration routes does it support?
Listed platforms are API, Linux, macOS, web and Windows. Developers can use an npm package, CLI, GitHub Action or REST API.
What does the scanner detect?
It detects prompt-injection, jailbreak, system-prompt-leak and data-exfiltration patterns in untrusted text. Authenticated hosted API calls add further detections, including indirect injection and tool abuse.
Does it store prompt text or Gateway provider keys?
Documentation says authenticated scans save a summary to the dashboard but do not store raw prompt text. Gateway provider keys are not stored or logged.
How do I get a paid plan?
Paid checkout is not self-serve yet. Customers should contact sales to be set up.
Alternatives to OpenSecureAI Scanner
- 1

PromptGuard
Free planWebAPIExtensionLinux7.9From $19 a month - 2
Promptfoo
Free planOpen sourceWebAPILinuxmacOS7.8Free plan - 3
Giskard
Free planOpen sourceWebAPILinuxSelf-hosted7.6Free plan - 4
AIRTA Red Team
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 5
CyberSecEval
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 6
Project Moonshot
Free planWebAPILinuxmacOS6.9Free plan