Augustus
Augustus is a Go-based vulnerability scanner for security professionals assessing large language models.
What Augustus is
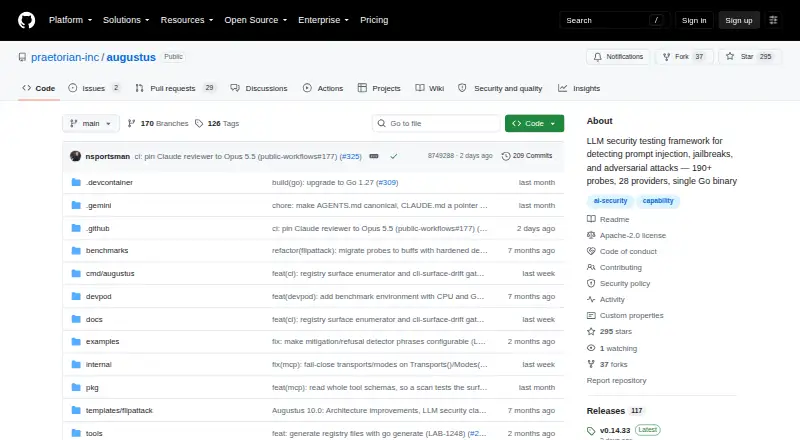
Augustus is a Go-based vulnerability scanner for security professionals assessing large language models. It tests models with adversarial attacks and produces vulnerability reports. Its coverage includes more than 210 probes across 47 categories, such as jailbreaks, prompt injection, data extraction, safety benchmarks, and agent attacks. The project supports 28 provider categories and 43 generator variants, including OpenAI, Anthropic, Azure OpenAI, AWS Bedrock, Vertex AI, Ollama, and custom REST endpoints. More than 90 detectors and seven prompt transformations support analysis. Results can be produced as tables, JSON, JSONL, or HTML reports. Augustus lists concurrent scanning, rate limiting, retries, and timeout handling among its built-in features. It is free, self-hosted, and licensed under Apache 2.0. It compiles as a portable single binary and can be installed with Go or built from source; the README requires Go 1.27.0 or later. The project is intended for authorized security testing, and users are instructed to test only systems they own or have explicit permission to assess.
Good
- Covers 47 attack categories.
- Supports 28 provider categories and 43 generator variants.
- Exports results as tables, JSON, JSONL, or HTML.
- Includes more than 90 detectors.
- Free and Apache 2.0 licensed.
Watch out
- Requires Go 1.27.0 or later.
- API usage may require provider credentials.
- For authorized testing only.
Who it suits
Augustus is for security professionals who need to scan language models for vulnerabilities. It suits teams able to install and run a self-hosted Go tool and test only with authorization.
Verdict
Augustus combines broad adversarial probe coverage with multiple provider and report options. Its Go requirement and authorized-use boundary are important considerations for security teams.
Plans and prices
From Augustus's own pricing page, checked 4 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Augustus | Free | Apache 2.0 licensed open-source software · API usage may require provider credentials |
The facts
Each one read from Augustus's own pages, with the date it was checked.
What it does
- Attack coverage
- The README describes 210+ vulnerability probes across 47 attack categories, including jailbreaks, prompt injection, data extraction, safety benchmarks, and agent attacks.checked 4 Oct 2026
- Authorized use
- The project says Augustus is designed for authorized security testing and instructs users to test only systems they own or have explicit permission to test.checked 4 Oct 2026
- Detectors
- It includes 90+ detectors such as pattern matching, LLM-as-a-judge, HarmJudge, Perspective API, and unsafe content detection.checked 4 Oct 2026
- Distribution
- Augustus compiles as a portable single binary and can be installed with Go or built from source; the README requires Go 1.27.0 or later.checked 4 Oct 2026
- Intended audience
- The README describes Augustus as built for production security testing and identifies security professionals as its users.checked 4 Oct 2026
- License
- The repository identifies Augustus as licensed under Apache 2.0.checked 4 Oct 2026
- Production features
- The project lists concurrent scanning, rate limiting, retry logic, and timeout handling as built-in production features.checked 4 Oct 2026
- Prompt transformations
- Seven prompt transformations include encoding, paraphrase, poetry, low-resource language translation, and case transforms.checked 4 Oct 2026
- Providers
- It supports 28 LLM provider categories with 43 generator variants, including OpenAI, Anthropic, Azure OpenAI, AWS Bedrock, Vertex AI, Ollama, and custom REST endpoints.checked 4 Oct 2026
- Purpose
- Augustus is a Go-based LLM vulnerability scanner for security professionals that tests models against adversarial attacks and produces vulnerability reports.checked 4 Oct 2026
- Reports
- Scan results can be output as tables, JSON, JSONL, or HTML reports.checked 4 Oct 2026
- Security reporting
- The security policy asks researchers to report vulnerabilities privately by email and says receipt will be acknowledged within 48 hours and severity assessed within 7 days.checked 4 Oct 2026
- Support
- The README directs users to open GitHub issues for bugs or feature requests and invites contributions of probes, detectors, and provider integrations.checked 4 Oct 2026
The company
- Founded
- 2010checked 28 Sep 2026
- Headquarters
- Austin, Texas, United Stateschecked 28 Sep 2026
Alternatives to Augustus
- 1
OpenSecureAI Scanner
Free planOpen sourceWebAPILinuxmacOS8.1From $49 a month - 2

PromptGuard
Free planWebAPIExtensionLinux7.9From $19 a month - 3
Promptfoo
Free planOpen sourceWebAPILinuxmacOS7.8Free plan - 4
Giskard
Free planOpen sourceWebAPILinuxSelf-hosted7.6Free plan - 5
AIRTA Red Team
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 6
CyberSecEval
Free planOpen sourceWebAPILinuxmacOS7.5Free plan