Puma Scan
Puma Scan is a static application security testing tool for C# development in Visual Studio.
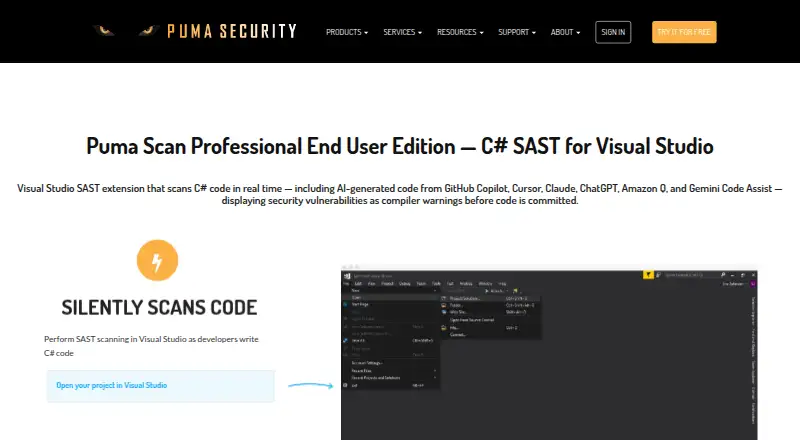
What Puma Scan is
Puma Scan is a static application security testing tool for C# development in Visual Studio. Its End User Edition checks code while developers write and reports vulnerabilities as compiler warnings before a commit. It supports C# in .NET Framework and .NET Core, including Web Forms and MVC, and the product page says it also covers AI-generated code from tools such as GitHub Copilot, Cursor, Claude, ChatGPT, Amazon Q, and Gemini Code Assist. For automated scanning, Puma Scan lists GitHub Actions, GitLab CI, and Azure DevOps integrations. CI editions can enforce severity thresholds and stop builds when requirements are not met. The Server Edition supports command-line scans, on-premises Azure DevOps build tasks, and exports findings in HTML, JSON, MSBuild, VSO, VSTest, and CSV formats. Community is free. End User is $299 a year, Server is $4,999 a year, Cloud CI Standard is $5,999 a year, and Cloud CI Unlimited is $10,999 a year, all billed annually. Trials last 30 days, require no credit card, and do not include reporting.
Good
- Scans C# code in Visual Studio as developers write.
- Can scan AI-generated code from listed coding tools.
- CI editions can stop builds at configured severity thresholds.
- Server Edition exports findings in six listed formats.
Watch out
- End User extension does not support VS Code.
- Legacy Web Site projects are unsupported.
- Trial reporting is unavailable.
- Paid editions are annual subscriptions.
Who it suits
Puma Scan is for .NET developers and security engineers working with C# in Visual Studio. Its pipeline editions are positioned for development, security, and operations teams that need automated scans and build thresholds.
Verdict
Puma Scan focuses on C# security analysis in Visual Studio, with pipeline options for automated checks and build controls. Confirm that its supported project types and editor match your development setup.
Plans and prices
From Puma Scan's own pricing page, checked 2 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Community | Free | Open source project |
| End User | $299 a year | 1 named user · up to 3 workstations · Annual subscription; license valid for one year and renewed annually |
| Server | $4,999 a year | Up to 5 build agents per license · additional bundles of 5 for $1,000 · includes 5 End User licenses · Annual renewal |
| Cloud CI Standard | $5,999 a year | Up to 20 build pipelines · includes 5 End User licenses · Annual renewal |
| Cloud CI Unlimited | $10,999 a year | Unlimited scanning within one organization · includes 5 End User licenses · Annual renewal |
The facts
Each one read from Puma Scan's own pages, with the date it was checked.
What it does
- AI-assisted code
- The product page says the scanner covers AI-generated code from GitHub Copilot, Cursor, Claude, ChatGPT, Amazon Q, and Gemini Code Assist.checked 2 Oct 2026
- CI integrations
- The maker lists GitHub Actions, GitLab CI, and Azure DevOps pipeline integrations for automated scanning.checked 2 Oct 2026
- Community edition behavior
- The Community Edition analyzers run locally in Visual Studio and do not communicate with Puma Scan servers to obtain rule updates.checked 2 Oct 2026
- Intended users
- Puma Scan describes its product as created for .NET security engineers and developers and positions pipeline editions for development, security, and operations teams.checked 2 Oct 2026
- Notable limitations
- Cross-platform code editors such as VS Code are not supported for the End User extension, and legacy Web Site projects are unsupported.checked 2 Oct 2026
- On-premises integration
- The Server Edition supports command-line scans and integration with on-premises Azure DevOps through a command-line build task.checked 2 Oct 2026
- Purpose
- Puma Scan is a static application security testing tool that scans C# code in Visual Studio and reports vulnerabilities as compiler warnings before code is committed.checked 2 Oct 2026
- Real-time scanning
- The End User Edition scans C# code in Visual Studio as developers write it.checked 2 Oct 2026
- Reports
- The Server Edition can export findings in HTML, JSON, MSBuild, VSO, VSTest, and CSV formats.checked 2 Oct 2026
- Security documentation
- The maker documents vulnerability-analysis rules and warns that static-analysis findings may include false positives and false negatives.checked 2 Oct 2026
- Security thresholds
- CI editions can apply configurable vulnerability severity thresholds and stop builds when requirements are not met.checked 2 Oct 2026
- Support
- The Professional End User Edition includes email support and scheduled telephone support; the annual subscription includes product support and updates.checked 2 Oct 2026
- Supported code
- The End User extension supports C# in .NET Framework and .NET Core, including .NET Web Forms and .NET MVC; legacy website projects are unsupported.checked 2 Oct 2026
The company
- Headquarters
- West Des Moines, Iowa, United Stateschecked 28 Sep 2026
Money
- Trial terms
- The product page offers 30-day trials with no credit card required and says reporting is unavailable during the trial.checked 2 Oct 2026
The full review of Puma Scan
Overview
Puma Scan is a static application security testing tool built around C# development in Visual Studio and security checks in CI pipelines. It is most compelling for .NET teams that want findings close to the code or build gates, but the Visual Studio extension rules out teams committed to editors such as VS Code.
Key features
The End User Edition scans C# while developers work in Visual Studio and reports vulnerabilities as compiler warnings before code is committed. That timing puts security feedback into day-to-day development, rather than leaving it until a pipeline run. It supports .NET Framework and .NET Core, including Web Forms and MVC, but not legacy Web Site projects. The editor restriction is equally important: the End User extension does not support cross-platform editors such as VS Code.
Puma Scan says its scanner covers AI-generated code from GitHub Copilot, Cursor, Claude, ChatGPT, Amazon Q, and Gemini Code Assist. That makes it relevant to teams adopting those assistants, though generated code still needs review: static analysis can produce false positives and false negatives. The maker documents its vulnerability-analysis rules, which gives security teams a basis for interpreting findings rather than treating every alert as conclusive.
For automated scanning, integrations include GitHub Actions, GitLab CI, and Azure DevOps. CI editions can apply configurable vulnerability-severity thresholds and stop builds that fail them, giving teams a way to turn policy into a build control. The Server Edition adds command-line scans and an on-premises Azure DevOps build task, and exports findings as HTML, JSON, MSBuild, VSO, VSTest, or CSV. Those controls are useful for teams that need reports and enforceable thresholds, but the more extensive pipeline options come at substantially higher annual prices than an individual Visual Studio license.
Pricing
Puma Scan has a free Community plan for open-source projects. Its analyzers run locally in Visual Studio and do not contact Puma Scan servers for rule updates, so it is a no-cost fit for eligible projects but not equivalent to a supported, regularly updated subscription.
The End User plan costs $299 a year on an annual subscription. It covers one named user on up to three workstations, with product support and updates; the Professional End User Edition also includes email and scheduled telephone support. This is the practical starting point for an individual .NET developer who wants the Visual Studio workflow without buying pipeline capacity. A 30-day trial is offered without a credit card, but reporting is unavailable during the trial.
For shared build workflows, Server costs $4,999 a year on annual renewal, covers up to five build agents, and includes five End User licenses. Additional bundles of five agents cost $1,000. Cloud CI Standard is $5,999 a year on annual renewal for up to 20 build pipelines, also with five End User licenses. Cloud CI Unlimited costs $10,999 a year on annual renewal and allows unlimited scanning within one organization, with the same five End User licenses. These plans suit teams that need centralized pipeline scanning; the choice is chiefly between Server's agent-based capacity and the cloud plans' pipeline limits. The substantial step up from the individual plan makes them difficult to justify for a solo developer or a team without build-gating needs.
Platforms
Puma Scan's End User workflow depends on Visual Studio, and the supported application code is C# in .NET Framework and .NET Core. Its deployment is hybrid, with local Visual Studio analyzers and both cloud CI and on-premises Azure DevOps options. Linux and macOS are among its listed platforms, but that does not change the End User extension's Visual Studio requirement. Teams working in VS Code or maintaining legacy Web Site projects should look elsewhere.
Who it's for
Puma Scan is aimed at .NET security engineers and developers, with its pipeline editions also positioned for development, security, and operations teams. The best fit is an organization that already builds C# applications in Visual Studio and wants either in-editor vulnerability warnings or severity-based CI controls. Its narrower editor and project support, plus the cost of pipeline editions, make it a less natural choice for mixed-language teams or small projects needing only a free general-purpose scanner.
Pros and cons
- Pros: In-editor warnings arrive before code is committed, giving Visual Studio developers an early opportunity to address vulnerabilities.
- Pros: CI integrations, configurable severity thresholds, and build stopping let teams enforce security requirements in pipelines.
- Pros: Server Edition supports on-premises Azure DevOps and several export formats, which helps teams with reporting or self-managed build workflows.
- Cons: The End User extension supports Visual Studio rather than VS Code, and excludes legacy Web Site projects.
- Cons: The Community analyzers do not obtain rule updates from Puma Scan servers, while the trial lacks reporting.
- Cons: Server and cloud CI subscriptions cost several thousand dollars annually, a steep commitment for teams that only need individual IDE scanning.
Alternatives
Compare static application security testing software if you want to weigh Puma Scan against tools with different language and workflow coverage.
- Skylos is a freemium alternative with local CLI scans and a cloud option; choose it if that CLI-and-cloud mix suits your workflow better.
- Horusec offers an Apache-licensed open-source CLI and platform, a fit for teams seeking a free open-source option.
- Semgrep Code has a free edition covering code and supply chain for up to 10 repositories and 10 contributors; consider it when those caps fit your team.
- Snyk Open Source focuses on SCA, with a free plan for five projects; choose it when dependency analysis is the priority.
- MobSF is a free, open-source option for mobile-focused platforms, including Android and iOS.
- Flawfinder is free, GPL-2.0+ open-source software for teams seeking a no-cost option across Linux, macOS, Windows, or self-hosted setups.
- OpenGrep is a free open-source static analysis CLI for Linux, macOS, and Windows.
- Bandit is free Apache-licensed software for Linux, macOS, and self-hosted environments.
Verdict
Choose Puma Scan if your team writes supported C# projects in Visual Studio and values early compiler-warning feedback or CI severity gates. Its strongest reason to buy is the combination of editor-level scanning and build controls; its strongest reason to look elsewhere is the Visual Studio and project-type constraint, compounded by the cost of pipeline plans.
Getting started
- Visit https://pumasecurity.io/product/
- Choose the free Community plan, a paid edition, or the 30-day trial
- Use the End User extension with C# projects in Visual Studio
- Connect GitHub Actions, GitLab CI, or Azure DevOps for pipeline scans
- Configure severity thresholds for CI builds when required
- Use Server command-line scans and export formats for server workflows
Limits worth knowing
The 30-day trial requires no credit card but does not provide reporting. The End User extension excludes cross-platform editors such as VS Code and legacy Web Site projects.
Questions
Is Puma Scan free?
Yes. Community is listed as free as an open-source project.
What does the End User plan cost?
End User costs $299 a year, billed as an annual subscription, for one named user and up to three workstations.
Which languages and editors does Puma Scan support?
Its analysis target is source, with one supported language: C#. IDE support is provided through Visual Studio; the End User extension does not support VS Code.
Does Puma Scan offer a free trial?
Yes. Trials last 30 days, require no credit card, and do not include reporting.
Which CI systems integrate with Puma Scan?
The listed integrations are GitHub Actions, GitLab CI, and Azure DevOps pipelines.
What are the Cloud CI prices?
Cloud CI Standard costs $5,999 a year for up to 20 build pipelines. Cloud CI Unlimited costs $10,999 a year for unlimited scanning within one organization.
Alternatives to Puma Scan
- 1
Semgrep Code
Free planOpen sourceWebAPIExtensionLinux8.3From $15 a month - 2
GitHub CodeQL
Free planWebExtensionLinuxmacOS7.5From $30 a month - 3
OpenGrep
Free planOpen sourceAPILinuxmacOSSelf-hosted7.3Free plan - 4
Bandit
Free planOpen sourceExtensionLinuxmacOSSelf-hosted7.2Free plan - 5
gosec
Free planOpen sourceAPILinuxmacOSSelf-hosted7.2Free plan - 6
Skylos
Free planWebAPIExtensionLinux7.0Free plan