Mend SAST
Mend SAST is a source-code security tool for finding vulnerabilities in code written by people or AI assistants and managing them in developer workflows.
What Mend SAST is
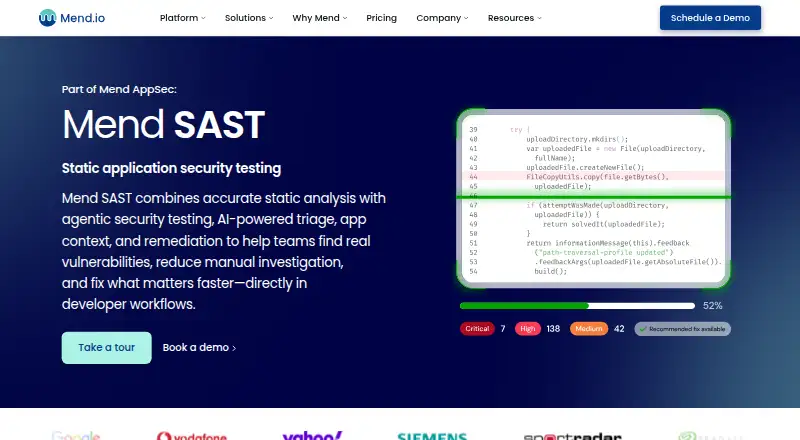
Mend SAST is a source-code security tool for finding vulnerabilities in code written by people or AI assistants and managing them in developer workflows. It supports more than 30 programming languages, including Java, JavaScript, TypeScript, Python, C#, Go, Ruby, PHP, Swift, Kotlin, and C/C++. Teams can use contextual project classification to prioritize findings based on factors such as sensitive data and critical functionality. Scanning runs on-premises or inside the customer’s environment, while findings, dashboards, and policy management run in Mend’s cloud. Mend says incremental scans of changed code can be up to 10x faster than traditional SAST tools. It detects hardcoded credentials, API keys, tokens, and certificates; detected secrets can trigger policy violations and fail a build. Integrations include IDEs, code hosts, and CI/CD tools, and vulnerability information can flow to Cursor, Windsurf, and Copilot. The Mend AppSec plan is listed at $1,000 a year, billed up to $1000 per developer per year, and includes SAST, SCA, AI-generated code security, AI-powered fix suggestions, and automated dependency updates.
Good
- Supports 30+ programming languages.
- Scans can run inside the customer’s environment.
- Detects hardcoded credentials, keys, tokens, and certificates.
- Integrates with IDEs, code hosts, and CI/CD tools.
- Developers can review and apply proposed fixes.
Watch out
- Mend AppSec is listed at $1,000 a year.
- Findings, dashboards, and policy management run in Mend’s cloud.
Who it suits
Mend SAST suits development teams that want to identify and prioritize code vulnerabilities within their workflows, including flaws in AI-generated code. Its in-environment scanning may suit teams that need proprietary source code to remain within their perimeter.
Verdict
Mend SAST combines broad language support, code scanning, contextual prioritization, and remediation guidance. Consider the hybrid handling of source code and cloud-based findings when assessing fit.
Plans and prices
From Mend SAST's own pricing page, checked 2 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Mend AppSec | $1,000 a year | Includes Mend SAST, Mend SCA, AI-generated code security, AI-powered fix suggestions, automated dependency updates · Up to $1000 per dev/per year |
The facts
Each one read from Mend SAST's own pages, with the date it was checked.
What it does
- AI code assistants
- It feeds vulnerability information to Cursor, Windsurf, and Copilot to help remediate custom code flaws in the AI workflow.checked 2 Oct 2026
- AI remediation
- Mend says its AI-powered remediation is 46% more accurate than benchmark competitors, and developers can review and apply proposed fixes.checked 2 Oct 2026
- Compliance
- Mend says its security management system incorporates ISO 27001, ISO 27017, and ISO 27701 controls, which are reviewed externally each year, and says its controls are evaluated for SOC 2 Type II.checked 2 Oct 2026
- Detection claims
- Mend says its detection starts with 38% better precision and 48% better recall than benchmark competitors.checked 2 Oct 2026
- Integrations
- The product page lists JetBrains, VS Code, Visual Studio, Cursor, Windsurf, GitHub, GitLab, Bitbucket, Azure DevOps, Jenkins, CircleCI, and GitHub Actions integrations.checked 2 Oct 2026
- Language coverage
- Mend SAST supports 30+ programming languages, including Java, JavaScript, TypeScript, Python, C#, Go, Ruby, PHP, Swift, Kotlin, and C/C++.checked 2 Oct 2026
- Purpose
- Mend SAST is a static application security testing tool for human- and AI-generated code, with vulnerability triage, contextual prioritization, and remediation in developer workflows.checked 2 Oct 2026
- Risk prioritization
- Contextual Project Classification analyzes factors such as sensitive data and critical functionality to help teams prioritize projects and findings.checked 2 Oct 2026
- Scanning speed
- Mend says incremental scans can run up to 10x faster than traditional SAST tools by analyzing changed code.checked 2 Oct 2026
- Secrets detection
- It detects hardcoded credentials, API keys, tokens, and certificates; detected secrets can trigger policy violations and fail a build.checked 2 Oct 2026
- Source code handling
- Scanning runs on-premises or inside the customer’s environment so proprietary source code stays inside its perimeter, while findings, dashboards, and policy management run in Mend’s cloud.checked 2 Oct 2026
- Support
- Mend’s site provides a support portal for opening and tracking support tickets.checked 2 Oct 2026
The company
- Company and headquarters
- Mend identifies itself as Mend.io (White Source Ltd.) and says it is headquartered in Israel.checked 2 Oct 2026
Money
- Plan inclusion
- Mend lists SAST as part of Mend AppSec, which also includes SCA, AI-generated code security, AI-powered fix suggestions, and automated dependency updates.checked 2 Oct 2026
Alternatives to Mend SAST
- 1
Semgrep Code
Free planOpen sourceWebAPIExtensionLinux8.3From $15 a month - 2
MobSF
Free planOpen sourceWebAPILinuxmacOS8.2From $2,999.99 a year - 3

GitHub CodeQL
Free planWebExtensionLinuxmacOS7.5From $30 a month - 4
gosec
Free planOpen sourceAPILinuxmacOSSelf-hosted7.2Free plan - 5
Horusec
Free planWebAPIExtensionLinux6.6Free plan - 6
Xygeni
Free planWebAPIExtensionLinux6.6Free plan