jscpd
jscpd is an open-source tool that scans repositories for repeated source code and can fail a build when duplication exceeds a configured threshold.
What jscpd is
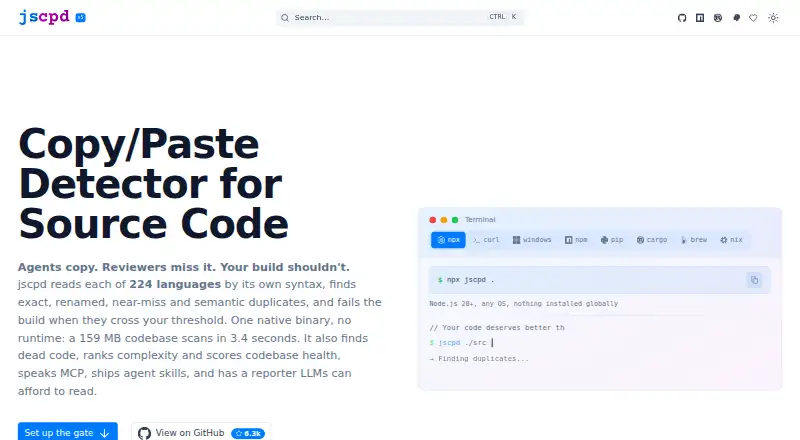
jscpd is an open-source tool that scans repositories for repeated source code and can fail a build when duplication exceeds a configured threshold. The project says it supports 224 languages. Exact clones are detected by default; optional modes cover renamed, near-miss and semantic clones, with semantic detection described as experimental. Version 5 is offered as a self-contained native binary that does not need a Node.js runtime, with direct macOS, Linux and Windows binaries, including x64 and ARM64 variants. Reports can be generated in HTML, JSON, XML, README badge, SARIF, CodeClimate and OpenMetrics formats. Its GitHub Action can enforce a threshold and upload SARIF for GitHub Code Scanning, and GitLab CI reporters are documented. Developers can also use it in pre-commit hooks through pre-commit, Husky or a shell hook, or run it in Docker. A dashboard summarizes project size, duplication, complexity, dead code and a health score. Dead-code analysis covers JavaScript, TypeScript and Python, plus Rust when compiler diagnostics are supplied. jscpd is free and open source.
Good
- Supports 224 languages, according to the project.
- Can fail builds when duplication exceeds a threshold.
- Version 5 native binary needs no Node.js runtime.
- Reports include SARIF, XML and OpenMetrics.
- GitHub Action can upload SARIF for code scanning.
Watch out
- Semantic clone detection is experimental.
- Dead-code analysis covers only listed languages.
- Rust dead-code analysis requires compiler diagnostics.
Who it suits
jscpd suits developers who want to identify repeated code in repositories during local work or CI/CD. Its threshold checks and CI integrations may be useful for teams that want builds to flag excess duplication.
Verdict
jscpd offers repository-level clone detection with several report formats and CI options. Semantic detection is experimental, and dead-code coverage varies by language.
Plans and prices
From jscpd's own pricing page, checked 29 Sep 2026.
| Plan | Price | What it gives you |
|---|---|---|
| jscpd | Free | Open-source code detector · installs via curl, PowerShell, npm, pip, cargo, Homebrew, Nix, Docker, or npx |
| jscpd open-source distribution | Free | self-hosted CLI; installation via npm, PyPI, Cargo, Homebrew, Nix, Docker or installers |
The facts
Each one read from jscpd's own pages, with the date it was checked.
What it does
- Agent skills
- Five installable skills provide workflows for duplication cleanup, dead-code removal and code migration tasks.checked 15 Oct 2026
- AI integrations
- A built-in MCP server lets Claude, Cursor, or another MCP client check code for clones, and the project provides agent skills.checked 29 Sep 2026
- API limitation
- The v5 CLI crate library target is internal and may change without notice; other languages are directed to JSON output or MCP.checked 15 Oct 2026
- CI integrations
- The official GitHub Action accepts a duplication threshold and uploads SARIF results to GitHub Code Scanning; GitLab and generic CI workflows are documented.checked 15 Oct 2026
- Clone types
- It detects exact clones by default and offers opt-in detection for renamed, near-miss, and semantic clones; semantic detection is described as experimental.checked 29 Sep 2026
- Codebase analysis
- The dashboard summarizes project size, duplication, complexity, dead code, and a health score in one run.checked 29 Sep 2026
- Codebase comparison
- Experimental compare mode pairs functions in two folders to measure porting progress or implementation parity.checked 15 Oct 2026
- Community distribution
- Open Collective says the tool is used in pipelines at Microsoft, Salesforce and Deutsche Bahn and bundled by Super-Linter, Mega-Linter and Codacy.checked 15 Oct 2026
- Complexity analysis
- The complexity mode ranks files and folders by complexity without running a clone scan.checked 15 Oct 2026
- Dashboard and health
- Dashboard and health modes combine duplication, dead-code and complexity measures into a scored project view.checked 15 Oct 2026
- Dead-code analysis
- The dead-code mode reports unused files, exports, symbols and imports for JavaScript, TypeScript and Python.checked 15 Oct 2026
- Dead-code limits
- The dashboard documentation says dead-code analysis covers JavaScript, TypeScript, and Python, plus Rust when compiler diagnostics are supplied.checked 29 Sep 2026
- Developer workflow
- It can run in pre-commit hooks through the pre-commit framework, Husky, or a shell hook.checked 29 Sep 2026
- Documentation depth
- Documentation includes installation, guides, concepts, CLI and configuration references, reporters, supported formats, Rust crates, MCP, benchmarks and migration material.checked 15 Oct 2026
- Editor integration
- The language server supplies diagnostics and navigation actions for Neovim, Helix, Sublime Text, Emacs and JetBrains editors.checked 15 Oct 2026
- Exact clones
- Default detection finds identical token sequences while ignoring whitespace, layout and comments.checked 15 Oct 2026
- Git history
- The history mode scans commits over a range and charts duplication changes over time.checked 15 Oct 2026
- Independent maintenance signal
- Snyk classified the project maintenance as healthy and reported one maintainer, active repository metadata and recent releases.checked 15 Oct 2026
- Languages
- The site says jscpd supports 224 languages.checked 29 Sep 2026
- License
- The project and its published packages use the permissive MIT license.checked 15 Oct 2026
- Limit: CI success ambiguity
- GitTested found unknown formats, missing paths, unwritable output, invalid modes and misspelled configuration keys could still exit with status zero.checked 15 Oct 2026
- Limit: human review required
- GitTested noted that jscpd identifies repeated passages but does not decide whether repetition should be refactored or retained.checked 15 Oct 2026
- Local use
- The site describes a CLI-first tool for laptops and CI/CD, and provides Docker installation.checked 29 Sep 2026
Where it runs
- Install platforms
- Official installers provide macOS and Linux shell builds plus Windows x64 and ARM64 PowerShell builds; Docker publishes amd64 and arm64 images.checked 15 Oct 2026
The full review of jscpd
Overview
jscpd is a free, open-source tool for finding duplicated code across a repository. It suits developers who want clone checks in local workflows or CI, with a configurable threshold that can fail a build. Its breadth of language support and reporting options make it flexible, though semantic clone detection remains experimental.
It uses token-based scanning and detects exact clones by default; renamed, near-miss, and semantic detection are opt-in. The project says it supports 224 languages, a useful reach for mixed-language repositories, but dead-code analysis is much narrower.
For a broader comparison, see Code Clone Detection Tools.
Key features
Clone detection and reports
Reports include HTML, JSON, XML, README badges, SARIF, CodeClimate, and OpenMetrics. That gives teams options for human-readable output, badges, and integration with automated code-analysis tools. Exact matching is the dependable default; teams considering semantic matching should treat it as experimental rather than a mature substitute for exact clone checks.
CI and developer workflows
The GitHub Action can scan a repository, enforce a duplication threshold, and upload SARIF results for GitHub Code Scanning. GitLab CI reporters are also documented. Checks can run before commits through the pre-commit framework, Husky, or a shell hook, making it possible to catch duplication earlier than a CI failure.
A built-in MCP server lets Claude, Cursor, and other MCP clients check code for clones, and the project provides agent skills. These integrations may suit teams adding clone checks to AI-assisted coding workflows, while the core threshold and reporting features remain useful without them.
Dashboard and dead-code analysis
One run can produce a dashboard summarizing project size, duplication, complexity, dead code, and a health score. Dead-code coverage is limited to JavaScript, TypeScript, and Python, with Rust support when compiler diagnostics are supplied. That makes the dashboard a useful overview for those languages, not a comprehensive dead-code analyzer for every language jscpd scans.
Pricing
jscpd is free and open source. The jscpd plan costs nothing and is described as an open-source code detector. There is no paid tier identified here, so its cost advantage comes without a trade-off between basic and premium feature sets. Installation options include curl, PowerShell, npm, pip, cargo, Homebrew, Nix, Docker, and npx.
Platforms
jscpd supports Linux, macOS, and Windows, as well as API and self-hosted use. Direct binaries are available for macOS, Linux, and Windows, including x64 and ARM64 variants. Version 5 is a self-contained native binary that does not require Node.js, reducing runtime setup for teams that prefer not to add Node to a machine. Docker installation is also provided.
Who it's for
jscpd is a strong fit for teams that want repository-wide clone detection with threshold enforcement in CI, especially when they need broad language coverage or multiple report formats. Its local CLI and pre-commit options also suit developers who want duplication checks before code reaches a shared branch.
It is less suitable as a single solution for broad dead-code analysis across many languages: that dashboard capability covers only JavaScript, TypeScript, Python, and conditionally Rust. Teams that need dependable semantic-clone detection should also be cautious, since that mode is experimental.
Pros and cons
- Pros: Free and open source, with no paid plan barrier to repository scans.
- Pros: Supports 224 languages and offers several clone modes, including opt-in renamed and near-miss detection.
- Pros: GitHub Action threshold enforcement, SARIF upload, GitLab CI reporters, and pre-commit options support checks at multiple stages.
- Pros: Native binaries for major desktop platforms, including ARM64, work without a Node.js runtime in v5.
- Cons: Semantic clone detection is experimental, so it is not the right basis for a critical semantic-analysis requirement.
- Cons: Dead-code analysis has limited language coverage compared with clone scanning.
Alternatives
PMD is another free, downloadable static code analyzer for Linux, macOS, Windows, and self-hosted use; consider it if a static analyzer better matches the workflow you need.
NiCad is free, MIT-licensed software for the same desktop and self-hosted platforms, but requires OpenTxl 11 or later; choose it if that dependency fits your environment.
Simian Similarity Analyzer is a free, open-source option for Linux, macOS, and Windows.
Duplo is free software under GNU GPL v2 or later, with prebuilt binaries for Alpine Linux, macOS, and Windows; its Alpine binary may suit users who need that platform.
art-dupl is another free option.
QuickDup is free and supports Linux, macOS, and Windows.
semdup is free and supports Linux, macOS, self-hosted, and Windows use.
dcd is free, AGPL-3.0-licensed software for Linux and macOS, with a separate priority-support plan; consider it if that platform range or support option fits your needs.
Verdict
Choose jscpd if you want a free, repository-level clone detector that can enforce duplication limits in CI and report results in formats your tooling can consume. Its broad language support, native binaries, and local-to-CI workflow are compelling strengths. Look elsewhere if broad dead-code coverage or production-ready semantic clone detection is central to your decision.