IntelOwl
IntelOwl is an open-source threat intelligence platform that enriches files and observables from multiple sources through one API.
What IntelOwl is
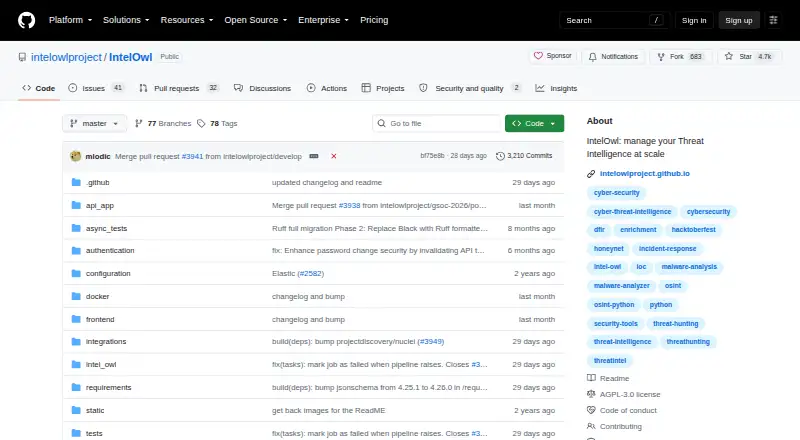
IntelOwl is an open-source threat intelligence platform that enriches files and observables from multiple sources through one API. It is described for threat hunting, security operations, incident response, threat intelligence, and vulnerability management. Users can request analyses through a web interface with dashboards and visualizations, or use its REST API and official Python and Go clients, including from the command line. A customizable plugin framework includes analyzers, connectors, pivots, visualizers, ingestors, and playbooks. Listed integrations include VirusTotal, AbuseIPDB, YARA, Oletools, ClamAV, and URLscan; connectors can send results to MISP, OpenCTI, YETI, and Slack. Deployment uses Docker Compose, with Debian-based Linux distributions, especially Ubuntu, documented as supported environments. Windows may run the software but is not officially supported; macOS requires a newer Bash than its bundled version 4 to run the startup script. IntelOwl is self-hosted and free under the AGPL-3.0 license. Its documentation recommends different compute and storage sizes for basic and intensive deployments.
Good
- Open-source and free to use.
- Provides a REST API and Python and Go clients.
- Customizable plugin framework supports multiple workflow components.
- Connectors can share results with MISP and OpenCTI.
Watch out
- Windows is not officially supported.
- macOS startup requires a newer Bash version.
- Deployment is self-hosted using Docker Compose.
Who it suits
IntelOwl suits security teams that need to enrich indicators and connect analysis to incident response, threat hunting, or related operations. It is intended for users able to deploy and maintain a self-hosted service.
Verdict
IntelOwl combines multi-source enrichment with a web interface, API, clients, and plugin-based workflows. Its self-hosted deployment and platform qualifications are important considerations for teams evaluating it.
Plans and prices
From IntelOwl's own pricing page, checked 9 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| IntelOwl | Free | Open-source solution; self-hosted deployment |
The facts
Each one read from IntelOwl's own pages, with the date it was checked.
What it does
- Analysis integrations
- The project lists integrations with services and tools including VirusTotal, AbuseIPDB, YARA, Oletools, ClamAV, and URLscan.checked 9 Oct 2026
- API and clients
- IntelOwl provides a REST API and official Python and Go clients, which can also be used from the command line.checked 9 Oct 2026
- Architecture
- The deployment includes a React frontend, Django backend, PostgreSQL database, Redis message broker, Celery task queue, and Nginx reverse proxy.checked 9 Oct 2026
- Data sharing controls
- Per-plugin maximum TLP settings govern which analyzers and connectors can run, and the documentation says RED prevents use of external services.checked 9 Oct 2026
- Deployment
- Installation uses Docker Compose and the project documents Debian-based Linux distributions, especially Ubuntu, as supported environments.checked 9 Oct 2026
- Deployment sizing
- The installation guide recommends 2 CPUs, 4 GB RAM, and 20 GB disk for a basic VM deployment, and 8 CPUs, 16 GB RAM, and 80 GB disk for intensive use.checked 9 Oct 2026
- License
- The GitHub repository identifies the project license as AGPL-3.0.checked 9 Oct 2026
- Maintainer
- The project README says management of IntelOwl has been fully in Certego's hands since version 6.8.0.checked 9 Oct 2026
- Plugin framework
- Its customizable plugins include analyzers, connectors, pivots, visualizers, ingestors, and playbooks.checked 9 Oct 2026
- Purpose
- IntelOwl is an open-source threat intelligence platform that enriches files and observables using multiple sources through a single API.checked 9 Oct 2026
- Support and consultancy
- The documentation says maintainers are available to offer paid consultancy and mentorship about deployments.checked 9 Oct 2026
- Threat sharing
- Pre-built connectors can send analysis results to MISP, OpenCTI, YETI, and Slack.checked 9 Oct 2026
- Use cases
- The project describes use cases including threat hunting, SOC operations, incident response, threat intelligence, and vulnerability management.checked 9 Oct 2026
- Web interface
- The built-in web interface includes dashboards, analysis visualizations, and forms for requesting analyses.checked 9 Oct 2026
Where it runs
- Platform limits
- The documentation says Windows may run IntelOwl but is not officially supported, and macOS requires upgrading its bundled Bash to a version newer than 4 to run the startup script.checked 9 Oct 2026
The full review of IntelOwl
IntelOwl is a threat intelligence platform for teams that need to enrich files and observables across multiple sources. It is best suited to security groups comfortable running and maintaining their own Linux deployment. Its open-source offering puts enrichment and workflow tools behind one API, but the operational footprint is substantial.
Overview
IntelOwl brings threat hunting, SOC operations, incident response, threat intelligence, and vulnerability management into a shared analysis workflow. Teams can request analyses through a web interface or REST API, or use the official Python and Go clients, including from the command line. Indicator enrichment, report management, workflow automation, and case management are included without a subscription charge.
The interface provides dashboards, analysis visualizations, and request forms. Underneath, IntelOwl combines a React frontend and Django backend with PostgreSQL, Redis, Celery, and Nginx. That gives the platform a broad working surface, but also means teams must take responsibility for deploying and maintaining several connected services. The project uses the AGPL-3.0 license, and its management has been fully in Certego's hands since version 6.8.0.
Key features
Multi-source enrichment and plugins
IntelOwl gathers analysis through one API, with integrations including VirusTotal, AbuseIPDB, YARA, Oletools, ClamAV, and URLscan. Its plugin framework covers analyzers, connectors, pivots, visualizers, ingestors, and playbooks. This flexibility is useful for teams shaping repeatable workflows around their own analysis needs; it also makes the platform a more involved choice than a narrow, ready-made lookup service.
Sharing and data controls
Pre-built connectors can send results to MISP, OpenCTI, YETI, and Slack, which helps teams move findings into collaboration and threat-sharing tools. Per-plugin maximum TLP settings govern which analyzers and connectors can run. The documentation specifies that RED prevents use of external services, an important safeguard for teams handling restricted data.
Pricing
IntelOwl is free and open source. Its IntelOwl plan costs nothing and is a self-hosted deployment, with indicator enrichment, report management, workflow automation, and case management. There is no paid tier to unlock those capabilities, but the tradeoff is that infrastructure and operational work remain with the adopting team.
The installation guide recommends 2 CPUs, 4 GB RAM, and 20 GB disk for a basic VM deployment, rising to 8 CPUs, 16 GB RAM, and 80 GB disk for intensive use. Maintainers offer paid consultancy and mentorship about deployments for teams that want specialist help.
Platforms
IntelOwl supports API, Linux, self-hosted, and web use. Installation uses Docker Compose, with Debian-based Linux distributions—especially Ubuntu—documented as supported environments. Windows may run the platform but is not officially supported. On macOS, the bundled Bash must be upgraded to a version newer than 4 to run the startup script. These qualifications make Linux the safer deployment choice, particularly for teams that do not want to troubleshoot operating-system differences.
Who it's for
IntelOwl fits security teams that need multi-source enrichment, configurable analysis pipelines, and connections to threat-sharing or collaboration tools, and that have the capacity to operate a self-hosted stack. Its range of use cases covers SOC work, threat hunting, incident response, threat intelligence, and vulnerability management. It is a poor fit for readers seeking a managed service or a deployment that avoids infrastructure ownership.
Pros and cons
- Pro: One API, a web interface, and Python and Go clients give teams several ways to request and inspect analyses.
- Pro: The plugin framework and integrations support workflows that can connect analysis to established sharing tools.
- Pro: Per-plugin TLP limits provide a way to prevent external services from handling RED data.
- Con: The multi-service Docker deployment requires meaningful capacity and ongoing administration, especially for intensive use.
- Con: Windows is not officially supported, while macOS users must adjust the bundled Bash before running the startup script.
- Con: Teams wanting deployment assistance may need paid consultancy or mentorship.
Alternatives
Threat Intelligence Platforms is a useful category overview for comparing options across the field.
Pulse Intelligence is another free, open-source self-hosted option, with API, Linux, macOS, web, and Windows platforms. Choose it instead if its Node.js 20.9+, PostgreSQL 17, and Redis-compatible-server requirements better suit your stack.
OpenAEV offers a free Community Edition for on-premise core attack simulation and tabletop exercises, with community support. It is the more relevant alternative when those are the central needs.
IBM X-Force Exchange has a free portal tier but no X-Force API access, so it may suit readers who need limited portal access rather than API-driven enrichment.
Kaspersky Threat Intelligence Portal provides free access to curated features, with limits on features and the number of suspicious files and URLs for Cloud Sandbox. Consider it when that bounded portal access is sufficient.
MISP is free, open-source software under AGPL, with a yearly support contract offered at €7.31 a year. It is an alternative for teams focused on threat sharing and prepared to evaluate its support option.
ThreatForge offers an AGPL-3.0-or-later Community Edition and a commercial Enterprise Edition. It is another open-source option for teams comparing community and commercial editions.
Security Vision TIP uses custom pricing through sales, with costs shaped by modules and products, connectors or processed events per second, additional nodes, and support level. It is an option for buyers who prefer an individually scoped commercial arrangement.
Threat Intelligence Platform offers a free subscription with 100 credits after sign-up; web analysis costs 10 credits per request and API requests cost 1–3 credits each. Its credit-based limits may suit readers who want a hosted web and API option with a defined free allowance.
Verdict
Choose IntelOwl if your security team wants flexible, multi-source enrichment and workflow control in a free, self-hosted platform—and has the Linux and operational capacity to run it. Look elsewhere if you need a managed experience, minimal infrastructure, or officially supported Windows deployment.
Getting started
- Open the IntelOwl GitHub repository
- Prepare a Debian-based Linux environment, especially Ubuntu
- Allocate the recommended CPU, memory, and disk resources
- Install and run the deployment with Docker Compose
- Use the web interface, REST API, Python client, or Go client
- Configure plugins, integrations, and TLP controls
Limits worth knowing
IntelOwl is self-hosted rather than offered as a listed hosted plan. Windows is not officially supported, and macOS requires Bash newer than version 4 for the startup script. Per-plugin maximum TLP settings can prevent analyzers or connectors from using external services, including when TLP RED is applied.
Questions
Is IntelOwl free?
Yes. The listed IntelOwl plan costs nothing, and the project is open source under AGPL-3.0.
Which platforms are supported?
IntelOwl supports API, Linux, self-hosted, and web use. Documentation focuses on Debian-based Linux, especially Ubuntu.
Can it run on Windows or macOS?
Windows may run IntelOwl but is not officially supported. macOS requires upgrading its bundled Bash to a version newer than 4.
What integrations are available?
Listed integrations include VirusTotal, AbuseIPDB, YARA, Oletools, ClamAV, URLscan, MISP, OpenCTI, YETI, and Slack.
How is IntelOwl deployed?
Installation uses Docker Compose in a self-hosted environment.
Who maintains IntelOwl?
The README says management has been fully in Certego’s hands since version 6.8.0.
Alternatives to IntelOwl
- 1
MISP
Free planOpen sourceWebAPILinuxSelf-hosted7.9From €7.31 a year - 2
Pulse Intelligence
Free planWebAPILinuxmacOS6.8Free plan - 3
Google Cloud Secret Manager
Free planWeb6.5From $0.02 a month - 4
Kaspersky Threat Intelligence Portal
Free planWebAPI6.5Free plan - 56.5From $4,550 a year
- 6
IBM X-Force Exchange
Free planWebAPI6.3Free plan