CodeRifts
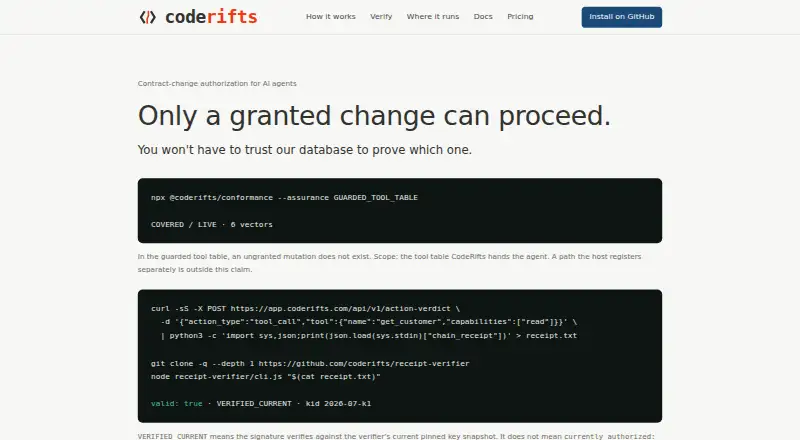
CodeRifts gives API teams a way to govern and authorize contract changes, including changes proposed by AI agents.
What CodeRifts is
CodeRifts gives API teams a way to govern and authorize contract changes, including changes proposed by AI agents. Its diff engine checks OpenAPI 3.0 and 3.1 schemas for breaking changes such as removed endpoints, newly required fields, changed response types, restricted enums, authentication changes, and modified parameters. It can find matching .yaml, .yml, and .json specifications in a repository. Security analysis flags weakened authentication, while schema scans identify new or altered fields such as SSNs, card numbers, and passports, with GDPR/CCPA warnings. Teams can set YAML policies in .coderifts.yml and block merges that breach limits, deprecation, or authentication rules. Integration options include GitHub App, GitHub Actions, GitLab CI, Bitbucket Pipelines, REST API, CLI, and an MCP server with three tools. Specifications are handled in memory and discarded after analysis; derived verdicts and metadata are retained instead. The Free plan is free, and paid plans are listed at $149 a month for Team and $1,500 a month for Enterprise.
Good
- Checks OpenAPI 3.0 and 3.1 for breaking changes
- Flags weakened authentication and sensitive schema fields
- Policies can block merges when rules are violated
- Specifications are discarded after in-memory analysis
Watch out
- No formal SLA is in place
- No SOC 2 report or third-party assessment is published
- Support has no promised response time during public beta
Who it suits
CodeRifts suits API teams that need to review schema changes, enforce contract policies, or check changes made by AI agents. Its integrations and CLI also suit teams working across supported CI and development workflows.
Verdict
CodeRifts combines schema-change detection with policy controls and options for CI and API workflows. Teams should weigh the lack of a formal SLA and published SOC 2 report against its stated data handling and governance capabilities.
Plans and prices
From CodeRifts's own pricing page, checked 30 Sep 2001.
| Plan | Price | What it gives you |
|---|---|---|
| Free | Free | public provider-verifiable boundary · 1,000 authorization cases/month · verification always free |
| Team | $149 a month | private production boundary · 10,000 authorization cases/month · $15 per 1,000 overage, prorated · free during beta |
| Enterprise | $1,500 a month | private bespoke boundary · volume-commitment authorization cases · discounted overage · unlimited users, agents and repositories · per month |
The facts
Each one read from CodeRifts's own pages, with the date it was checked.
What it does
- API limits
- The API documentation states a limit of 100 authenticated requests per API key per minute and 30 anonymous non-agent requests per IP per minute.checked 30 Sep 2001
- Breaking detection
- Its core diff engine detects breaking changes in OpenAPI 3.0 and 3.1 schemas, including endpoint removals, required-field additions, response-type changes, enum restrictions, authentication changes and parameter modifications.checked 30 Sep 2001
- CI integrations
- Documented integrations include GitHub App, GitHub Actions, GitLab CI, Bitbucket Pipelines, REST API and CLI.checked 30 Sep 2001
- CLI support
- The CLI command npx coderifts diff works anywhere Node.js runs.checked 30 Sep 2001
- Compliance
- The Trust Center states GDPR handling practices and says no SOC 2 report or third-party assessment is published.checked 30 Sep 2001
- Data handling
- CodeRifts processes API specifications in memory, discards them after analysis and persists derived verdicts and metadata rather than schema bodies or source code.checked 30 Sep 2001
- GitHub permissions
- The GitHub App requests pull-request read/write, contents read, checks write and metadata read permissions.checked 30 Sep 2001
- MCP
- The MCP server exposes three tools: preflight_change_set, verify_receipt and get_decision_details.checked 30 Sep 2001
- PII detection
- It scans new or modified schemas for fields such as SSNs, credit-card numbers and passports and flags them with GDPR/CCPA warnings.checked 30 Sep 2001
- Policy controls
- The policy engine evaluates YAML rules in .coderifts.yml and can block merges that violate limits, deprecation requirements or authentication requirements.checked 30 Sep 2001
- Purpose
- CodeRifts provides contract-change authorization and governance for AI agents and API teams.checked 30 Sep 2001
- Security analysis
- It detects authentication downgrades such as OAuth2 changes to API keys, removed bearer tokens and weakened security schemes.checked 30 Sep 2001
- Service level
- CodeRifts has no formal SLA yet and targets 99.9% uptime.checked 30 Sep 2001
- Spec discovery
- CodeRifts automatically finds OpenAPI specifications in .yaml, .yml and .json files matching its repository patterns.checked 30 Sep 2001
- Support
- Support is provided at [email protected], with no promised response time during public beta.checked 30 Sep 2001
Alternatives to CodeRifts
- 1
Karate
Free planOpen sourceAPIExtensionLinuxmacOS8.1From $8.33 a month - 2
ATA API Governance
Free planWebAPIExtensionLinux7.7From $0.88 a month - 3
Postman
Free planWebExtensionLinuxmacOS7.5From $9 a month - 4
oasdiff
Free planWebAPILinuxmacOS7.2From $100 a month - 5
Routebase
Free planWebAPILinuxmacOS7.1From $9 a month - 6
SwaggerHub
Free planWebSelf-hosted7.0From $61.67 a month