ZeroFox Attack Surface Intelligence
- Android app
- Not listed
- Free plan
- No
- Runs on
- api, Web
Summary
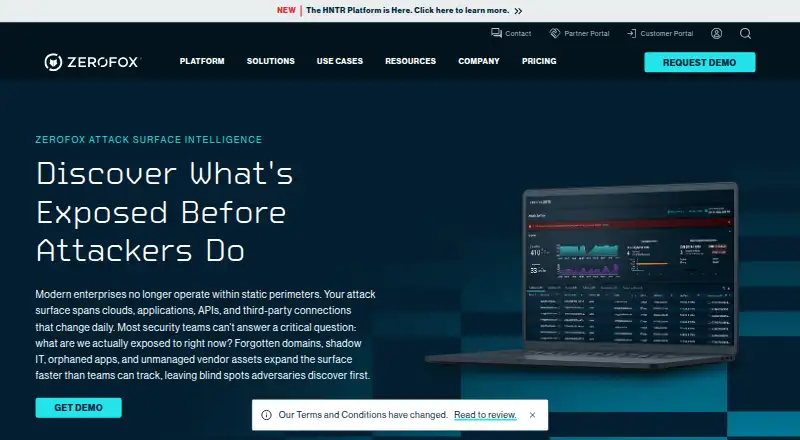
ZeroFox Attack Surface Intelligence continuously discovers and prioritizes internet-facing assets across cloud environments, applications, shadow IT, and third parties. Its inventory can cover domains, IP addresses, applications, cloud resources, APIs, SaaS exposures, and assets connected through vendors. The service combines discovery with real-time threat intelligence and AI remediation guidance. It uses EPSS, CVSS, and CISA KEV to help teams prioritize exposures, and visual maps show exposure chains and discovery paths. Monitoring can identify cloud sprawl, misconfigurations, and shadow IT across multi-cloud environments, as well as vendor risks outside a customer’s direct control. Connections include native connectors, webhooks, syslog, and REST APIs; listed integrations include Splunk, Microsoft Sentinel, ServiceNow, Jira, and Slack. The API connector can send alerts to other tools and request takedowns through an application. The product is sold as a tailored package, with pricing available on request. ZeroFox names security operations leaders, threat intelligence analysts, CISOs, cloud security engineers, and marketing teams among its intended users.
Who it is for
The product suits organizations seeking continuous visibility into internet-facing assets, cloud exposures, and vendor-connected risks. Its stated audiences include security operations leaders, threat intelligence analysts, CISOs, cloud security engineers, and marketing teams.
What is good
- Continuously monitors internet-facing assets.
- Uses EPSS, CVSS, and CISA KEV for prioritization.
- Maps exposure chains and discovery paths.
- Connects to listed security and workflow tools.
What to know first
- Pricing is available by request.
- The listed Foundation Bundle includes limited annual takedowns.
Everything Xiaomi review
ZeroFox Attack Surface Intelligence: the full review
ZeroFox Attack Surface Intelligence combines asset discovery with exposure prioritization and threat context. Teams should request a tailored quote and check whether the available bundle structure fits their needs.
ZeroFox Attack Surface Intelligence continuously maps internet-facing assets and connects exposure findings to threat context and remediation guidance. It is best suited to security teams managing broad, changing environments, including cloud, SaaS, and third-party assets. Its strongest case is the combination of discovery and risk prioritization; custom pricing and bundle options make a quote essential before budgeting.
Overview
The product inventories both known and unknown assets across domains, IPs, applications, cloud resources, APIs, SaaS exposures, and vendor-connected infrastructure. Continuous monitoring matters for organizations whose internet-facing footprint changes faster than a periodic inventory can keep up. The scope is broader than an internal asset list, but teams should expect to assess how its findings fit their own workflows and exposure priorities.
ZeroFox combines discovery with real-time threat intelligence and AI remediation guidance. EPSS, CVSS, and CISA KEV inform prioritization, helping teams focus on exposures with stronger risk signals rather than treating every finding equally. Visual mapping of exposure chains and discovery paths can help explain how assets relate, while third-party monitoring extends visibility beyond infrastructure the customer directly controls.
Key features
- External and cloud discovery: It finds cloud assets, APIs, applications, and other internet-facing resources, and detects cloud sprawl, misconfigurations, and shadow IT across multi-cloud environments. This makes it a fit for teams with fragmented infrastructure, though the breadth of findings still needs to be translated into an actionable remediation queue.
- Threat-informed prioritization: EPSS, CVSS, and CISA KEV help order exposures by risk context. Security operations teams can use that direction to triage at scale rather than relying on a flat inventory.
- Attack-path and vendor context: Exposure-chain mapping shows discovery paths, and vendor-connected asset monitoring covers risks outside direct organizational control. This is useful where third parties enlarge the effective attack surface.
- Monitoring and remediation: Monitoring is continuous and covers employee credentials, customer credentials, corporate domains, and VPN credentials. Remediation support is included; the Platform API Connector can connect alerts to other tools and request takedowns through an application.
- Integrations: Native connectors, webhooks, syslog, and REST APIs connect the product to existing systems. Named integrations include Splunk, Microsoft Sentinel, ServiceNow, Jira, and Slack, giving teams several routes to place alerts in operational workflows.
Pricing
ZeroFox Attack Surface Intelligence uses custom pricing: the tailored package requires a quote. The pricing page also describes bundles as optional, not mandatory. Its Foundation Bundle includes 2 Brand Protection, 10 Domain Protection, and 250 takedowns per year; those are bounded quantities, so teams evaluating that bundle should check whether they match their protection needs. No per-seat price or trial term is provided for Attack Surface Intelligence.
The product is paid, so it is a less direct fit for organizations seeking a self-serve free tier or a predictable published entry price. Request a tailored quote and compare the proposed scope with the assets, monitoring, and remediation capacity the team needs.
Platforms
ZeroFox supports web and API access. That combination suits teams that want a browser-based view as well as programmatic connections to security and service-management tools.
Who it's for
ZeroFox identifies security operations leaders, threat intelligence analysts, CISOs, cloud security engineers, and marketing teams as beneficiaries. It is most compelling for organizations that need continuous visibility across cloud environments, shadow IT, applications, and third parties, and that can act on prioritized findings. A team looking only for a small, low-cost inventory tool may find the tailored paid package difficult to justify.
Pros and cons
- Pro: Discovery spans known and unknown assets, cloud and SaaS exposures, and third-party assets, addressing blind spots beyond a conventional owned-asset list.
- Pro: EPSS, CVSS, CISA KEV, threat intelligence, and visual exposure mapping give teams context for deciding what to address first.
- Pro: Continuous monitoring, remediation support, and integrations support a workflow from finding exposure to routing alerts and pursuing takedowns.
- Con: Custom pricing requires a sales quote, limiting straightforward cost comparisons before scoping.
- Con: The Foundation Bundle specifies annual takedown and protection quantities, which may not fit every team's requirements even though bundles are optional.
Alternatives
Consider FullHunt if a free evaluation route is more important than ZeroFox's broader threat-context and remediation proposition: its Free plan is 0.00 USD per free, capped at 10 credits/month and limited to evaluation or internal use, while Builder is 149.00 USD. CyCognito Platform is another quote-based option, with pricing based on active IPs and web applications across stated asset-scale bands from up to 5,000 to 100,001+.
Detectify Surface Monitoring may suit a team that prefers a published annual price structure: its Starter is 0.00 EUR per year, with up to 5 users and 1 team, though Surface Monitoring costs extra per domain; Standard is 2500.00 EUR per year. Censys Attack Surface Management is a quote-required alternative priced by assets under management.
Tenable One Attack Surface Management is an alternative for teams considering a broader platform spanning IT, cloud, web applications, and OT. Qualys External Attack Surface Management offers a 30-day, 0.00 USD per free option for CSAM with EASM, making it worth considering for a time-limited evaluation. CrowdStrike Falcon Surface and Outpost24 Attack Surface Management are also alternatives; both use quote-based pricing.
For broader category comparisons, see Attack Surface Management Software and Digital Risk Protection Software.
Verdict
ZeroFox Attack Surface Intelligence is a strong choice for security organizations that need continuous external asset discovery tied to threat context, risk prioritization, and remediation support. Its breadth across cloud, SaaS, shadow IT, and third parties is the clearest reason to choose it. Look elsewhere if a published low-cost plan is a requirement; otherwise, request a tailored quote and ensure the bundle and scope fit the team’s actual needs.
ZeroFox Attack Surface Intelligence plans and pricing
All plansCompared on attack surface management software
- External asset discovery
- Yeszerofox.com
- Attack-path analysis
- Yeszerofox.com
- Cloud asset discovery
- Yeszerofox.com
- Monitoring frequency
- continuouszerofox.com
- API access
- Yeszerofox.com
Facts
- Purpose
- Continuously discovers, prioritizes, and contextualizes internet-facing assets across cloud environments, applications, shadow IT, and third parties.zerofox.com · 4 Oct 2026
- Threat context
- The product fuses asset discovery with real-time threat intelligence and AI remediation guidance.zerofox.com · 4 Oct 2026
- Asset discovery
- It inventories known and unknown assets across domains, IPs, applications, cloud resources, APIs, SaaS exposures, and third-party assets.zerofox.com · 4 Oct 2026
- Prioritization
- It uses EPSS, CVSS, and CISA KEV to help teams address high-risk exposures first.zerofox.com · 4 Oct 2026
- Visual mapping
- Visual mapping shows exposure chains and discovery paths.zerofox.com · 4 Oct 2026
- Third-party risk
- The product monitors third-party risks and vendor-connected assets beyond the customer's direct control.zerofox.com · 4 Oct 2026
- Cloud and SaaS
- It detects cloud sprawl, misconfigurations, and shadow IT across multi-cloud environments.zerofox.com · 4 Oct 2026
- Integrations
- ZeroFox says it connects through native connectors, webhooks, syslog, and REST APIs, and lists integrations including Splunk, Microsoft Sentinel, ServiceNow, Jira, and Slack.zerofox.com · 4 Oct 2026
- API capability
- The Platform API Connector can connect alerts to other tools and request takedowns through an application.zerofox.com · 4 Oct 2026
- Security certifications
- ZeroFox states that it holds SOC 2 Type II and UK Cyber Essentials certifications and participates in the EU-U.S. Data Privacy Framework and its UK and Swiss extensions.zerofox.com · 4 Oct 2026
- Trust resources
- Its Trust Center lists the SOC 2 Type II report, a 2026 Cyber Essentials certificate, and security controls including penetration testing and vulnerability monitoring procedures.trust.zerofox.com · 4 Oct 2026
- Support
- The product page advertises 24/7 technical assistance from security experts and customer success managers.zerofox.com · 4 Oct 2026
- Intended users
- The maker identifies security operations leaders, threat intelligence analysts, CISOs, cloud security engineers, and marketing teams as beneficiaries.zerofox.com · 4 Oct 2026
- Notable limits
- The pricing page lists a Foundation Bundle with 2 Brand Protection, 10 Domain Protection, and 250 takedowns per year; it also says bundles are not mandatory.zerofox.com · 4 Oct 2026
Company
- Founded
- 2013zerofox.com · 28 Sept 2026
- Headquarters
- Baltimore, Maryland, United Stateszerofox.com · 28 Sept 2026
Best ZeroFox Attack Surface Intelligence alternatives
See all 20
Where it ranks on Everything Xiaomi
Is ZeroFox Attack Surface Intelligence yours?
Claim it for free: prove the domain, then correct facts, plans and screenshots. An editor reviews every change.
Sources
- zerofox.com/solutions/attack-surface-intelligence/· checked 4 Oct 2026
- zerofox.com/solutions/attack-surface-intelligence/a· checked 4 Oct 2026
- zerofox.com/platform/integrations/· checked 4 Oct 2026
- zerofox.com/pricing/· checked 4 Oct 2026
- zerofox.com/platform/security-and-compliance/· checked 4 Oct 2026
- trust.zerofox.com· checked 4 Oct 2026