SignPath Foundation
- Android app
- Not listed
- Free plan
- Yes
- Runs on
- api, Web
Summary
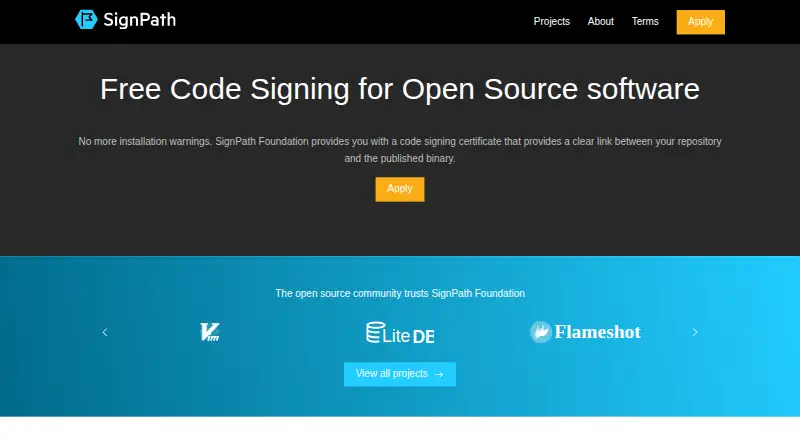
SignPath Foundation provides code-signing certificates to eligible open-source projects, linking published binaries to their source repositories. SignPath.io performs the signing and checks that each release’s signed files are automated builds from the project’s stated repository. Certificate private keys are generated and kept on a hardware security module. Every release needs manual approval, and projects must assign author, reviewer, and approver responsibilities, with a team member approving each request. Eligible projects must be actively maintained, have an existing release, use an OSI-approved open-source license, and contain neither proprietary code nor malware. Team members must use multi-factor authentication for both SignPath and repository access. Supported trusted build systems include Jenkins, GitHub, GitLab, Azure DevOps, TeamCity, and AppVeyor. The service supports signing many file types, including Windows executables, Android packages, Java archives, Debian and RPM packages, and OCI container images. Its free subscription is for eligible open-source projects. The certificate identifies SignPath Foundation as the publisher, and the Foundation can decline applications.
Who it is for
SignPath Foundation is for actively maintained, already released open-source projects that meet its eligibility and security requirements. It suits teams able to enforce multi-factor authentication and manually approve each release.
What is good
- Free subscription for eligible open-source projects.
- Private keys are protected by a hardware security module.
- Release builds are checked against the stated source repository.
- Supports multiple trusted build systems.
- Signing supports many software and package formats.
What to know first
- Every release requires manual signing approval.
- All project team members must use multi-factor authentication.
- The certificate names SignPath Foundation as publisher.
- Applications may be rejected at the Foundation’s discretion.
Verdict
SignPath Foundation offers a free code-signing route for qualifying open-source projects, with build verification and protected keys. Teams should account for the eligibility rules and manual approval process.
SignPath Foundation plans and pricing
All plansCompared on code signing software
- Free plan
- Yessignpath.org
- Supported targets
- Windows executables and scripts, MSI, CAB, AppX/MSIX, NuGet, Java archives, Android packages, RPM, Debian packages, Office macros, XML, JSON, OCI container images, ClickOnce, and arbitrary filessignpath.org
- Certificate provided
- Yessignpath.org
- Cloud signing
- Yessignpath.org
- HSM key protection
- Yessignpath.org
- Trusted timestamping
- Yessignpath.org
- CI/CD signing
- Yessignpath.org
- Approval workflows
- Yessignpath.org
Facts
- Purpose
- SignPath Foundation provides code-signing certificates to open-source projects to link published binaries to their repositories.signpath.org · 4 Oct 2026
- Signing service
- The Foundation provides certificates through SignPath.io, which performs the code signing.signpath.org · 4 Oct 2026
- Key protection
- SignPath says certificate private keys are securely generated and stored on a hardware security module.signpath.org · 4 Oct 2026
- Build verification
- For each release, SignPath.io verifies that signed files are automated builds from the project’s stated source repository.signpath.org · 4 Oct 2026
- Build integrations
- The documentation lists Jenkins, GitHub, GitLab, Azure DevOps, TeamCity, and AppVeyor as supported trusted build systems.docs.signpath.io · 4 Oct 2026
- Approval requirement
- Every release requires manual approval for signing.signpath.org · 4 Oct 2026
- Eligibility
- Eligible projects must be actively maintained, already released, use an OSI-approved open-source license, and contain no proprietary code or malware.signpath.org · 4 Oct 2026
- Team security
- All project team members must use multi-factor authentication for SignPath and source-code repository access.signpath.org · 4 Oct 2026
- Signing roles
- Projects must define author, reviewer, and approver responsibilities, and a team member must approve each signing request.signpath.org · 4 Oct 2026
- Software restrictions
- The Foundation does not sign software with features designed to identify or exploit vulnerabilities or bypass execution-environment security measures.signpath.org · 4 Oct 2026
- Certificate identity
- The Foundation certificate is issued to SignPath Foundation, which is therefore named as the software publisher.signpath.org · 4 Oct 2026
- Acceptance discretion
- The Foundation may accept or reject an application at its discretion and is under no obligation to accept a project.signpath.org · 4 Oct 2026
- Operator
- SignPath Foundation says it is currently operated by SignPath GmbH, the company behind SignPath.io.signpath.org · 4 Oct 2026
Company
- Headquarters
- Vienna, Austriasignpath.org · 28 Sept 2026
Best SignPath Foundation alternatives
See all 20
Where it ranks on Everything Xiaomi
Is SignPath Foundation yours?
Claim it for free: prove the domain, then correct facts, plans and screenshots. An editor reviews every change.
Sources
- signpath.org· checked 4 Oct 2026
- signpath.org/about· checked 4 Oct 2026
- signpath.org/terms· checked 4 Oct 2026
- docs.signpath.io/trusted-build-systems/· checked 4 Oct 2026