ShadowSecurityScanner
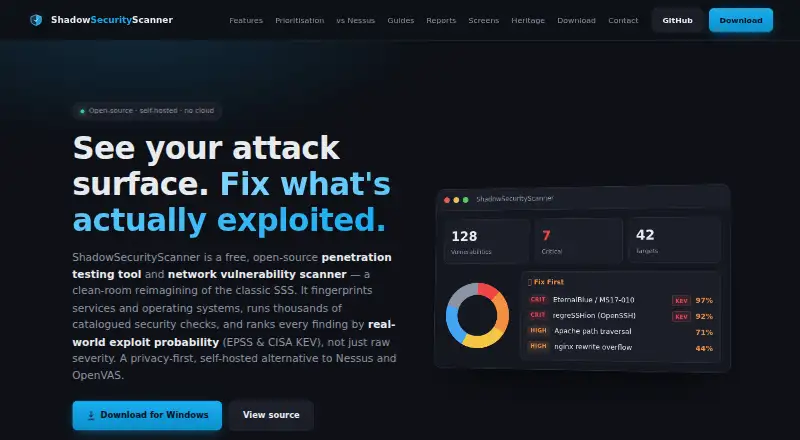
ShadowSecurityScanner is a free, open-source desktop tool for penetration testing and network vulnerability scanning.
What ShadowSecurityScanner is
ShadowSecurityScanner is a free, open-source desktop tool for penetration testing and network vulnerability scanning. It runs locally on Windows, macOS and Linux, and can scan network hosts, servers, web applications and network appliances. Its checks combine port scanning with service and operating-system fingerprinting and thousands of active network and web-application security checks. Findings receive FIRST.org EPSS scoring and are flagged against the CISA Known Exploited Vulnerabilities catalog. Scan comparison can identify findings that are new, regressed or resolved since an earlier scan. Reports can be exported as PDF, HTML, SARIF, XML or CSV; SARIF is described as suitable for GitHub code scanning. Its audit catalog refreshes from a signed update feed that includes daily CISA KEV updates, Nuclei and curated advisories. The application has no cloud component or telemetry, stores its database in the user's profile, and is distributed as one self-contained desktop app without agents or a database server. Listed requirements include Windows 10/11, macOS 11 or later for Apple Silicon, and Linux x64 or ARM64. The maker says to use it only for authorized security testing; denial-of-service tests are excluded.
Good
- Runs locally with no cloud component or telemetry.
- Compares scans to flag new, regressed and resolved findings.
- Exports PDF, HTML, SARIF, XML and CSV reports.
- No agents or database server are required.
- Free and open source.
Watch out
- Denial-of-service tests are intentionally excluded.
- macOS requirement is version 11 or later for Apple Silicon.
- Use is limited to authorized security testing.
Who it suits
It is intended for security engineers, system administrators, red teams and DevSecOps pipelines. Use it only for authorized security testing.
Verdict
ShadowSecurityScanner provides local scanning, scan comparisons and multiple report formats without requiring agents or a database server. Its stated scope excludes denial-of-service tests, and the maker limits use to authorized testing.
Plans and prices
From ShadowSecurityScanner's own pricing page, checked 8 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free | Free | Free to use · open-core model |
The facts
Each one read from ShadowSecurityScanner's own pages, with the date it was checked.
What it does
- Audit catalog
- The audit catalog refreshes from a signed update feed, including daily CISA KEV updates, Nuclei, and curated advisories.checked 8 Oct 2026
- Deployment
- It is distributed as a single self-contained desktop app with no agents or database server required.checked 8 Oct 2026
- Exploit prioritization
- Findings are scored with FIRST.org EPSS and flagged against the CISA Known Exploited Vulnerabilities catalog.checked 8 Oct 2026
- Intended users
- The maker identifies security engineers, system administrators, red teams, and DevSecOps pipelines as intended users.checked 8 Oct 2026
- Privacy
- The app runs on the user's machine, with no cloud component or telemetry, and stores its database in the user's profile.checked 8 Oct 2026
- Purpose
- ShadowSecurityScanner is a free, open-source penetration testing tool and network vulnerability scanner.checked 8 Oct 2026
- Reports and integration
- The app exports PDF, HTML, SARIF, XML, and CSV; SARIF is described as suitable for GitHub code scanning.checked 8 Oct 2026
- Scanning
- It combines automated port scanning, service and operating-system fingerprinting, and thousands of active network and web-application security checks.checked 8 Oct 2026
- Scan tracking
- Scan diffing identifies findings that are new, regressed, or resolved since a prior scan.checked 8 Oct 2026
- Support
- The maker invites questions, demos, or enterprise support inquiries and says it usually replies within a day.checked 8 Oct 2026
- Use limitation
- The maker says to use the scanner only for authorized security testing and states that denial-of-service tests are intentionally excluded.checked 8 Oct 2026
Where it runs
- Platform requirements
- The download page lists Windows 10/11, macOS 11 or later for Apple Silicon, and Linux x64 or ARM64 builds.checked 8 Oct 2026
- Supported platforms
- Native desktop downloads are listed for Windows, macOS, and Linux.checked 8 Oct 2026
Alternatives to ShadowSecurityScanner
- 1
NSAuditor AI
Free planOpen sourceAPILinuxmacOSSelf-hosted8.0From $470 a year - 2

ManageEngine Vulnerability Manager Plus
Free planWebAPILinuxmacOS7.9From $695 a year - 3
Intruder
Free planWebAPILinuxmacOS7.4Free plan - 4
ScanTitan
Free planWebAPI7.3From $119 a year - 5

OpenVAS
Free planWebAPILinuxmacOS7.2From €2,524 a year - 6
NSAuditor AI
Free planLinuxmacOSSelf-hostedWindows6.9From $470 a year