ScanTitan
ScanTitan is a cloud-based platform for vulnerability scanning and attack-surface monitoring, with malware detection and removal.
What ScanTitan is
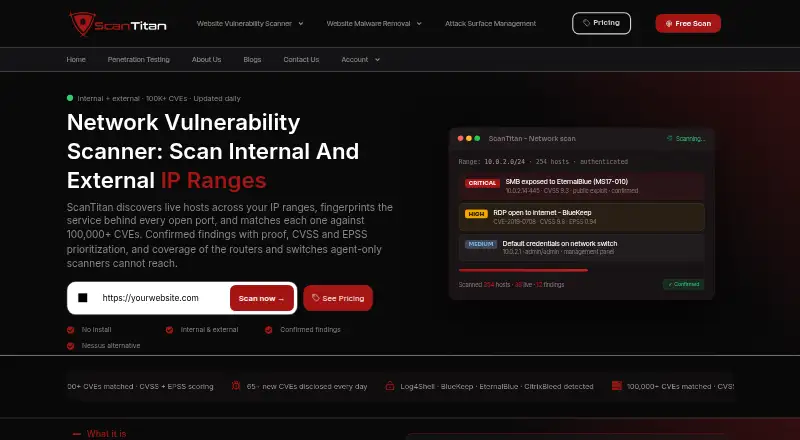
ScanTitan is a cloud-based platform for vulnerability scanning and attack-surface monitoring, with malware detection and removal. Its network scanner finds live hosts, identifies services on open ports, and checks software versions against a database containing more than 100,000 CVEs. Coverage includes known vulnerabilities, misconfigurations, weak or default credentials, network devices, SSL/TLS, and end-of-life services. Findings include reproducible request-and-response evidence and CVSS and EPSS prioritization. Reports can be exported as PDF, JSON, or HTML, with compliance exports mapped to PCI DSS 11.3, ISO 27001, SOC 2, and HIPAA. Integrations include Slack alerts, Jira ticket creation, AWS, Azure and GCP coverage, SIEM export, a REST API, and JSON webhooks. The free plan requires no credit card and has no trial expiry; Professional costs $119 a year, billed yearly. ScanTitan is available on the web and by API, and scans only customer-specified external-facing assets—not internal infrastructure or employee devices.
Good
- Checks against a database of over 100,000 CVEs
- Findings include reproducible request-and-response evidence
- Exports reports as PDF, JSON, and HTML
- Free plan has no credit card requirement or expiry
Watch out
- Does not scan internal infrastructure or employee devices
- Professional costs $119 a year, billed yearly
Who it suits
It may suit SMBs, mid-market SaaS firms, e-commerce businesses, digital agencies, and compliance-driven industries seeking scans of specified external-facing assets. The stated scope excludes internal infrastructure and employee devices.
Verdict
ScanTitan combines external asset scanning, malware tools, integrations, and compliance-oriented reporting. Its stated scanning scope is limited to customer-specified external-facing assets.
Plans and prices
From ScanTitan's own pricing page, checked 15 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free | Free | Malware scanning · Basic exposure scanning · Basic malware monitoring · Basic uptime monitoring · free forever |
| Professional | $119 a year | Advanced vulnerability scanning · Advanced exposure scanning · Advanced malware monitoring · Uptime monitoring · Vulnerability monitoring · Exposure monitoring · billed yearly |
| Business | $155 a year | 360° vulnerability scanning · 360° exposure scanning · Network exposure monitoring · Brand monitoring · Vulnerability intelligence · Exploit intelligence · API access · billed yearly |
| Consultant | $486 a year | Unlimited scans · Unlimited website add/delete · White-labeled PDF reports · API access · 360° scanning · per concurrent website |
| Enterprise | Priced on request | Threat intelligence · Custom scan limits · SLA · Dedicated support · White-label reporting · API access · custom pricing |
The facts
Each one read from ScanTitan's own pages, with the date it was checked.
What it does
- API access
- The pricing page lists API access for Business, Consultant, and Enterprise plans.checked 3 Oct 2026
- API scanning
- The API scanner imports OpenAPI, Swagger or Postman definitions and tests REST, GraphQL, SOAP and gRPC endpoints against the OWASP API Top 10.checked 15 Oct 2026
- Attack-surface management
- EASM discovers subdomains, shadow IT, open ports, certificates and cloud assets, then continuously reassesses changes and new critical CVEs.checked 15 Oct 2026
- Cloud integrations
- The attack-surface page lists AWS, Azure, GCP, Cloudflare, Slack, Jira, Vanta, Splunk and webhooks.checked 15 Oct 2026
- Confirmed findings
- The network scanner says confirmed findings include reproducible request-and-response evidence and prioritization using CVSS and EPSS.checked 3 Oct 2026
- Coverage
- The network scanner describes checks for known CVEs, misconfigurations, weak or default credentials, network devices, SSL/TLS, and end-of-life services.checked 3 Oct 2026
- Credentialed scanning
- Authenticated network scans check patches, configuration, and CIS/NIST benchmark gaps using supplied credentials.checked 15 Oct 2026
- Credential handling
- Credentials for authenticated scanning are described as encrypted in transit and used only during the active scan session, without retention afterward.checked 15 Oct 2026
- Data handling
- The company says scan findings remain in the customer account during the active plan, can be deleted on request, and are not sold or shared with third parties.checked 3 Oct 2026
- Data residency
- The security page says scan findings are stored on EU servers, encrypted at rest with AES-256 and transmitted with TLS 1.2 or higher.checked 15 Oct 2026
- Data retention
- Findings remain during an active plan, are retained for 30 days after cancellation for export, and can be deleted on request under GDPR Article 17.checked 15 Oct 2026
- Developer integrations
- Documented integrations include GitHub Actions, GitLab, Postman, Jira, Slack, Azure and JSON webhooks.checked 15 Oct 2026
- Documentation depth
- Public developer material consists mainly of curl examples, a GitHub Actions action, supported specification formats and integration descriptions rather than a separate documentation portal.checked 15 Oct 2026
- Integrations
- The network scanner lists Slack alerts, Jira ticket creation, AWS, Azure and GCP cloud coverage, SIEM export, REST API, and JSON webhooks.checked 3 Oct 2026
- Intended users
- The company identifies SMBs, mid-market SaaS firms, e-commerce businesses, digital agencies, and compliance-driven industries as intended customers.checked 3 Oct 2026
- Limit: Capterra listing
- Capterra states that no free trial and no free version are included and that pricing is contact-vendor, which differs from ScanTitan's own free plan page.checked 15 Oct 2026
- Limit: internal scope
- The about page says ScanTitan is not suitable for internal network scanning or endpoint protection, despite the network page describing an internal connector.checked 15 Oct 2026
- Limit: one-site license
- Two Entrepreneur reviewers complained that their deal license allowed only one website and one site at a time.checked 15 Oct 2026
The company
- Company focus
- LinkedIn describes ScanTitan as a cyber-exposure assessment and threat-intelligence solution for discovering and monitoring vulnerabilities on exposed systems.checked 15 Oct 2026
- Company headquarters
- LinkedIn lists headquarters in Papendrecht, South Holland, while ScanTitan's about page gives Den Haag, Netherlands as its headquarters and Dubai as a branch office.checked 15 Oct 2026
- Company size
- LinkedIn lists ScanTitan as a privately held IT services company with 2–10 employees.checked 15 Oct 2026
- Founded
- LinkedIn and ScanTitan's about page both state that the company was founded in 2014.checked 15 Oct 2026
- Headquarters
- The Hague, Netherlandschecked 28 Sep 2026
Money
- Free access
- The pricing page describes a free plan with no credit card and no trial expiry, and the contact page also offers a free domain scan without an account.checked 3 Oct 2026
Alternatives to ScanTitan
- 1
NSAuditor AI
Free planOpen sourceAPILinuxmacOSSelf-hosted8.0From $470 a year - 2

ManageEngine Vulnerability Manager Plus
Free planWebAPILinuxmacOS7.9From $695 a year - 3
Intruder
Free planWebAPILinuxmacOS7.4Free plan - 4

OpenVAS
Free planWebAPILinuxmacOS7.2From €2,524 a year - 5
NSAuditor AI
Free planLinuxmacOSSelf-hostedWindows6.9From $470 a year - 6
Nuclei
Free planLinuxmacOSSelf-hostedWindows6.8Free plan