Seemplicity Application Security
- Android app
- Not listed
- Free plan
- No
Summary
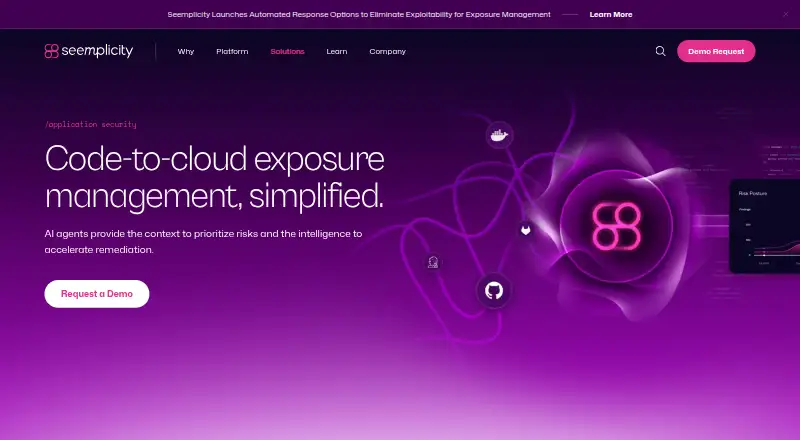
Seemplicity Application Security organizes application security findings into prioritized, fix-ready work. It correlates results from SAST, DAST, SCA, IAST, and API security tools, then uses threat intelligence and business context—including application criticality, data type, and internet-facing status—to identify reachable and exploitable vulnerabilities. AI agent teams group findings by root cause, identify a likely fixer, and route tasks into Jira or other developer ticketing tools. The product tracks remediation progress and SLA compliance across an application portfolio, and connects findings to a repository, code line where possible, and developer owner. Its dashboard maps application flaws to OWASP Top 10 and other GRC standards, while reporting offers executive and technical views. Listed integrations include GitHub Code Scanning, GitLab, Jira, Snyk, SonarQube, and Veracode; flexible APIs can power workflows. Seemplicity was founded in 2020 and is based in San Jose and Tel Aviv-Yafo. Pricing is on request.
Who it is for
It suits security, vulnerability management, DevSecOps, and GRC teams that coordinate application fixes with developers. Teams seeking to map flaws to compliance standards may also find its dashboard relevant.
What is good
- Correlates five categories of application security findings.
- Prioritizes vulnerabilities using threat and business context.
- Routes root-cause groups into developer ticketing tools.
- Tracks remediation and SLA compliance across portfolios.
- Provides OWASP and GRC coverage views.
What to know first
- Pricing is available on request.
- Technical support is provided on a reasonable-effort basis.
Verdict
Seemplicity brings finding correlation, prioritization, routing, and remediation tracking into one application security workflow. Its fit depends on whether teams need these cross-tool processes and are prepared to request pricing.
Compared on application security orchestration platforms
- Remediation workflows
- Yesseemplicity.ai
Facts
- Purpose
- Seemplicity normalizes, prioritizes, and automates application security workflows to turn findings into fix-ready tasks.seemplicity.ai · 4 Oct 2026
- Finding sources
- The product correlates findings from SAST, DAST, SCA, IAST, and API security tools.seemplicity.ai · 4 Oct 2026
- Risk prioritization
- It uses threat intelligence and business context such as application criticality, data type, and internet-facing status to identify reachable and exploitable vulnerabilities.seemplicity.ai · 4 Oct 2026
- Automated routing
- AI agent teams group findings by root cause, identify the likely fixer, and route tasks into Jira or other developer ticketing tools.seemplicity.ai · 4 Oct 2026
- Remediation tracking
- The product tracks remediation progress and SLA compliance across an application portfolio in real time.seemplicity.ai · 4 Oct 2026
- Compliance views
- Its dashboard maps application flaws to OWASP Top 10 and other GRC standards and shows coverage and exposure gaps.seemplicity.ai · 4 Oct 2026
- Code ownership context
- Seemplicity can connect findings to a code repository, line of code where possible, and developer owner.seemplicity.ai · 4 Oct 2026
- Integrations
- The integration directory lists tools including GitHub Code Scanning, GitLab, Jira, Snyk, SonarQube, and Veracode.seemplicity.ai · 4 Oct 2026
- Intended teams
- The site identifies CISOs, vulnerability management leaders, security engineering and DevSecOps, and GRC and compliance teams as audiences for its solutions.seemplicity.ai · 4 Oct 2026
- Security statement
- Seemplicity says it has taken technical and organizational measures to protect collected information from loss, misuse, unauthorized access, disclosure, alteration, destruction, and other unauthorized processing.seemplicity.ai · 4 Oct 2026
- Support
- The terms say Seemplicity provides technical support on a reasonable-effort basis under its Maintenance and Support Program.seemplicity.ai · 4 Oct 2026
- Pricing availability
- The application security page directs visitors to request a demo and does not state a product price.seemplicity.ai · 4 Oct 2026
- Tool coverage
- The product correlates findings from SAST, DAST, SCA, IAST, and API security tools.seemplicity.ai · 4 Oct 2026
- Task routing
- AI agent teams group application findings by root cause, identify a fixer, and route fix-ready tasks to Jira or other developer ticketing tools.seemplicity.ai · 4 Oct 2026
- Tracking
- The product tracks remediation progress and SLA compliance across an application portfolio in real time.seemplicity.ai · 4 Oct 2026
- Code and ownership context
- It can connect findings to a code repository, line of code where possible, and developer owner.seemplicity.ai · 4 Oct 2026
- Compliance view
- A live-updating dashboard maps application flaws to OWASP Top 10 and other GRC standards.seemplicity.ai · 4 Oct 2026
- Reporting
- The product provides flexible metrics and executive or technical views for tracking application security remediation progress.seemplicity.ai · 4 Oct 2026
- API
- The integrations page describes flexible APIs for powering workflows.seemplicity.ai · 4 Oct 2026
- Audience
- The product is presented for security and application security teams working with developers to prioritize and remediate application risks.seemplicity.ai · 4 Oct 2026
- Company security evidence
- A customer testimonial on Seemplicity’s site says the customer completed a SOC 2 Type II audit with no further auditor questions; this is a testimonial, not a stated company certification.seemplicity.ai · 4 Oct 2026
Company
- Founded
- 2020seemplicity.ai · 28 Sept 2026
- Headquarters
- San Jose, California, United States; Tel Aviv-Yafo, Israelseemplicity.ai · 28 Sept 2026
Best Seemplicity Application Security alternatives
See all 20
Where it ranks on Everything Xiaomi
Is Seemplicity Application Security yours?
Claim it for free: prove the domain, then correct facts, plans and screenshots. An editor reviews every change.
Sources
- seemplicity.ai/application-security/· checked 4 Oct 2026
- seemplicity.ai/integrations/· checked 4 Oct 2026
- seemplicity.ai/privacy-policy/· checked 4 Oct 2026
- seemplicity.ai/terms-conditions/· checked 4 Oct 2026
- seemplicity.ai/why/· checked 4 Oct 2026