rules_docker
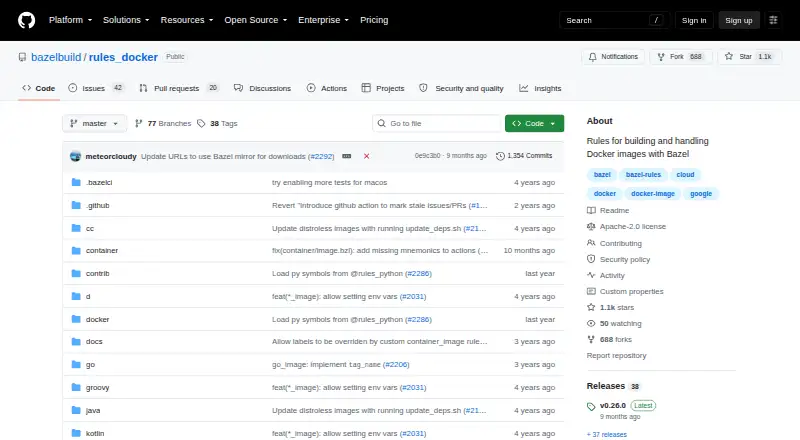
rules_docker is a set of Bazel rules for pulling base images, adding build artifacts and assets, and publishing container images.
What rules_docker is
rules_docker is a set of Bazel rules for pulling base images, adding build artifacts and assets, and publishing container images. Its basic pull, build, and push operations do not require or use Docker, and images created with container_image are described as deterministic and reproducible. Basic rules include container_image, container_bundle, container_import, container_load, container_pull, and container_push. Registry operations use google/go-containerregistry, and the README describes standard Docker authentication for private images. Language image rules cover Python, Node.js, Java, Scala, Groovy, C++, Go, Rust, and D. They use distroless language runtimes by default and allow a configurable base. Extra rules for apt-get packages or running commands inside containers need a properly configured Docker binary. The rules work on macOS without boot2docker or docker-machine and do not require workstation root access. They are free under Apache License 2.0 and maintained on an as-needed basis; the repository points to rules_oci as an alternative.
Good
- Basic image operations do not require or use Docker.
- container_image outputs are described as deterministic and reproducible.
- Includes image rules for nine programming languages.
- Does not require workstation root access.
Watch out
- Windows use is not supported.
- Extra package-install and command rules require a configured Docker binary.
- The project is maintained on an as-needed basis.
- Language image rules do not expose Docker-related attributes.
Who it suits
rules_docker suits teams using Bazel to build and publish container images, particularly those seeking basic image operations without Docker. It supports Linux and macOS use, but not Windows.
Verdict
rules_docker offers a broad set of Bazel rules for common image workflows, including daemonless basic operations. Its Windows exclusion, Docker requirement for some extra rules, and as-needed maintenance are worth considering.
Plans and prices
From rules_docker's own pricing page, checked 4 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| rules_docker | Free | Apache-2.0 · maintained on an as-needed basis · Windows is not supported |
The facts
Each one read from rules_docker's own pages, with the date it was checked.
What it does
- Container operations
- Basic rules include container_image, container_bundle, container_import, container_load, container_pull, and container_push.checked 4 Oct 2026
- Docker dependency
- The basic image pull, build, and push rules do not require or use Docker.checked 4 Oct 2026
- Language rules
- The project provides image rules for Python, Node.js, Java, Scala, Groovy, C++, Go, Rust, and D.checked 4 Oct 2026
- License
- The repository is licensed under Apache License 2.0.checked 4 Oct 2026
- Maintenance
- The repository says rules_docker is maintained on an as-needed basis and points users to rules_oci as an alternative.checked 4 Oct 2026
- Notable limitation
- The README says language image rules do not expose Docker-related attributes, so adding a custom environment variable or symlink requires using a container_image target.checked 4 Oct 2026
- Package and run rules
- Additional rules can install apt-get packages and run commands inside containers, but they require a properly configured Docker binary.checked 4 Oct 2026
- Purpose
- rules_docker is a set of Bazel rules for pulling base images, adding build artifacts and assets, and publishing container images.checked 4 Oct 2026
- Registry integration
- container_pull and container_push use google/go-containerregistry for registry interactions, and the README describes standard Docker authentication for private images.checked 4 Oct 2026
- Reproducibility
- The repository says images produced by container_image are deterministic and reproducible.checked 4 Oct 2026
- Runtime base
- Higher-level language image rules use distroless language runtimes by default, with a configurable base attribute.checked 4 Oct 2026
- Security reporting
- The security policy directs vulnerability reports to Google's g.co/vulnz intake and says the Google Security Team processes reports within a day and responds within a week, depending on severity.checked 4 Oct 2026
- Workstation access
- The README says these rules do not require root access on the workstation.checked 4 Oct 2026
Where it runs
- Platform support
- The README says the rules can be used on OSX without boot2docker or docker-machine, while Windows use is not supported.checked 4 Oct 2026
Alternatives to rules_docker
- 1
Garden
Free planOpen sourceWebAPILinuxmacOS8.3From $50 a month - 2
AWS CodeBuild
Free planWebAPILinuxmacOS7.9From $0.01 a month - 3
Amazon EC2
Free planAndroidiOSWebAPI7.6Free plan - 4
Source-to-Image
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.2Free plan - 5
Dagger
Free planWebLinuxmacOSSelf-hosted7.1From $50 a month - 6
BuildKit
Free planAPILinuxmacOSSelf-hosted6.8Free plan