PolicyForge
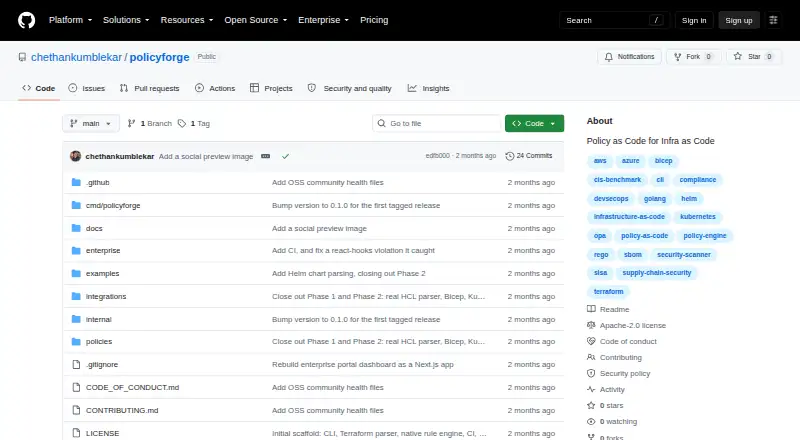
PolicyForge is an open-source policy-as-code scanner for infrastructure-as-code, aimed at teams working with Terraform, Bicep, Kubernetes manifests, or Helm …
What PolicyForge is
PolicyForge is an open-source policy-as-code scanner for infrastructure-as-code, aimed at teams working with Terraform, Bicep, Kubernetes manifests, or Helm charts. It processes these formats through a unified resource model and evaluates OPA/Rego rules with OPA. Because the policy engine is embedded at build time, scans do not require a network connection. Teams can supply additional `.rego` rules at scan time with `--policy-dir`, without forking or rebuilding. The project lists 11 built-in rules covering Azure CIS Foundations, AWS, and Kubernetes Pod Security. Each scan generates an SBOM, and the project supports SLSA provenance predicates, cosign signing, and attestations. For Azure, it compares declared infrastructure with live state through Resource Graph, limited to resource types and attributes its rules understand. CI/CD options include a GitHub Action that uploads SARIF to GitHub code scanning and an Azure DevOps task that publishes SARIF as a build artifact. An optional self-hosted portal adds dashboards, audit trails, organization-wide policy management, and SOC2/PCI compliance rollups. The core scanner, rule packs, and CI/CD integrations are Apache 2.0 open source; the portal is source-available under the same license. Helm charts require a local `helm template` command to render; without Helm, charts found are skipped with a warning.
Good
- Scans four infrastructure-as-code formats.
- Scans have no network dependency.
- Custom Rego rules can be added at scan time.
- Generates an SBOM on every scan.
- Includes GitHub Actions and Azure DevOps integrations.
Watch out
- Helm charts are skipped if Helm is unavailable.
- Azure drift checks cover only understood resource types and attributes.
- Portal retention and multi-tenancy remain unresolved questions.
Who it suits
PolicyForge may suit infrastructure teams that need policy checks across Azure and Bicep as well as Terraform, Kubernetes, or Helm. It also offers CI/CD reporting and an optional self-hosted portal.
Verdict
PolicyForge combines offline policy scanning with supply-chain outputs and CI/CD reporting. Teams using Helm need a local Helm installation, and the optional portal's listed unresolved questions merit consideration.
Plans and prices
From PolicyForge's own pricing page, checked 9 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Open source | Free | Core scanner, rule packs, and CI/CD integrations are open source under Apache 2.0 |
The facts
Each one read from PolicyForge's own pages, with the date it was checked.
What it does
- Built-in policies
- The project lists 11 built-in rules covering Azure CIS Foundations, AWS, and Kubernetes Pod Security.checked 9 Oct 2026
- CI/CD integrations
- The repository describes a GitHub Action that uploads SARIF to GitHub code scanning and an Azure DevOps task that publishes SARIF as a build artifact.checked 9 Oct 2026
- Custom rules
- Users can add `.rego` rules at scan time with `--policy-dir` without forking or rebuilding.checked 9 Oct 2026
- Drift detection
- It compares declared infrastructure code with live Azure state through Resource Graph, limited to resource types and attributes its rules understand.checked 9 Oct 2026
- Enterprise portal
- An optional self-hosted portal provides a dashboard, audit trail, org-wide policy management, and SOC2/PCI compliance rollups.checked 9 Oct 2026
- Intended users
- The project is aimed at teams scanning infrastructure-as-code, with Azure and Bicep given first-class support alongside Terraform, Kubernetes, and Helm.checked 9 Oct 2026
- License and availability
- The core scanner, rule packs, and CI/CD integrations use Apache 2.0, and the self-hosted enterprise portal is source-available under the same license.checked 9 Oct 2026
- Policy engine
- Policy rules are Rego evaluated by OPA and embedded at build time; scans have no network dependency.checked 9 Oct 2026
- Portal authentication
- The portal uses HTTP Basic Auth for ingestion and supports per-user OIDC or Entra ID SSO when configured.checked 9 Oct 2026
- Portal limitations
- The repository lists retention policy, attestation verification, and real multi-tenancy as unresolved portal questions.checked 9 Oct 2026
- Purpose
- PolicyForge is an open-source policy-as-code scanner for infrastructure-as-code.checked 9 Oct 2026
- Runtime requirements
- Helm charts are rendered through a locally installed `helm template`; without Helm, PolicyForge warns and skips charts it finds.checked 9 Oct 2026
- Supply chain
- It generates an SBOM on every scan and supports SLSA provenance predicates and cosign signing and attestations.checked 9 Oct 2026
- Supported formats
- It scans Terraform, Bicep, Kubernetes manifests, and Helm charts through a unified resource model.checked 9 Oct 2026
Alternatives to PolicyForge
- 1
Terraform
Free planWebAPILinuxmacOS8.0Free plan - 2
AWS CloudFormation
Free planiOSWebAPILinux7.7Free plan - 3
Kyverno
Free planOpen sourceWebAPILinuxmacOS7.7Free plan - 4
Open Policy Agent Gatekeeper
Free planOpen sourceAPILinuxSelf-hosted7.2Free plan - 5
Fairwinds Polaris
Free planWebLinuxmacOSSelf-hosted7.1Free plan - 6
Google Cloud Organization Policy
Free planWebAPILinuxmacOS7.1Free plan