OSForensics
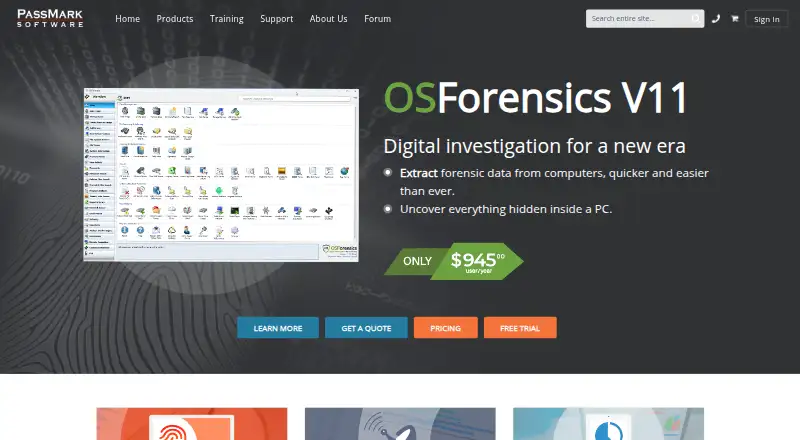
OSForensics is digital investigation software for extracting and examining forensic data from computers.
What OSForensics is
OSForensics is digital investigation software for extracting and examining forensic data from computers. It searches and indexes files, searches within documents and email archives, and attempts to recover deleted files. Hashing can verify files or compare them with known files, while extension checks can flag files whose extensions appear incorrect. The software can surface recent activity such as opened documents, web history, connected USB devices and network shares. Password tools target commonly used web browsers and can use rainbow tables to retrieve passwords from hashes. Investigators can organize evidence into case files, cryptographically hash data and export reports readable as HTML or PDF, including narratives and external reports. An automatic secure audit trail records investigation activity. Disk imaging tools create and restore images to support analysis while protecting original evidence data; the software can also run from a USB drive. Listed evidence sources include Windows, Mac, Linux, Android and iOS/macOS file systems, disk images, memory dumps, email and browser data, among others. The Free license has feature differences; the Trial Edition lasts 30 days and is feature-restricted. The subscription costs $95 per user per month.
Good
- Indexes files and searches inside documents and email archives.
- Creates disk images for analysis.
- Exports case reports in HTML and PDF.
- Can run from a portable USB drive.
Watch out
- Trial Edition is feature-restricted and lasts 30 days.
- Subscription costs $95 per user per month.
- 32-bit support is deprecated.
- Windows 7 and Windows 8 are listed among supported systems.
Who it suits
OSForensics suits investigators who need to examine computer evidence, create case reports and maintain an audit trail. Its listed evidence sources include mobile file systems, disk images and memory dumps.
Verdict
OSForensics combines evidence search, activity analysis, case reporting and disk imaging in a Windows investigation tool. Compare the feature-restricted trial and license terms with the needs of your casework.
Plans and prices
From OSForensics's own pricing page, checked 7 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| OSForensics Trial Edition | Free | Feature-restricted · 1 install · free public forum support · no upgrades · 30-day trial |
| OSForensics Free | Free | Free license; feature differences apply · Free |
| OSForensics Subscription | $95 a month | Access to latest version and updates · priority support · license stops working when subscription expires · $95.00 per user per month subscription |
| OSForensics Subscription | $945 a year | Access to latest version and updates · priority support · license stops working when subscription expires · $945.00 per user per year subscription |
| OSForensics Perpetual License (12 months support) | $1,680, paid once | Software never expires · includes 12 months of support · 2 machine installs and 1 USB install for the same user · $1680.00 per user per license |
| OSForensics Perpetual License (36 months support) | $3,675, paid once | Software never expires · includes 36 months of support · 2 machine installs and 1 USB install for the same user · $3675.00 per user per license |
| OSForensics Site License | Priced on request | Tiered by estimated users within an organization · Enquire for pricing |
The facts
Each one read from OSForensics's own pages, with the date it was checked.
What it does
- Activity analysis
- It can surface recent user activity such as opened documents, web history, connected USB devices and network shares.checked 7 Oct 2026
- Audit trail
- OSForensics can automatically maintain a secure audit trail of activities carried out during an investigation.checked 7 Oct 2026
- Case reports
- Case files group evidence, hash data cryptographically, and can be exported as HTML- and PDF-readable reports with narratives and external reports.checked 7 Oct 2026
- Drive imaging
- It creates and restores disk images to support analysis without risking the integrity of original evidence data.checked 7 Oct 2026
- Evidence identification
- It uses file hashing to verify files or match them against known files and can identify files with incorrect extensions.checked 7 Oct 2026
- Integrations and formats
- The product can read popular email formats including PST and can browse SQLite databases used by iPhone, Firefox and Chrome.checked 7 Oct 2026
- Password recovery
- Its password tools can recover passwords from commonly used web browsers and use rainbow tables to retrieve passwords from hashes.checked 7 Oct 2026
- Portability
- OSForensics can run from a portable USB drive, and the download page says it can be run from USB.checked 7 Oct 2026
- Purpose
- OSForensics is digital investigation software for extracting forensic data from computers.checked 7 Oct 2026
- Search and recovery
- It searches and indexes files, searches inside documents and email archives, and attempts to recover deleted files.checked 7 Oct 2026
- Support
- Purchases include business-hours support by phone, email or online forums; the trial edition includes free public forum support.checked 7 Oct 2026
- Supported system
- The listed system requirements include Windows 7, 8, 10, 11 and Windows Server 2012, 2016, 2019 and 2022; 32-bit support is deprecated.checked 7 Oct 2026
- Vendor location
- PassMark Software lists its Australian head office in Surry Hills, New South Wales, and a North American branch in Redwood City, California.checked 7 Oct 2026
The company
- Headquarters
- Sydney, Australiachecked 28 Sep 2026
Where it runs
- Machine requirements
- The download page lists 2 GB minimum RAM, recommends 16 GB or more, and requires 500 MB free disk space unless run from USB.checked 7 Oct 2026
The full review of OSForensics
OSForensics suits investigators who need to examine varied computer evidence and document their work in one Windows-based workflow. Its range of search, activity-review and case tools is a clear strength; its substantial license costs make it harder to justify for occasional use.
Overview
OSForensics brings file search, evidence identification, activity analysis, password recovery, disk imaging and case reporting together. It can work with evidence from Windows, Mac, Linux, Android and iOS/macOS file systems, as well as disk images, memory dumps, emails, browser data, registry hives, SQLite and ESE databases. That breadth is useful when a case crosses evidence types, though the software itself is designed for Windows.
It supports Windows 7, 8, 10 and 11, plus Windows Server 2012, 2016, 2019 and 2022; 32-bit support is deprecated. The minimum is 2 GB of RAM, with 16 GB or more recommended, and 500 MB of free disk space unless running from USB. USB portability is practical for field work, but does not change the Windows system requirement.
Key features
Search and indexing cover files, document contents and email archives, and the software attempts to recover deleted files. Hashing can verify files or match them against known files, while extension checks can flag files whose names do not match their type. These tools help narrow large evidence collections, but recovery is an attempt, not a guarantee that deleted material can be restored.
Activity analysis can surface opened documents, web history, connected USB devices and network shares, giving investigators a way to review traces of recent user activity. Password tools can recover passwords from commonly used web browsers and use rainbow tables to retrieve passwords from hashes. Their scope is specific; they should not be mistaken for a promise to unlock any account or encrypted data.
Case files group evidence, hash data cryptographically and produce reports readable as HTML or PDF, with narratives and external reports. An automatically maintained secure audit trail records investigation activity. Together, these features support a documented workflow rather than leaving findings scattered across separate searches.
Disk imaging can create and restore images so analysis can proceed without risking the integrity of original evidence. OSForensics can also browse popular email formats such as PST and SQLite databases used by iPhone, Firefox and Chrome. Export formats include HTML, PDF, CSV and MHT.
Pricing
The free plan costs nothing, with feature differences from paid editions. It is the no-cost option to consider first, but does not promise the full feature set. The OSForensics Trial Edition is also free for a 30-day trial; it is feature-restricted, allows 1 install, includes free public forum support and has no upgrades.
The Subscription costs $95 a month, billed per user per month. It includes the latest version and updates, plus priority support, but the license stops working when the subscription expires. It fits users who want current software without a perpetual purchase, provided they can accept the ongoing fee and loss of access at expiry.
The Perpetual License (12 months support) costs $1,680, paid once, per user. The software does not expire, and the license includes 12 months of support, 2 machine installs and 1 USB install for the same user. At $3,675, paid once, the Perpetual License (36 months support) offers the same install allowances, but extends included support to 36 months. These suit sustained casework better than a short-term subscription, though both require a significant upfront commitment.
The Site License uses custom pricing, tiered by estimated users within an organization. Purchases include business-hours support by phone, email or online forums; the trial has free public forum support. The published starting note of From $89/mo does not match the listed subscription price of $95 a month, so buyers should confirm the applicable quote before committing.
Platforms
The supported operating systems are Windows 7, 8, 10 and 11, and Windows Server 2012, 2016, 2019 and 2022. Although evidence sources include Mac, Linux, Android and iOS/macOS file systems, those are evidence types rather than supported desktop platforms for running OSForensics. The download can run from a USB drive, with no installation disk-space requirement in that mode.
Who it's for
OSForensics is best suited to professional investigators who regularly search mixed evidence collections, review user activity, image drives and prepare case reports. Its audit trail and report exports matter where findings need a documented record. Occasional users may find the paid licenses difficult to justify, while teams needing to run their primary forensic software on macOS or Linux should look elsewhere.
Pros and cons
- Pros: Search, activity analysis, imaging, password tools and case reporting sit in one investigation workflow, reducing the need to assemble separate tools for these tasks.
- Pros: Broad evidence sources include mobile file systems, memory dumps, emails and databases, useful for cases that span several formats.
- Pros: Cryptographic case hashing, an audit trail and HTML/PDF reports help preserve and communicate investigation work.
- Cons: The perpetual licenses cost $1,680, paid once or $3,675, paid once per user, a steep entry price for occasional work.
- Cons: The software's system requirements are Windows-only, despite its ability to process evidence from other operating systems.
- Cons: The trial is feature-restricted and lasts 30 days, so it may not represent the complete paid workflow.
Alternatives
Compare digital forensics software if you want to weigh tools across the category.
- Hayabusa is a free choice for investigators who want a tool available on Linux, macOS and Windows.
- NetworkMiner offers a free edition and GPLv2 open-source software for readers seeking an open-source alternative.
- Paraben E3 Forensic Platform is worth considering for broader platform support, with Android, iOS, Linux, macOS and Windows listed, and monthly plans starting at $60 a month.
- Plaso is a free option for readers seeking a tool available on Linux, macOS, Windows and self-hosted environments.
- Volatility 3 is a free and open-source option for readers focused on memory forensics.
- CAINE offers a free ISO image for readers who prefer a Linux and Windows forensic environment.
- Exterro FTK Imager is a free Windows-only choice when forensic imaging and preview are the priority.
- The Sleuth Kit is a free, open-source option for readers looking for forensic tools and a C library.
Verdict
Choose OSForensics if your regular Windows casework benefits from broad evidence search, activity review, imaging and documented reporting in one suite. Its strongest reason to buy is that integrated investigation workflow; its strongest reason to look elsewhere is the high per-user license cost, especially for occasional use or teams that need a non-Windows desktop platform.
Getting started
- Visit the OSForensics website
- Choose the Free license, 30-day Trial Edition, Subscription, or perpetual license
- Download for a supported Windows system or use the USB route
- Install with at least 2 GB RAM and 500 MB free disk space unless running from USB
- Create a case and add files, images, memory dumps, emails, or other supported evidence sources
Limits worth knowing
The Trial Edition lasts 30 days, is feature-restricted, allows one install, provides free public forum support, and includes no upgrades. The monthly Subscription costs $95 per user per month and stops working when the subscription expires.
Questions
Is OSForensics free?
A Free license is available at no cost. A separate Trial Edition is also free for 30 days.
What does the Subscription plan cost?
The Subscription costs $95 per user per month and includes the latest version, updates, and priority support.
Which systems are supported?
Listed systems include Windows 7, 8, 10, 11 and Windows Server 2012, 2016, 2019, and 2022. The platforms list also includes Android and self-hosted.
Can OSForensics run from USB?
Yes. It can run from a portable USB drive, and the download page describes USB use.
What reports can it export?
Case reports can be exported as HTML, PDF, CSV, or MHT files.
What evidence can it examine?
Sources include Windows, Mac, Linux, Android, iOS/macOS file systems, disk images, memory dumps, emails, browser data, registry hives, SQLite, and ESE databases.
Alternatives to OSForensics
- 1
Paraben E3 Forensic Platform
AndroidiOSLinuxmacOS7.1From $699 a year - 2
Belkasoft X Forensic
AndroidiOSLinuxmacOS6.5 - 3
MOBILedit Forensic
Windows6.4€99 one-time - 4
Cellebrite Inseyets
WebWindows6.2 - 5
SIFT Workstation
Free planLinuxSelf-hostedWindows6.2Free plan - 6
The Sleuth Kit
Free planAPILinuxmacOSSelf-hosted6.2Free plan