Hayabusa
Hayabusa is a free, open-source tool for Windows event log forensics and threat hunting.
What Hayabusa is
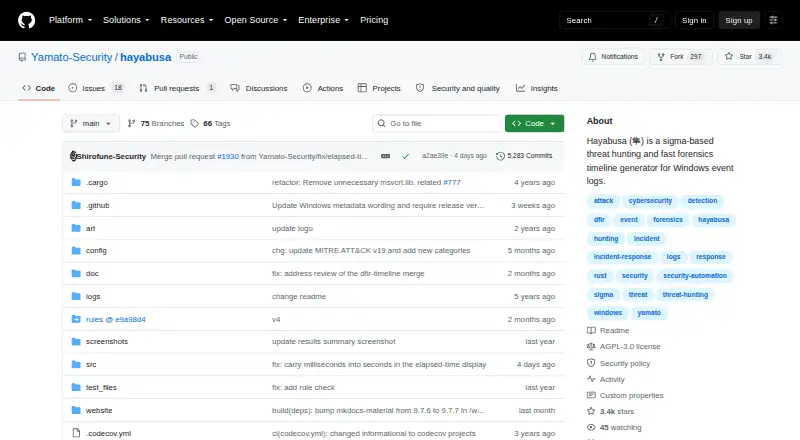
Hayabusa is a free, open-source tool for Windows event log forensics and threat hunting. It processes EVTX logs from a single host or many hosts into CSV, JSON or JSONL timelines. Analysis features include computer and event ID metrics, logon summaries, keyword pivoting, HTML summary reports and MITRE ATT&CK mapping. Hayabusa supports Sigma, including v2 correlation rules, and the project describes its curated detection rules as numbering over 4,000.
The tool can run live on one system, analyze collected logs offline or hunt across endpoints with the Velociraptor Hayabusa artifact. Results can be imported into Elastic Stack, Timesketch and Timeline Explorer; JSON can also be analyzed with jq. The project says its multithreaded Rust implementation can deliver up to a 5x speed improvement and describes Rust as memory-safe. Special Windows live-response packages bundle the binary with encoded rules and configuration files to reduce files written to a system and help avoid antivirus false positives on YAML rule files. Hayabusa runs on Windows, macOS and Linux, but has no Linux ARM MUSL binary because it does not run properly. It is released under AGPLv3, with detection rules under Detection Rule License 1.1.
Good
- Exports timelines as CSV, JSON and JSONL.
- Supports Sigma v2 correlation rules.
- Includes HTML summaries and MITRE ATT&CK mapping.
- Can hunt across endpoints with Velociraptor.
Watch out
- No Linux ARM MUSL binary is provided.
- Mobile, disk and memory forensics are not supported.
- Detection rules use a separate license.
Who it suits
Hayabusa suits people investigating Windows event logs or hunting for threats across collected logs and endpoints. It also fits workflows that use Sigma rules or the listed timeline analysis integrations.
Verdict
Hayabusa focuses on Windows event log timelines and threat hunting, with multiple analysis options and integrations. Check its platform limitation and separate detection-rule license before adopting it.
Plans and prices
From Hayabusa's own pricing page, checked 8 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Hayabusa | Free | GNU AGPLv3 software · detection rules use DRL 1.1 |
The facts
Each one read from Hayabusa's own pages, with the date it was checked.
What it does
- Analysis features
- Features include computer and event ID metrics, logon summaries, keyword pivoting, HTML summary reports, and MITRE ATT&CK mapping.checked 8 Oct 2026
- Detection rules
- The project homepage describes its curated detection rules as numbering over 4,000.checked 8 Oct 2026
- Enterprise hunting
- Hayabusa can run live on one system, analyze collected logs offline, or hunt across endpoints with the Velociraptor Hayabusa artifact.checked 8 Oct 2026
- Integrations
- The project documents importing results into Elastic Stack, Timesketch, and Timeline Explorer, and analyzing JSON with jq.checked 8 Oct 2026
- Licensing
- Hayabusa is released under AGPLv3 and its detection rules under Detection Rule License 1.1; the project says internal, SaaS, and consulting use are allowed, with a request to open-source improvements made for SaaS use.checked 8 Oct 2026
- Live response
- Special Windows live response packages bundle the binary, XOR-encoded rules, and configuration files to reduce files written to the system and help avoid antivirus false positives on YAML rule files.checked 8 Oct 2026
- Purpose
- Hayabusa is a Windows event log forensics timeline generator and threat hunting tool.checked 8 Oct 2026
- Security
- Hayabusa is written in Rust, which the project describes as memory-safe.checked 8 Oct 2026
- Sigma support
- Hayabusa supports the Sigma specification, including v2 correlation rules.checked 8 Oct 2026
- Speed
- The project says its Rust implementation is multi-threaded and can deliver up to a 5x speed improvement.checked 8 Oct 2026
- Support
- The maintainers invite bug reports through GitHub and say the project is actively maintained and they are happy to fix reported bugs.checked 8 Oct 2026
- Timeline output
- It consolidates events from one host or thousands into CSV, JSON, or JSONL timelines.checked 8 Oct 2026
Where it runs
- Platform limit
- The project says it does not provide a Linux ARM MUSL binary because it does not run properly.checked 8 Oct 2026
- Platforms
- The project lists Windows, Linux, and macOS support, with binaries for those operating systems.checked 8 Oct 2026
The full review of Hayabusa
Hayabusa is a Windows event-log timeline and threat-hunting tool for investigators and defenders working with EVTX data. It is a strong fit for focused log analysis across individual machines or endpoint fleets, but not for teams seeking a broad forensic suite.
Overview
Hayabusa can run live on one system, examine logs collected for offline analysis, or hunt across endpoints using the Velociraptor Hayabusa artifact. That flexibility makes it useful for both a single-host investigation and larger hunts without changing its core focus: Windows event logs.
The project says its multithreaded Rust implementation can deliver up to a 5x speed improvement. Treat that as a stated maximum, not a result to expect on every dataset. Rust’s memory-safety properties are relevant for software processing security evidence, though they do not replace operational safeguards.
Key features
Timelines and detection
Hayabusa consolidates events from one host or thousands into CSV, JSON, or JSONL timelines. It supports the Sigma specification, including v2 correlation rules, and its curated detection rules number over 4,000. This is a substantial set of hunting capabilities at no software charge; the separate detection-rule license still matters for adoption.
Investigation tools and integrations
Computer and event ID metrics, logon summaries, keyword pivoting, HTML summary reports, and MITRE ATT&CK mapping help analysts move from a large event stream toward relevant activity. Results can be imported into Elastic Stack, Timesketch, or Timeline Explorer, while jq can be used to analyze JSON. Those options suit teams already working with these tools, but do not amount to case collaboration, which Hayabusa does not provide.
Live-response packaging
Special Windows live-response packages bundle the executable with XOR-encoded rules and configuration files. The approach is intended to reduce files written to the system and help avoid antivirus false positives on YAML rules, a practical consideration for response work on Windows endpoints.
Pricing
Hayabusa costs nothing under GNU AGPLv3; detection rules use DRL 1.1. There are no paid software tiers described, so the free plan is the tool itself rather than a limited entry level. The maintainers say internal, SaaS, and consulting use are allowed, and ask users to open-source improvements made for SaaS use. Organizations should assess both licenses, especially the distinct rule terms, before distributing or building a service around it.
Platforms
Hayabusa supports Windows, macOS, and Linux, with Windows event logs (EVTX) as its evidence source. One concrete limitation is that the project does not provide a Linux ARM MUSL binary because it does not run properly. Hayabusa does not offer mobile forensics, disk imaging, memory forensics, or case collaboration, so it should complement rather than replace tools for those needs.
Who it's for
Incident responders and threat hunters who need to turn EVTX collections into timelines, apply Sigma rules, and work across one or many endpoints are the clearest audience. It is also a sensible option for teams that want open-source event-log analysis and can work within AGPLv3 and DRL 1.1. Investigators needing broader evidence acquisition, mobile or memory analysis, or shared case management should choose a more comprehensive toolset.
Pros and cons
- Pros: Generates CSV, JSON, and JSONL timelines from one host or thousands, giving analysts flexible output for different workflows.
- Pros: Sigma v2 correlation support and over 4,000 curated rules provide meaningful detection coverage without a software fee.
- Pros: Live, offline, and Velociraptor-based endpoint hunting support several investigation scales.
- Cons: Its scope is limited to Windows event-log evidence; it does not cover disk, memory, or mobile forensics.
- Cons: No case collaboration is provided, leaving teams to handle shared investigation workflows elsewhere.
- Cons: The rules have a separate license from the software, and Linux ARM MUSL is unsupported.
Alternatives
For a broader directory of tools in this category, see Digital Forensics Software.
- NetworkMiner is another free-plan, open-source option, with source written in managed C# on the Microsoft .NET Framework and released under GPLv2.
- OSForensics is worth considering if you want a Windows option with a free edition and a 30-day trial edition.
- Paraben E3 Forensic Platform offers a broader platform across Windows, macOS, Linux, iOS, and Android, with paid monthly plans beginning at $60 a month.
- Plaso is a free alternative for readers comparing forensic timeline tools.
- Volatility 3 is a free, open-source option to consider for a different forensic workflow.
- CAINE is a free ISO-based option for readers who prefer a Linux- and Windows-supported environment.
- Exterro FTK Imager is a Windows-only option for forensic imaging and preview, with a free plan and a paid Pro plan.
- Arkime is a free, open-source alternative for readers seeking a Linux, self-hosted, web, or API-oriented tool.
Verdict
Choose Hayabusa if Windows event logs are central to your investigations and you want flexible timelines, extensive Sigma-based hunting, and live or fleet-level workflows without a software fee. Its focused capabilities and multiple analysis paths are compelling; look elsewhere if you need disk, memory, or mobile forensics, case collaboration, or cannot accept the separate detection-rule license.
Getting started
- Open the Hayabusa project website on GitHub.
- Choose a Windows, macOS, or Linux route for your environment.
- Use Hayabusa live on a Windows system or analyze collected EVTX logs offline.
- For endpoint hunting, use the Velociraptor Hayabusa artifact.
- Export timelines as CSV, JSON, or JSONL and send results to a documented integration if needed.
Limits worth knowing
Hayabusa is free software under GNU AGPLv3, and its detection rules use DRL 1.1. The project does not provide a Linux ARM MUSL binary because it does not run properly.
Questions
How much does Hayabusa cost?
The listed Hayabusa plan costs nothing.
Is Hayabusa open source?
Yes. The software is released under AGPLv3, while detection rules use Detection Rule License 1.1.
Which platforms does it support?
Hayabusa supports Windows, macOS, and Linux. The project does not provide a Linux ARM MUSL binary.
What log source and export formats does it use?
It analyzes Windows event logs in EVTX format and can create CSV, JSON, and JSONL timelines.
What tools can use its results?
The project documents importing results into Elastic Stack, Timesketch, and Timeline Explorer, and analyzing JSON with jq.
Can Hayabusa be used for live or endpoint hunting?
It can run live on one system, analyze collected logs offline, or hunt across endpoints with the Velociraptor Hayabusa artifact.
Alternatives to Hayabusa
- 1

Arkime
Free planOpen sourceWebAPILinuxSelf-hosted7.3Free plan - 2
Plaso
Free planOpen sourceAPILinuxmacOSSelf-hosted7.3Free plan - 3
CAINE
Free planOpen sourceLinuxSelf-hostedWindows7.1Free plan - 4
Paraben E3 Forensic Platform
AndroidiOSLinuxmacOS7.1From $699 a year - 5
OSForensics
Free planAndroidSelf-hostedWindows7.0From $945 a year - 6
NetworkMiner
Free planLinuxmacOSWindows6.9$1,300 one-time