Malwagon
Malwagon is a cloud-based malware analysis sandbox for examining suspicious files and activity.
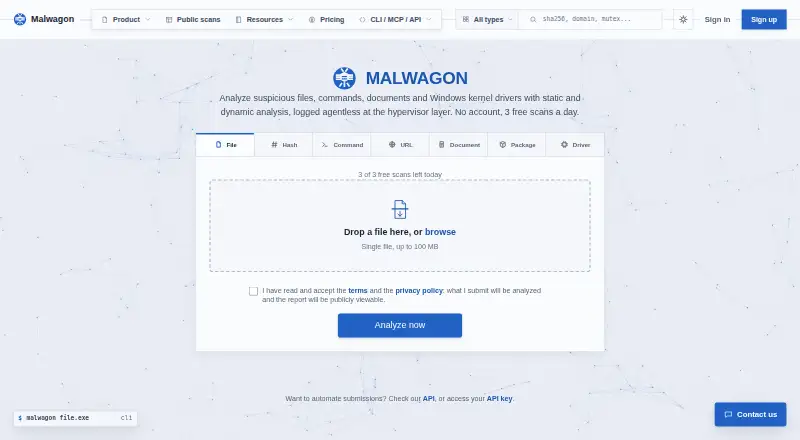
What Malwagon is
Malwagon is a cloud-based malware analysis sandbox for examining suspicious files and activity. It accepts executables and archives up to 128 MB, URLs, shell commands, office and PDF documents, Windows kernel drivers, pip packages and file hashes. Each analysis runs in its own virtual machine under a kernel-level hypervisor, then the machine is discarded. Static checks include YARA, signature scanning, disassembly, secrets scanning and configuration extraction; dynamic analysis records kernel telemetry, memory forensics and network activity. Results provide scored verdicts with evidence and can include MITRE ATT&CK mappings, generated detection rules and exports such as STIX 2.1, MISP, PDF and DOCX. Malwagon offers a REST API, MCP server and Python CLI. Free-tier reports are public; paid plans can make reports private, and Ultra Privacy deletes stored scan data after analysis. Malwagon is aimed at incident responders, detection engineers, SOC analysts and threat researchers.
Good
- Accepts files, URLs, commands, documents and packages.
- Analysis runs in a separate virtual machine.
- Reports can include ATT&CK mappings and detection rules.
- REST API, MCP server and Python CLI are available.
Watch out
- Free-tier reports are publicly viewable.
- Free Scan limits submissions to three per source address daily.
- Archives and executables are limited to 128 MB.
- Private reports require a paid plan.
Who it suits
It suits security teams and researchers who need to analyze suspicious files, URLs or commands and review evidence-backed results. Unauthenticated users can also submit untrusted attachments and read reports.
Verdict
Malwagon brings static and dynamic analysis, evidence-backed verdicts and exportable detection outputs into one service. Check the report visibility and scan limits that apply to the plan you choose.
Plans and prices
From Malwagon's own pricing page, checked 15 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Community | Free | 20 scan credits/month · 120-second runs · Windows 10 and Ubuntu 24.04 · 1 concurrent scan · public reports |
| Free scan | Free | 3 scans per source address per day · Windows 10 22H2 · network isolated · public report · no account |
| Pro | $79 a month | 200 credits/month · 300-second runs · 7 sandboxes · 3 concurrent scans · private reports · API and MCP · $79/mo; $790/yr billed yearly |
| Business | $199 a month | 500 credits/month · 600-second runs · 7 sandboxes · 5 concurrent scans · private reports · API and MCP · $199/mo; $1,990/yr billed yearly |
| Team / Enterprise | Priced on request | 5,000 credits/month · 600-second runs · 7 sandboxes · 10 concurrent scans · 10 seats · shared pool · role management |
The facts
Each one read from Malwagon's own pages, with the date it was checked.
What it does
- Account security
- The service documents 12-character minimum passwords, TOTP two-factor authentication, sign-in rate limiting and revocable API tokens.checked 15 Oct 2026
- AI data boundary
- The AI narrative receives locally derived summaries, API-call sequences, indicators and extracted strings rather than sample bytes.checked 15 Oct 2026
- Analysis layers
- Static analysis includes YARA, capability identification, obfuscated-string recovery, packer and entropy checks, signature scanning, disassembly, secrets scanning and configuration extraction.checked 30 Sep 2026
- API upload limit
- The API has a file-upload route, but the documentation says the MCP server cannot upload bytes and other API submissions name targets as text.checked 15 Oct 2026
- CLI
- The Python CLI installs with pip, has no dependencies, runs on Linux, macOS and Windows, and returns exit codes for clean, malicious, suspicious and error results.checked 15 Oct 2026
- CLI licence
- The PyPI package identifies itself as MIT licensed and OSI-approved.checked 15 Oct 2026
- CLI maintainer
- PyPI lists one maintainer, zecrain, and credits Malwagon as the author.checked 15 Oct 2026
- CLI release
- PyPI lists version 0.1.3 uploaded on September 7, 2026, with a 0.1.2 release also dated September 7, 2026.checked 15 Oct 2026
- CLI runtime
- The PyPI package requires Python 3.8 or newer and is classified for Windows, macOS, Linux/POSIX and Python 3.checked 15 Oct 2026
- Command analysis
- Command analysis executes PowerShell, CMD and bash text after local decoding of common obfuscation forms.checked 15 Oct 2026
- Data handling
- Malwagon says submitted samples stay on its infrastructure; external reputation services receive only hashes and derived indicators.checked 15 Oct 2026
- Detection outputs
- Reports can export ATT&CK Navigator, STIX 2.1, MISP, defanged IOC, PDF and DOCX formats, plus generated YARA, Sigma and Suricata rules.checked 15 Oct 2026
- Document analysis
- Document analysis opens Office, PDF, RTF, OneNote, CHM and web-container formats in the application that owns the format.checked 15 Oct 2026
- Documentation depth
- The documentation covers submission modules, analysis options, report interpretation, exports, visibility, retention, REST endpoints, MCP methods, errors and rate limits.checked 15 Oct 2026
- Dynamic analysis
- Dynamic analysis records ETW kernel telemetry, memory forensics, hypervisor introspection, network capture and JA3/JA4 fingerprints.checked 30 Sep 2026
- File analysis
- File analysis supports PE, DLL, .NET, ELF, Go, scripts and archives up to 128 MB, with static and dynamic analysis.checked 15 Oct 2026
- Hypervisor isolation
- Each analysis runs in its own full virtual machine under a kernel-level hypervisor, and the machine is discarded after the run.checked 30 Sep 2026
- Integrations
- The service provides a bearer-token REST API, an MCP server at https://malwagon.com/mcp, and a Python CLI installable with pip.checked 30 Sep 2026
- Internet egress
- Internet-connected detonation is a paid-plan, per-scan option; anonymous and Community runs remain network isolated.checked 15 Oct 2026
- Isolation
- Each analysis runs in its own virtual machine under a kernel-level hypervisor and the machine is discarded after the run.checked 15 Oct 2026
- Kernel-driver analysis
- Windows kernel drivers receive static BYOVD analysis covering their control interface, signing and known-abuse status; they are not kernel-detonated.checked 15 Oct 2026
Where it runs
- CLI platforms
- The Malwagon CLI has no dependencies and runs on Linux, macOS and Windows.checked 30 Sep 2026
The company
- Company founding
- No founding year is stated on the reviewed official pages or the PyPI project page.checked 15 Oct 2026
- Company headquarters
- No headquarters location is stated on the reviewed official pages or the PyPI project page.checked 15 Oct 2026
The full review of Malwagon
Malwagon is a cloud malware-analysis service for examining suspicious files, links, commands and packages. It suits incident responders and detection teams that need both behavioral evidence and outputs they can take into security workflows. Its strongest case is broad analysis with API access; public reports make the free plans unsuitable for confidential samples.
Overview
Malwagon analyzes submissions in isolated virtual machines and returns scored verdicts with evidence. It accepts executables and archives up to 128 MB, URLs, PowerShell, CMD and bash commands, office and PDF documents, Windows kernel drivers, pip packages, and MD5, SHA-1 or SHA-256 hashes. That range is useful when an investigation begins with something other than a conventional executable.
Every run gets its own full virtual machine under a kernel-level hypervisor, which is discarded after analysis. Samples remain on Malwagon-operated infrastructure; third parties receive hashes and derived indicators for reputation lookups, while the AI layer receives locally derived summaries rather than sample bytes. That handling is paired with an important plan distinction: free-tier reports are public, paid plans can keep reports private, and Ultra Privacy deletes stored scan data after analysis. Teams working with sensitive material should not treat a free account as a private workspace.
Key features
Static analysis combines YARA, capability identification, obfuscated-string recovery, packer and entropy checks, signature scanning, disassembly, secrets scanning and configuration extraction. This gives analysts several complementary ways to inspect a sample before relying on observed behavior, though the value is greatest for readers able to interpret technical evidence.
Dynamic analysis captures ETW kernel telemetry, memory forensics, hypervisor introspection and network activity, including JA3/JA4 fingerprints. Reports can map findings to MITRE ATT&CK and generate YARA, Sigma and Suricata rules. Exports to ATT&CK Navigator, STIX 2.1, MISP, defanged IOC lists, PDF and DOCX make results more portable than a report confined to the service.
A bearer-token REST API, MCP server and Python CLI provide options for automation and developer workflows. The CLI has no dependencies and runs on Linux, macOS and Windows. These interfaces are a practical advantage for teams that want analysis in existing processes; they matter less to occasional users who only need a one-off report.
Pricing
The Free scan option costs nothing and allows three scans per source address per day, with Windows 10 22H2, no internet egress and public reports. It is a narrow route to quick triage, not a confidential or broadly configurable service.
Community also costs nothing, but provides 20 scan credits per month, 120-second runs, Windows 10 and Ubuntu 24.04, one concurrent scan and public reports. Its monthly credits and two sandboxes are more useful for recurring community analysis, but public visibility and short runs are real constraints.
Pro costs $79 a month, billed $790/yr billed yearly. It raises the allowance to 200 scan credits per month and 300-second runs, includes all seven sandboxes, three concurrent scans, private reports, REST API and MCP access. This is the clearest fit for individual analysts or small teams that need privacy and automation without enterprise capacity.
Business costs $199 a month, billed $1,990/yr billed yearly. Its 500 monthly credits, 600-second runs and five concurrent scans suit heavier workloads, while retaining all seven sandboxes, private reports and REST API and MCP access. Team / Enterprise has custom pricing and includes 5,000 credits per month, 600-second runs, all seven sandboxes, ten concurrent scans, ten seats, a shared credit pool and organization reports; it is aimed at coordinated teams rather than solo use.
Platforms
Malwagon is a cloud service with web, API, Linux, macOS and Windows support. Its CLI runs on Linux, macOS and Windows, so command-line use does not require a single desktop platform.
Who it's for
Incident responders, detection engineers, SOC analysts and threat researchers are the natural audience: the service joins static and dynamic examination with evidence, detection-rule generation and structured exports. Unauthenticated users can submit untrusted attachments and read reports, which lowers the barrier to basic triage, but public reporting makes that route inappropriate for sensitive cases.
Pros and cons
- Broad input coverage: supports URLs, commands, packages, drivers, documents and hashes as well as files, covering varied investigation starting points.
- Useful downstream outputs: ATT&CK mappings, generated detection rules and several export formats can carry findings into other tools and processes.
- Privacy is plan-dependent: free reports are public; private reports and post-analysis deletion require paid privacy options.
- Free capacity is constrained: Community has 20 monthly credits, 120-second runs and one concurrent scan, limiting sustained or parallel work.
- Paid plans require an annual billing commitment: Pro and Business show monthly prices but are billed yearly at the stated annual totals.
Alternatives
Compare malware analysis sandboxes if you want to weigh this category more broadly. ANY.RUN is another freemium option with a free trial and Android, iOS, desktop, web and API platforms; choose it when that platform coverage better matches your environment. Retrace offers a free community feed, standard execution queue, web interface, basic report export and unlimited public analyses, making it a fit for users who prioritize that community access.
CAPE Sandbox is free, open-source software with a self-hosted setup, so consider it when self-hosting is the priority. Bitdefender Total Security is a different kind of option: its Total Security Individual plan costs $59.99 a year for five devices and one account, suited to readers seeking device security rather than a malware-analysis sandbox. Zscaler Private Access is a paid access platform rather than a sandbox alternative for sample analysis.
Hatching Triage uses volume-based licensing, with packages starting at 500 analyses per day and scaling toward 50,000 per day; it is worth considering when analysis volume is the main requirement. Hybrid Analysis offers a free community service with 30 file uploads per month and a 100 MB maximum upload, a fit for readers whose needs fit those caps. CrowdStrike Falcon Pro is a paid endpoint-security option at $14.99 a month per device, with Windows and macOS firewall policies and detection details up to 90 days, rather than a direct sandbox substitute.
Verdict
Malwagon is a strong choice for security practitioners who need varied sample inputs, behavioral analysis and portable detection outputs through one service. The main reason to choose it is that combination of analysis depth and workflow integration; look elsewhere if you need private analysis without a paid plan, a self-hosted sandbox, or free capacity beyond the limited public tiers.
Getting started
- Open the Malwagon website
- Choose Free Scan, Community, Pro, Business, or Team / Enterprise
- Submit a supported file, URL, command, document, package, driver, or hash
- Review the scored verdict and evidence report
- Use the REST API, MCP server, or Python CLI for automated submissions
- Select a paid plan when private reports or higher scan capacity are required
Limits worth knowing
Free Scan allows 3 scans per source address per day with public reports and no internet egress. Community provides 20 scan credits monthly, 120-second runs, one concurrent scan, and public reports; Pro starts at $79.00 per month with 200 credits and private reports.
Questions
Is Malwagon free?
Yes. Free Scan and Community are listed at 0.00 USD.
What does Pro cost?
Pro costs $79 a month; the listed yearly billing price is $790/yr.
Which platforms support the Malwagon CLI?
The dependency-free CLI runs on Linux, macOS, and Windows.
Can Malwagon analyze URLs and network activity?
Yes. It accepts URLs and records network traffic plus JA3/JA4 fingerprints during dynamic analysis.
Are free reports private?
No. Free-tier reports are publicly viewable; paid plans can keep scans private.
Does Malwagon provide an API?
Yes. It offers a bearer-token REST API and an MCP server at https://malwagon.com/mcp.
Alternatives to Malwagon
- 1
ANY.RUN
Free planAndroidiOSWebAPI7.5Free plan - 2
CAPE Sandbox
Free planOpen sourceWebAPILinuxSelf-hosted7.4Free plan - 3
Detonate
Free planWebAPILinuxSelf-hosted7.3From $4,990 a year - 4
CrowdStrike Falcon Pro
AndroidiOSWebAPI7.1From $99.99 a year - 5
Retrace
Free planAndroidWebAPILinux6.9Free plan - 6
Symantec IT Management Suite
WebAPILinuxmacOS6.8