LXC
LXC is free software for creating and managing Linux system or application containers using containment features in the Linux kernel.
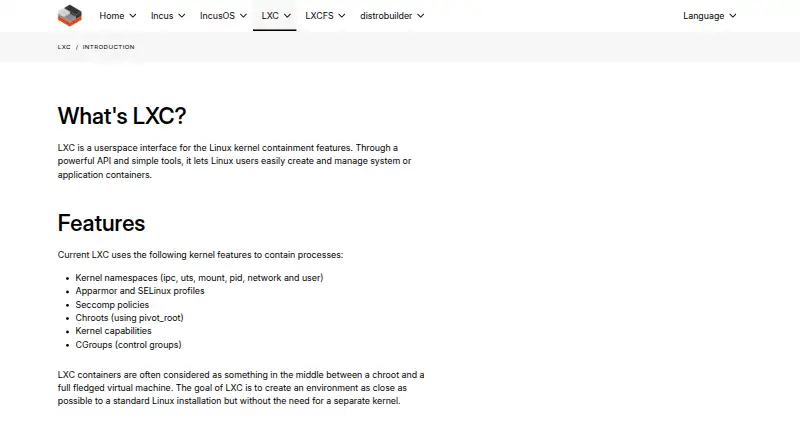
What LXC is
LXC is free software for creating and managing Linux system or application containers using containment features in the Linux kernel. It aims to give containers an environment similar to a standard Linux installation without requiring a separate kernel. The project includes the liblxc library, container control tools, distribution templates, and API bindings for Python 3, Lua, Go, Ruby, and Haskell. Its containment mechanisms include kernel namespaces, AppArmor and SELinux profiles, seccomp policies, chroots, kernel capabilities, and cgroups. LXC is included in most Linux distributions and is generally installed through the distribution package manager. Its minimum requirements include a supported C library and Linux kernel version 2.6.32 or later. The project lists LXC 7.0 and 6.0 as long-term support releases, supported through June 1, 2031 and June 1, 2029 respectively. The project describes unprivileged containers as safe by design because container root maps to an unprivileged host user. However, LXC does not prevent denial-of-service attacks by default, and the project advises configuring cgroup limits for untrusted containers. It also warns that privileged containers run processes as host root. The software is mostly under GNU LGPLv2.1+, with some components under BSD 2-clause or GNU GPLv2 licenses.
Good
- Free software included in most Linux distributions.
- Does not require a separate kernel for containers.
- Includes tools, templates, and language API bindings.
- Offers long-term support releases.
Watch out
- Requires Linux kernel version 2.6.32 or later.
- Does not prevent denial-of-service attacks by default.
- Privileged containers run processes as host root.
Who it suits
LXC suits Linux users who need to create and manage system or application containers without a separate kernel. It may fit people who can configure cgroup limits and understand the different risks of privileged containers.
Verdict
LXC provides Linux container management with a broad set of containment mechanisms and tools. Users running untrusted containers should configure cgroup limits and avoid exposing privileged container root access.
Plans and prices
From LXC's own pricing page, checked 8 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| LXC | Free | Linux kernel required · No separate kernel for containers · Free software; no charge stated |
The facts
Each one read from LXC's own pages, with the date it was checked.
What it does
- Components
- LXC includes the liblxc library, standard container control tools, distribution templates, and API bindings for Python 3, Lua, Go, Ruby, and Haskell.checked 8 Oct 2026
- Container model
- LXC aims to provide an environment close to a standard Linux installation without requiring a separate kernel.checked 8 Oct 2026
- Installation
- LXC is included in most Linux distributions and is generally installed through the distribution package manager.checked 8 Oct 2026
- Licensing
- LXC is free software, with most code under GNU LGPLv2.1+ and some components under BSD 2-clause or GNU GPLv2 licenses.checked 8 Oct 2026
- Minimum requirement
- The listed hard requirements include a supported C library and a Linux kernel version 2.6.32 or later.checked 8 Oct 2026
- Privileged container caution
- The documentation warns that privileged containers run processes as host root and should not give untrusted parties access to container root.checked 8 Oct 2026
- Purpose
- LXC is a userspace interface to Linux kernel containment features for creating and managing system or application containers.checked 8 Oct 2026
- Release support
- The project lists LXC 7.0 and 6.0 as long term support releases, with support through June 1, 2031 and June 1, 2029 respectively.checked 8 Oct 2026
- Security features
- LXC uses kernel namespaces, AppArmor and SELinux profiles, seccomp policies, chroots, kernel capabilities, and cgroups to contain processes.checked 8 Oct 2026
- Security limits
- LXC says it does not prevent denial-of-service attacks by default and advises configuring cgroup limits when running untrusted containers.checked 8 Oct 2026
- Security model
- The project describes unprivileged containers as safe by design because container root maps to an unprivileged user outside the container.checked 8 Oct 2026
- Security reporting
- Security issues can be reported by email to the project security address or through a private GitHub security advisory.checked 8 Oct 2026
The company
- Founded
- 2008checked 28 Sep 2026
Alternatives to LXC
- 1
LXD
Free planWebAPILinuxSelf-hosted7.0From $25 a year - 2
BuildKit
Free planAPILinuxmacOSSelf-hosted6.8Free plan - 3
Incus
Free planAPILinuxmacOSSelf-hosted6.8Free plan - 4
Apptainer
Free planAPILinuxmacOSSelf-hosted6.7Free plan - 5
crun
Free planLinuxSelf-hosted6.5Free plan - 6

Buildah
Free planAPILinuxSelf-hosted6.4Free plan