
FourCore ATTACK
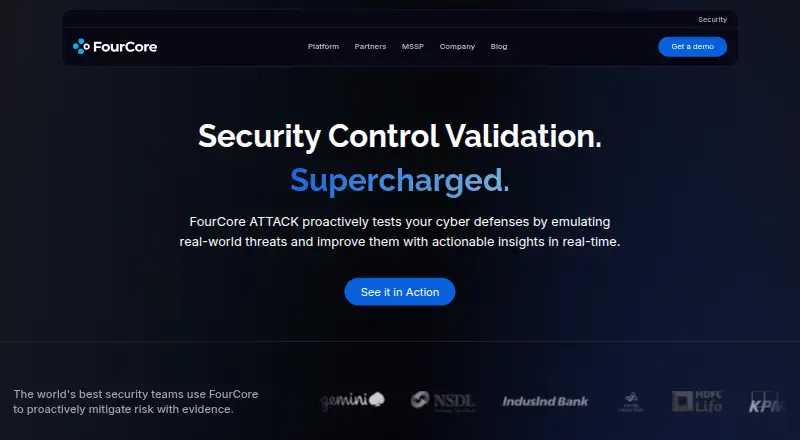
FourCore ATTACK is a platform for simulating cyberattacks to check how an organization’s security controls respond.
What FourCore ATTACK is
FourCore ATTACK is a platform for simulating cyberattacks to check how an organization’s security controls respond. It uses threat intelligence connected to the organization’s environment to help prioritize controlled campaigns that emulate adversary tactics, techniques, procedures, indicators, and artifacts. Results map to MITRE ATT&CK and classify outcomes as detected, partially detected, blocked, or missed. Campaign evidence connects simulated behavior with telemetry, alerts, timing, control responses, and recommended next steps. The platform describes coverage for endpoints, email, network segmentation, WAF, SIEM, EDR, XDR, firewalls, DLP, and exfiltration controls. Teams can generate or refine Sigma, YARA, Snort, and configuration changes, then run the behavior again after updates. FourCore says the service is available as AWS-hosted SaaS and invites customers to discuss on-premises options. Pricing is on request. Its intended users include SecOps and detection engineering teams responsible for detection, response, and control assurance.
Good
- Maps simulation outcomes to MITRE ATT&CK.
- Covers endpoint, email, network, and other controls.
- Links campaign evidence to telemetry and alerts.
- Can generate or refine detection rules and configuration changes.
Watch out
- Pricing is available on request.
- On-premises options require contacting FourCore.
- Windows and Linux agents connect to its SaaS platform.
Who it suits
FourCore ATTACK is aimed at security teams that need to assess detection and response controls across multiple attack surfaces. It may suit SecOps or detection engineering teams that want to map simulation outcomes to MITRE ATT&CK and retest changes.
Verdict
FourCore ATTACK combines controlled simulations, outcome evidence, and follow-up rule or configuration changes. Its broad control coverage and deployment details are worth reviewing alongside the organization’s preferred hosting approach and requested pricing.
The facts
Each one read from FourCore ATTACK's own pages, with the date it was checked.
What it does
- Attack emulation
- It emulates adversary tactics, techniques, procedures, indicators, and artifacts in controlled campaigns.checked 8 Oct 2026
- ATT&CK coverage
- Simulation results map to MITRE ATT&CK techniques and classify outcomes as detected, partially detected, blocked, or missed.checked 8 Oct 2026
- Coverage
- The platform describes testing endpoint, email, network segmentation, WAF, SIEM, XDR, DLP, and exfiltration controls.checked 8 Oct 2026
- Deployment
- The FAQ says FourCore ATTACK is available as an AWS-hosted SaaS platform and invites customers to contact FourCore about on-premises solutions.checked 8 Oct 2026
- Detection improvement
- It can generate or refine Sigma, YARA, Snort, and configuration changes, then retest the behavior.checked 8 Oct 2026
- Endpoint agents
- FourCore describes lightweight Windows and Linux agents that connect to its SaaS platform; the Windows agent is provided as a preconfigured MSI and installed as a service.checked 8 Oct 2026
- Evidence
- Campaign results can link simulated behavior to control responses, telemetry, alert timing, ATT&CK techniques, and recommended next actions.checked 8 Oct 2026
- Integrations
- Listed integrations include CrowdStrike, SentinelOne, Microsoft Sentinel, QRadar, Trend Micro Vision One, Proofpoint, Cisco Secure Email, Cortex XDR, and ServiceNow.checked 8 Oct 2026
- Intended users
- The platform is presented for security teams responsible for detection, response, and control assurance, including SecOps and detection engineering teams.checked 8 Oct 2026
- Named integrations
- Its integrations page lists Trend Micro Vision One, Microsoft Defender for Endpoint, Harfanglab, Qualys Cloud EDR, LimaCharlie, CrowdStrike, SentinelOne, Microsoft Sentinel, QRadar, ZScaler NSS, Proofpoint, Cisco Secure Email, Cortex XDR, and ServiceNow.checked 8 Oct 2026
- Penetration testing
- FourCore says third-party security experts conduct detailed product penetration tests at least annually.checked 8 Oct 2026
- Pricing
- The maker pages reviewed direct visitors to book a demo and do not state plan prices.checked 8 Oct 2026
- Product
- FourCore ATTACK is an adversarial exposure validation platform that simulates cyberattacks to test security controls.checked 8 Oct 2026
- Purpose
- FourCore ATTACK continuously simulates real-world cyberattacks to validate whether security controls work.checked 8 Oct 2026
- Remediation
- The platform can generate or refine Sigma, YARA, Snort, and configuration changes, then retest behavior after updates.checked 8 Oct 2026
- Safety
- The FAQ says its attack simulations are designed not to disrupt or destroy target systems.checked 8 Oct 2026
- Security certification
- FourCore says it maintains ISO 27001:2022 certification and lists CSA STAR Level 1.checked 8 Oct 2026
- Security controls
- FourCore states that UI and API communications use HTTPS/TLS 1.2 or higher and that customers can choose 2FA enforcement or SSO.checked 8 Oct 2026
- Security testing
- FourCore says third-party security experts perform detailed product penetration tests at least annually.checked 8 Oct 2026
- Simulation safety
- FourCore says its simulations are safe and do not disrupt or destroy target systems.checked 8 Oct 2026
- Threat assessment
- Its agentic threat intelligence connects current threats with an organization’s environment to help prioritize tests.checked 8 Oct 2026
- Validation
- The platform correlates simulation steps with telemetry, alerts, and outcomes across security tools.checked 8 Oct 2026
- Workflow integrations
- The platform describes carrying findings into Jira and ServiceNow workflows.checked 8 Oct 2026
The company
- Company
- The About page identifies Aarush Ahuja, Hardik Manocha, and Swapnil as FourCore’s CEO, COO, and CTO co-founders, respectively.checked 8 Oct 2026
The full review of FourCore ATTACK
FourCore ATTACK is a continuous adversarial-exposure platform for security and detection teams that need evidence from recurring attack simulations. It fits organizations operating several security controls and seeking a remediation loop rather than a one-time assessment. Its strongest advantage is linking realistic behavior to telemetry and follow-up changes; custom pricing and deployment discussions make it less suitable for buyers seeking a self-service package.
Overview
FourCore ATTACK continuously models real-world cyberattacks and relates current threat intelligence to an organization’s environment so teams can prioritize tests. Controlled campaigns reproduce adversary tactics, techniques, procedures, indicators and artifacts through lightweight Windows and Linux agents connected to the platform. FourCore says the simulations are designed not to disrupt or destroy target systems, an important consideration when exercises involve production-connected defenses.
Campaign evidence connects each simulated action with telemetry, control responses, alert timing, MITRE ATT&CK techniques and recommended next steps. Outcomes are categorized as detected, partially detected, blocked or missed, giving SecOps and detection engineers a more actionable coverage view than a basic pass/fail result.
Key features
- Broad control coverage. Tests span endpoints, email, WAF, network segmentation, SIEM, EDR, XDR, firewalls, DLP and exfiltration controls. This breadth suits teams validating a defense-in-depth program, though it may be excessive for a narrowly focused endpoint review.
- Continuous, agent-based simulations. Scheduling supports recurring validation, while Windows and Linux agents provide coverage for those operating systems. The Windows agent arrives as a preconfigured MSI and runs as a service, reducing deployment friction for managed Windows estates.
- ATT&CK-mapped evidence. Correlation of behavior, alerts, telemetry and outcomes helps detection engineers identify where a control failed and communicate gaps in a common framework.
- Closed-loop remediation. FourCore can generate or refine Sigma, YARA and Snort rules, as well as configuration changes, then retest the behavior. That makes it more useful for teams prepared to act on findings than for organizations wanting a report-only exercise.
- Operational integrations. Findings can move into Jira and ServiceNow workflows. Named connections include CrowdStrike, SentinelOne, Microsoft Sentinel, QRadar, Trend Micro Vision One, Proofpoint, Cisco Secure Email, Cortex XDR, Trend Micro Vision One, Harfanglab, Qualys Cloud EDR, LimaCharlie and ZScaler NSS.
- Security and access controls. FourCore states that UI and API traffic uses HTTPS/TLS 1.2 or higher, with customer-selectable 2FA enforcement or SSO. It says third-party experts perform detailed product penetration tests at least annually, and cites ISO 27001:2022 certification and CSA STAR Level 1.
Pricing
FourCore ATTACK uses paid, custom pricing. The maker directs prospective customers to book a demo rather than publishing plans, seat counts, quotas, trial terms or renewal conditions. This approach can accommodate an organization-specific deployment, but it prevents a quick budget comparison and makes the product a poor fit for teams that require transparent subscription tiers.
Platforms
The platform is offered across Linux, Windows, web and self-hosted environments, with a hybrid deployment model. FourCore describes an AWS-hosted SaaS service and invites customers to discuss on-premises solutions, so organizations with strict locality requirements should confirm the appropriate architecture before committing.
Who it's for
FourCore ATTACK is aimed at SecOps, detection engineering and other security teams responsible for detection, response and control assurance. It is a strong match for organizations that need scheduled validation across multiple tools and can connect findings to engineering workflows. Smaller teams with only one or two controls, limited capacity to tune detections, or a requirement for fixed public pricing may find its sales-led model and broad scope harder to justify.
Pros and cons
Pros
- Evidence beyond a scan: ATT&CK mapping and detected/partially detected/blocked/missed outcomes show how defenses actually responded.
- Remediation loop: Rule and configuration changes can be refined and retested, shortening the path from finding to validation.
- Wide ecosystem: Coverage and integrations span endpoint, email, network and analytics controls, with Jira and ServiceNow workflow support.
- Safety and assurance: Non-destructive simulation claims, TLS, optional SSO or 2FA, annual penetration testing and stated certifications support use in security-sensitive environments.
Cons
- No public plans or prices: Buyers must engage FourCore to understand commercial scope, limits and renewal terms.
- Deployment qualification required: SaaS is AWS-hosted, while on-premises use requires a separate discussion.
- Operational overhead: The product delivers most value to teams able to investigate telemetry, tune controls and run follow-up campaigns.
Alternatives
Atomic Red Team is a free, open-source option for quick tests that run in five minutes or less across API, Linux, macOS and Windows; choose it for minimal setup and community-developed test content rather than a commercial evidence loop.
Infection Monkey is a free, open-source breach-and-attack simulation tool for Linux, Windows, web and self-hosted deployments, making it preferable when avoiding licensing cost is the priority.
MITRE Caldera is a free Apache-licensed cybersecurity framework for API, Linux, macOS, self-hosted and web environments; pick it when an extensible open-source framework is more important than managed validation.
OpenAEV offers a free-forever on-premises Community Edition with core attack simulation, tabletop exercises and community support, plus paid options; it suits teams wanting an on-premises entry point.
AttackIQ Platform provides a free tier with testing packages and adversary research, alongside paid credit-based purchasing; consider it when those packaged access options fit better than custom engagement.
Keysight Eggplant Test is enterprise software with a trial and quote-based pricing across a broad platform list; choose it when that enterprise testing focus is the requirement.
Stratus Red Team is a free option for API, Linux, macOS, self-hosted and Windows environments.
Pentera Platform is a paid platform with quote-based commercial terms; it is an alternative for buyers seeking a similarly sales-led product evaluation.
See the broader Breach and Attack Simulation Software category for more choices.
Verdict
Choose FourCore ATTACK if your security team needs continuous, ATT&CK-mapped proof across diverse controls and wants remediation rules or configurations retested in the same workflow. Look elsewhere if transparent pricing, a fully self-service open-source deployment or a narrowly scoped test is more important than its integrated validation cycle.
Alternatives to FourCore ATTACK
- 1
AttackIQ Platform
Free planWebAPILinuxmacOS7.9From $4,995 a month - 2
Google Cloud Secret Manager
Free planWeb6.5From $0.02 a month - 3
MITRE Caldera
Free planWebAPILinuxmacOS6.3Free plan - 4
OpenAEV
Free planWebAPILinuxSelf-hosted6.3Free plan - 5
SafeBreach Validate
WebAPILinuxmacOS6.3 - 6
Atomic Red Team
Free planAPILinuxmacOSWindows6.2Free plan