EventSentry File Monitoring
EventSentry File Monitoring tracks file additions and removals, size changes, SHA-256 checksum changes, and transaction-log tampering.
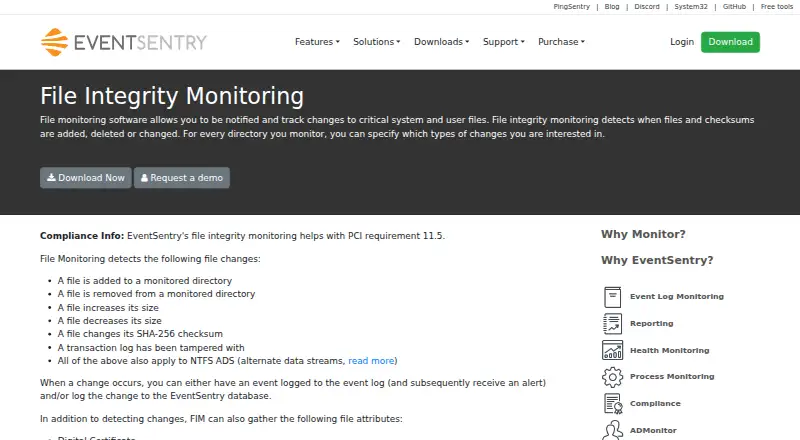
What EventSentry File Monitoring is
EventSentry File Monitoring tracks file additions and removals, size changes, SHA-256 checksum changes, and transaction-log tampering. It can gather digital certificates and entropy, which can help detect certain ransomware outbreaks. Changes can be logged to the Application event log with customizable severity and details such as previous and new sizes or checksums. The current status of monitored files can be consolidated in the EventSentry database for comparisons across computers. Notification and integration targets include email, MSSQL, PostgreSQL, MySQL and Oracle databases, HTTP(S), Syslog, SNMP traps, and executable processes. Exported text event logs can be cryptographically signed and timestamped to help detect tampering. EventSentry says its file integrity monitoring helps with PCI requirement 11.5. The full edition is an on-premise perpetual license listed at $85 per Windows device, and EventSentry Light is free for monitoring five machines. The feature is listed for Linux, macOS, web, and Windows, while the supplied supported operating-system list covers Windows versions from NT 4 SP6 through Server 2025.
Good
- Tracks file changes, checksums, and transaction-log tampering.
- Can gather certificates and entropy.
- Supports several notification and integration targets.
- EventSentry Light is free for five machines.
- Full edition is a perpetual on-premise license.
Watch out
- The product does not currently report who changed a file.
- Full edition costs $85 per Windows device.
- EventSentry Light has no SIEM capability or dashboards.
- Agentless monitoring is not supported.
Who it suits
File Monitoring suits organizations that need to track file integrity and route change notifications to logs, databases, or other systems. The listed customer base includes individual users, consulting firms, government agencies, universities, and large corporations.
Verdict
EventSentry File Monitoring covers multiple file-change types and offers a range of alert destinations. Buyers should note that change attribution is not currently available and the full edition is priced per Windows device.
Plans and prices
From EventSentry File Monitoring's own pricing page, checked 1 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| EventSentry Light | Free | monitor 5 machines · basic log monitoring · community support · no SIEM capability · no dashboards |
| EventSentry | $85, paid once | perpetual license · no data limit · on-premise · phone/email support · per Windows device |
The facts
Each one read from EventSentry File Monitoring's own pages, with the date it was checked.
What it does
- Alerts
- Changes can be logged to the Application event log with customizable severity and can include previous and new sizes or checksums.checked 1 Oct 2026
- Audience
- The customer base includes individual users, consulting firms, government agencies, universities and Fortune 500 corporations.checked 1 Oct 2026
- Change attribution
- EventSentry currently does not report who made a file change; the page says this is planned for a future release.checked 1 Oct 2026
- Compliance
- EventSentry file integrity monitoring helps with PCI requirement 11.5.checked 1 Oct 2026
- Consolidation
- The current status of monitored files can be consolidated in the EventSentry database for comparison across computers.checked 1 Oct 2026
- Database security
- The built-in database can be restricted to local-host access, and EventSentry service users lack permission to delete or modify data.checked 1 Oct 2026
- Encryption
- The documentation says BitLocker can protect the EventSentry database at rest when it runs on Windows.checked 1 Oct 2026
- File attributes
- File monitoring can gather digital certificates and entropy, with entropy usable to detect certain ransomware outbreaks.checked 1 Oct 2026
- Integrations
- Notification and integration targets include email, MSSQL/PostgreSQL/MySQL/Oracle databases, HTTP(S), Syslog, SNMP traps and executable processes.checked 1 Oct 2026
- Purpose
- File integrity monitoring tracks additions, removals, size changes, SHA-256 checksum changes and transaction-log tampering.checked 1 Oct 2026
- Security
- Event logs exported to text files can be cryptographically signed and timestamped to detect tampering.checked 1 Oct 2026
- Support
- EventSentry Light includes community support, while the full edition includes phone and email support plus getting-started assistance.checked 1 Oct 2026
The company
- Founded
- 2002checked 28 Sep 2026
- Headquarters
- Chicago, Illinois, United Stateschecked 28 Sep 2026
The full review of EventSentry File Monitoring
EventSentry File Monitoring is an on-premises file integrity monitoring feature for Windows environments. It suits administrators who need configurable alerts, cross-computer comparison and compliance support. Its chief limitation is that it records file changes without identifying who made them.
Overview
Monitoring covers additions, removals, file-size changes, SHA-256 checksum changes and transaction-log tampering. That breadth helps teams spot unexpected changes across important files, and the product supports PCI requirement 11.5. But it is a weaker fit for investigations where accountability depends on knowing which user made a change.
The full edition is licensed per Windows device, so costs rise with the number of devices being monitored. In return, the license is perpetual, on-premises and has no data limit—an attractive model for organizations that prefer local deployment and predictable licensing over a recurring subscription.
Key features
File records can include digital certificates and entropy, which can help detect certain ransomware outbreaks. Changes can be written to the Application event log at a customizable severity and include previous and new sizes or checksums. That detail can help administrators assess what changed, though it does not close the attribution gap.
EventSentry can consolidate the current status of monitored files in its database for comparison across computers. Alerts and integrations can go to email, MSSQL, PostgreSQL, MySQL or Oracle databases, HTTP(S), Syslog, SNMP traps and executable processes. The range is useful for teams that need to route notifications into existing systems rather than rely on one destination.
Exported event logs can be cryptographically signed and timestamped to help detect tampering. Database access can be restricted to the local host, and EventSentry service users cannot delete or modify data. When the database runs on Windows, BitLocker can protect it at rest. These controls strengthen local record protection, but they do not identify the person behind a file change.
Pricing
EventSentry Light costs nothing and covers up to 5 machines, with basic log monitoring and community support. It has no SIEM capability or dashboards, so it is best for small deployments that need a no-cost starting point rather than the full monitoring feature set.
EventSentry costs $85, paid once, billed per Windows device. The perpetual on-premises license has no data limit and includes phone and email support. It is the relevant option for organizations needing the full edition, but device-based pricing means the total depends on deployment size. A 30-day trial is available.
Platforms
The supported platform list covers Windows NT 4 SP6 through Windows 11, plus Windows Server releases from 2000 through Server 2025. Deployment is on-premises, and agentless monitoring is not supported. Although the service is associated with Linux, macOS and web platforms, the full license is billed per Windows device; organizations should evaluate the stated Windows support before planning deployment.
Who it's for
EventSentry serves a broad customer base, including individual users, consulting firms, government agencies, universities and large corporations. It is most compelling for Windows administrators who value detailed change records, centralized comparisons, multiple alert destinations and PCI 11.5 support. Teams that require user-level attribution should choose a tool that provides it.
Pros and cons
- Broad change coverage: tracks additions, removals, size and checksum changes, and transaction-log tampering.
- Flexible alert routing: supports email, databases, HTTP(S), Syslog, SNMP traps and executable processes.
- Local data protections: signed and timestamped exports, restricted database access and optional BitLocker protection on Windows help guard records against tampering.
- No change attribution: teams cannot use EventSentry to determine who made a file change.
- Paid license scales by device: the $85, paid once price is per Windows device, which can make larger deployments more expensive.
Alternatives
File Integrity Monitoring Software is the broader category directory for comparing options. Consider Paessler PRTG Network Monitor if a freemium alternative with a 100-sensor free tier and broad platform support better suits the deployment. Wazuh offers a free, self-hosted open-source option, with a paid Small plan starting at $571 a month. OWASP Amass is a free, open-source framework for readers seeking a no-cost tool rather than a paid monitoring license. Elastic Security may suit readers looking for a freemium security platform. FIM is a free open-source alternative with no usage limits stated. Open Source Tripwire is a free GPL-2.0 option for file and directory integrity monitoring. OSSEC offers a free command-line option with core rules and no dedicated support staff. AIDE is a free GPL-2.0 alternative for self-hosted use.
Verdict
Choose EventSentry File Monitoring if you manage Windows devices and need broad file-change detection, centralized comparison and flexible alert delivery with local record protections. The perpetual, no-data-limit license is appealing for sustained on-premises use, but per-device pricing and the lack of change attribution make it a poor choice when identifying the person behind a change is essential.
Getting started
- Visit the EventSentry file monitoring website.
- Choose EventSentry Light or the full EventSentry edition.
- Use the 30-day trial if you want to evaluate the paid edition.
- Deploy on-premise and select Windows devices for the full edition.
Limits worth knowing
EventSentry Light is free for up to five machines and excludes SIEM capability and dashboards. The full EventSentry license is $85 per Windows device, billed once, and has no data limit.
Questions
Is there a free plan?
Yes. EventSentry Light costs nothing and supports monitoring five machines.
What does the full edition cost?
EventSentry costs $85 per Windows device, billed once as a perpetual license.
Is there a trial?
Yes, a 30-day trial is available.
Where does it run?
Deployment is on-premise. The feature is listed for Linux, macOS, web, and Windows, while the supported operating-system list names Windows versions from NT 4 SP6 through Server 2025.
Does it identify who changed a file?
No. EventSentry currently does not report who made a file change.
What support is included?
EventSentry Light includes community support. The full edition includes phone and email support, plus getting-started assistance.
Alternatives to EventSentry File Monitoring
- 1
Wazuh
Free planOpen sourceWebAPILinuxmacOS8.4From $571 a month - 2
OSSEC
Free planOpen sourceAPILinuxmacOSSelf-hosted8.0From $55 a year - 3
Kaspersky Endpoint Security for Business
AndroidiOSWebAPI7.8From $29.99 a month - 4
PA File Sight
AndroidiOSWebAPI7.7From $30 a month - 5
Paessler PRTG Network Monitor
Free planAndroidiOSWebAPI7.7From $200 a month - 6
Avidemux
Free planOpen sourceWebLinuxmacOSWindows7.3Free plan