cfn-nag
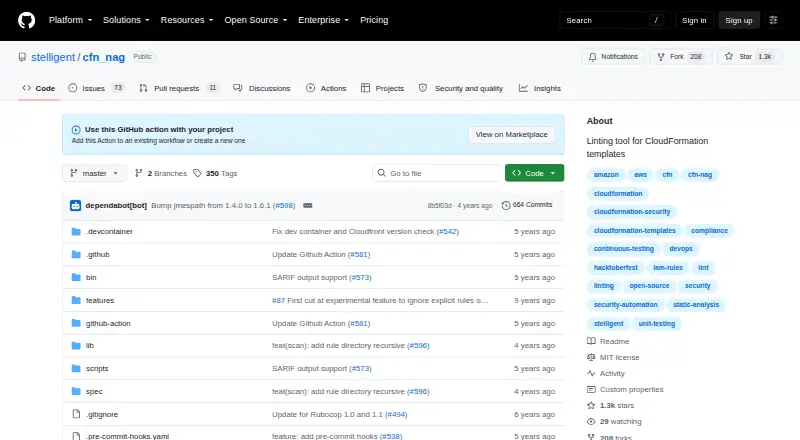
cfn-nag is a free static analysis tool that scans CloudFormation templates for patterns that may indicate insecure infrastructure.
What cfn-nag is
cfn-nag is a free static analysis tool that scans CloudFormation templates for patterns that may indicate insecure infrastructure. Its checks include overly permissive IAM and security group rules, disabled access logs or encryption, and password literals. It accepts JSON, .template, YAML, and YML files, and recursively scans subdirectories when given a directory. Results go to standard output, with JSON output available; failures return a non-zero exit code, while warnings return success. Installation is documented through RubyGems and Homebrew, with Ruby 2.5 or later required for gem installation. A Dockerfile and published Docker Hub image are also provided, and the project documents use in GitHub Actions and AWS CodePipeline. Users can filter checks with profiles and deny lists, suppress rules for individual resources, and create custom rules distributed as gems or loaded from S3. The project describes the tool as able to work offline, with S3 rule retrieval optional. As static analysis, it cannot see parameter values supplied at deployment unless those values are provided in a JSON file. By default, Fn::If analysis uses the true outcome; condition values are needed to inspect false outcomes.
Good
- Scans JSON, .template, YAML, and YML files.
- Checks IAM, security group, logging, encryption, and password patterns.
- Supports profiles, deny lists, and custom rules.
- Documents GitHub Actions and AWS CodePipeline use.
- MIT-licensed and designed to work offline.
Watch out
- Requires Ruby 2.5 or later for gem installation.
- Deployment parameter values require a supplied JSON file.
- Default Fn::If analysis does not inspect false outcomes.
- Does not analyze Terraform or Kubernetes.
Who it suits
It suits teams checking AWS CloudFormation templates for security-related patterns in local or pipeline workflows. Users who need custom checks can add rules, while those analyzing deployment parameters need to supply them separately.
Verdict
cfn-nag focuses on CloudFormation checks and offers ways to tailor or extend its rules. Keep its static-analysis limits in mind, especially for deployment-supplied values and conditional branches.
Plans and prices
From cfn-nag's own pricing page, checked 3 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| cfn-nag | Free | MIT-licensed software · Ruby >= 2.5 |
The facts
Each one read from cfn-nag's own pages, with the date it was checked.
What it does
- Checks
- The project lists checks for overly permissive IAM and security group rules, disabled access logs or encryption, and password literals.checked 3 Oct 2026
- Conditional analysis limit
- By default, cfn-nag substitutes the true outcome for Fn::If, so rules do not inspect false outcomes unless condition values are provided.checked 3 Oct 2026
- Docker
- A Dockerfile is provided, and the project says its image is published as stelligent/cfn_nag on Docker Hub.checked 3 Oct 2026
- Install
- The project documents installation with RubyGems and Homebrew, and requires Ruby 2.5 or later for gem installation.checked 3 Oct 2026
- Integrations
- The project documents running cfn-nag in GitHub Actions workflows and deploying it in AWS CodePipeline through the AWS Serverless Application Repository.checked 3 Oct 2026
- License
- The project uses the MIT License, which grants permission to use, copy, modify, merge, publish, distribute, sublicense, and sell the software subject to its terms.checked 3 Oct 2026
- Offline use
- The gem specification describes cfn-nag as a static analysis tool that must work without network connectivity, while noting S3 rule retrieval is optional.checked 3 Oct 2026
- Output
- Results go to standard output; JSON output is available, and failures return a non-zero exit code while warnings return success.checked 3 Oct 2026
- Purpose
- cfn-nag scans CloudFormation templates for patterns that may indicate insecure infrastructure.checked 3 Oct 2026
- Rule customization
- Users can filter checks with profiles and deny lists, suppress rules per resource, and develop custom rules distributed as gems or loaded from S3.checked 3 Oct 2026
- Support
- The project directs users to submit bug reports and feature requests through its GitHub issue tracker.checked 3 Oct 2026
- Template analysis limit
- Static analysis cannot see parameter values supplied at deployment unless users provide those values through a JSON file.checked 3 Oct 2026
- Template inputs
- The scanner processes JSON, .template, YAML, and YML files and recursively scans subdirectories when given a directory.checked 3 Oct 2026
Alternatives to cfn-nag
- 1
Chef InSpec
Free planOpen sourceAPILinuxmacOSSelf-hosted8.0From $59 a year - 2
AWS CloudFormation
Free planiOSWebAPILinux7.7Free plan - 3
CIS-CAT Pro Assessor
Free planAPILinuxmacOSSelf-hosted7.7From $2,400 a year - 4
Test Kitchen
Free planOpen sourceAPILinuxmacOSSelf-hosted7.2Free plan - 5
kube-score
Free planWebLinuxmacOSSelf-hosted7.0Free plan - 6
Conftest
Free planLinuxmacOSWindows6.8Free plan