Windows PE Packer
Windows PE Packer is a free, MIT-licensed command-line project for packing Windows PE files to make analysis more difficult.
What Windows PE Packer is
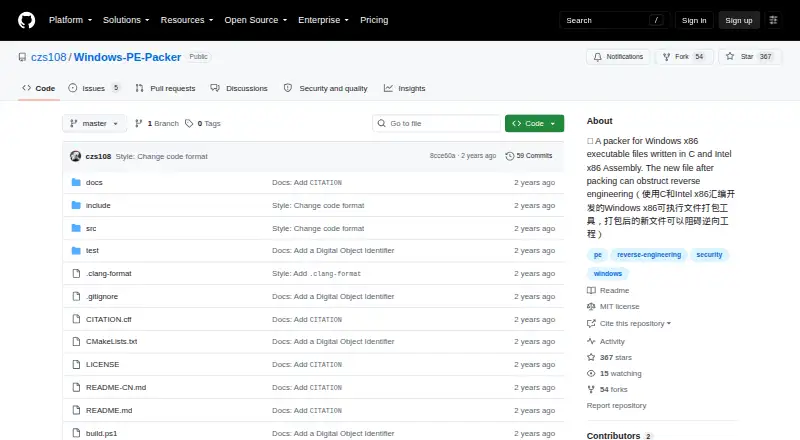
Windows PE Packer is a free, MIT-licensed command-line project for packing Windows PE files to make analysis more difficult. It transforms the import table, encrypts sections, clears section names, and adds a shell-entry. When a packed file runs, the entry decrypts sections, restores the original import table, and performs relocation. The project says this approach can obstruct disassembly, searches for constant strings, and import-table analysis. Its command takes an input filename and an output filename: PE-Packer <input-file> <output-file>. The current project handles only 32-bit .exe programs and must be configured for 32-bit Windows. Building it requires MASM32, MinGW-w64 with the i686 architecture, and CMake. The maker describes it as a beginner demonstration for learning about the Windows PE format and assembly, and warns that compatibility problems and bugs make it unsuitable for practical use. It is written in C and Intel x86 Assembly. The MIT license provides the software as-is without warranty, and the repository has no releases listed.
Good
- Free and distributed under the MIT License.
- Demonstrates import-table transformation and section encryption.
- Command-line input and output are documented.
- Written in C and Intel x86 Assembly.
Watch out
- Processes only 32-bit .exe programs.
- Requires MASM32, i686 MinGW-w64, and CMake to build.
- Maker says bugs and compatibility issues prevent practical use.
- Repository lists no releases.
Who it suits
This project suits learners studying Windows PE format and assembly who want to examine a packing demonstration. It is not suited to practical use, according to its maker.
Verdict
Windows PE Packer is a learning-oriented demonstration with a narrow 32-bit executable scope. Its stated compatibility problems and bugs are important constraints for anyone considering it beyond study.
Plans and prices
From Windows PE Packer's own pricing page, checked 10 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Windows PE Packer | Free | MIT licensed · processes 32-bit .exe programs |
The facts
Each one read from Windows PE Packer's own pages, with the date it was checked.
What it does
- Analysis resistance
- The project says packing obstructs disassembly, searching constant strings, and analyzing the import table.checked 10 Oct 2026
- Architecture limit
- It can currently process only 32-bit .exe programs.checked 10 Oct 2026
- Build requirements
- The project must be configured for Windows 32-bit and requires MASM32, MinGW-w64 with i686 architecture, and CMake.checked 10 Oct 2026
- Command-line use
- The documented command takes an input filename and an output filename: PE-Packer <input-file> <output-file>.checked 9 Oct 2026
- Downloads
- The repository's Releases page says there are no releases.checked 9 Oct 2026
- Implementation
- It is written in C and Intel x86 Assembly.checked 10 Oct 2026
- License
- The software is distributed under the MIT License, which permits use, copying, modification, distribution, sublicensing, and sale subject to its conditions.checked 10 Oct 2026
- License terms
- The MIT license grants permission to use, copy, modify, merge, publish, distribute, sublicense, and sell copies, subject to its stated conditions.checked 9 Oct 2026
- Packing features
- Packing transforms the original import table, encrypts sections, clears section names, and installs a shell-entry.checked 10 Oct 2026
- Project status
- The maker describes it as a beginner demo for studying Windows PE Format and Assembly Language and says it has compatibility problems and bugs that make it unsuitable for practical use.checked 10 Oct 2026
- Purpose
- Windows PE Packer packs Windows PE files to obstruct reverse engineering.checked 10 Oct 2026
- Runtime behavior
- When a packed file runs, its shell-entry decrypts sections, initializes the original import table, and performs relocation.checked 10 Oct 2026
- Security documentation
- The repository README describes anti-reverse-engineering behavior but does not state security or compliance certifications.checked 9 Oct 2026
- Supported files
- The project can currently process only 32-bit .exe programs.checked 9 Oct 2026
- Usage
- The command-line usage takes an input filename and an output filename: PE-Packer <input-file> <output-file>.checked 10 Oct 2026
- Warranty
- The MIT license provides the software “AS IS” without warranty.checked 10 Oct 2026
Where it runs
- Build platform
- The project must be configured on or for 32-bit Windows and requires MASM32, MinGW-w64 with i686 architecture, and CMake.checked 9 Oct 2026
The company
- Maker
- The GitHub profile identifies the maker as Chenzs108 and lists Suzhou, Jiangsu, China.checked 10 Oct 2026
Alternatives to Windows PE Packer
- 1
Obsidian
Free planOpen sourceAndroidiOSExtensionLinux8.4From $48 a year - 2
Enigma Protector
WebAPILinuxSelf-hosted7.4 - 3
Virbox Protector
AndroidiOSLinuxmacOS7.1CN¥2,499 one-time - 4
VMProtect
LinuxmacOSWindows6.6 - 5
Crinkler
Free planWindows6.3Free plan - 6
Themida
Windows6.3From €79 a year