Wfuzz
Wfuzz is a framework for automating web application security assessments and finding and exploiting vulnerabilities.
What Wfuzz is
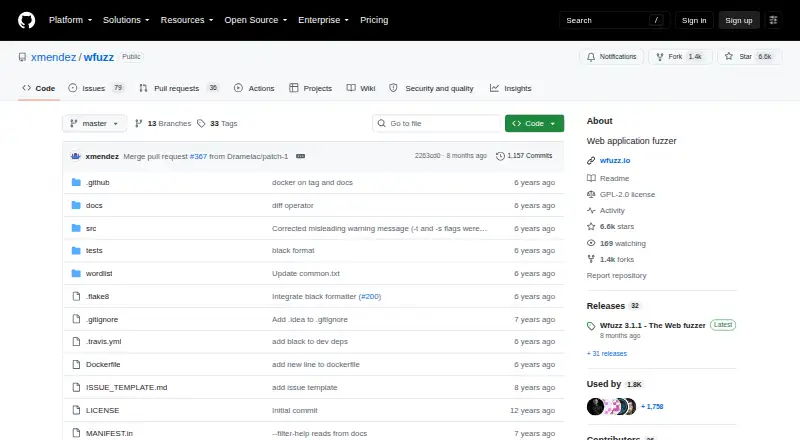
Wfuzz is a framework for automating web application security assessments and finding and exploiting vulnerabilities. It substitutes values from payloads for FUZZ markers in HTTP requests, letting assessors test parameters, authentication, forms, directories, files, and headers. Its documented request coverage also includes paths, POST data, cookies, custom headers, and HTTP verbs. Users can combine payloads, apply encoders, and filter responses to select or hide results. A plugin-supported vulnerability scanner is part of the framework, and its modular design allows users to build plugins. Wfuzz can expose a language interface to prior requests and responses from Wfuzz or tools such as Burp for manual or semi-automated testing. The project also includes wfpayload for generating payloads and wfencode for encoding and decoding. It runs locally and is available for Linux, macOS, and Windows; installation options include pip and a Docker image. The project is GPL-2.0 licensed and free, with documentation and GitHub issues and pull requests for project activity. Its releases page lists version 3.1.1 as the latest release.
Good
- Tests paths, parameters, cookies, and headers.
- Supports multiple payloads, encoders, and response filters.
- Modular scanner supports user-built plugins.
- Includes payload-generation and encoding tools.
- Free under GPL-2.0.
Watch out
- The listed latest release is version 3.1.1.
- It is aimed at web assessment and pentesting work.
Who it suits
Wfuzz is suited to people performing web application assessments or penetration testing who need to generate and test values across HTTP request components. It is a local tool for users comfortable with its installation options and assessment workflow.
Verdict
Wfuzz offers broad HTTP request fuzzing and plugin-based vulnerability scanning in a free, locally run framework. Its focus is web application assessment rather than general-purpose software use.
Plans and prices
From Wfuzz's own pricing page, checked 7 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free/open-source | Free | GPL-2.0 licensed · available through pip, GitHub releases, or Docker |
The facts
Each one read from Wfuzz's own pages, with the date it was checked.
What it does
- Audience
- The README describes Wfuzz as a tool for people performing web application assessments and pentesting.checked 7 Oct 2026
- Burp support
- Wfuzz can expose a language interface to prior requests and responses made with Wfuzz or tools such as Burp for manual and semi-automatic testing.checked 7 Oct 2026
- Fuzzing
- It replaces FUZZ markers in HTTP requests with values from payloads, allowing inputs to be tested in request parameters, authentication, forms, directories, files, and headers.checked 7 Oct 2026
- Installation
- The project README gives pip installation and a Docker image command as installation options.checked 7 Oct 2026
- License
- The GitHub repository identifies the project as licensed under GPL-2.0.checked 7 Oct 2026
- Other tools
- The framework includes wfpayload for generating payloads and wfencode for encoding and decoding.checked 7 Oct 2026
- Payloads and filters
- The documentation describes multiple payloads, combining payloads, encoders, and filters for selecting or hiding responses.checked 7 Oct 2026
- Plugins
- Its vulnerability scanner is supported by plugins, and the framework is modular so users can build plugins.checked 7 Oct 2026
- Purpose
- Wfuzz is a framework for automating web application security assessments and finding and exploiting web application vulnerabilities.checked 7 Oct 2026
- Release
- The GitHub releases page lists Wfuzz 3.1.1 as the latest release.checked 7 Oct 2026
- Request coverage
- The documentation describes fuzzing paths and files, URL parameters, POST requests, cookies, custom headers, and HTTP verbs.checked 7 Oct 2026
- Support
- The project links to documentation and uses GitHub issues and pull requests for project activity.checked 7 Oct 2026
Alternatives to Wfuzz
- 1
Jazzer
Free planOpen sourceAPILinuxmacOSSelf-hosted7.3Free plan - 2
AFL++
Free planAndroidLinuxmacOSSelf-hosted7.2From €20,000 a year - 3
Mayhem
Free planWebAPILinuxmacOS7.0From $236 a month - 4

ClusterFuzz
Free planWebLinuxmacOSSelf-hosted6.8Free plan - 5
cargo-fuzz
Free planLinuxmacOSWindows6.7Free plan - 6
boofuzz
Free planAPILinuxSelf-hostedWindows6.4Free plan