VMware Secrets Manager
VMware Secrets Manager (VSecM) is a free, open-source secrets store for holding configuration and delivering it to workloads.
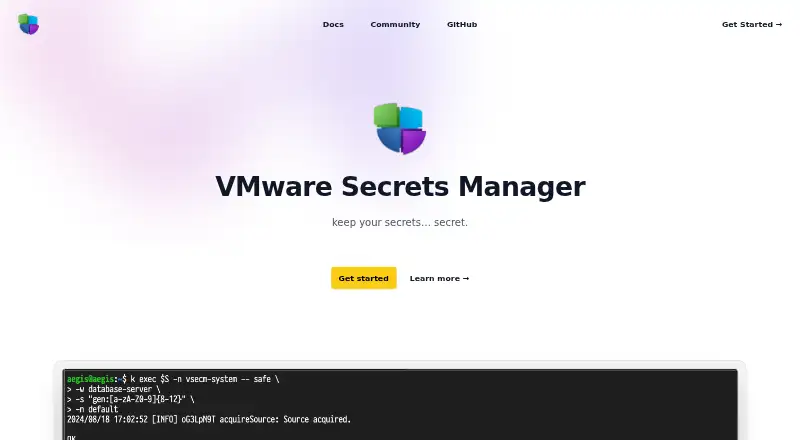
What VMware Secrets Manager is
VMware Secrets Manager (VSecM) is a free, open-source secrets store for holding configuration and delivering it to workloads. It is designed to run only on Kubernetes, using SPIFFE-compatible workload identity; SPIRE is its default identity control plane. Secrets can be delivered through a sidecar, init container, SDK or Kubernetes Secret, and can be changed at runtime without rebooting workloads. The SDK can retrieve rotated secrets without requiring an application restart or eviction. VSecM records creation and update times, keeps secret versions, supports GoLang transformations and interpolation onto Kubernetes Secrets, and can federate secrets across namespaces and clusters. Plaintext secrets stay in memory, while data saved to disk and backups is encrypted. If a component fails, workloads can continue using existing secrets, and the component can recover from an encrypted backup. Installation uses Helm charts or Makefile targets and requires Helm, kubectl, a running cluster and make. The project is in active maintenance mode, with new feature work deferred while development focuses on SPIKE v1.0.
Good
- Secret delivery supports sidecars, init containers and SDKs.
- Rotated secrets can be retrieved without application restarts.
- Supports secret version history and federation.
- Disk data and backups are encrypted.
Watch out
- Runs only on Kubernetes.
- Plaintext secret capacity depends on allocated memory.
- New feature implementations are deferred during maintenance mode.
- Secretless root-key protection requires manual key provision after restarts.
Who it suits
VSecM suits teams running Kubernetes that need to store and deliver secrets to workloads. It is not intended for standalone or non-Kubernetes operation.
Verdict
VSecM offers several workload delivery paths, runtime updates and secret history for Kubernetes environments. Its Kubernetes-only design and memory-bound plaintext storage should factor into deployment planning.
Plans and prices
From VMware Secrets Manager's own pricing page, checked 11 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free and open source | Free | BSD 2-Clause licensed · designed to run on Kubernetes |
The facts
Each one read from VMware Secrets Manager's own pages, with the date it was checked.
What it does
- Compatibility
- VSecM is designed to run on Kubernetes only and is not intended to run outside Kubernetes or as a standalone binary.checked 11 Oct 2026
- Data protection
- Sensitive data is stored in memory, while data saved to disk and backups are encrypted.checked 5 Oct 2026
- Encryption
- The production documentation says VSecM Safe encrypts secrets using age, or AES-256-GCM in FIPS-compliant environments.checked 11 Oct 2026
- Federation
- VSecM supports federation of secrets across namespaces and clusters.checked 5 Oct 2026
- FIPS mode
- FIPS mode is off by default and can be enabled by setting VSECM_SAFE_FIPS_COMPLIANT to true.checked 11 Oct 2026
- Identity
- VSecM uses SPIFFE as its identity control plane for workload authentication.checked 5 Oct 2026
- Identity integration
- VSecM uses SPIRE as its default identity control plane, and SPIFFE-compatible identity control planes can also be used.checked 11 Oct 2026
- Installation
- VSecM installs into a Kubernetes cluster using Helm charts or Makefile targets; the documented prerequisites include Helm, kubectl, a running cluster, and make.checked 5 Oct 2026
- Kubernetes requirement
- VSecM is designed to run only on Kubernetes, not as a standalone binary or outside Kubernetes.checked 5 Oct 2026
- Legacy workloads
- VSecM can create Kubernetes Secret objects for workloads that cannot use its SDK or Sidecar integration.checked 11 Oct 2026
- License
- The VSecM code is distributed under the BSD 2-Clause License.checked 5 Oct 2026
- No admin token
- VSecM requires no admin token for operation, though users may provide a root token and then manually unlock after a crash.checked 5 Oct 2026
- Operational limit
- VSecM Safe keeps plaintext secrets in memory, so the quantity of secrets is limited by the memory allocated to it.checked 11 Oct 2026
- Project status
- The project says it is in active maintenance mode, prioritizing security fixes while deferring new feature development until SPIKE reaches v1.0.checked 11 Oct 2026
- Purpose
- VMware Secrets Manager is a Kubernetes-native key-value store for securely storing and dispatching secrets to cloud-native workloads.checked 11 Oct 2026
- Resilience
- Workloads can continue using existing secrets when a VSecM component fails, and the component can recover state from an encrypted backup.checked 5 Oct 2026
- Resource limits
- The project notes that in-memory storage limits capacity and says a couple of gigabytes of RAM can hold many plain-text secrets.checked 5 Oct 2026
- Rotation
- The VSecM SDK can retrieve rotated secrets without requiring the application to restart or be evicted.checked 11 Oct 2026
- Secret delivery
- Secrets can be delivered to workloads with the VSecM SDK, Sidecar, or Init Container, or persisted as Kubernetes Secret objects.checked 11 Oct 2026
- Secret history
- VSecM records creation and update timestamps and keeps version history for secrets.checked 5 Oct 2026
- Secretless mode
- If operators opt out of Kubernetes Secrets for root-key protection, they must manually provide the root key again after VSecM Safe restarts or is evicted, crashes, or rescheduled.checked 11 Oct 2026
- Security
- Plaintext secrets are held in memory, while data VSecM saves to disk is encrypted.checked 11 Oct 2026
- Security response
- The stated target is to fix confirmed medium-or-higher severity vulnerabilities within 60 days and respond initially to vulnerability reports within 14 days.checked 5 Oct 2026
- Support
- The project directs users to its Slack workspace for questions and community help, and to GitHub Issues for bug reports, feature requests, or questions.checked 11 Oct 2026
Alternatives to VMware Secrets Manager
- 1
Envshed
Free planWebAPILinuxmacOS7.6From $5 a month - 2
Keyway
Free planWebAPILinuxmacOS7.1From €9 a month - 3
Infisical
Free planWebAPILinuxSelf-hosted7.0From $2 a month - 4

Oracle Cloud Infrastructure Secret Management
Free planWebAPI7.0Free plan - 5
secr
Free planWebAPIExtensionLinux7.0From $6 a month - 6
SikkerKey
Free planWebAPILinuxmacOS7.0From $29 a month