TrollEye CTEM Platform
TrollEye CTEM Platform is web software for managing security exposures across applications, cloud, infrastructure, identities, endpoints, networks, code repo…
What TrollEye CTEM Platform is
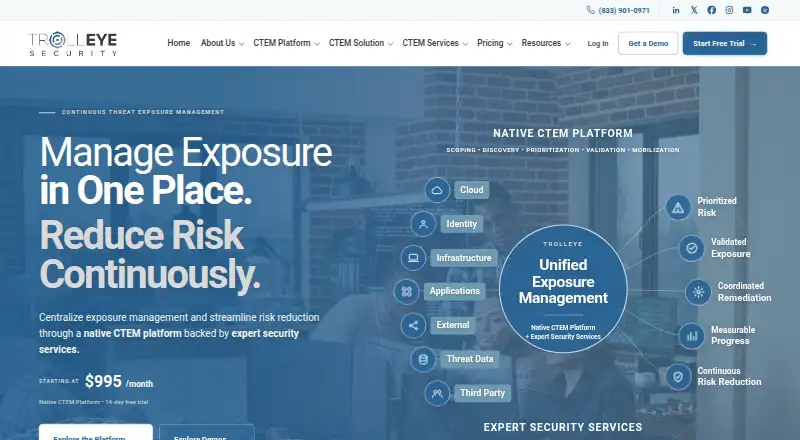
TrollEye CTEM Platform is web software for managing security exposures across applications, cloud, infrastructure, identities, endpoints, networks, code repositories, and third parties. It scopes and discovers exposures, then prioritizes them with contextual risk scoring, attack-path analysis, threat intelligence, asset criticality, and compensating-control context. Validation options include automated checks, manual penetration testing, control-effectiveness testing, and proof of exploitability. Remediation tools provide role-based workflows, Jira and ticket synchronization, root-cause analysis, and remediation initiatives. Listed integrations include GitHub, Jira, Azure DevOps, Slack, Microsoft Teams, AWS, and Microsoft Azure. TrollEye says its AI agents correlate exposure data, identify exploitable attack paths, and suggest remediation actions. The platform preserves security evidence for SOC 2 technical operations but does not replace a CPA firm, formal examination, or broader GRC process.
Good
- Covers applications, cloud, identities, and third parties
- Contextual scoring and attack-path analysis
- Automated and manual validation options
- Jira, GitHub, AWS, and Azure integrations
- 14-day trial available
Watch out
- No free plan
- SOC 2 support does not replace formal examination
Who it suits
It suits focused, growing, mature, and enterprise security teams needing exposure prioritization and remediation workflows. Web access is intended for organizations managing varied assets and compliance evidence.
Verdict
TrollEye combines broad asset coverage, contextual prioritization, validation, and remediation workflows in a web platform. Its paid plans target teams with different program sizes, while enterprise terms require a custom discussion.
Plans and prices
From TrollEye CTEM Platform's own pricing page, checked 4 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| CTEM Essentials | $995 a month | 200 AI vulnerability analyses/month · 4 Apex autonomous engagements/month · 1 business unit · 1 cloud account · 1,000 workloads · 200 monitored assets · 5 users |
| CTEM Growth | $2,995 a month | 1,500 AI vulnerability analyses/month · 12 Apex autonomous engagements/month · 2 business units · 6 cloud accounts · 6,000 workloads · 1,500 monitored assets · 30 users |
| CTEM Professional | $8,995 a month | 5,000 AI vulnerability analyses/month · 32 Apex autonomous engagements/month · 6 business units · 20 cloud accounts · 20,000 workloads · 5,000 monitored assets · 12 service credits/month · Unlimited users |
| CTEM Enterprise | Priced on request | Custom analysis and engagement capacity · 6+ business units · 20+ cloud accounts · 20,000+ workloads · 5,000+ monitored assets · 12+ service credits/month · Unlimited users |
The facts
Each one read from TrollEye CTEM Platform's own pages, with the date it was checked.
What it does
- AI agents
- TrollEye says its AI agents correlate exposure data, surface exploitable attack paths, and recommend remediation actions.checked 4 Oct 2026
- Asset coverage
- It assesses applications, cloud, infrastructure, identities, endpoints, networks, code repositories, and third parties.checked 4 Oct 2026
- Compliance scope
- TrollEye says it supports technical security operations and evidence for SOC 2 but does not replace the CPA firm, formal examination, or broader GRC process.checked 4 Oct 2026
- Integrations
- The platform page lists GitHub, Jira, Azure DevOps, Slack, Microsoft Teams, AWS, and Microsoft Azure as integrations.checked 4 Oct 2026
- Prioritization
- Native prioritization capabilities include context-based risk scoring, attack-path analysis, threat intelligence, and compensating-control context.checked 4 Oct 2026
- Purpose
- The platform scopes, discovers, prioritizes, validates, and mobilizes remediation for security exposures.checked 4 Oct 2026
- Remediation workflows
- It offers role-based workflows, Jira and ticket synchronization, root-cause analysis, and remediation initiatives.checked 4 Oct 2026
- Security evidence
- The SOC 2 solution page says TrollEye preserves findings, testing results, ownership, remediation, retesting, and verification history to support SOC 2 evidence.checked 4 Oct 2026
- Support
- Every CTEM package includes regular cadence calls with the TrollEye team.checked 4 Oct 2026
- Validation
- The platform lists automated validation, manual penetration testing, control-effectiveness testing, and proof of exploitability.checked 4 Oct 2026
The company
- Founded
- 2019checked 28 Sep 2026
- Headquarters
- Cumming, Georgia, United Stateschecked 28 Sep 2026
- Intended teams
- The pricing page describes Essentials for focused teams, Growth for growing security programs, Professional for mature programs, and Enterprise for enterprise environments.checked 4 Oct 2026
Money
- Trial
- The site advertises an eligible 14-day free trial of the CTEM platform.checked 4 Oct 2026
Alternatives to TrollEye CTEM Platform
- 1
AttackIQ Platform
Free planWebAPILinuxmacOS7.9From $4,995 a month - 2
runZero
Free planWebAPILinuxmacOS7.8Free plan - 3
Mondoo CSPM
Free planOpen sourceWebAPIExtensionLinux7.7Free plan - 4
Obsonis Exposure Management Platform
AndroidiOSWebAPI7.0From $25 a month - 5
Qualys Enterprise TruRisk Platform
AndroidiOSWebAPI6.9 - 6
CrowdStrike Falcon Surface
WebLinuxmacOSWindows6.6