Trivy Operator
Trivy Operator is a free, self-hosted Kubernetes operator that scans clusters for security issues and stores reports as Kubernetes resources, accessible thro…
What Trivy Operator is
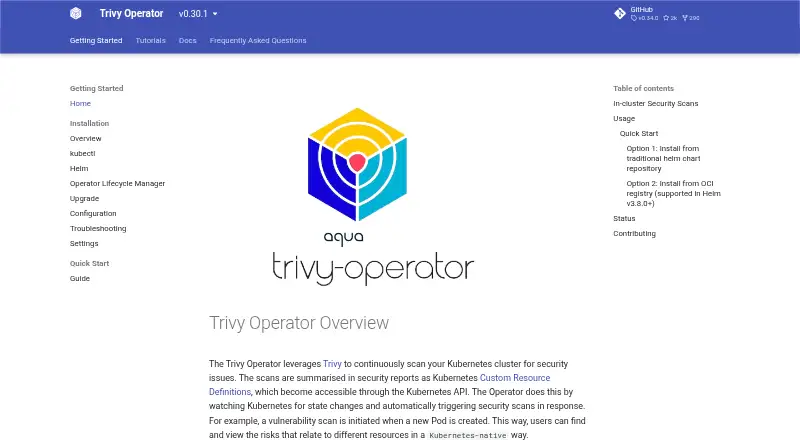
Trivy Operator is a free, self-hosted Kubernetes operator that scans clusters for security issues and stores reports as Kubernetes resources, accessible through the Kubernetes API. It watches for changes in Kubernetes state and can initiate scans when resources such as Pods are created. Reports cover workload vulnerabilities, configuration audits, exposed secrets, RBAC assessments, infrastructure assessments, and deprecated API use. Configuration audits can apply predefined rules or custom Open Policy Agent policies. The operator also produces compliance reports for Kubernetes hardening guidance, the CIS Kubernetes Benchmark, and Pod Security Standards profiles, as well as Software Bill of Materials reports for workloads. A /metrics endpoint is exposed by default for Prometheus to scrape. Installation options include Helm, kubectl manifests, and Operator Lifecycle Manager; Helm is recommended for tracking custom configuration. Trivy Operator has no user interface. The project is described as incubating, and some APIs and custom resource definitions may change.
Good
- Free plan.
- Scans Kubernetes workloads for vulnerabilities.
- Reports cover secrets, RBAC, configuration, and deprecated APIs.
- Produces compliance and SBOM reports.
- Can be installed with Helm, kubectl, or Operator Lifecycle Manager.
Watch out
- No user interface.
- Project is incubating.
- Some APIs and custom resource definitions may change.
Who it suits
Trivy Operator suits teams managing Kubernetes clusters that want security scans and reports available through the Kubernetes API. It is intended for self-hosted use and has no user interface.
Verdict
Trivy Operator covers multiple Kubernetes security checks and exposes reports and metrics within a cluster. Teams should account for its lack of a user interface and the possibility of project API changes.
Plans and prices
From Trivy Operator's own pricing page, checked 2 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Trivy Operator | Free | Open source Kubernetes operator · scans security issues and stores reports as Kubernetes resources |
The facts
Each one read from Trivy Operator's own pages, with the date it was checked.
What it does
- Automatic scans
- It watches Kubernetes state changes and triggers scans when resources change, such as when a Pod is created.checked 2 Oct 2026
- Compliance
- It produces compliance reports for Kubernetes hardening guidance, the CIS Kubernetes Benchmark, and Pod Security Standards profiles.checked 2 Oct 2026
- Compliance reports
- Built-in compliance outputs cover NSA/CISA Kubernetes hardening guidance, CIS Kubernetes Benchmark 1.23, and Kubernetes Pod Security Standards baseline and restricted profiles.checked 15 Oct 2026
- Configuration auditing
- It audits Kubernetes resources with predefined rules or custom Open Policy Agent policies.checked 15 Oct 2026
- Configuration audits
- It audits Kubernetes resource configuration using predefined rules or custom Open Policy Agent policies.checked 2 Oct 2026
- Configuration limits
- Documented defaults include a five-minute scan-job timeout, a maximum of 10 concurrent scan jobs, one concurrent node-collector job, and 30-second retry delay.checked 15 Oct 2026
- Custom resources
- The project defines namespaced VulnerabilityReport, ConfigAuditReport, ExposedSecretReport, RbacAssessmentReport, InfraAssessmentReport and SbomReport resource types plus cluster-level report types.checked 15 Oct 2026
- Documentation depth
- Official documentation includes installation, configuration, troubleshooting, quick starts, tutorials, integrations, scanner settings, private registries, compliance, CRD schemas, and FAQ material.checked 15 Oct 2026
- Exposed secrets
- It creates reports identifying exposed secrets and their locations in cluster workloads.checked 15 Oct 2026
- Helm installation
- The Helm instructions add Aqua's chart repository and install into a trivy-system namespace.checked 15 Oct 2026
- Independent field benchmark
- Safeguard reported a 31-minute first full-coverage time for 1,400 pods and a 14-second median scan for an 800 MB image in its v0.30/v0.70 test.checked 15 Oct 2026
- Infrastructure assessment
- It assesses configuration of Kubernetes core components such as etcd, the API server, scheduler, and controller manager.checked 15 Oct 2026
- Installation
- It can be installed through Helm, kubectl manifests, or Operator Lifecycle Manager; Helm is recommended for tracking custom configuration.checked 2 Oct 2026
- Installation methods
- Installation is documented through static YAML manifests, Helm, and Operator Lifecycle Manager.checked 15 Oct 2026
- Integrations
- Official documentation describes metrics, Lens extension, webhook, and Policy Reporter integrations.checked 2 Oct 2026
- Kubernetes API
- Security reports are Kubernetes Custom Resource Definitions and are readable through normal Kubernetes API mechanisms.checked 15 Oct 2026
- KubeVela integration
- KubeVela documents a Trivy Operator add-on with a metrics service reachable on port 9115.checked 15 Oct 2026
- Lens extension
- A separate Aqua Lens extension displays vulnerability, misconfiguration, exposed-secret, RBAC, and Kubernetes infrastructure reports; its documented prerequisite is Lens 4.0 or newer.checked 15 Oct 2026
- License
- The repository is licensed under Apache-2.0.checked 15 Oct 2026
- Limit: multi-cluster operations
- Safeguard's comparison says Trivy Operator has no built-in multi-cluster console and requires external aggregation for large estates.checked 15 Oct 2026
- Limit: native UI
- Safeguard says the operator produces CRDs but has no native dashboard, so users commonly add DefectDojo, Dependency-Track, or vendor consoles.checked 15 Oct 2026
- Limit: reporting and UI
- PeerSpot reviewers repeatedly request better report interpretation, PDF/CSV outputs, and built-in report analysis or a user-friendly interface.checked 15 Oct 2026
- Limit: runtime and malware coverage
- PeerSpot reviewers say Trivy lacks dynamic runtime scanning and that malware or anomaly detection may require a separate tool such as ClamAV.checked 15 Oct 2026
The company
- Company ownership status
- Crunchbase describes Aqua Security as a private Series E company headquartered in Ramat Gan, Tel Aviv, Israel, with a 251–500 employee range.checked 15 Oct 2026
Alternatives to Trivy Operator
- 1
Kubescape
Free planOpen sourceAPILinuxmacOSSelf-hosted8.2From $30 a month - 2
Kyverno
Free planOpen sourceWebAPILinuxmacOS7.7Free plan - 3
Open Policy Agent Gatekeeper
Free planOpen sourceAPILinuxSelf-hosted7.2Free plan - 4
Sysdig Secure
WebAPILinuxmacOS7.2From $20 a month - 5
Fairwinds Polaris
Free planWebLinuxmacOSSelf-hosted7.1Free plan - 6
KSPM Pro
Free planWeb6.5From $100 a month