Strig
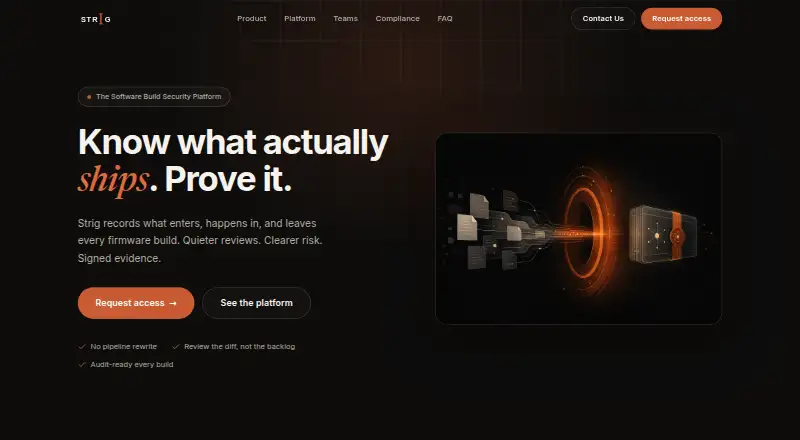
Strig monitors firmware builds and records their inputs, compiler and linker events, and outputs.
What Strig is
Strig monitors firmware builds and records their inputs, compiler and linker events, and outputs. It turns that record into risk findings and signed audit evidence, combining static analysis, software composition analysis, SBOM generation, CVE tracking, and binary analysis in a report and release gate. Build comparisons can highlight dependency updates, hardening flags, and resolved findings. Policy thresholds determine a pass or fail verdict and a CI exit code. Strig generates CycloneDX SBOMs from compiled source and binaries, including flags for undeclared components. It can ingest findings from existing tools and capture builds through systems such as Make, CMake, Bazel, Yocto, and Ninja. Deployment options include SaaS, on-premise, and fully air-gapped environments; on-premise and air-gapped deployments keep source, binaries, and build records inside the customer network. For those scans, Strig says its own network access is blocked and information stays inside the environment by design. It targets firmware and embedded software teams and produces evidence for assessors, but does not certify customers. Pricing is on request, and the listed platform is Linux.
Good
- Combines multiple analyses in one report and release gate
- Creates CycloneDX SBOMs from source and binaries
- Build comparisons surface release changes
- Supports air-gapped and on-premise deployment
- Captures builds from several build systems
Watch out
- Pricing is available on request
- Air-gap update and offline licensing details are being finalized
- Does not certify customers
Who it suits
Strig is aimed at firmware and embedded software teams, including R&D, DevSecOps, product security, CISO, quality, and compliance roles. It may suit organizations that need build records and evidence for assessors.
Verdict
Strig brings build monitoring, security analysis, and policy-based release decisions together for firmware and embedded software. Teams considering an air-gapped deployment should account for the still-finalizing update and licensing details.
Plans and prices
From Strig's own pricing page, checked 8 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Strig | Priced on request | Licensed per environment · price depends on build volume and deployment model |
The facts
Each one read from Strig's own pages, with the date it was checked.
What it does
- Air-gap details
- The operational details for air-gapped vulnerability-data updates and offline licensing are still being finalized, according to the FAQ.checked 8 Oct 2026
- Analysis
- The platform combines SAST, software composition analysis, SBOM generation, CVE tracking, and binary analysis in one report and release gate.checked 8 Oct 2026
- Build comparison
- Build-to-build diffs highlight release changes, including dependency updates, hardening flags, and resolved findings.checked 8 Oct 2026
- Build gate
- Policy thresholds produce a deterministic pass or fail verdict and a CI exit code.checked 8 Oct 2026
- Coding standards
- The site lists SEI CERT C/C++, MITRE CWE, MISRA C:2025/C++:2023, OASIS SARIF 2.1.0, and the OpenSSF Compiler Hardening Guide as supported.checked 8 Oct 2026
- Deployment
- The site describes on-premise, fully air-gapped, and SaaS deployment options; on-premise and air-gapped deployments keep source, binaries, and build records inside the customer network.checked 8 Oct 2026
- Integrations
- Strig can ingest findings from existing tools and capture builds using systems that invoke compiler and linker commands, including Make, CMake, Bazel, Yocto, and Ninja.checked 8 Oct 2026
- Intended users
- The product is aimed at firmware and embedded software teams, including R&D, DevSecOps, product security, CISO, quality, and compliance roles.checked 8 Oct 2026
- Not a certification
- Strig says it produces evidence for assessors but does not certify customers.checked 8 Oct 2026
- Purpose
- Strig monitors firmware builds, records inputs, compile and link events, and outputs, then produces risk findings and signed audit evidence.checked 8 Oct 2026
- SBOM
- Strig generates CycloneDX SBOMs from compiled source and binaries and flags undeclared components.checked 8 Oct 2026
- Security and data
- For on-premise and air-gapped scans, the site says Strig blocks its own network access and that no information leaves the environment by design.checked 8 Oct 2026
- Support
- Customers can request access for a pilot or contact the company to discuss build and compliance requirements.checked 8 Oct 2026
Alternatives to Strig
- 1
Sigstore
Free planOpen sourceWebAPILinuxmacOS7.6Free plan - 2
GUAC
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 3
OX Security
Free planWebAPIExtensionLinux7.4Free plan - 4
ActiveState Platform
Free planWebAPILinuxmacOS7.2Free plan - 5
JFrog Artifactory
WebAPILinuxSelf-hosted7.1From $50 a month - 6
Wisec
Free planWebAPILinuxmacOS7.1From €990 a year