Wisec
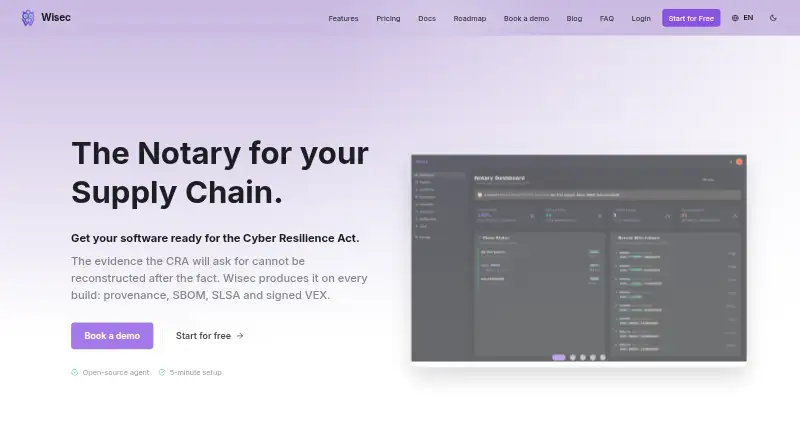
Wisec collects and preserves software build evidence to help teams prepare for Cyber Resilience Act requirements.
What Wisec is
Wisec collects and preserves software build evidence to help teams prepare for Cyber Resilience Act requirements. It links builds in a cryptographically signed chain using Ed25519 and records SLSA provenance with public Sigstore/Rekor timestamps. For each build, it can generate signed CycloneDX software bills of materials and VEX documents describing whether detected CVEs are exploitable. Eleven anomaly rules check project history and known-bad patterns. Teams can set CI policies to block or warn on secrets, vulnerable dependencies, unapproved contributors, risk thresholds, and CVE severity. Wisec supports GitLab CI, GitHub Actions, Jenkins, and Azure DevOps, and imports SARIF findings from compatible scanners such as CodeQL, Semgrep, Snyk, and Trivy. It maps evidence to NIS2, SOC2, ISO 27001, and CRA and exports PDF reports; for CRA and ISO 27001, the mapping is evidence support, not a claim of conformity. The Free plan includes 3 projects and 1,000 builds/month. Business is billed €990/yr at the founder rate, and Pro is billed €2,990/yr at the founder rate.
Good
- Signed build chain uses Ed25519 and SLSA provenance.
- Generates signed CycloneDX SBOMs and VEX documents.
- Policy gates can block or warn on specified risks.
- Imports findings from SARIF-compatible scanners.
- Data residency is stated as 100% in the EU.
Watch out
- Free is limited to 3 projects and 1,000 builds/month.
- Business and Pro founder rates have higher standard rates from 2027.
- Self-hosting is available only to Enterprise customers.
- CircleCI and Travis CI support is listed as coming soon.
Who it suits
The Free plan is described for small projects and security exploration; Business is for growing teams that need notarization. Pro is aimed at organizations seeking full control, while Enterprise adds self-hosting options.
Verdict
Wisec brings build evidence, policy gates, scanner findings, and compliance evidence mapping into a CI-focused service. Check plan limits and deployment requirements, and note that CRA and ISO 27001 evidence mapping is not a conformity claim.
Plans and prices
From Wisec's own pricing page, checked 5 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free | Free | 3 projects · 1,000 builds/month · 30 days history · 1 PDF certificate/month · Community support |
| Business | €990 a year | 10 projects · 20,000 builds/month · 1 year history · Email support (48h response) · €990/yr (founder rate); standard rate €5,000/yr from 2027 |
| Pro | €2,990 a year | Unlimited projects and builds · Lifetime archives · Priority support (24h response) · €2,990/yr (founder rate); standard rate €15,000/yr from 2027 |
| Enterprise | Priced on request | Unlimited projects and builds · On-premise or private cloud deployment · Dedicated 24/7 priority support · Custom billing · Custom quote |
The facts
Each one read from Wisec's own pages, with the date it was checked.
What it does
- Anomaly detection
- Eleven rules run on every build, including five calibrated to project history and six for known-bad patterns.checked 5 Oct 2026
- CI integrations
- Dedicated CI/CD support is listed for GitLab CI, GitHub Actions, Jenkins, and Azure DevOps; CircleCI and Travis CI are described as coming soon.checked 5 Oct 2026
- Compliance evidence
- Wisec maps evidence to NIS2, SOC2, ISO 27001, and CRA and can export audit-ready PDF reports; for CRA and ISO 27001 it says this is evidence mapping, not a conformity claim.checked 5 Oct 2026
- Cryptographic records
- Builds are linked in a chain and signed with Ed25519, with SLSA provenance and public Sigstore/Rekor timestamping.checked 5 Oct 2026
- Open-source agent
- The CI agent is open source under Apache-2.0, while the platform is managed and hosted in the EU.checked 5 Oct 2026
- Policy gate
- Users can define block or warn policies for secrets, vulnerable dependencies, unapproved contributors, risk thresholds, and CVE severity, enforced at the CI gate.checked 5 Oct 2026
- Purpose
- Wisec collects, signs, and preserves software build evidence such as provenance, SBOM, SLSA, and VEX for Cyber Resilience Act readiness.checked 5 Oct 2026
- SBOM and VEX
- It generates signed CycloneDX SBOMs and signed VEX documents describing the exploitability status of detected CVEs.checked 5 Oct 2026
- Scanner imports
- Wisec imports SARIF v2.1.0 findings from CodeQL, Semgrep, Snyk, Trivy, or other SARIF-compatible tools.checked 5 Oct 2026
- Security and residency
- The maker says data is encrypted in transit and at rest, platform data is hosted in France, and data residency is 100% in the EU.checked 5 Oct 2026
- Self-hosting
- Self-hosting is available to Enterprise customers, with on-premise or private cloud deployment listed.checked 5 Oct 2026
- Source code handling
- Wisec says its agent runs in CI and does not clone repositories; since agent v1.2.0 it withholds scanner-quoted code before sending findings.checked 5 Oct 2026
- Support
- Free includes community support, Business lists email support with a 48-hour response, Pro lists priority support with a 24-hour response, and Enterprise lists dedicated 24/7 priority support.checked 5 Oct 2026
- Target users
- The Free plan is described for small projects and security exploration, Business for growing teams requiring notarization, and Pro for organizations demanding full control.checked 5 Oct 2026
The company
- Headquarters
- Saint-Priest, Francechecked 28 Sep 2026
The full review of Wisec
Wisec is a CI-focused service for collecting and preserving software-build security evidence. It is best suited to teams that need signed build records, release controls, and audit evidence in their delivery pipeline. Its free plan is a practical starting point, but meaningful growth brings steep capacity and price jumps.
Overview
Wisec links builds into a cryptographically signed chain using Ed25519, with SLSA provenance and public Sigstore/Rekor timestamping. It also generates signed CycloneDX SBOMs and VEX documents describing whether detected CVEs are exploitable. That combination gives teams a record tied to specific builds, not just a collection of security documents.
The CI agent runs without cloning repositories, and Wisec says it withholds scanner-quoted code before transmitting findings. The agent is open source under Apache-2.0; the platform is managed and hosted in the EU. The maker says data is encrypted in transit and at rest, with platform data hosted in France and residency in the EU. Self-hosting is limited to Enterprise, so organizations requiring deployment in their own environment must budget for a custom arrangement.
Key features
Eleven anomaly rules run on each build: five calibrated to project history and six aimed at known-bad patterns. Teams can define block or warn policies for secrets, vulnerable dependencies, unapproved contributors, risk thresholds, and CVE severity, then enforce them at the CI gate. This is useful for teams that want security checks to affect release decisions; it also puts policy design and maintenance at the center of the service's value.
Dedicated CI/CD integrations cover GitLab CI, GitHub Actions, Jenkins, and Azure DevOps. CircleCI and Travis CI are described as coming soon, so teams on those systems should not count on dedicated support now. Wisec also imports SARIF v2.1.0 findings from CodeQL, Semgrep, Snyk, Trivy, and other compatible tools, letting teams bring scanner results into the build-evidence workflow.
For audit work, Wisec maps evidence to NIS2, SOC2, ISO 27001, and CRA and exports PDF reports. Its CRA and ISO 27001 mapping is evidence support, not a conformity claim. Teams should treat it as help organizing evidence rather than a substitute for establishing compliance.
Pricing
Wisec has a free plan, paid plans, and a 14-day trial. Business and Pro show founder-rate pricing alongside higher standard rates from 2027; those future rates materially change the long-term cost calculation.
| Plan | Price | Limits and support |
|---|---|---|
| Free | free | 3 projects, 1,000 builds/month, 30 days of history, 1 PDF certificate/month, community support |
| Business | €990 a year; billed €990/yr at founder rate, standard rate €5,000/yr from 2027 | 10 projects, 20,000 builds/month, 1 year of history, email support with a 48-hour response |
| Pro | €2,990 a year; billed €2,990/yr at founder rate, standard rate €15,000/yr from 2027 | Unlimited projects and builds, lifetime archives, priority support with a 24-hour response |
| Enterprise | Custom pricing | Unlimited projects and builds, on-premise or private cloud deployment, dedicated 24/7 priority support, custom billing |
Free is aimed at small projects and security exploration, but the 30-day history and single monthly PDF certificate make it a limited home for ongoing audit records. Business targets growing teams needing notarization and expands build volume and retention, though its 10-project cap and 48-hour email support remain constraints. Pro removes project and build quotas and adds lifetime archives and faster priority support, making it the more suitable paid tier for organizations demanding full control of capacity. Enterprise is the only route to on-premise or private cloud deployment; teams pay custom pricing for that flexibility and dedicated support.
Platforms
Wisec supports API, Linux, macOS, self-hosted, web, and Windows environments. Self-hosted deployment is an Enterprise option rather than a general deployment choice.
Who it's for
Wisec fits software teams that already use CI and scanners and want build-linked provenance, SBOMs, VEX, policy gates, and exportable compliance evidence in one workflow. It is particularly relevant to teams preparing CRA evidence or managing audit requirements across NIS2, SOC2, and ISO 27001. Small teams can explore the service at no cost; teams with high build volumes, long retention needs, or deployment-control requirements should weigh the paid tiers carefully. It is a weaker fit for teams that need dedicated CircleCI or Travis CI support today, or that expect evidence mapping itself to establish conformity.
Pros and cons
- Pros: Signed build chains, SLSA provenance, signed SBOMs, and VEX documents connect several kinds of security evidence to builds.
- Pros: Block-or-warn policies and anomaly rules can make security findings part of CI release decisions.
- Pros: SARIF imports support findings from several named scanners, while PDF exports and framework mapping support audit preparation.
- Pros: The open-source CI agent runs without cloning repositories; the maker also says it withholds scanner-quoted code and keeps platform data in the EU.
- Cons: Free retention is only 30 days, with one PDF certificate per month and a 1,000-build monthly cap.
- Cons: Business and Pro list founder rates alongside much higher standard rates from 2027, which makes future subscription cost a major consideration.
- Cons: Self-hosting requires Enterprise, and dedicated CircleCI and Travis CI support is not yet described as available.
Alternatives
For a broader comparison, browse Software Supply Chain Security Software. Consider Sonatype Nexus Repository if its free Community Edition, ecosystem support, CI/CD integration, or external PostgreSQL option better matches your repository needs. ActiveState Platform may suit organizations whose free tier for public projects is sufficient or those seeking its paid enterprise offering.
DevGuard is another freemium option in this category. Choose GUAC if you want a free, MIT-licensed project and are prepared to set it up with Docker, Docker Compose, and jq. StepSecurity offers a free Community plan for unlimited public repositories on GitHub-hosted runners in GitHub Cloud.
Chainloop offers a free, open-source, self-hosted Community Edition without a UI or curated policy library, a different trade-off for teams prioritizing self-hosting. SafeDep Platform may appeal to teams that want its free open-source tools without a SafeDep account. Choose Sigstore if free signing infrastructure for developers and software providers is the priority.
Verdict
Wisec is a strong fit for CI-driven teams that need signed, build-linked evidence and enforceable security policies, especially when audit preparation matters. Its clearest advantages are the combination of provenance, scanner imports, policy gates, and evidence exports. Look elsewhere if you need self-hosting without Enterprise, current dedicated CircleCI or Travis CI support, or a paid plan whose standard pricing remains close to the founder rate.
Alternatives to Wisec
- 1
Sigstore
Free planOpen sourceWebAPILinuxmacOS7.6Free plan - 2
GUAC
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 3
OX Security
Free planWebAPIExtensionLinux7.4Free plan - 4
ActiveState Platform
Free planWebAPILinuxmacOS7.2Free plan - 5
JFrog Artifactory
WebAPILinuxSelf-hosted7.1From $50 a month - 6
DevGuard
Free planWebAPILinuxmacOS7.0From €449.10 a month