SourceTrust
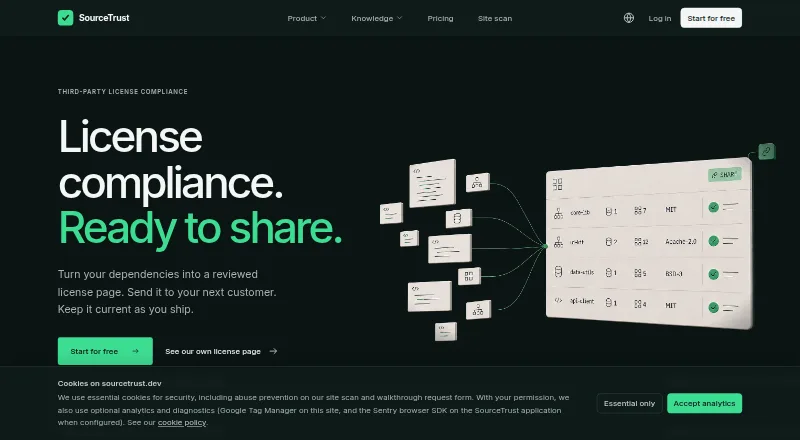
SourceTrust helps teams review third-party software licenses and publish a shareable compliance page for products they ship.
What SourceTrust is
SourceTrust helps teams review third-party software licenses and publish a shareable compliance page for products they ship. It brings direct and transitive dependencies from repositories, lockfiles, and SBOMs into one inventory, then checks retrieved packages against registry digests and reads their license text. Teams must review and confirm records before publication, and the platform flags packages needing a decision. Listed repository connections include GitHub, GitLab, and Azure DevOps; supported inputs include lockfiles and SBOMs, with 14 formats across 9 ecosystems. Outputs include a hosted attestation page, THIRD_PARTY_LICENSES.md, NOTICE, CycloneDX, SPDX, JSON, CSV, plist, and branded PDF. Repository synchronization and publish-drift checks flag differences from the published snapshot. Pages can be password-protected and excluded from search engines. SourceTrust says it reads lockfiles and SBOMs rather than source code, and parses lockfiles in the browser before upload. Eligible public GitHub projects can publish for $0, subject to fair use and SourceTrust attribution. The company describes the software as tooling, not legal advice.
Good
- Collects dependencies from repositories, lockfiles, and SBOMs
- Flags packages needing a team decision
- Offers multiple license and SBOM export formats
- Pages can be password-protected
Watch out
- Standard project billing starts on first publish or export download
- Free publishing is limited to eligible public GitHub projects
- Free publishing requires fair use and SourceTrust attribution
Who it suits
SourceTrust suits teams that need to review dependencies and publish license compliance information for shipped products. Eligible public GitHub projects may qualify for its free publishing option; it is software tooling, not legal advice.
Verdict
SourceTrust combines dependency inventory, license review, and compliance outputs for shipped products. Teams should note the publication-based billing trigger and that the product is not legal advice.
Plans and prices
From SourceTrust's own pricing page, checked 29 Sep 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Open source | Free | eligible public GitHub repository · fair use applies · SourceTrust attribution |
| Per project — monthly | $29 a month | per shipped product · unlimited users · two watched branches · Monthly |
| Per project — yearly | $299 a year | per shipped product · unlimited users · two watched branches · Yearly |
| Extra watched branch | $550 a month | per project · beyond the two included branches · Same monthly or yearly choice as your plan |
| Custom domain | $49,499 a month | one hostname for every attestation page in your organization · non-refundable once provisioned · Same monthly or yearly choice as your plan |
| Security monitoring | — | organization-wide · daily OSV advisory scans · vendor-only findings · Same monthly or yearly choice as your plan |
The facts
Each one read from SourceTrust's own pages, with the date it was checked.
What it does
- Audience and limitation
- The company describes the product as license compliance infrastructure for shipped products and says it is software tooling, not a law firm or legal advice.checked 29 Sep 2026
- Change monitoring
- Repository sync and publish-drift checks flag when the live inventory differs from the published snapshot.checked 29 Sep 2026
- Data access
- SourceTrust says it reads lockfiles and SBOMs, never source code, and parses lockfiles in the browser before upload.checked 29 Sep 2026
- Exports
- Outputs include a hosted attestation page, THIRD_PARTY_LICENSES.md, NOTICE, CycloneDX, SPDX, JSON, CSV, plist, and branded PDF.checked 29 Sep 2026
- Integrations
- The site lists GitHub, GitLab, and Azure DevOps repository connections, plus lockfile and SBOM imports.checked 29 Sep 2026
- Inventory
- It gathers direct and transitive dependencies from repositories, lockfiles, and SBOMs into one inventory.checked 29 Sep 2026
- Open source eligibility
- Eligible public GitHub projects can publish an attestation page for $0 with no card or trial clock, subject to fair use and SourceTrust attribution.checked 29 Sep 2026
- Purpose
- SourceTrust helps teams review third-party software licenses and publish a shareable license compliance page for products they ship.checked 29 Sep 2026
- Review gates
- Nothing is published until the team has reviewed and confirmed the record, and the product flags packages that need a decision.checked 29 Sep 2026
- Security controls
- Pages can be password-protected and excluded from search engines, and optional vulnerability findings remain vendor-only.checked 29 Sep 2026
- Support
- SourceTrust offers a live walkthrough and lists [email protected] for platform questions.checked 29 Sep 2026
- Supported inputs
- The platform overview says it supports 14 formats across 9 ecosystems, including CycloneDX SBOM uploads.checked 29 Sep 2026
- Verification
- SourceTrust retrieves the shipped package, checks it against the registry digest, and reads the license text inside it.checked 29 Sep 2026
The company
- Founded
- 2026checked 28 Sep 2026
- Headquarters
- Copenhagen, Denmarkchecked 28 Sep 2026
Money
- Free review
- Projects, dependency imports, and license reviews are free for as long as needed; standard project billing starts on first publish or export download.checked 29 Sep 2026
Alternatives to SourceTrust
- 1
DeepFilterNet
Free planOpen sourceAPILinuxmacOSSelf-hosted7.6Free plan - 2
FOSSology
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 3
ScanCode.io
Free planWebAPILinuxmacOS7.0Free plan - 4
FOSSA
Free planWebAPILinuxSelf-hosted6.4Free plan - 5
DejaCode
WebAPILinuxSelf-hosted6.3From $500 a month - 6
FossID Workbench
WebAPILinuxSelf-hosted6.2