ShadowStrike Phantom
ShadowStrike Phantom is an open-source endpoint protection platform for Windows that is in pre-alpha and active development.
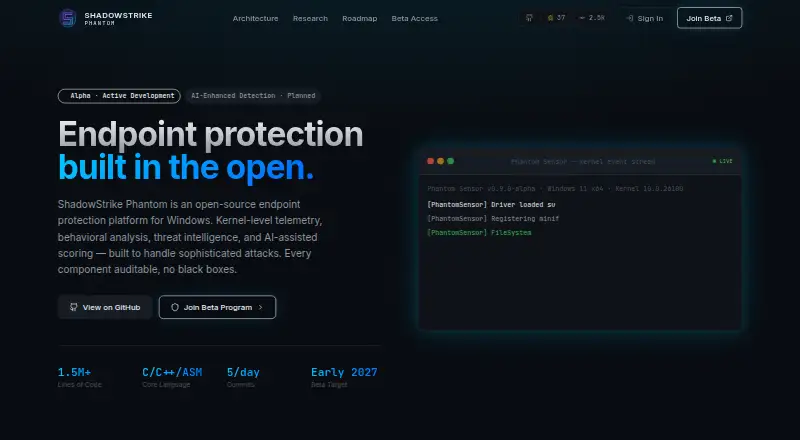
What ShadowStrike Phantom is
ShadowStrike Phantom is an open-source endpoint protection platform for Windows that is in pre-alpha and active development. Its minifilter driver is described as intercepting file reads, writes, creates, and deletes. An attack-chain tracker correlates kernel events across process trees and maps activity to MITRE ATT&CK, while listed detection capabilities include memory inspection, syscall tracing, network detection, anti-evasion, and ransomware detection. The platform also lists IOC lookups, STIX/TAXII feed support, and a URL reputation engine. It defines more than 550 MITRE ATT&CK technique IDs, with 14 rules active and 18 pending. The source code, kernel callbacks, detection rules, and heuristics are publicly auditable on GitHub under an AGPL-3.0 license. AI-enhanced detection is marked as planned, while ML inference is described as part of the scan pipeline. The roadmap places user-space detection engines at 76% completion and notes that core scan engines, the Windows service layer, and end-to-end integration remain among the work ahead. The maker explicitly says the product is not for production use.
Good
- Open-source under an AGPL-3.0 license
- Detection features include memory and syscall analysis
- Maps attack chains to MITRE ATT&CK
- Source code and detection rules are publicly auditable
Watch out
- Pre-alpha and not for production use
- Only 14 detection rules are active
- Core scan engines and service integration remain on roadmap
- AI-enhanced detection is planned
Who it suits
It may interest Windows users and security developers who want to inspect an open-source endpoint protection project in development. The roadmap describes future consumer-focused and enterprise-focused products, both planned for public beta in Phase 3.
Verdict
ShadowStrike Phantom lists a broad set of endpoint detection capabilities and makes its code and rules publicly auditable. Its pre-alpha status and unfinished scan engines make it unsuitable for production use.
The facts
Each one read from ShadowStrike Phantom's own pages, with the date it was checked.
What it does
- AI status
- AI-enhanced detection is marked planned on the homepage, which also describes ML inference in the scan pipeline as a capability.checked 4 Oct 2026
- Behavioral detection
- Its attack-chain tracker correlates kernel events across process trees and maps activity to MITRE ATT&CK with real-time threat scoring.checked 9 Oct 2026
- Behavior analysis
- The site says its attack-chain tracker correlates kernel events across process trees and maps them to MITRE ATT&CK.checked 4 Oct 2026
- Detection coverage
- The site says 550+ MITRE ATT&CK technique IDs are defined, with 14 rules active and 18 pending.checked 4 Oct 2026
- Development status
- The site describes Phantom as pre-alpha and says it is not for production use.checked 9 Oct 2026
- Future integrations
- The planned Phantom XDR phase lists SIEM connectors for Elastic SIEM, Splunk, Microsoft Sentinel, and OpenSearch, plus MISP and OpenCTI integrations.checked 4 Oct 2026
- Integrations
- The roadmap lists planned SIEM connectors for Elastic SIEM, Splunk, Microsoft Sentinel, and OpenSearch, plus MISP and OpenCTI threat-intelligence integrations.checked 9 Oct 2026
- Intended users
- The roadmap describes Phantom Home as targeting consumers and Phantom EDR as targeting enterprise endpoints; both are planned products.checked 9 Oct 2026
- Kernel monitoring
- Phantom Sensor uses a Windows minifilter driver to intercept file-system reads, writes, creates, and deletes.checked 9 Oct 2026
- License
- The site links to an AGPL-3.0 license.checked 4 Oct 2026
- Memory and syscall analysis
- Listed capabilities include detecting process injection and hollowing, shellcode, ROP chains, direct syscalls, and NTDLL integrity issues.checked 9 Oct 2026
- Not for production
- The maker labels the product pre-alpha and not for production use.checked 4 Oct 2026
- Product
- ShadowStrike Phantom is an open-source endpoint protection platform for Windows.checked 9 Oct 2026
- Ransomware protection
- Listed ransomware features include honeypot file monitoring, shadow-copy protection, backup integrity checks, and entropy analysis.checked 9 Oct 2026
- Roadmap
- The roadmap describes Phantom Home as consumer-focused and Phantom EDR as enterprise-focused, with both public betas planned in Phase 3.checked 4 Oct 2026
- Roadmap status
- The roadmap says the kernel-driver phase is 97% complete, with driver signing pending, and user-space engines are 76% complete.checked 9 Oct 2026
- Security infrastructure
- The architecture page describes AES-GCM and RSA-OAEP for IPC channel encryption and Authenticode validation for loaded modules.checked 4 Oct 2026
- Support
- The site provides [email protected] and directs users to GitHub Discussions for community discussions.checked 9 Oct 2026
- Threat detection
- Listed detection features include memory inspection, syscall tracing, network detection, anti-evasion, and ransomware detection.checked 4 Oct 2026
- Threat intelligence
- The site lists IOC lookups, STIX/TAXII feed support, and a URL reputation engine.checked 9 Oct 2026
- Transparency
- The maker says source code is publicly auditable on GitHub and describes the project as licensed under AGPL-3.0.checked 9 Oct 2026
Alternatives to ShadowStrike Phantom
- 1
AEGIS
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 2

AppCheck
Free planWebLinuxWindows7.5Free plan - 3

ManageEngine Ransomware Protection Plus
Free planWebSelf-hostedWindows7.4From $6.99 a year - 4
Rubrik Security Cloud
WebAPILinuxmacOS6.9 - 5
Sophos Intercept X for Mobile
AndroidiOS6.8 - 6
NeuShield Ransomware Protection
Free planWebWindows6.7From $24.99 a year