SENTINEL RED
SENTINEL RED is a free, open-source suite for security and quality testing of applications built with large language models.
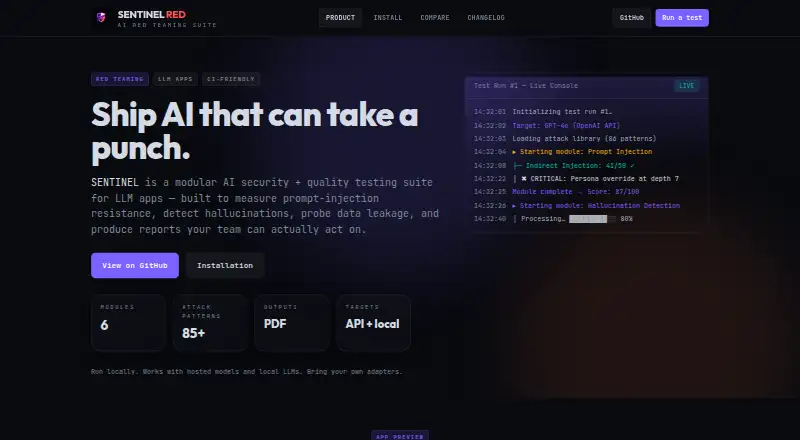
What SENTINEL RED is
SENTINEL RED is a free, open-source suite for security and quality testing of applications built with large language models. Six modules address prompt injection, hallucinations, data leakage, adversarial testing, poisoning, and compliance, with more than 85 attack patterns listed. Tests can target APIs or local systems, hosted models or local LLMs, using user-provided adapters. A typical run involves adding a model target and API key, choosing modules and test depth, watching live results in a WebSocket dashboard, and generating a PDF report with scoring. The REST API can create runs, poll their status, and download reports programmatically. SENTINEL can run locally, in pipelines, or on schedules. The recommended deployment uses Docker Compose and opens the dashboard at localhost:3000. OpenAI and Anthropic keys are shown as configuration examples, with multiple providers supported through environment variables or dashboard settings. Its local-first design is intended to keep secrets on the user’s machine. The project is self-hosted and licensed under AGPL-3.0.
Good
- Six modules cover major LLM security risks
- More than 85 attack patterns listed
- Supports hosted models and local LLMs
- Live WebSocket results and PDF scoring reports
- Runs locally, in pipelines, or on schedules
Watch out
- Self-hosted deployment requires Docker Compose
- AGPL-3.0 license applies
- User-provided adapters are needed for targets
Who it suits
It suits engineers, auditors, product teams, and security teams shipping AI applications. Teams wanting local, pipeline, or scheduled testing can use its API, dashboard, and adapters.
Verdict
SENTINEL RED provides modular LLM testing with live monitoring, report generation, and programmatic control. Its self-hosted, AGPL-3.0 setup suits teams comfortable managing local deployments and provider keys.
The facts
Each one read from SENTINEL RED's own pages, with the date it was checked.
What it does
- API
- The REST API can create runs, poll their status, and download PDF reports programmatically.checked 8 Oct 2026
- Attack library
- The homepage lists more than 85 attack patterns.checked 8 Oct 2026
- Attack patterns
- The homepage lists more than 85 attack patterns.checked 8 Oct 2026
- CI use
- The product says it can run locally, in pipelines, or on schedules.checked 8 Oct 2026
- Deployment
- The installation page recommends running locally with Docker Compose and accessing the dashboard at localhost:3000.checked 8 Oct 2026
- Execution
- SENTINEL is designed to run locally and supports hosted models and local LLMs through adapters.checked 8 Oct 2026
- Installation
- The recommended installation uses Docker Compose and opens the dashboard at localhost:3000.checked 8 Oct 2026
- Intended users
- The site describes SENTINEL as built for engineers, auditors, and security teams shipping AI.checked 8 Oct 2026
- License
- The GitHub repository lists the project under the AGPL-3.0 license.checked 8 Oct 2026
- Live results
- The dashboard streams test results live via WebSocket.checked 8 Oct 2026
- Product
- SENTINEL is a modular AI security and quality testing suite for LLM applications.checked 8 Oct 2026
- Provider configuration
- The installation page shows OpenAI and Anthropic API keys configured through environment variables and says multiple providers are supported.checked 8 Oct 2026
- Providers
- The installation page gives OpenAI and Anthropic API keys as provider configuration examples.checked 8 Oct 2026
- Reports
- Users can generate PDF reports with actionable scoring.checked 8 Oct 2026
- Security handling
- The installation page says its local-first design keeps secrets on the user's machine, and keys can be stored in environment variables or configured in dashboard settings.checked 8 Oct 2026
- Security posture
- The maker says SENTINEL is designed to run locally so users can keep secrets on their own machine.checked 8 Oct 2026
- Targets
- The suite supports API and local targets, hosted models, and local LLMs, with user-provided adapters.checked 8 Oct 2026
- Testing coverage
- Its six modules cover prompt injection, hallucinations, data leakage, adversarial testing, poisoning, and compliance.checked 8 Oct 2026
- Workflow
- Users add a model target and API key, choose modules and test depth, watch results, and generate a report.checked 8 Oct 2026
The company
- Maker
- The site footer says SENTINEL RED was built by Abou D.checked 8 Oct 2026
Alternatives to SENTINEL RED
- 1
OpenSecureAI Scanner
Free planOpen sourceWebAPILinuxmacOS8.1From $49 a month - 2

PromptGuard
Free planWebAPIExtensionLinux7.9From $19 a month - 3
Promptfoo
Free planOpen sourceWebAPILinuxmacOS7.8Free plan - 4
Giskard
Free planOpen sourceWebAPILinuxSelf-hosted7.6Free plan - 5
AIRTA Red Team
Free planOpen sourceWebAPILinuxmacOS7.5Free plan - 6
CyberSecEval
Free planOpen sourceWebAPILinuxmacOS7.5Free plan