SCYTHE
SCYTHE is a continuous Adversarial Exposure Validation platform for enterprise security teams.
What SCYTHE is
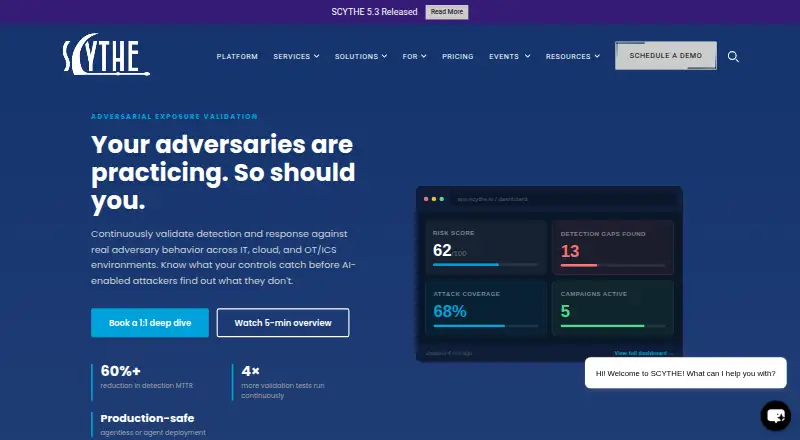
SCYTHE is a continuous Adversarial Exposure Validation platform for enterprise security teams. It runs MITRE ATT&CK-mapped campaigns to examine whether security controls detect, alert, block, and respond to simulated adversary activity. Campaigns can span multiple stages and draw on named threat actors; results connect control outcomes with ATT&CK coverage and identified gaps. AI can create campaigns from plain-language threat descriptions, but a person must approve execution. Deployment options include cloud SaaS, on-premises, hybrid, and air-gapped environments. Listed integrations include security products and services such as CrowdStrike Falcon, Microsoft Defender, Splunk, Microsoft Sentinel, ServiceNow, and Jira. SCYTHE says it integrates bidirectionally with SIEM, SOAR, EDR, ticketing systems, and security controls. The company describes tests as controlled, configurable, logged, and auditable, with explicit authorization required for destructive capabilities. It identifies itself as SOC 2 Type II certified and says it undergoes an annual independent security audit. Pricing is custom-quoted based on environment scope; a free trial is available, but there is no free plan. Managed validation is also offered for organizations wanting campaigns operated and coverage reported for them.
Good
- Maps campaign outcomes to MITRE ATT&CK coverage.
- Supports cloud, on-premises, hybrid, and air-gapped deployment.
- AI-generated campaigns require human approval before execution.
- Tests are described as logged and auditable.
- A free trial is available.
Watch out
- No free plan is offered.
- Pricing is custom-quoted based on environment scope.
- Destructive capabilities require explicit authorization.
Who it suits
It is intended for enterprise security teams, including organizations in financial services, critical infrastructure, federal and defense, and healthcare. Managed validation may suit teams that want SCYTHE to operate campaigns and report detection coverage.
Verdict
SCYTHE focuses on validating control responses through mapped adversary campaigns, with deployment options for varied environments. Teams should weigh the custom-quoted pricing and decide whether to operate campaigns themselves or use its managed service.
Plans and prices
From SCYTHE's own pricing page, checked 30 Sep 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Advanced | Priced on request | Everything in Foundation · AI-driven test plans · CTI-to-emulation automation · air-gapped support · priority support and dedicated CSM · Custom-quoted based on environment scope |
| Enterprise | Priced on request | Everything in Advanced · IT/OT hybrid deployment · SIEM rules validation · agentic workflow threat emulation · Custom-quoted based on environment scope |
| Foundation | Priced on request | Unlimited seats & agents · full ATT&CK module library · full integration support · scheduled campaigns · cloud & hybrid support · Custom-quoted based on environment scope |
| Global Enterprise | Priced on request | Everything in Enterprise · custom SLA · white-glove onboarding · joint threat intelligence integration · named executive sponsor · Custom-quoted based on environment scope |
The facts
Each one read from SCYTHE's own pages, with the date it was checked.
What it does
- AI campaigns
- AI can generate campaigns from plain-language threat descriptions, and execution requires human approval.checked 30 Sep 2026
- Compliance
- The homepage identifies SCYTHE as SOC 2 Type II certified and describes an annual independent security audit.checked 30 Sep 2026
- Customer support
- Foundation includes standard onboarding and support, while Advanced includes priority support and a dedicated customer success manager.checked 30 Sep 2026
- Deployment
- Listed deployment options are cloud (SaaS), on-premises, hybrid, and air-gapped.checked 30 Sep 2026
- Emulation
- It runs continuous MITRE ATT&CK-mapped adversary campaigns, including multi-stage campaigns based on named threat actors.checked 30 Sep 2026
- Integrations
- Listed integrations include CrowdStrike Falcon, Microsoft Defender, SentinelOne, Cortex XDR, Splunk, Microsoft Sentinel, IBM QRadar, Google Chronicle, Elastic SIEM, ServiceNow, and Jira.checked 30 Sep 2026
- Integration workflow
- SCYTHE says it integrates bidirectionally with SIEM, SOAR, EDR, ticketing systems, and security controls.checked 30 Sep 2026
- Intended users
- SCYTHE describes its audience as enterprise security teams, including financial services, critical infrastructure, federal and defense, and healthcare organizations.checked 30 Sep 2026
- Managed service
- SCYTHE offers managed adversarial exposure validation for organizations that want the company to operate campaigns and report on detection coverage.checked 30 Sep 2026
- Pricing limits
- Enterprise tiers include unlimited seats, agents, modules, and emulations; pricing is custom-quoted based on environment scope.checked 30 Sep 2026
- Product
- SCYTHE is a continuous Adversarial Exposure Validation platform that emulates real adversary behavior to validate security controls in an organization's environment.checked 30 Sep 2026
- Production safety
- The company says tests are controlled, configurable, logged, and auditable, and destructive capabilities require explicit authorization.checked 30 Sep 2026
- Validation
- The platform tests whether controls detect, alert, block, and respond, and maps results to ATT&CK coverage and identified gaps.checked 30 Sep 2026
The company
- Founded
- 2018checked 28 Sep 2026
- Headquarters
- Miami, Florida, United Stateschecked 28 Sep 2026
Alternatives to SCYTHE
- 1
AttackIQ Platform
Free planWebAPILinuxmacOS7.9From $4,995 a month - 2
Kali Linux
Free planOpen sourceAndroidLinuxmacOSSelf-hosted7.6Free plan - 3
OWASP ZAP
Free planOpen sourceAPIExtensionLinuxmacOS7.6Free plan - 4
ImmuniWeb
AndroidiOSWebAPI6.8From €595 a year - 5
Astra Security
WebAPI6.5From $699 a year - 6
Pentest-Tools.com API Scanner
WebAPILinuxmacOS6.5From $95 a month