Sandlock
Sandlock is a Linux process sandbox for confining untrusted code with policies enforced by the kernel.
What Sandlock is
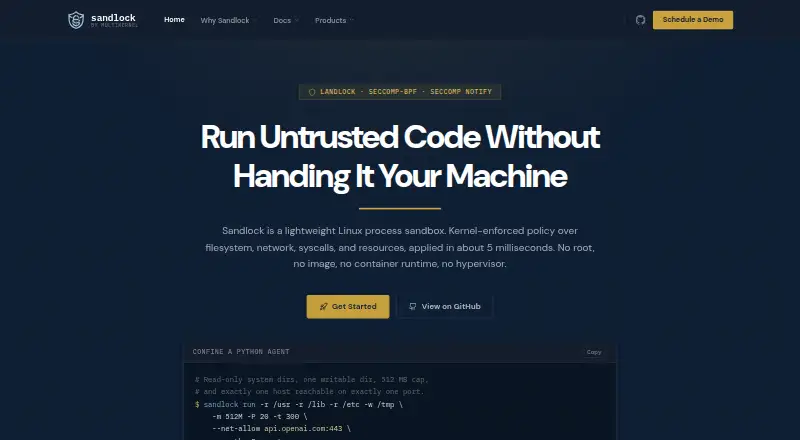
Sandlock is a Linux process sandbox for confining untrusted code with policies enforced by the kernel. It uses Landlock, seccomp-bpf, and seccomp user notification to control filesystem access, network activity, system calls, and resource use. Policies can deny network egress by default, allow HTTP traffic according to method, host, and path, stage writes using copy-on-write, and apply resource limits. A supervisor can add credentials through a proxy after an HTTP rule check, so the sandboxed process does not hold the secret itself.
Sandlock offers a CLI, Python SDK, Rust API, Go SDK, OCI runtime, and MCP server. Its OCI runtime integrates with containerd, CRI-O, and Kubernetes; its remote MCP API can connect to Claude Desktop, Cursor, or another MCP client. It runs as a regular user without root, a container runtime, or a hypervisor. Linux 6.12 or later provides the full protection set by default; older kernels require explicitly waiving unavailable protections. Sandlock shares the host kernel, so kernel vulnerabilities and hardware side channels are outside its security guarantees.
Good
- Free Apache-2.0 plan has no caps, telemetry, or registration.
- Controls filesystem, network, system calls, and resources.
- Runs as an ordinary user without root.
- Offers CLI, SDKs, APIs, OCI runtime, and MCP server.
Watch out
- Full protection set defaults to Linux 6.12 or later.
- Shares the host kernel; kernel flaws are outside its guarantees.
- Commercial API and Scheduler are self-hosted licensed software.
Who it suits
Sandlock may suit teams running AI agent tools, untrusted builds, or code for individual requests on Linux. It offers both developer interfaces and integrations with container and MCP environments.
Verdict
Sandlock combines kernel-enforced controls with interfaces for code, container, and MCP workflows. Check its kernel requirement and shared-kernel threat boundary against your deployment needs.
Plans and prices
From Sandlock's own pricing page, checked 4 Oct 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Sandlock | Free | No caps · no telemetry · no registration · Apache-2.0 |
| Sandbox HTTP API | — | Unlimited sandboxes and keys per deployment · priced by fleet size · self-hosted · Annual license |
| Sandbox Scheduler | — | Priced by node count · self-hosted · Annual license |
The facts
Each one read from Sandlock's own pages, with the date it was checked.
What it does
- Commercial deployment
- The commercial HTTP API and Scheduler are licensed software deployed on the customer's infrastructure, with no hosted or shared-tenant offering.checked 4 Oct 2026
- Credential handling
- The supervisor attaches secrets in the proxy only after the HTTP ACL check, so the sandboxed workload does not hold the secret value.checked 4 Oct 2026
- Enforcement
- It uses Landlock, seccomp-bpf, and seccomp user notification to control filesystem, network, syscalls, and resources.checked 4 Oct 2026
- Integrations
- The OCI runtime works with containerd, CRI-O, and Kubernetes, and the remote MCP API can be used with Claude Desktop, Cursor, or another MCP client.checked 4 Oct 2026
- Interfaces
- The product provides a CLI, Python SDK, Rust API, Go SDK, OCI runtime, and MCP server.checked 4 Oct 2026
- Kernel requirement
- Linux 6.12 or later supports the full protection set by default; older kernels can be used if missing protections are explicitly waived per policy.checked 4 Oct 2026
- Policy controls
- Policies can restrict filesystem access, default-deny network egress, apply HTTP method/host/path rules, inject credentials, stage writes with copy-on-write, and set resource limits.checked 4 Oct 2026
- Privileges
- Sandlock runs as an ordinary user and does not require root, a container runtime, or a hypervisor.checked 4 Oct 2026
- Purpose
- Sandlock is a lightweight Linux process sandbox for confining untrusted code with kernel-enforced policies.checked 4 Oct 2026
- Support
- Engineering support and a response SLA are included with each commercial license.checked 4 Oct 2026
- Threat boundary
- Sandlock shares the host kernel, and its security guarantees do not cover kernel vulnerabilities or hardware side channels.checked 4 Oct 2026
- Use cases
- The maker describes use for AI agent tool use, CI and untrusted builds, and per-request code execution.checked 4 Oct 2026
The company
- Company
- Sandlock is a Multikernel Technologies project; the maker lists its address as San Jose, California.checked 4 Oct 2026
- Headquarters
- San Jose, California, United Stateschecked 28 Sep 2026
Alternatives to Sandlock
- 1

Context Agent Sandboxes
Free planAndroidiOSWebAPI8.0From $20 a month - 2
E2B
Free planOpen sourceWebAPILinuxmacOS8.0From $150 a month - 3
Northflank
Free planWebAPILinuxmacOS8.0From $2.70 a month - 4
Daytona
Free planWebAPILinuxmacOS7.9Free plan - 5
ANY.RUN
Free planAndroidiOSWebAPI7.5Free plan - 6
Vercel
Free planWebAPI7.0$20 usage-based