RapidFort
RapidFort is a software supply chain security platform for containerized applications, combining vulnerability analysis, runtime visibility, hardened images …
What RapidFort is
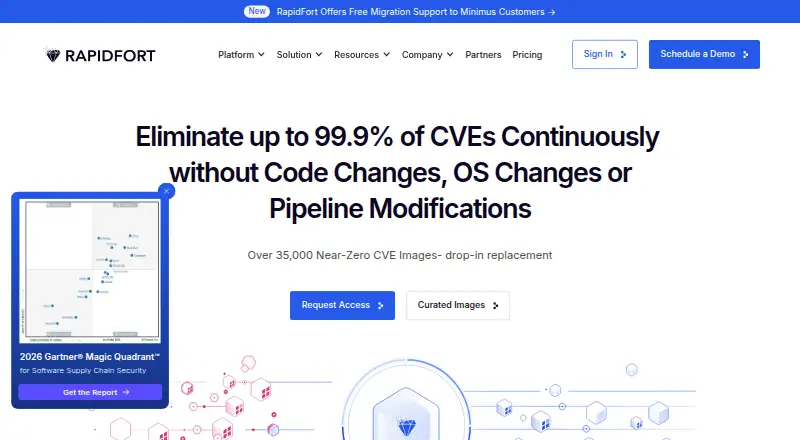
RapidFort is a software supply chain security platform for containerized applications, combining vulnerability analysis, runtime visibility, hardened images and compliance validation. Its Analyzer examines images, registries, CI pipelines and clusters, with vulnerability intelligence intended to reduce scanner noise. Profiler reports runtime behavior and builds a Runtime Bill of Materials from production usage; Optimizer removes unused components and refreshes hardened images on continuous 24-hour cycles. RapidFort also offers more than 35,000 curated near-zero-CVE container images. Its compliance service provides ongoing validation and audit artifacts aligned with benchmarks including CIS, STIG, NIST, HIPAA, PCI and FedRAMP. The free tier includes five curated images from a limited catalog, daily rebuilding and patching, and compatibility with standard container registries. Full-catalog and platform plans are custom-priced. RapidFort describes on-premises deployment, including air-gapped environments, and says continuous runtime profiling has less than 1% overhead without application changes. It presents the platform for security, DevSecOps and procurement teams, including in regulated settings.
Good
- Free tier includes five curated images.
- Scans images, registries, CI pipelines and clusters.
- Creates runtime bills of materials from production usage.
- Supports compliance validation and audit artifacts.
- Describes on-premises and air-gapped deployment.
Watch out
- Free catalog is limited to five images.
- Full-catalog and platform pricing is custom.
- Free tier includes daily, not 24-hour, rebuilds.
Who it suits
RapidFort is aimed at security, DevSecOps and procurement teams working with containerized applications. Its on-premises and air-gapped deployment options may suit organizations with those deployment requirements.
Verdict
RapidFort covers image analysis, runtime profiling, hardening and compliance in one container security platform. The free tier is limited, while broader catalog and platform offerings require custom pricing.
Plans and prices
From RapidFort's own pricing page, checked 30 Sep 2026.
| Plan | Price | What it gives you |
|---|---|---|
| Free | Free | 5 curated near-zero CVE images from a limited catalog · daily rebuilds and patching · Alpine, Debian, UBI, Ubuntu LTS · standard container registries |
| Custom — Full Catalog | Priced on request | 35,000+ curated images · full SBOM export · CIS and DISA STIG variants · FIPS 140-2 and 140-3 compliant images |
| Custom — Images + Platform | Priced on request | Full catalog plus platform · runtime profiling and RBOM · 24-hour hardening refresh · compliance validation and audit artifacts |
The facts
Each one read from RapidFort's own pages, with the date it was checked.
What it does
- Analyzer
- RapidFort Analyzer scans images, registries, CI pipelines, and clusters and provides validated vulnerability intelligence to help reduce scanner noise.checked 30 Sep 2026
- Compliance
- RapidFort CART provides continuous compliance validation and automated audit artifacts aligned with CIS, STIG, NIST, HIPAA, PCI, and FedRAMP benchmarks.checked 30 Sep 2026
- Container registries
- The free tier is described as compatible with standard container registries.checked 30 Sep 2026
- Curated images
- RapidFort offers more than 35,000 curated near-zero CVE container images built on trusted Linux distributions.checked 30 Sep 2026
- Deployment
- RapidFort describes an on-premises platform deployable through the Big Bang Helm Chart in on-premises or air-gapped environments.checked 30 Sep 2026
- Exports
- The pricing page lists SBOM export formats JSON, CSV, SPDX, and CycloneDX, with VEX and XML support for the full catalog tier.checked 30 Sep 2026
- Optimizer
- RapidFort Optimizer removes unused components and builds hardened images on continuous 24-hour cycles.checked 30 Sep 2026
- Product
- RapidFort is a software supply chain security platform for containerized applications, combining vulnerability analysis, runtime visibility, image hardening, and compliance validation.checked 30 Sep 2026
- Profiler and RBOM
- RapidFort Profiler reports runtime behavior and generates a Runtime Bill of Materials from actual production usage.checked 30 Sep 2026
- Runtime overhead
- The platform overview states continuous runtime profiling has less than 1% overhead and requires no application changes.checked 30 Sep 2026
- Security and compliance
- RapidFort states that its offering supports frameworks including FedRAMP, HIPAA, PCI, SOC 2, CMMC, CRA, NIS2, DISA STIG, CIS, and NIST SP 800-53.checked 30 Sep 2026
- Support
- RapidFort provides a Technical Support contact link on its website.checked 30 Sep 2026
- Target users
- RapidFort presents its products for security, DevSecOps, and procurement teams, including organizations in regulated and mission-critical environments.checked 30 Sep 2026
The company
- Founded
- 2020checked 28 Sep 2026
- Headquarters
- Sunnyvale, California, United Stateschecked 28 Sep 2026
The full review of RapidFort
RapidFort is a container security platform for teams that want to manage image risk, runtime visibility and compliance in a connected workflow. It is strongest for security and DevSecOps teams in regulated or mission-critical environments; teams seeking only a lightweight scanner may find its broader scope unnecessary.
Overview
RapidFort covers several stages of container security: scanning images and registries, observing what applications use at runtime, producing hardened images, and validating compliance. Its hybrid deployment model, including on-premises and air-gapped deployment, makes it a candidate for organizations with strict infrastructure constraints. The trade-off is that the free plan is narrow, while the full catalog and platform features require custom pricing.
Key features
Analysis and curated images
Analyzer scans images, registries, CI pipelines and clusters, using validated vulnerability intelligence intended to reduce scanner noise. That breadth is useful when a team needs visibility across its delivery path, rather than a registry-only check. The catalog contains more than 35,000 curated near-zero-CVE images built on trusted Linux distributions, but only five images from a limited catalog are included free.
Runtime profiling and hardening
Profiler reports runtime behavior and creates a Runtime Bill of Materials from production usage. RapidFort says continuous profiling adds less than 1% overhead and needs no application changes, a practical advantage for teams seeking runtime insight without modifying workloads. Optimizer removes unused components and rebuilds hardened images on continuous 24-hour cycles; the platform plan's 24-hour hardening refresh gives teams a path to keep those images current.
Compliance and exports
CART provides continuous compliance validation and automated audit artifacts aligned with CIS, STIG, NIST, HIPAA, PCI and FedRAMP benchmarks. RapidFort also says its offering supports frameworks including SOC 2, CMMC, CRA and NIS2. SBOM exports include JSON, CSV, SPDX and CycloneDX; VEX and XML support is reserved for the full catalog tier. This is a meaningful fit for audit-conscious teams, though the compliance workflow is part of the custom-priced platform rather than the free entry point.
Pricing
RapidFort uses a freemium model, but the free tier is best understood as a limited image-catalog option rather than a free version of the full platform.
- Free: free. Includes five curated near-zero-CVE images from a limited catalog, daily rebuilds and patching, Alpine, Debian, UBI and Ubuntu LTS images, and compatibility with standard container registries. It suits a small evaluation or a team that can work within those five images; it does not include the full catalog, runtime profiling or compliance validation.
- Custom — Full Catalog: custom pricing. Adds 35,000+ curated images, full SBOM export, CIS and DISA STIG variants, and FIPS 140-2 and 140-3 compliant images. This is the relevant step up for teams that need breadth and specialized image variants without the full platform.
- Custom — Images + Platform: custom pricing. Includes the full catalog plus runtime profiling and RBOM, 24-hour hardening refresh, compliance validation and audit artifacts. It fits teams consolidating image security, runtime visibility and compliance; the custom price means it is less suitable for buyers needing a fixed low-cost plan.
Platforms
RapidFort supports Linux, web and self-hosted use, with a hybrid deployment model. It also describes an on-premises platform deployable through the Big Bang Helm Chart in on-premises or air-gapped environments. Registry scanning, image scanning, SBOM generation, runtime protection and Kubernetes security are supported.
Who it's for
RapidFort is aimed at security, DevSecOps and procurement teams, particularly in regulated and mission-critical organizations. It is a good fit when curated images, runtime behavior, hardening and audit artifacts need to sit in one security program. An organization that only wants an open-source scanner, or cannot justify custom-priced catalog and platform capabilities, should look elsewhere.
Pros and cons
- Pro: Scanning spans images, registries, CI pipelines and clusters, giving teams a wider view than a single registry check.
- Pro: Runtime profiling, hardened-image rebuilding and compliance artifacts connect operational and audit needs in one platform.
- Pro: On-premises and air-gapped deployment accommodates environments with restricted connectivity.
- Con: The free catalog is capped at five images, limiting its usefulness for teams with larger image estates.
- Con: Runtime profiling, compliance validation and the broader catalog require custom pricing, which is a poor fit for buyers who need predictable public pricing.
Alternatives
For a broad comparison of products in this space, see Container Security Software, Container Image Scanning Tools and Cloud Vulnerability Scanners.
- Sysdig Secure is a paid alternative whose licensing is based on the number of hosts, or compute instances for CSPM; choose it when that host-based model better matches how you budget.
- Kubescape, maintained by ARMO, offers a free Apache 2.0 open-source CLI and Kubernetes operator that can be self-hosted; choose it when an open-source, Kubernetes-focused option is preferable to RapidFort's curated catalog and integrated platform.
- Deepfence ThreatMapper offers a free plan described as having no limits or hidden features; choose it when that free-plan structure is more important than RapidFort's curated images and compliance workflow.
- Trivy is a free, Apache-2.0 licensed open-source scanner; choose it when scanning is the need and RapidFort's runtime and compliance scope would be unnecessary.
- Aqua Security is a paid option with code-repository discovery and scanning and container image vulnerability and risk scanning; choose it when those stated capabilities suit the requirement.
- Wiz Container and Kubernetes Security is a paid, web-based alternative; choose it when a web-only option is the preference.
- Google Artifact Analysis charges $0.26 per scan for automatic scanning, with subsequent scans of the same image free; choose it when per-scan pricing fits better than RapidFort's custom-priced broader platform.
- Falco is a free, open-source option for Linux and self-hosted use; choose it when those platform needs and a zero-cost starting point are the priority.
Verdict
Choose RapidFort if your security or DevSecOps team needs curated container images, runtime profiling, hardening and compliance validation together, especially in regulated or air-gapped environments. Its strongest reason to choose it is that connected workflow; its strongest reason to look elsewhere is the five-image free cap and custom pricing for the capabilities that make the platform comprehensive.
Alternatives to RapidFort
- 1
Mondoo CSPM
Free planOpen sourceWebAPIExtensionLinux7.7Free plan - 2
Grype
Free planOpen sourceLinuxmacOSSelf-hostedWindows7.4Free plan - 3
Sysdig Secure
WebAPILinuxmacOS7.2From $20 a month - 4
Alibaba Cloud Container Registry
Free planWebAPILinuxWindows7.1Free plan - 5
Trivy
Free planLinuxmacOSSelf-hostedWindows7.0Free plan - 6
ZeroPath
WebAPILinuxmacOS6.5From $1,000 a month